

Topology
The following diagram shows an example of network connectivity for Aviatrix Edge Gateway to Transit Gateway in AWS.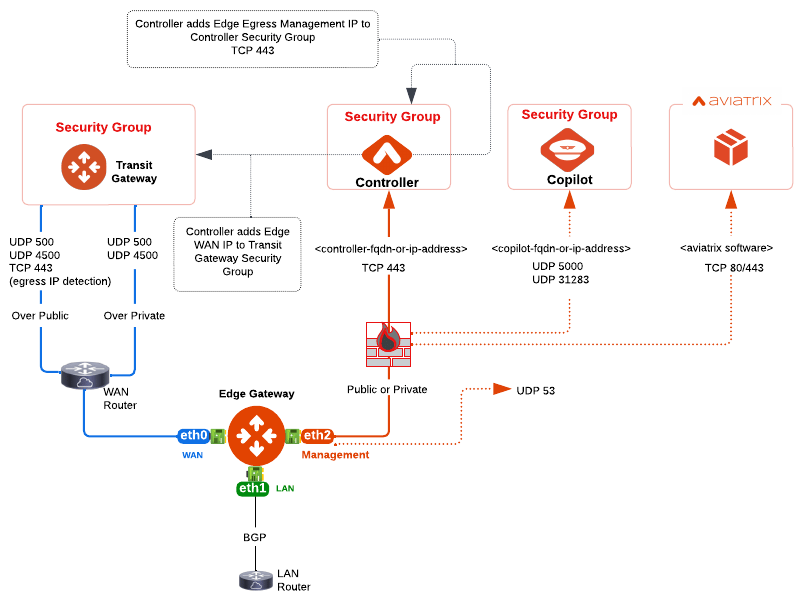
Prerequisites
Before you deploy an Aviatrix Edge Gateway on VMware ESXi or KVM, ensure the prerequisite requirements are complete, see Prerequisites for Edge Spoke Deployment on VMware ESXi and KVM .Aviatrix Edge Spoke Gateway Deployment Workflow
To deploy Aviatrix Edge Spoke Gateway, first you need to procure and onboard your edge device on the platform of your choice (see Prerequisites for Edge Spoke Deployment on VMware ESXi and KVM ). Next, you deploy the Aviatrix Edge Gateway on the edge device and attach the Edge Gateway to the Aviatrix Transit Gateway for cloud connectivity. Then, configure the Edge Gateway for LAN-side connectivity. The diagram below provides a high-level view of the four-step process for deploying Aviatrix Edge Spoke Gateway in Aviatrix CoPilot. You have the option to use either VMware ESXi or an open-source Kernel-based Virtual Machine (KVM) to deploy the Edge Spoke Gateway VM and attach the ISO file. The ISO file is the equivalent of the Zero-Touch Provisioning (ZTP) token. ZTP allows to remotely deploy and provision network devices at remote locations.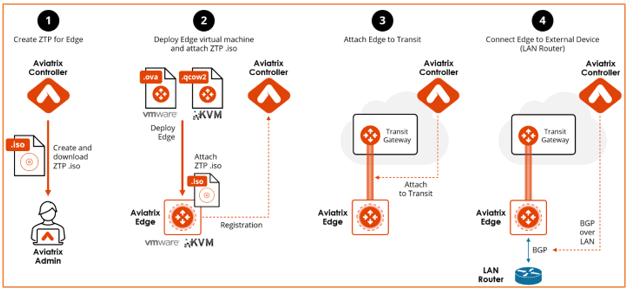
- Create the ZTP ISO for the primary Edge Gateway.
- Deploy the primary Edge Gateway Virtual Machine and Attach ZTP ISO.
- Create the ZTP ISO for the secondary Edge Gateway.
- Deploy the secondary Edge Gateway Virtual Machine and Attach ZTP ISO.
- Attach the primary Edge Gateway to a Transit Gateway.
- Connect the Edge Gateway to an external device.
Creating the ZTP ISO for the Edge Gateway (Self-Managed Platform)
You must have port 443 open to the IP address of the Aviatrix Controller. For the required port access for Edge Gateway deployment, refer to Aviatrix Edge Gateway Ports and Protocols . In Aviatrix CoPilot:- Go to Cloud Fabric > Hybrid Cloud > Edge Gateways tab.
- Click + Spoke Gateways, then provide the following information.
Deploying multiple Edge Gateways for the same site is supported. A maximum of
8 Edge Gateways are supported.
Configuring the Edge Gateway Interfaces
By default, an Aviatrix Edge Gateway has three interfaces: one WAN interface on eth0, one LAN interface on eth1, and one Management interface on eth2. You will need these configuration information to configure the interfaces. In the Interface Configuration section, configure the WAN, LAN, and Management interfaces for the Edge Gateway.Configuring the WAN Interface
Click WAN, then provide the following information. For IP and DNS settings, enter using the applicable format. For example, if the Edge Gateway’s WAN IP is 10.1.1.151, enter 10.1.1.151/24 or what your netmask is.To change or update the Edge Gateway WAN connectivity to Transit Gateway, you
will need to first detach the Edge-to-Transit gateway attachment, if there is
an attachment.
Configuring the LAN Interface
Click LAN, then provide the following information.
VLAN Interface
If your LAN is segmented into virtual LANs (VLANs), click + VLAN Interface
to add one or more VLAN sub-interfaces, then provide the following information
for each VLAN sub-interface.
You cannot edit the VLAN ID after the Edge Gateway is created. To edit the
VLAN sub-interface attributes, it is highly recommended to delete and recreate
the VLAN sub-interface configuration.
Configuring the MGMT Interface
Click MGMT, then provide the following information.
CoPilot creates the ISO file and downloads the file to your downloads folder.
Next, log in to your VMware ESXi or KVM host and upload the ISO or cloud-init
file to a datastore or storage device. Then, deploy the Edge Gateway VM instance
and attach the ISO or cloud-init image file to complete the Edge Gateway
creation and authentication with the Aviatrix Controller.
The ISO file expires after 24 hours. You cannot download it again and will
have to repeat the above steps. You must mount the ISO file to an Edge VM to
complete the Edge Gateway registration within 24 hours. See Deploying the
Edge Gateway Virtual Machine
Instance.
Creating a Highly Available Edge Gateway (Self-Managed Platform)
Before you can create the highly available Edge Gateway, the primary Edge Gateway must be deployed and its status must be Up. You must have port 443 open to the IP address of the Aviatrix Controller. For the required port access for Edge Gateway deployment, refer to Aviatrix Edge Gateway Ports and Protocols . To create a secondary (HA) Edge Gateway, follow these steps.- In Aviatrix CoPilot, go to Cloud Fabric > Edge > Gateways tab.
- In the table, locate the primary Edge Gateway for which you want to create the HA gateway and click its Edit icon.
- In the Edit Edge Gateway dialog box, from the High Availability dropdown menu, select Active-Active or Active-Standby mode.
- In the Interfaces section, configure the WAN, LAN, and Management interfaces for the secondary (HA) Edge Gateway.
LAN Interface
Click LAN, then provide the following information.
VLAN Interface
Provide the following information for each VLAN sub-interface.
VLAN configurations are added to the primary Edge Gateway. On the secondary
Edge Gateway, some fields are disabled and non-editable, the field value
appears when it is selected.
The ISO file expires after 24 hours. You cannot download it again and will
have to repeat the above steps. You must mount the ISO file to an Edge VM to
complete the Edge Gateway registration within the 24-hour timeframe.
Deploying the Edge Gateway Virtual Machine Instance and Attaching the ZTP ISO
See:- Deploying the Edge Gateway Virtual Machine in VMware ESXi
- Deploying the Edge Gateway Virtual Machine in KVM
Deploying the Edge Gateway Virtual Machine in VMware ESXi
To deploy the Edge Gateway virtual machine, follow these steps.- If you have not downloaded the ESXi OVA file, download the file by using the link provided to you by Aviatrix Support. See Download the Aviatrix Secure Edge Image File .
- Log in to VMware vSphere Web client to access the ESXi host. You can use vSphere Web client to manage ESXi host, launch a VM, mount ISO files, and start and stop the Aviatrix Edge Gateway.
- Load the OVA file into the ESXi using vSphere, go to ESXi > Virtual Machines > Create/Register VM.
- Select Deploy a virtual machine from an OVF or OVA file and click Next.
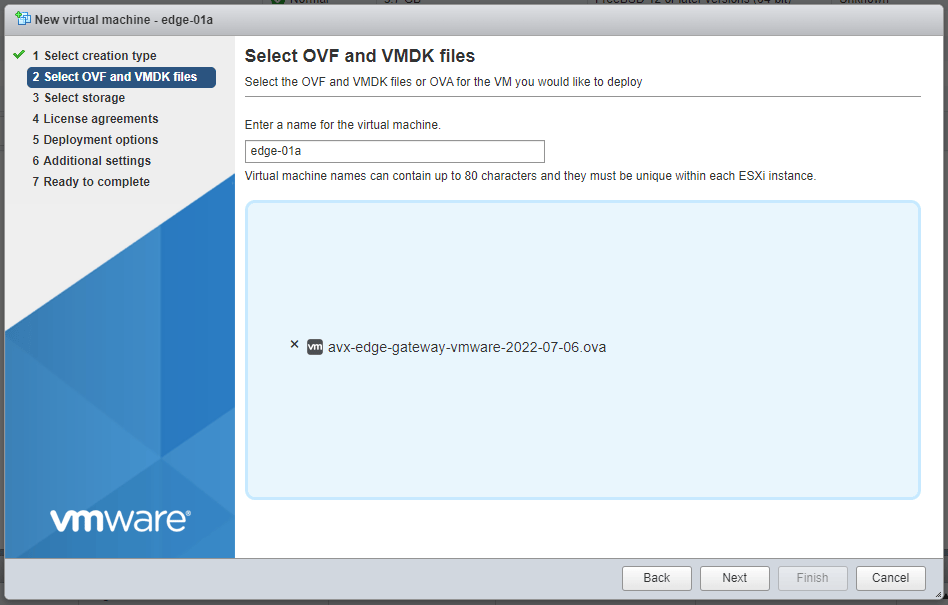
-
Enter a name for the Aviatrix Secure Edge VM and drag the OVA file into the
blue pane, then click Next.
- In the Select storage page, select the storage device where to create the VM instance (the OVA is installed in this instance) and click Next.
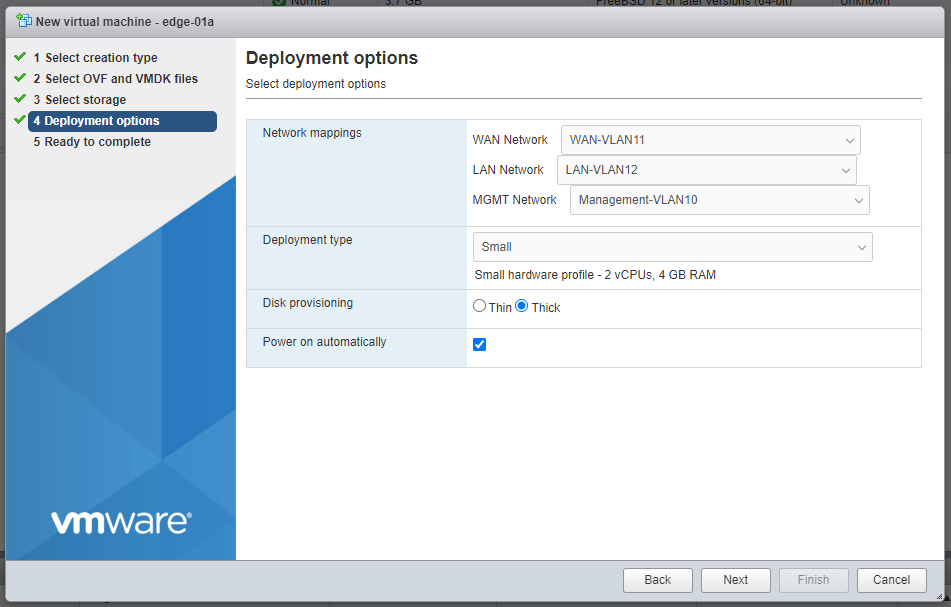
-
In the Deployment options window, enter the Network mappings for WAN,
LAN, and MGMT network interfaces and select the Deployment type. (Refer
to the pull-down menu or see
Virtual Machine CPU and Memory Configurations
.)
If necessary, you can change the network interface mappings after deployment.
- Click Next.
- In the Ready to complete page, click Finish.
Attaching the ISO File to the Edge Gateway Virtual Machine in VMware ESXi
The ZTP ISO file can only be used for a single Aviatrix Secure Edge VM
instance, and only one time for that instance.
The ZTP token expires after 24 hours. If you wait too long to boot up the VM
with the attached ISO image, it will not work. In that case, delete the Edge
Gateway in the Aviatrix CoPilot and create a new Edge Gateway to receive a new
ISO file.
- Upload the ISO file downloaded from Aviatrix CoPilot to your VMware datastore.
- In vSphere, select the Aviatrix Secure Edge VM you created and click Edit settings.
- Select the Virtual Hardware tab.
- Next to CD/DVD Drive 1, click the dropdown menu and select Datastore ISO file.
- Next to CD/DVD Drive 1, ensure the Connect box is checked and click Save. Connect at power on is required when you attach the ISO image to the VM for the first time. If the VM is powered on at the time you attach the ISO image, select the ISO file and save the configuration to make the ISO available to ZTP.
-
Next to the CD/DVD Media, click Browse, locate the datastore and select
the ISO file you uploaded.
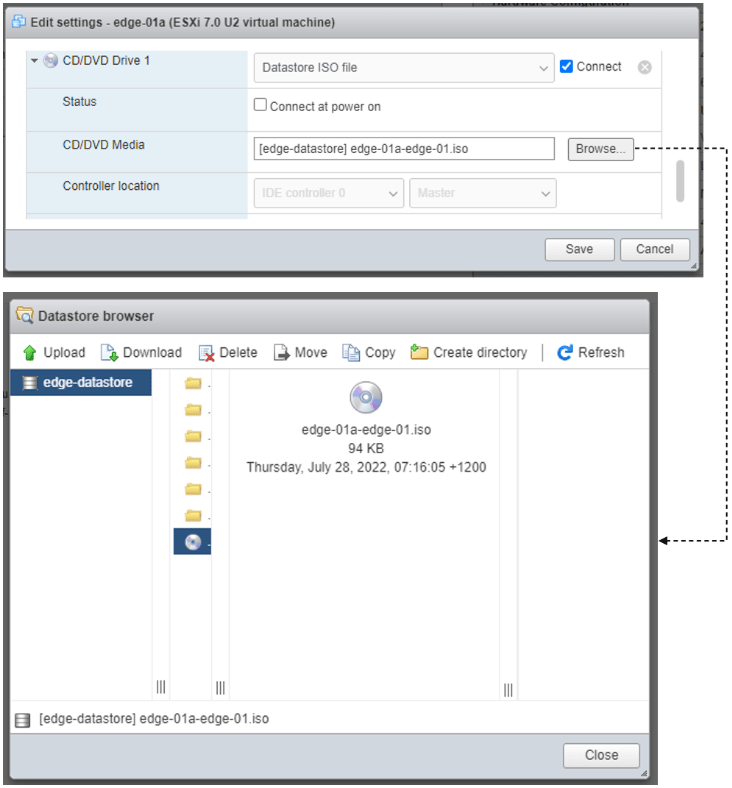
- Click Save. ZTP auto-mounts the ISO file and deploys the Edge Gateway on the VM.
Deploying the Edge Gateway Virtual Machine in KVM
Before you begin, on the KVM Linux host ensure the LAN, WAN, and MGMT network bridges are associated with the physical ethernet interfaces on the KVM sever. Refer to KVM product documentation.KVM Hypervisor does not support configuration of RX/TX queue size during
runtime. RX/TX queue size should be configured during Edge Gateway VM bootup.
See Enabling Multiqueue virtio-net on
KVM.
- If you have not downloaded the KVM QCOW2 file, download the file by using the link provided to you by Aviatrix Support. See Download the Aviatrix Secure Edge Image File .
- Launch Virtual Machine Manager UI to access the KVM host.
-
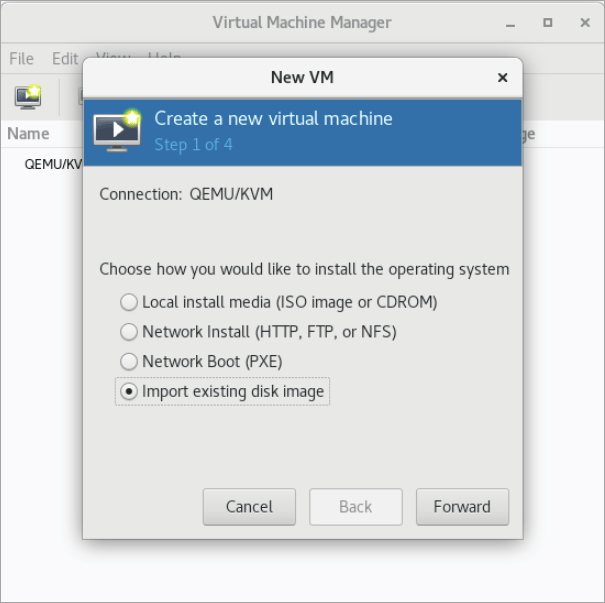
Create a new virtual machine from an existing disk image.
a. From the File menu, select New virtual machine.
b. Select the option Import existing disk image.
c. Click Forward.
-
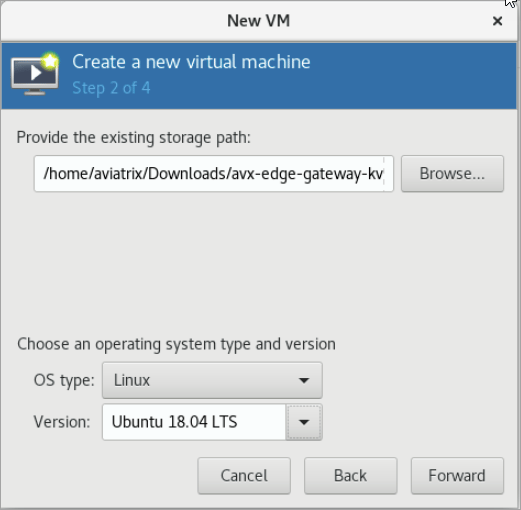
Provide the path to the KVM QCOW2 file and specify the operating system type
and version.
a. Enter the path or use the Browse button to locate the KVM QCOW2 file you
previously downloaded.
b. For OS type, select Linux.
c. For Version, select Ubuntu 18.04 LTS.
d. Click Forward.
-
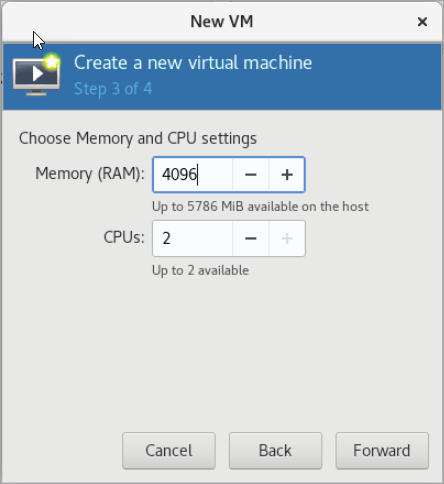
Enter the memory and CPU settings for the Edge Gateway VM and click
Forward.
-
Enter a name for the Edge Gateway VM and check the Customize configuration
before install checkbox, then click Finish.
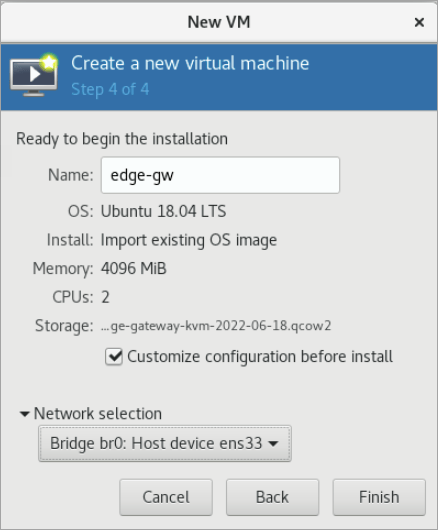
-
Add the LAN and MGMT virtual bridge interfaces.
a. Click Add Hardware.
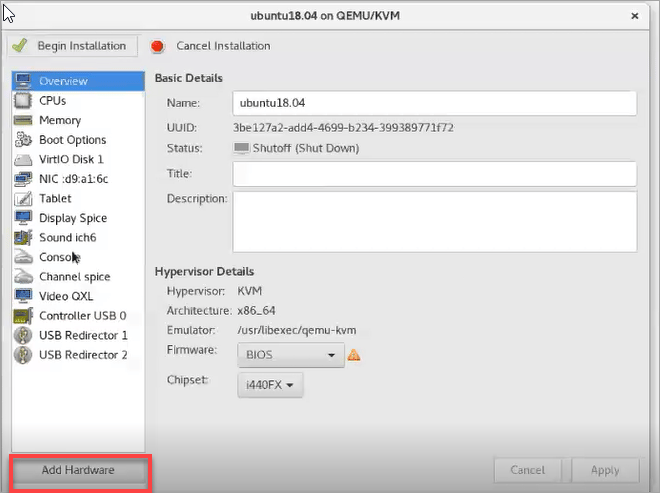
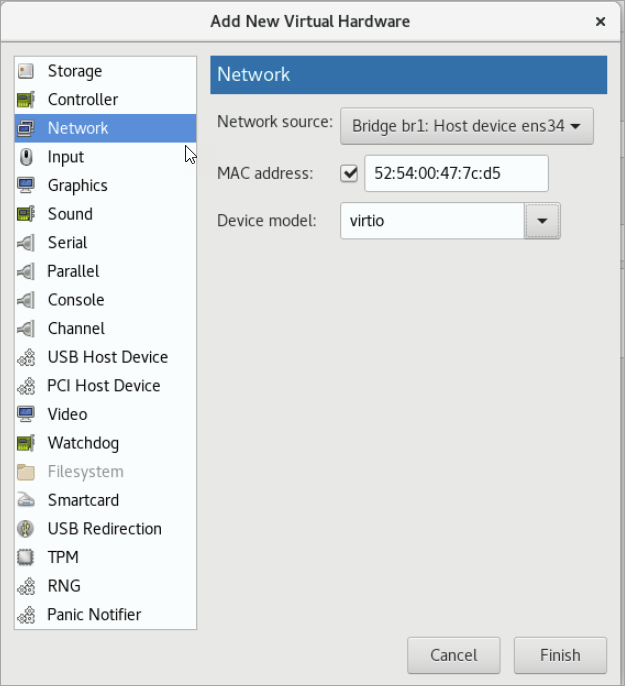
-
Choose the storage device and attach the ISO file to the VM.
a. In Add New Virtual Hardware, select Storage from the left pane.
b. Select the option Select or create custom storage.
c. Click Manage.
d. Locate and select the KVM iso file which you previously uploaded.
e. Click Choose Volume.
f. Click Finish.
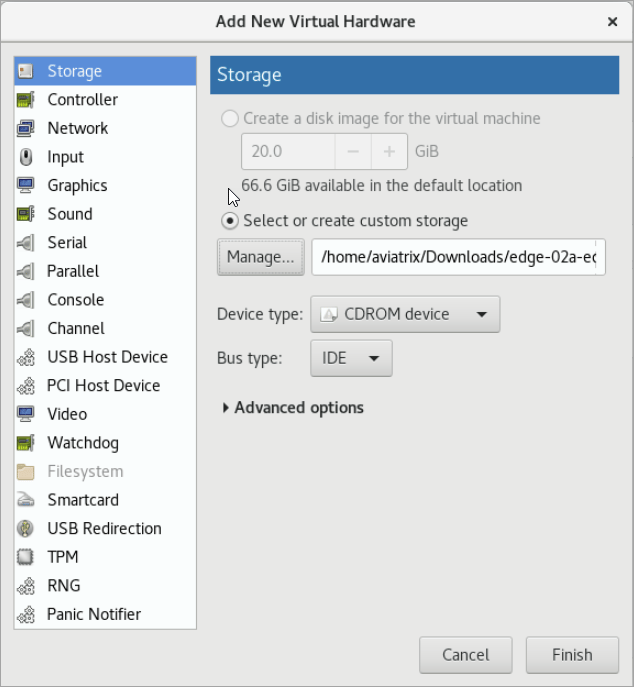
- Click Begin Installation to create the Edge Gateway VM on the KVM host.
Attach an Edge Spoke Gateway to a Transit Gateway
To attach an Edge Spoke Gateway to a Transit Gateway, perform the prerequisites then create the attachment.Prerequisites
Before you create the attachment:- Ensure Local ASN Number is configured on Edge and Transit Gateway.
-
If the Edge to Transit Gateway attachment is over public network, you need to
update the WAN Public IP on the Edge Gateway.
- Go to Cloud Fabric > Hybrid Cloud > Edge Gateways tab.
- Click Spoke Gateways.
- Locate the Edge Gateway, and click its Edit icon on the right.
- In Edit Edge Gateway, go to Interface Configuration and click WAN.
-
In Public IP, click Discover.
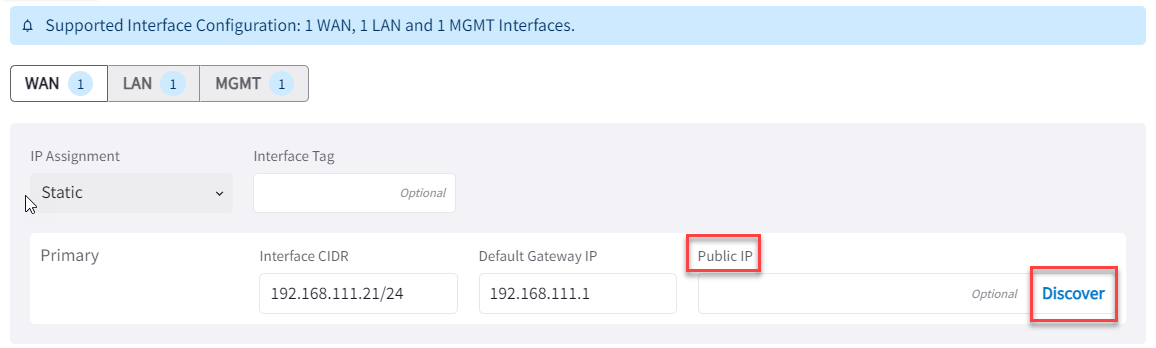
- Verify the WAN Public IP and click Save.
Attach Edge Spoke Gateway to Transit Gateway
To create a High Performance Encryption attachment peering, make sure the
Transit Gateway is created with High Performance Encryption enabled.
If you want Jumbo Frame enabled for the attachment peering, make sure to
enable Jumbo Frame on the Edge Gateway before you attach it to the Transit
Gateway.
- In Aviatrix CoPilot, go to Cloud Fabric > Hybrid Cloud > Edge Gateways tab.
- Click Spoke Gateways.
-
Locate the Edge Spoke Gateway, and click Manage Gateway Attachments icon

- In Manage Gateway Attachments > Transit Gateway tab, click +Attachment and provide the following information.
To attach the Edge Spoke Gateway to another Transit Gateway, click +
Attachment again and provide the required information.
You can attach an Edge Spoke Gateway to multiple Transit Gateways. Each
attachment can be configured with different parameters, such as connecting
interfaces, connection over private or public network, high-performance
encryption, and Jumbo Frame.
- Click Save.
Manage Gateway Attachments
You can attach an Edge Spoke Gateway to multiple Transit Gateways. Each attachment can be configured with different parameters, such as connecting interfaces, connection over private or public network, high-performance encryption, and Jumbo Frame. Click + Attachment and provide the required information.
Advanced
Next,
connect the Edge Gateway to the external device.
Connecting Edge Spoke Gateway to an External Device (BGP over LAN)
For LAN-side connectivity, you can connect the Edge Spoke Gateway to an external device, such as a LAN BGP router. To connect the Edge Gateway to the LAN BGP router, follow these steps.- In CoPilot, navigate to Networking > Connectivity > External Connections (S2C) tab.
- From + External Connection To dropdown menu, select External Device, then provide the following information.
- In LAN Configuration, provide the following information.
- Click Save.