- Perform the prerequisite steps.
- Configure the VNet Peering Between Transit and Azure Route Server VNets.
- Configure the BGP peering Between Azure Route Server and Transit Gateways.
- Configure the BGP over LAN External Connection to Azure Route Server.
Prerequisites
Ensure the following prerequisites are met:- The Aviatrix Controller is updated to software version 6.8 or above.
-
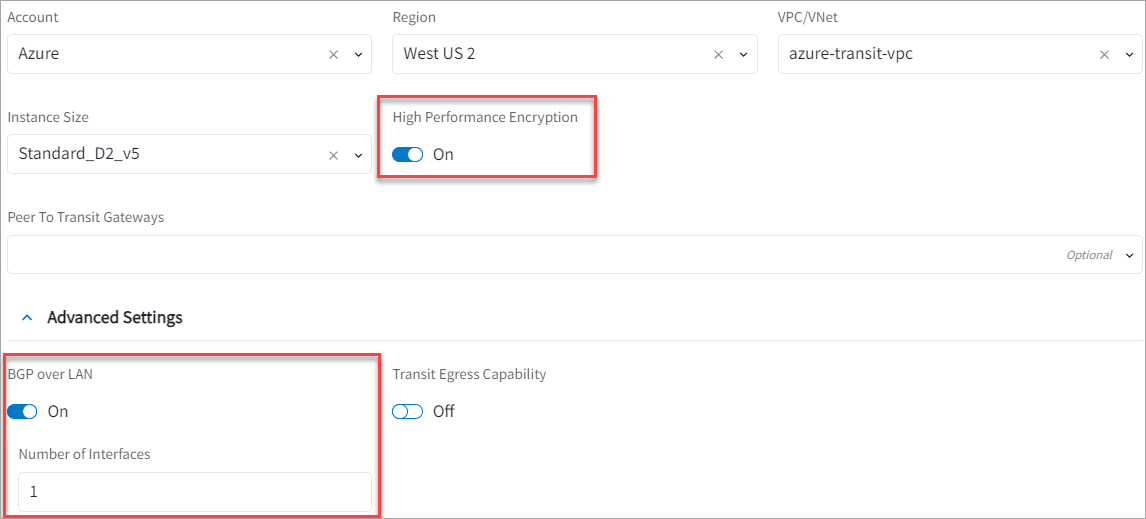
Aviatrix Transit Gateways are deployed with High Performance Encryption (HPE)
and with BGP over LAN enabled. You only need to configure one BGP over LAN
interface to peer with both Azure Route Server instances.
- A BGP ASN is assigned to the Transit Gateways (configure by going to CoPilot > Cloud Fabric > Gateways > Transit Gateways tab, select the Transit Gateway and go to Settings > Border Gateway Protocol (BGP) > Local AS Number).
-
Complete the following tasks in Azure:
- Create a VNet to deploy the Azure Route Server.
- Deploy the Azure Route Server in this VNet by referring to the applicable Azure documentation.
-
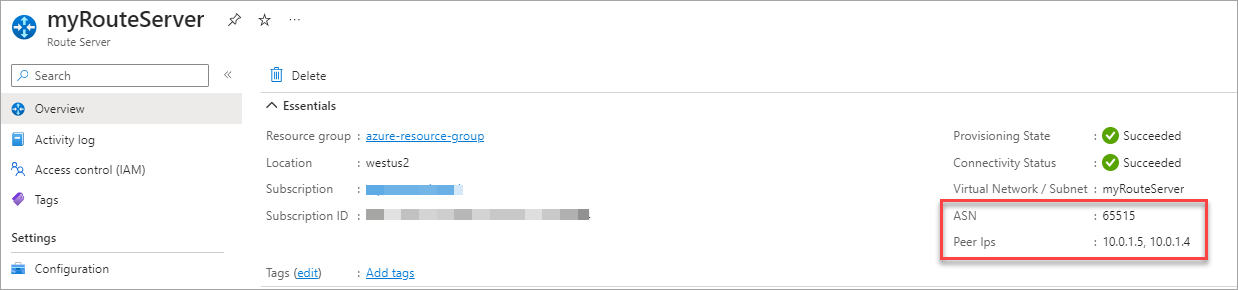
Go to your Route Server > Overview and record the ASN and the private IP
addresses of the Azure Route Server endpoints you created. You will use
these later in the Aviatrix CoPilot configuration.
Configure the VNet Peering Between Transit and Azure Route Server VNets
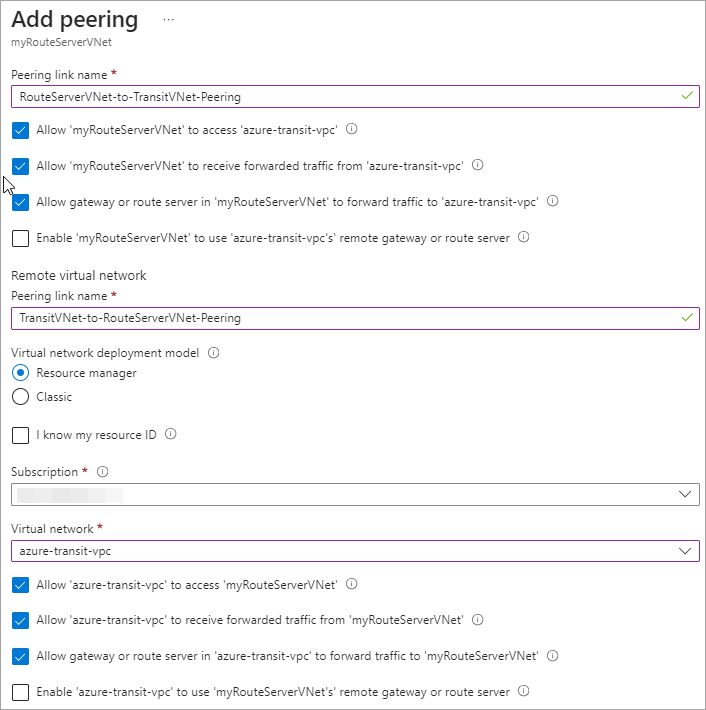
You need to configure the VNet peering between the VNet that is hosting the Azure Route Server and the Aviatrix Transit VNet. Follow these steps to configure the peering parameters from the Azure Route Server VNet to the Aviatrix Transit VNet.- Launch the Azure Portal.
-
Go to Virtual networks and select your Route Server VNet.
- Under Settings, click Peerings.
- On the Peerings page, click Add.
-
On the Add peering page, select the following options:
- Click Add.
Configure the BGP peering Between Azure Route Server and Transit Gateways
-
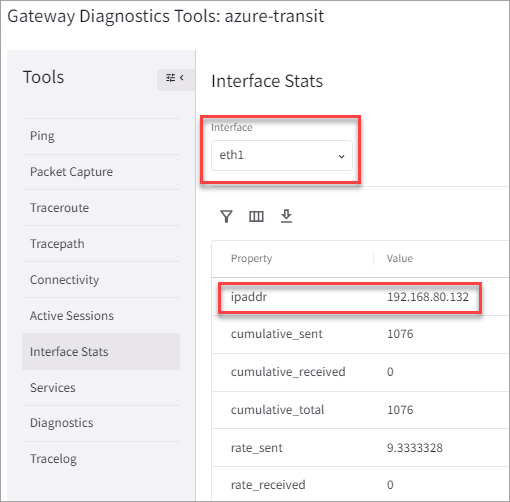
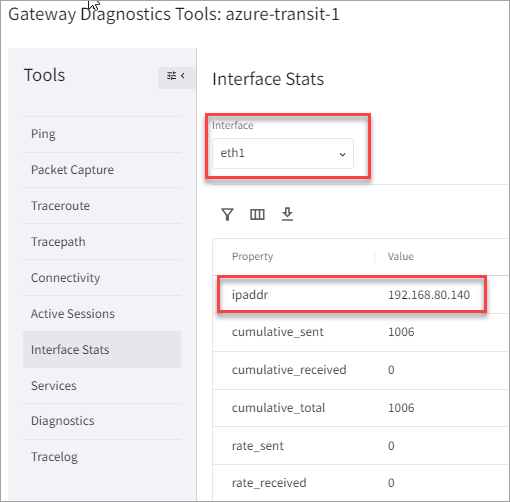
In Aviatrix CoPilot, go to Cloud Fabric > Gateways, select your
primary Transit Gateway and click Gateway Diagnostics. Then, click
Interface Stats and record the IP address assigned to the BGP over LAN
interface. Repeat this step for the HA Transit Gateway.
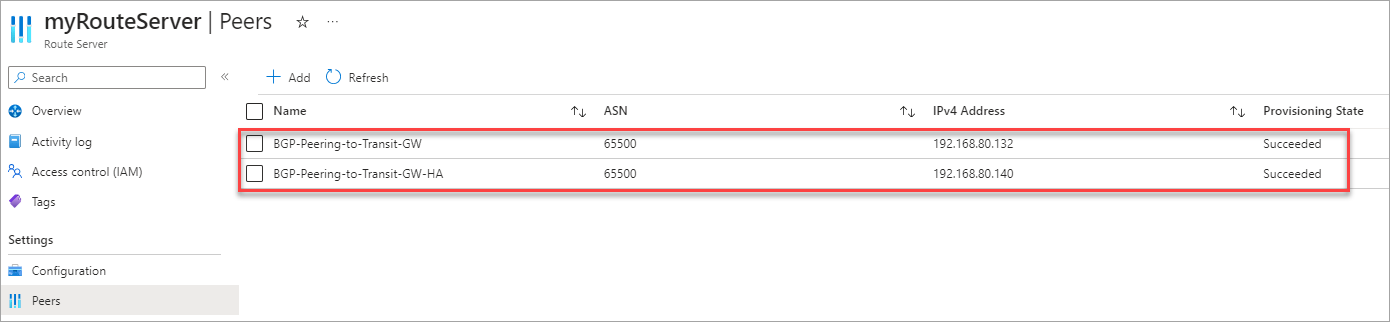
- In your Azure portal, go to Route Servers > select your Azure Route Server > Peers, and click Add.
-
Configure the Azure Route Server peering to both remote Aviatrix Transit
Gateways in the Transit VNet by specifying the ASN you configured for your
Aviatrix Transit Gateways and the IP address of the BGP over LAN network
interface on each Transit Gateway. Refer to the
Prerequisites section to find the ASN number.
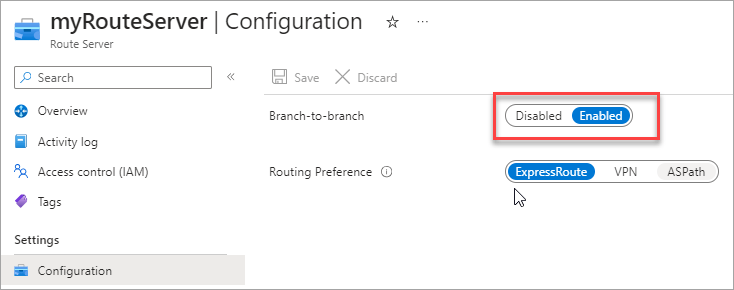
- Go to Route Servers > select your Azure Route Server > Configuration.
-
Next to Branch-to-branch, select Enabled.
This option allows the Azure Virtual Network Gateways to propagate the routes
the Azure Route Server has learned from the Aviatrix Transit Gateways. It is
disabled by default.
Configure the BGP over LAN External Connection to Azure Route Server
- CoPilot UI
- Terraform
In Aviatrix CoPilot:
- Go to Networking > Connectivity > External Connections (S2C) tab.
- Click + External Connection.
-
Provide the following information.
-
Click + Connection to add a new connection.
- Click Save.
Verifying the LAN Connection Status
You can check the tunnel status by going to Diagnostics > Cloud Routes > External Connections. Confirm that Tunnel Status is Up and that HA Status (Activemesh for the Route Servers) and BGP Status is enabled.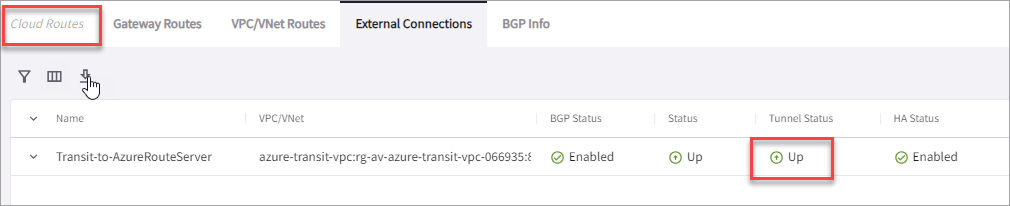
Verifying the BGP Session Status
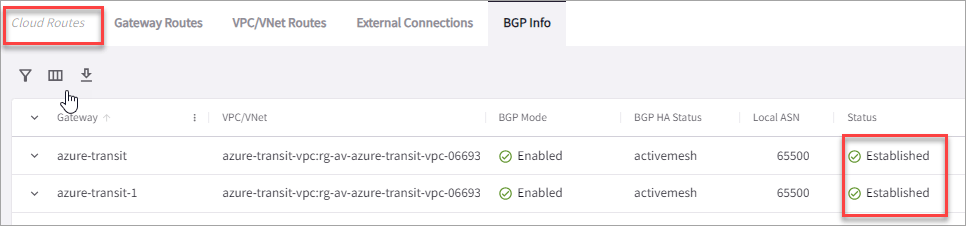
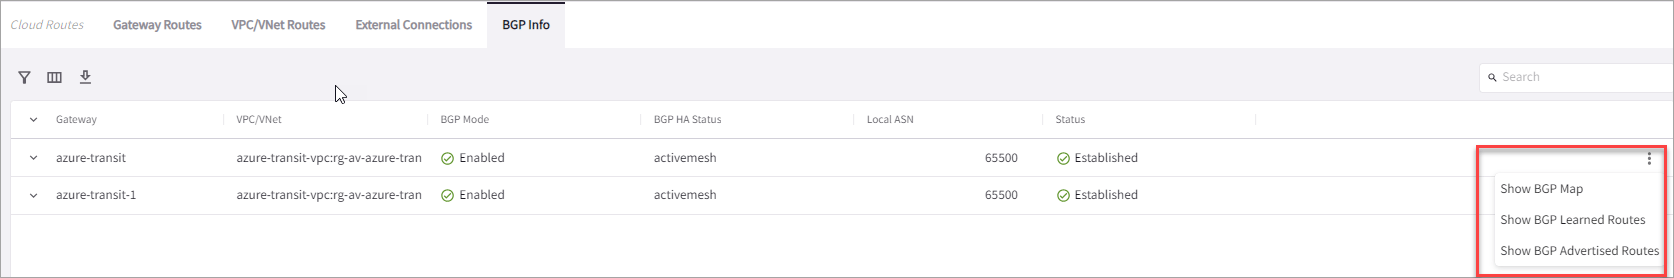
You can check the BGP session status by going to Diagnostics > Cloud Routes > BGP Info. The Status should be Established. If some external connections for the selected Transit Gateway are Not Established, the overall BGP Status for the Transit Gateway is Partially Established.