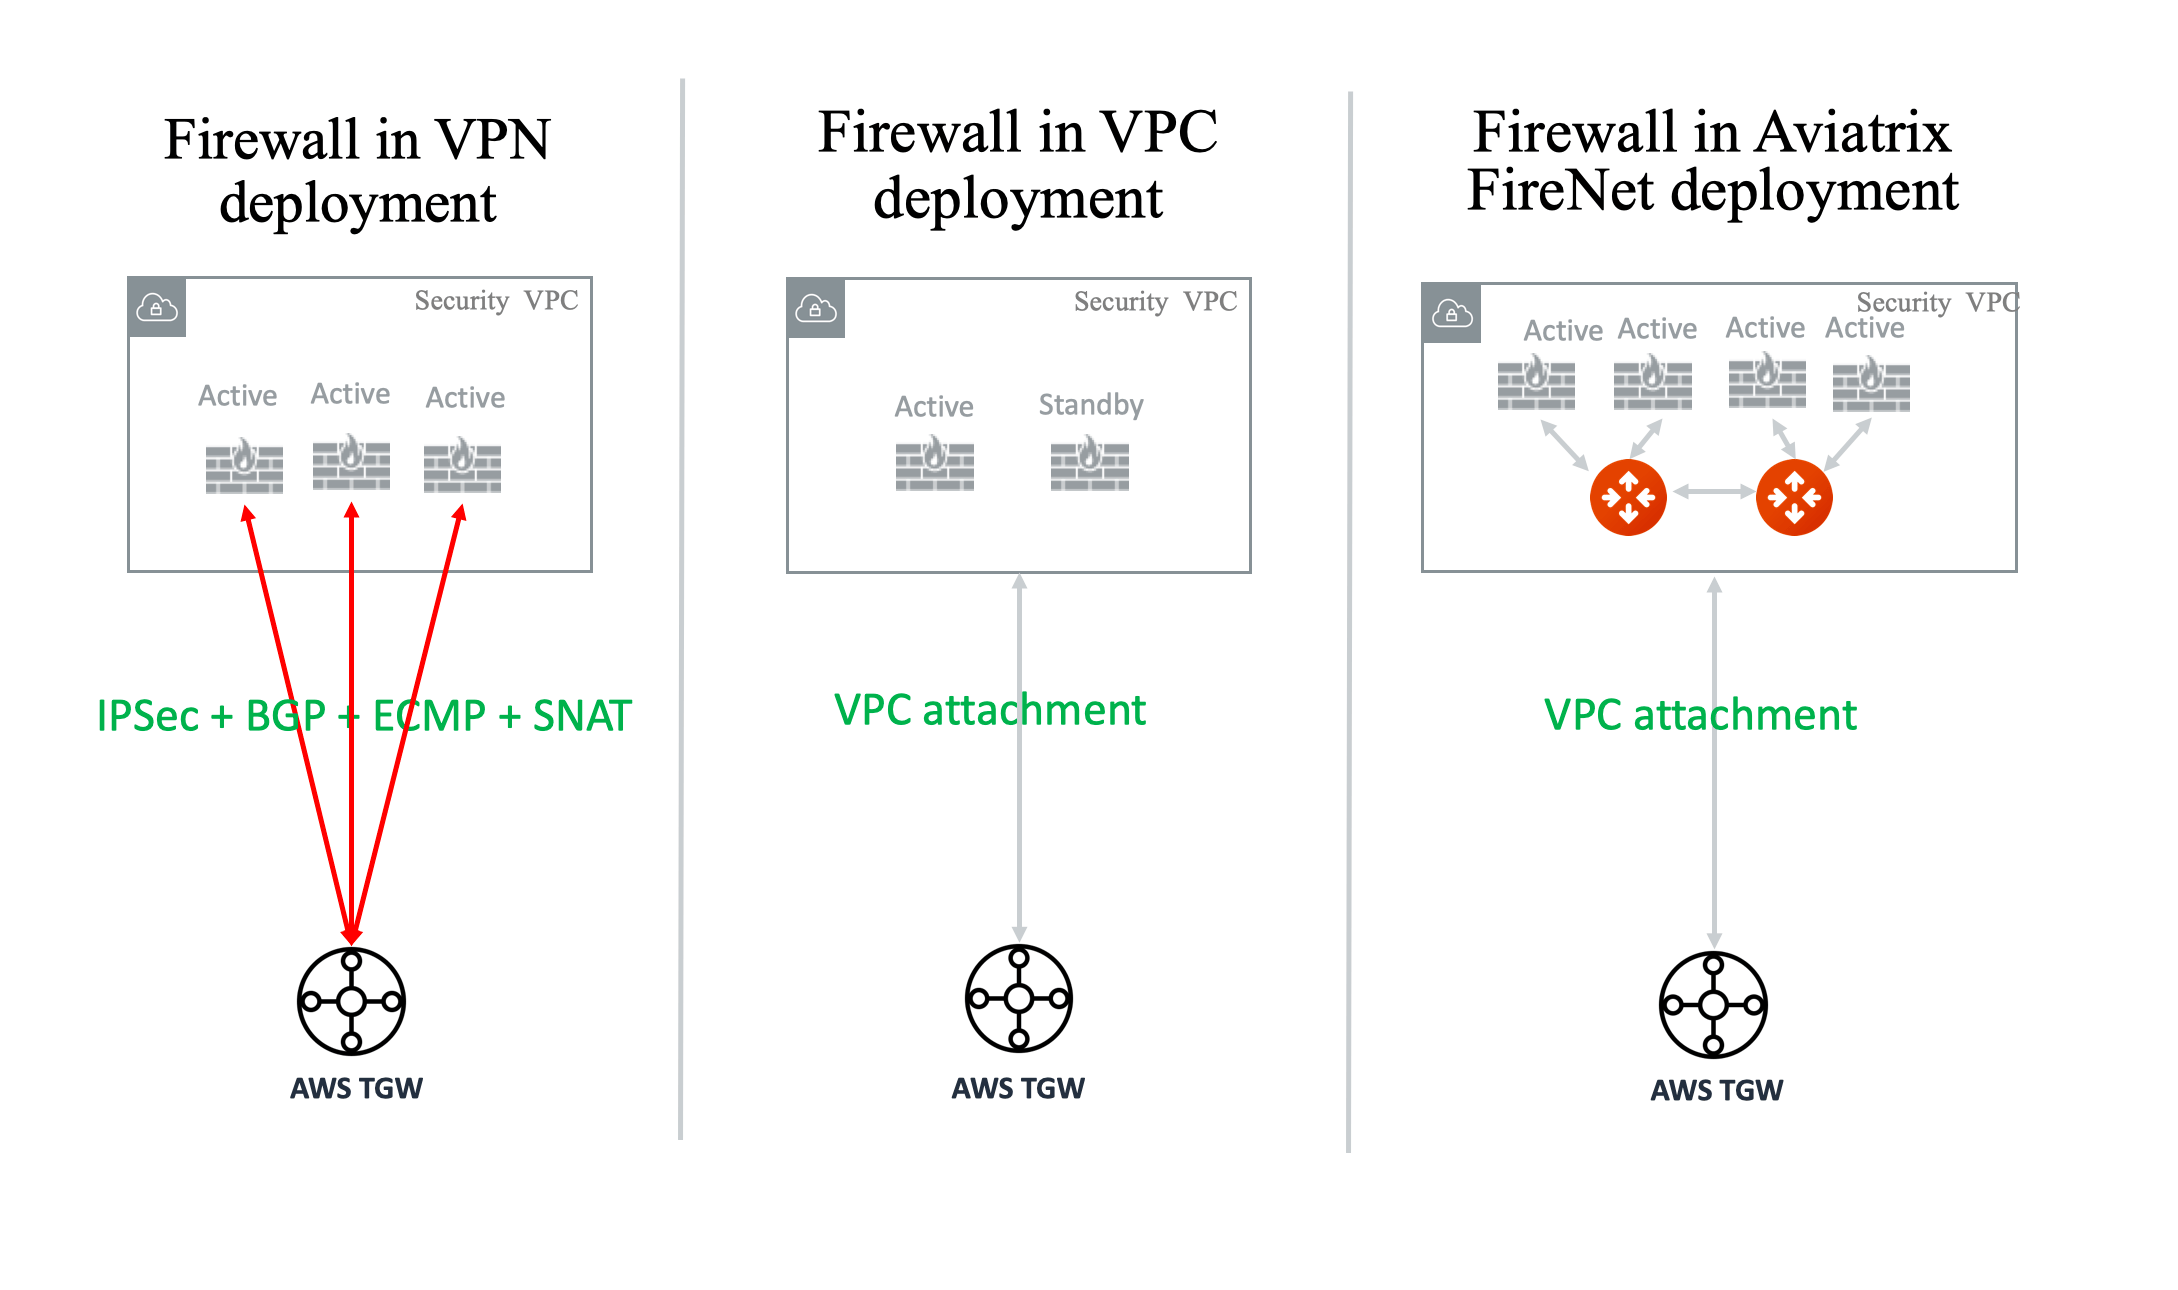
There are two native deployments: TGW VPN to connect to firewall or TGW VPC attachment to connect to firewall.
There are two native deployments: TGW VPN to connect to firewall or TGW VPC
attachment to connect to firewall.The three different deployment models are illustrated in the diagram below.If an AWS Transit Gateway connects to a firewall by using its built in VPN
function, it must run IPsec and BGP. If you run more than one firewall instance
using ECMP, each firewall instance must configure SNAT function to ensure that
both source and destination-initiated traffic lands on the same firewall
instance. Furthermore, since native deployment requires an IPsec VPN which
limits its performance to 1Gbps, in this scenario a single firewall instance can
only perform at 500Mbps since the VPN function is traversed twice.A more detailed functional comparison is described in the table below.