

Introduction
Transit BGP to LAN allows Aviatrix Transit Gateways to communicate with a pair of instances in the same VPC in AWS without running any tunneling protocol such as IPsec or GRE. One use case is to interoperate with third-party virtual appliances such as SD-WAN cloud instances that do not have the capability to support BGP over any tunneling protocols. For example, integrating with SD-WAN gateways can be deployed as below, where an Aviatrix Multicloud Transit Gateway connects to a third-party cloud instance in the same VPC in AWS.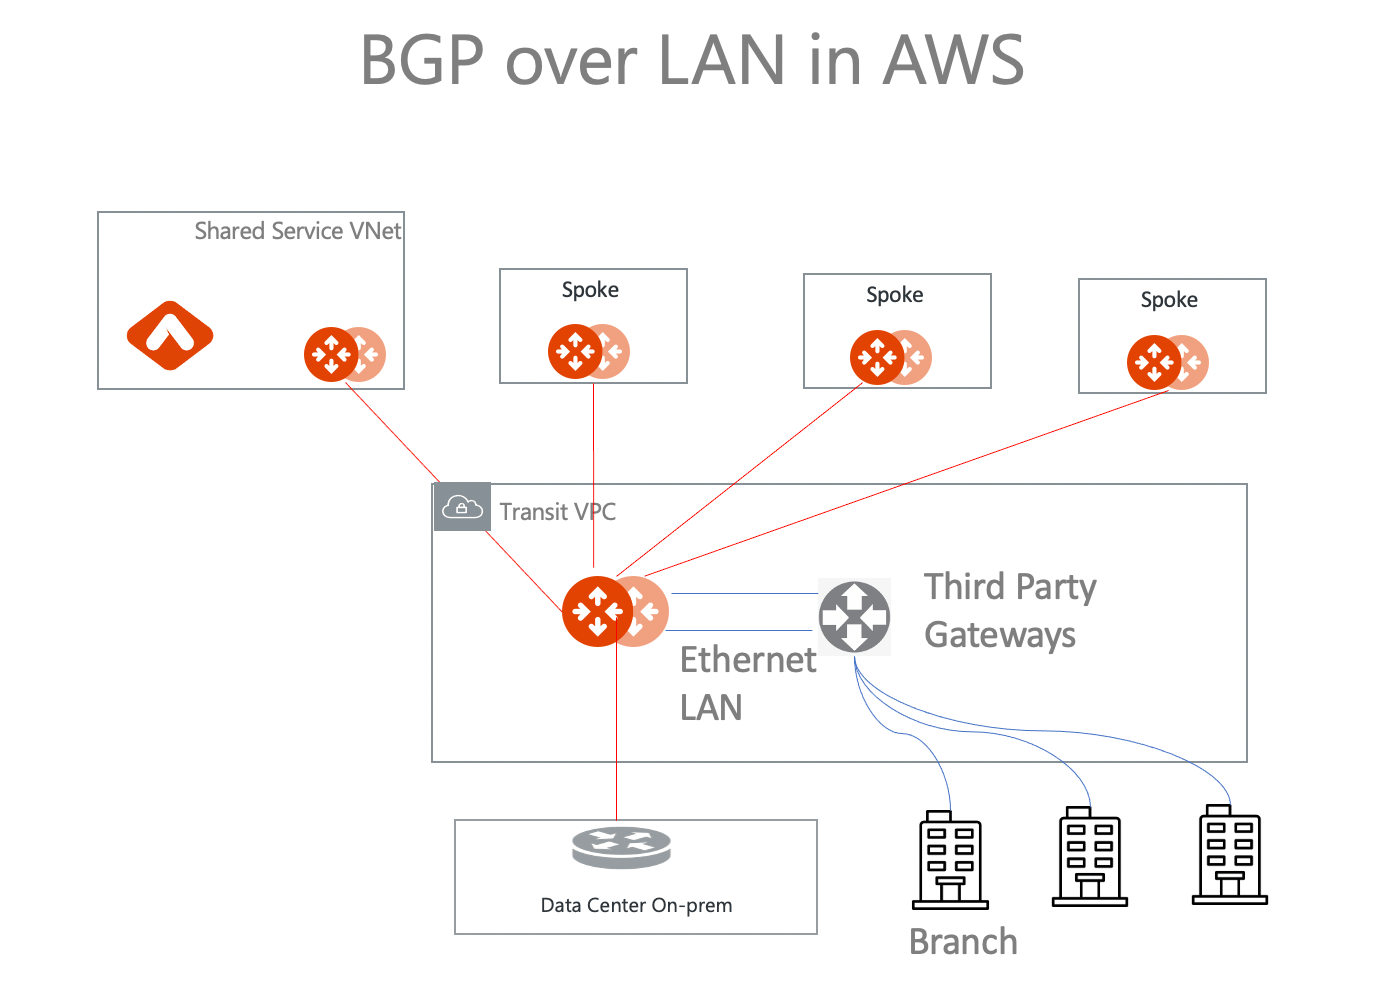
- Multi Cloud Global Transit FAQ
- Global Transit Network Workflow Instructions (AWS/Azure/GCP/OCI)
- Aviatrix Transit Gateway to External Devices
- Transit Network Design Patterns
- This solution supports only ActiveMesh 2.0, please check this doc How to migrate to ActiveMesh 2.0 for migration detail.
- This solution is available to AWS and Azure. The AWS workflow in this document is just an example. Please adjust the topology depending on your requirements.
- Controller 8.2 or later: An instance size that supports at least 2 interfaces is required, such as t3.small and t2.medium in AWS.
- Controller 6.3 to 8.1: An instance size that supports at least 5 interfaces is required, such as c4.4xlarge, c5.4xlarge, and c5n.4xlarge in AWS.
- LAN interfaces for Aviatrix Transit Primary and third-party cloud instance must be in the same Availability Zone.
The key ideas for this solution are:
- A BGP session is established between a third-party cloud instance and an Aviatrix Transit Gateway via each LAN interface in the same VPC.
- Data plane traffic also runs between a third-party cloud instance and Aviatrix Transit Gateway via each LAN interface without a tunnel protocol such as IPsec and GRE.
Prerequisites
- Upgrade Aviatrix Controller to at least version 6.3 for the instance with a minimum of 5 interfaces and Controller version to 8.2 for the instance with a minimum of 2 interfaces.
- In this example, you are going to deploy the below VPCs in AWS:
- Transit VPC (i.e. 10.1.0.0/16) by utilizing Aviatrix feature Create a VPC with Aviatrix FireNet VPC option enabled.
- Spoke VPCs (i.e. 192.168.1.0/24 and 192.168.2.0/24) by utilizing Aviatrix feature Create a VPC as the previous step or manually deploying it in each cloud portal. Moreover, feel free to use your existing cloud network.
- Third-party cloud instance supports high throughput.
Deploying the Aviatrix Multicloud Transit Solution
Refer to Global Transit Network Workflow Instructions for the below steps. Please adjust the topology depending on your requirements.- Deploy the Aviatrix Multicloud Transit Gateway and HA with High Performance Encryption Mode enabled. In this example, size c5n.4xlarge is selected to benchmark performance.
- Deploy a Spoke Gateway and HA to launch Aviatrix Spoke gateway and enable HA with High Performance Encryption Mode enabled in the Spoke VPC. In this example, size c5n.4xlarge is selected to benchmark performance.
- To resize an existing Aviatrix Gateway to t3.small or t2.medium (2 interfaces), only for BGP over LAN, ensure FireNet option is disabled, see Resizing Aviatrix Gateway Instances
- Attach Spoke Gateways to Transit Network.
Launching Third-Party Cloud Instances
Deploy third-party cloud instances in the same VPC where the Aviatrix Transit Gateways are located.- Create a third-party cloud instance and put the MGMT interface in the public gateway subnet.
- Create a new public WAN subnet and a dedicated routing table for the WAN interface if needed.
- Create a new private LAN subnet and a dedicated routing table (optional) for the LAN interface.
- Make sure the function “Source/Dest check on third-party cloud instance’s interfaces” is disabled.
The primary Aviatrix Transit Gateway must be deployed in the same Available
Zone (AZ) as the first third-party cloud instance. The HA Transit Gateway if
deployed must reside in the same AZ as the second cloud instance.
Building BGP over LAN
Configure BGP over LAN on the Aviatrix Transit Gateway.- In CoPilot, go to Networking > Connectivity > External Connections (S2C).
- Click External Connection.
- In the Add External Connection dialog, select External Device and BGP over LAN.
- Enter the following information in the fields.
- Click Save to generate BGP session over LAN.
Downloading the BGP over LAN configuration
- On the External Connections (S2C) tab, click the vertical ellipsis
 and select Download
Configuration.
- Select the Vendor type, Platform, and Software.
- Click Download.
Configuring BGP over LAN on Third-Party Cloud Instance
- Open the downloaded BGP over LAN configuration file.
- Configure the related BGP and LAN settings in the third-party cloud instance.