> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Back Up and Restore Your Controller on Controller UI
> Back up and restore Aviatrix Controller configuration using the Controller UI.
This page introduces:
* [Backing up Your Controller Configuration on Controller](#backup-controller-controllerui)
* [Restoring Your Controller Configuration on Controller UI](#restore-controller-controller-ui)
Starting from CoPilot version 3.14, you have the option to back up and restore
your Aviatrix Controller directly from the CoPilot UI. See
Back up and Restore Your Controller on CoPilot UI
for more details.
## Backing up Your Controller Configuration on Controller
Aviatrix stores the Controller backup in an AWS S3 bucket or an Azure Container.
Before you begin, determine where you would like to store the backup and create
either the S3 bucket or Azure Container.
Creating regular backups of your Aviatrix Controller is essential to ensure the
security and integrity of your network configurations. In the event of a failure
or the need to migrate to a new Controller, having a backup allows you to
quickly restore your settings and minimize downtime.
* Make sure your Controller backup and Controller restore take place in the same
CSP (Cloud Service Provider): AWS, Azure, or GCP and share the same basic
configuration. For example, an AWS backup can only restore to another AWS
Controller.
* Note that in the case of AWS backups, an AWS Controller set up with IAM roles
cannot back up and restore to an AWS Controller set up with a secret key, or
vice versa.
* (AWS) The S3 bucket you use or create for Controller HA and Backups does not
need to have public access enabled and should be configured to restrict
general public access.
1. Log into the Controller.
2. Go to **Settings** > **Maintenance** > select the **Backup & Restore** tab.
3. Under the *Backup* section:
* Select the appropriate *Cloud Type* and *Account Name*.
* AWS: populate the *S3 Bucket Name*.
* Azure: populate the Region, Storage Name, and Container Name.
* GCP: populate the Bucket Name, Gcloud Project Credentials, and File Name.
* OCI: populate the Tenancy OCID, User OCID, Compartment OCID, API Private
Key File, Bucket Name, Region, and File Name.
4. (Optional) You can click *Multiple Backup* to enable multiple backups. See
[Multiple Backup](#multiple-backup) for more details.
By default, only the latest configuration data is stored. Each time the
configuration is backed up, it overwrites the previous one. If you would like
to keep every copy, check the box *Multiple Backup*.
5. Click ***Enable***.
The first time you enable this feature, the configuration will backed up to your
specified location. After this, the configuration data is automatically backed
up daily at 12 am.
### Multiple Backup Selecting the *Multiple Backup* checkbox enables the
Controller to backup a maximum of 3 rotating backups. Each backup filename will
contain the date and time of when the backup is made. Additionally, the backup
without any date and time in the filename contains a copy of the latest backup.
If you want to force an immediate backup (e.g. for a configuration change) you
can accomplish this by clicking *Backup Now*. If multiple backups are not
enabled, each time the configuration is backed up, the backup up file will be
overwritten. Otherwise, the oldest backed up file will be overwritten.
Selecting the *Multiple Backup* option is recommended. If the backup is already
Enabled, go ahead and Disable it, turn on the Multiple Backup option and then
Enable the backup again.
You should enable cross-region replication in AWS when creating your S3 buckets.
This ensures that an S3 bucket remains accessible if there is a regional CSP
failure. The replacement Controller can retrieve and restore its backup file.
## Restoring Your Controller Configuration on Controller UI
Make sure your Controller backup and Controller restore take place in the same CSP (Cloud Service Provider): AWS, Azure, or GCP and share the same basic configuration. For example, an AWS backup can only restore to another AWS Controller.
Note that in the case of AWS backups, an AWS Controller set up with IAM roles
cannot backup and restore to an AWS Controller set up with a secret key, or vice
versa.
### Initialize a New Controller
If you are starting from a new Controller, follow these steps to get started:
1. Log into the Controller with the *admin* username and the default password.
2. Follow the initial steps to get the Controller up and running:
1. Shut down the older Controller.
2. Transfer the IP address to the new Controller.
3. Proceed to configure the new Controller by entering an email address.
4. Change your admin password.
5. Enter or skip the proxy configuration.
6. Allow the upgrade to run.
### Restore Controller Configurations on Controller UI
Once you are past the initial configuration steps:
1. Log into the Controller.
2. Go to **Settings** > **Maintenance** > select the **Backup & Restore** tab.
3. Under the *Restore* section:
* Select the *Cloud Type* for the Location:
* For AWS/ARM:
* If you would like to use an existing account, please make sure you create
one Access Account only with the *exact* Access Account Name that was
used in your previous Controller. Mark the *Use Cloud Account Name*
checkbox and select the account. Otherwise, enter an *Access Key* and
*Secret Key*.
* Enter the *Bucket Name* and *File Name* of the file to restore. The file
name can be obtained from the external storage that you configured to
store your backups. It may display as "CloudN\_\\_save-cloudx-config.enc".
* For Azure:
* Enter the *Subscription ID* and *Directory ID*.
* Enter the *Application Client ID* and *Application Client Secret*
* Enter the *Storage Name*, *Container Name*, and *File Name* of the file
to restore. The file name can be obtained from the external storage that
configured to store your backups. It may display as
"CloudN\_\\_save-cloudx-config.enc".
* For GCP:
* Enter the *Bucket Name*.
* Upload the GCP Project Credentials.
* Enter the *File Name* of the file to restore. The file name can be
obtained from the external storage that configured to store your backups.
It may display as "CloudN\_\\_save-cloudx-config.enc".
* For OCI:
* If you would like to use an existing account, please make sure you create
one Access Account only with the *exact* Access Account Name that was
used in your previous Controller. Mark the *Use Cloud Account Name*
checkbox and select the account. Otherwise, enter a *Tenancy OCID*, *User
OCID*, *Compartment OCID*. Upload an *OCI Private Key*.
* Enter the *Bucket Name*, *Region* and *File Name* of the file to restore.
The file name can be obtained from the external storage that configured
to store your backups. It may display as "CloudN\_\\_save-cloudx-config.enc".
4. Click *Restore*.
AWS S3 allows uploaded backup files to be encrypted in the server side
for more secure storage. The encryption is all done in the AWS S3 server
side. This server side secure storage is in addition to the already
encrypted Aviatrix Controller backups.
Follow the steps below to enable AWS Encrypted backups:
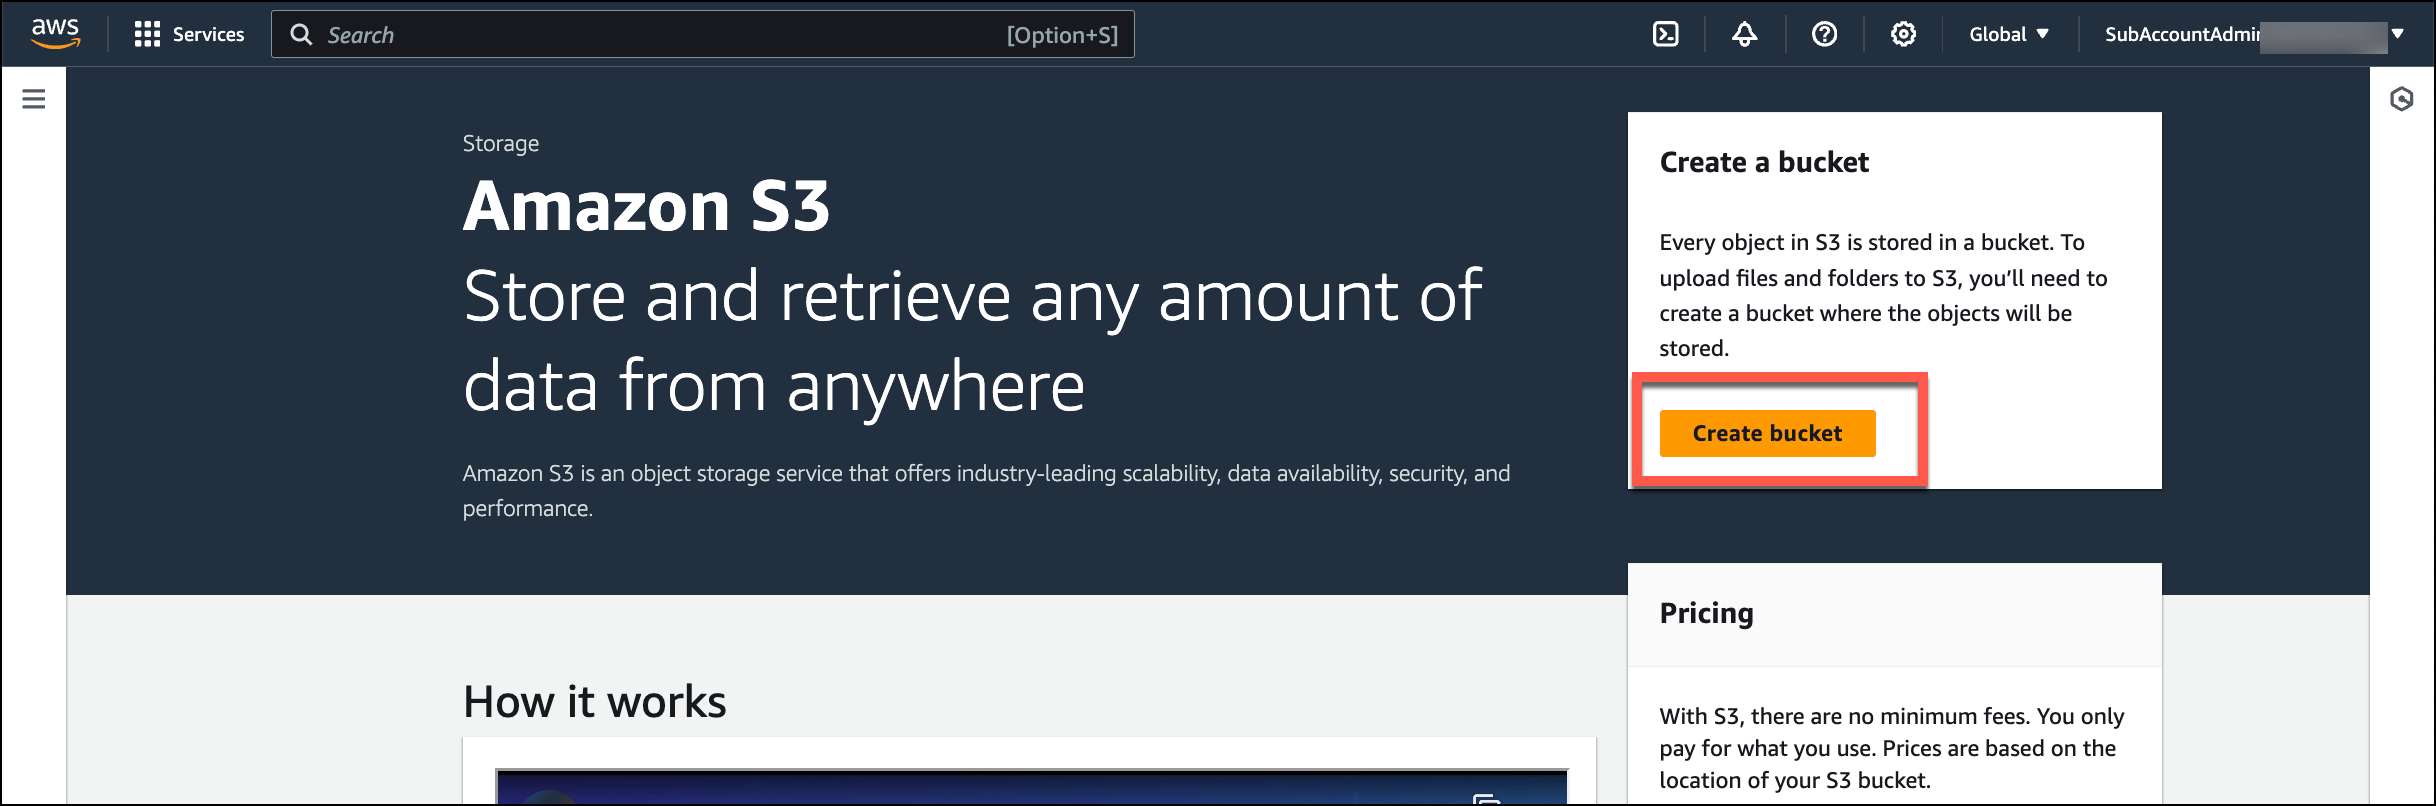
1. Create AWS S3 bucket.
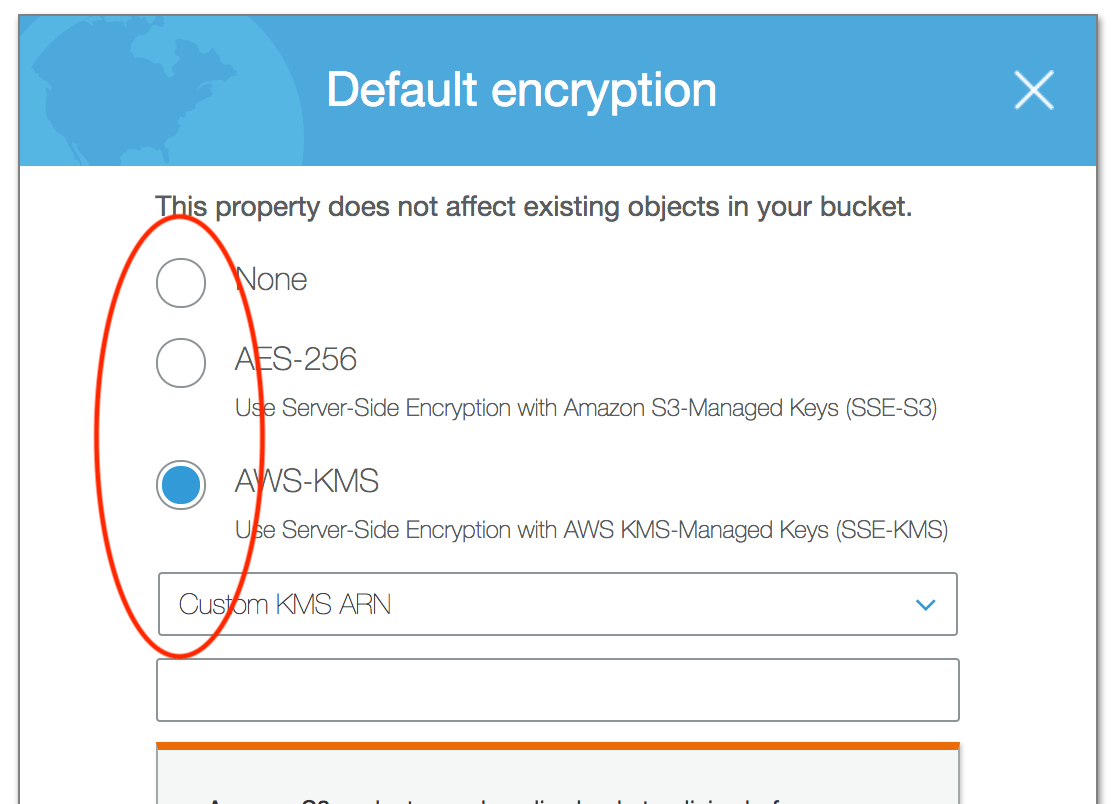
 2. After configuring other bucket properties, configure bucket server side encryption by selecting either **Server-side encryption with AWS Key Management Service keys (SSE-KMS)** or **Dual-layer server-side encryption with AWS Key Management Service keys (DSSE-KMS)**.
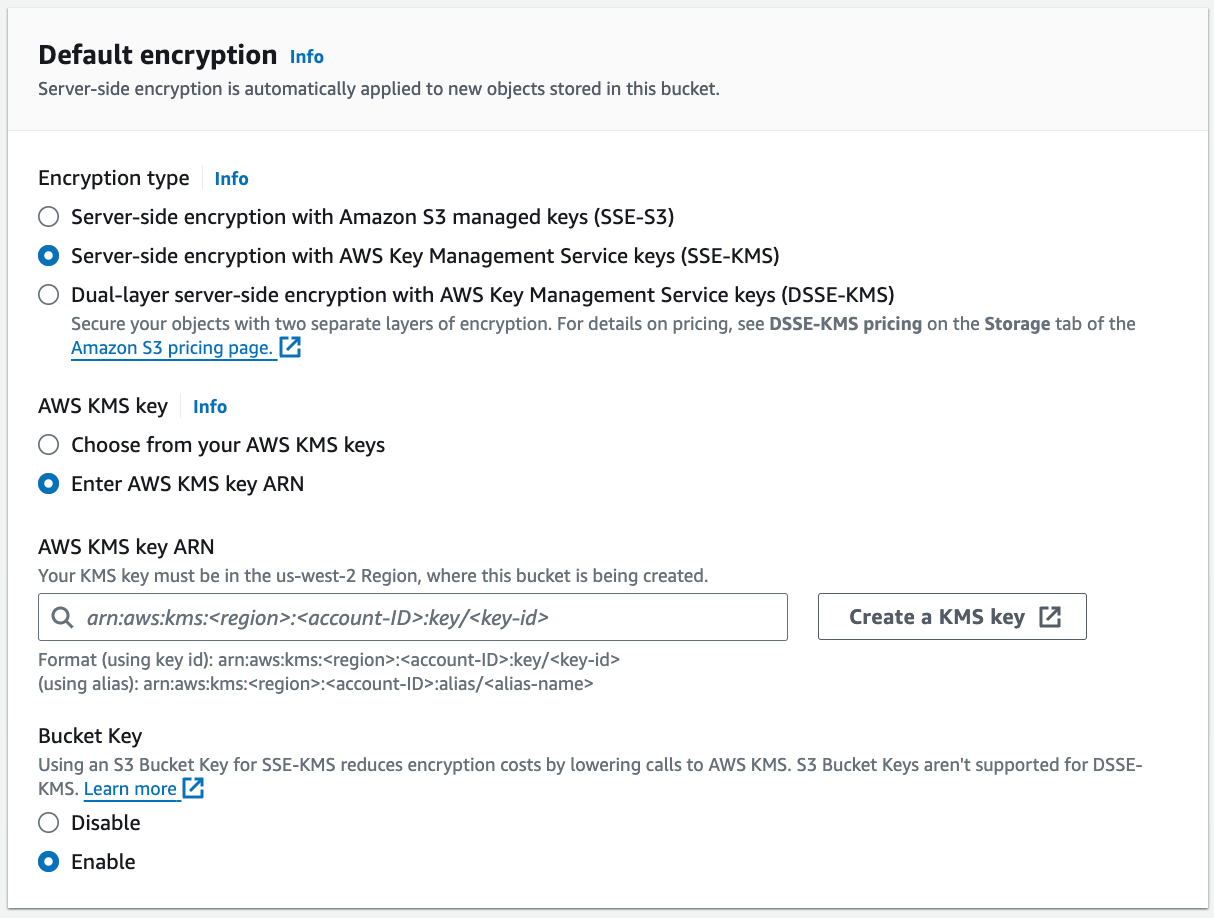
 3. Click **Create a KMS key** to create a new key. A separate tab opens where you can configure and save the key.
4. After the key is saved, go back to the Create bucket tab and enter the key in the **AWS KMS key ARN** field.
5. Click **Create bucket**.
Configure Azure Private Link for secure backups.
When using Azure Private Link for backups:
1. Ensure your Azure account has Private Link enabled.
2. Configure the storage account with Private Endpoint.
3. Update your backup settings to use the Private Link connection.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.