> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Example Configuration for Palo Alto VM-Series in AWS
> You can follow these steps to set up your Palo Alto VM-Series firewall and validate that packets are indeed sent to the VM-Series for VPC-to-VPC inspection.
You can follow these steps to set up your Palo Alto VM-Series firewall and
validate that packets are indeed sent to the VM-Series for VPC-to-VPC
inspection.
You must first have launched a firewall instance in your AWS cloud portal.
## Resetting the VM-Series Password
You must download the access key to change the password for the Palo Alto
VM-Series. You do this from the Security > FireNet tab.
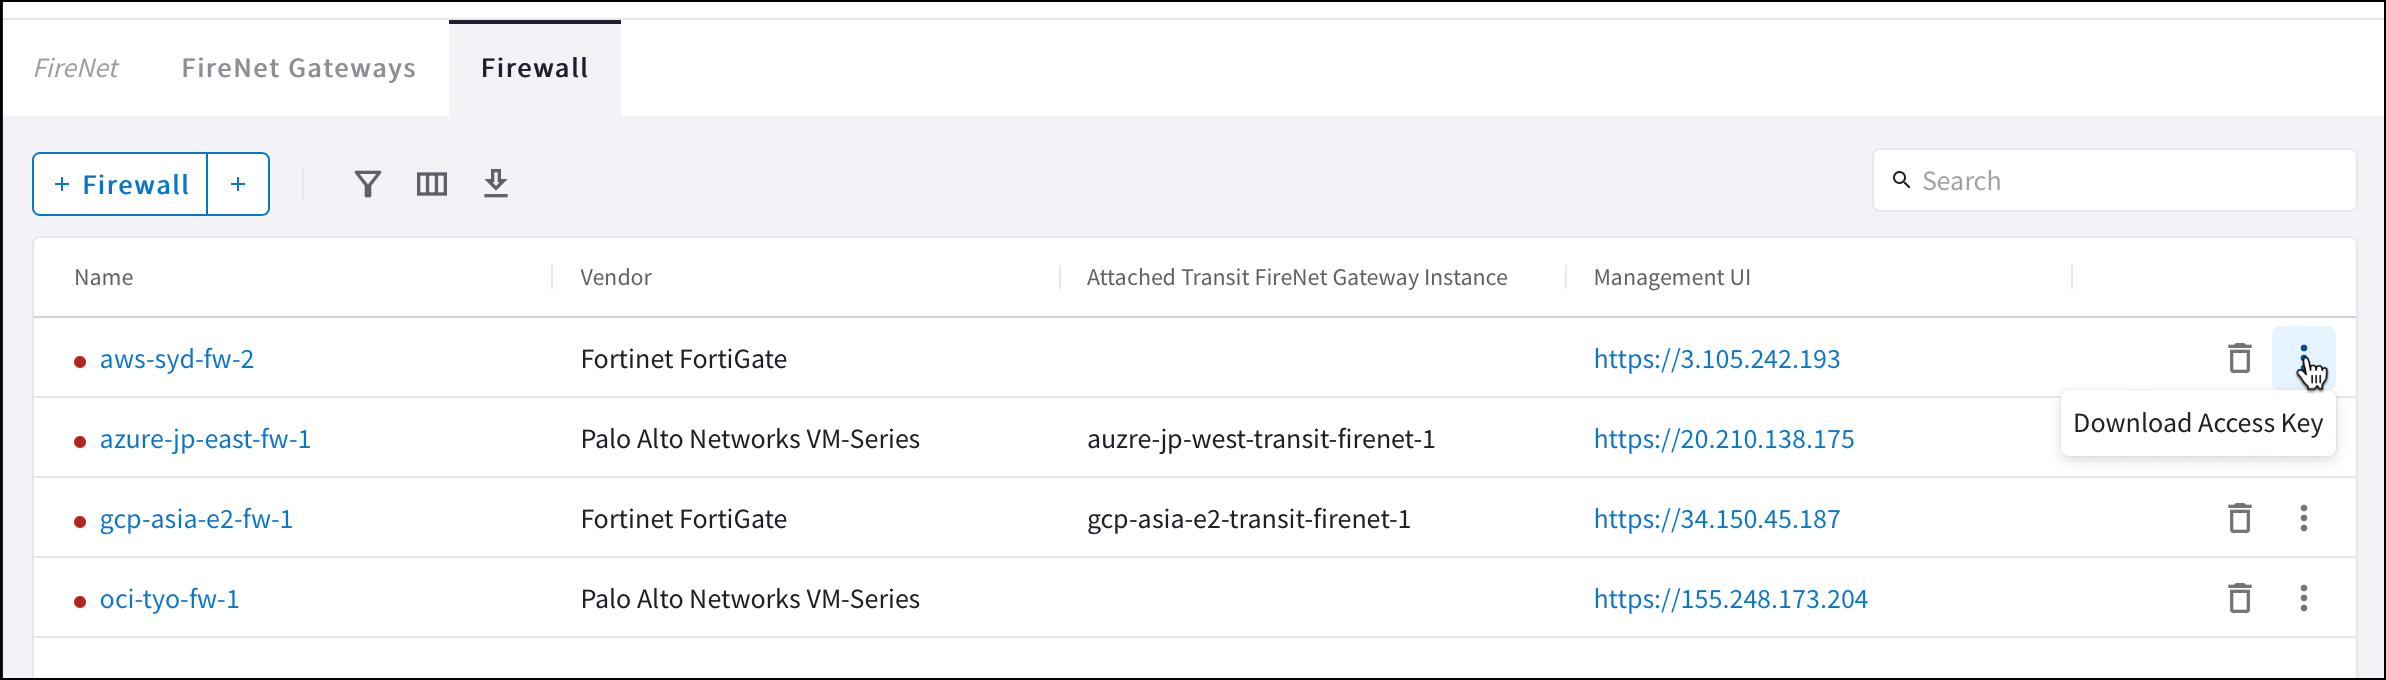 After you download the .pem file, change the file permission to 600. If you
are asked to enter a password during the login, the VM-Series is still not
ready. Wait and try again. It usually takes up to 15 minutes for the VM-Series
to be ready. When the VM-Series is ready, you will no longer be prompted for a
password.
For metered AMI, open a terminal/command prompt and run the following:
```bash theme={null}
ssh -i admin@
configure
set mgt-config users admin password
commit
```
For BYOL, open a terminal/command prompt and run the following:
```bash theme={null}
ssh -i admin@
configure
set mgt-config users admin password
set deviceconfig system dns-setting servers primary
commit
```
You can then terminate the SSH session.
## Logging into the VM-Series
Click the Management UI link on the FireNet tab (shown above) to access the UI
of the Palo Alto VM-Series firewall.
Your login information is "admin" and the password you configured in the
previous section.
## Dynamic Updates
To make sure your firewall is up-to-date, in your firewall UI you can navigate
to Device > Dynamic Updates and click **Check Now**. You can then download and
install the latest versions of Applications and Threat Wildfire updates.
## Configuring VM-Series Ethernet 1/1 with WAN Zone
WAN is Wide Area Network.
Ethernet 1/1 is a data plane interface assigned to the WAN zone. Provides
external access to the Internet.
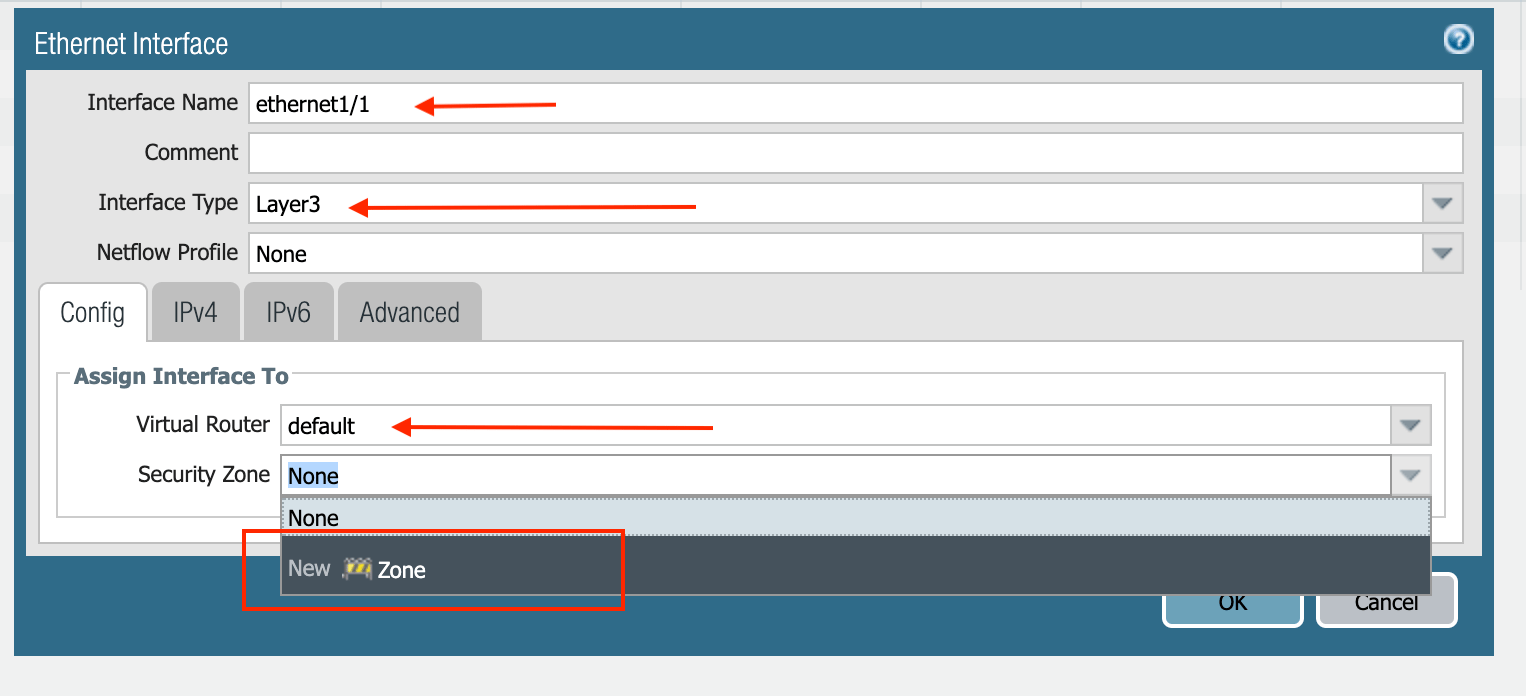
1. Once logged in, click on the Network tab to see a list of ethernet
interfaces. Click ethernet1/1 and configure as per the following screenshot.
2. Select the Network tab.
3. Click ethernet1/1.
4. Select layer3 for Interface Type.
5. Select the Config tab in the popup Ethernet Interface window.
6. Select default for Virtual Router at the Config tab.
7. Click New Zone for Security Zone to create a WAN zone.
8. At the next popup screen, name the new zone WAN and click OK.
 9. Select the IPV4 tab in the popup Ethernet Interface window.
10. Select DHCP Client.
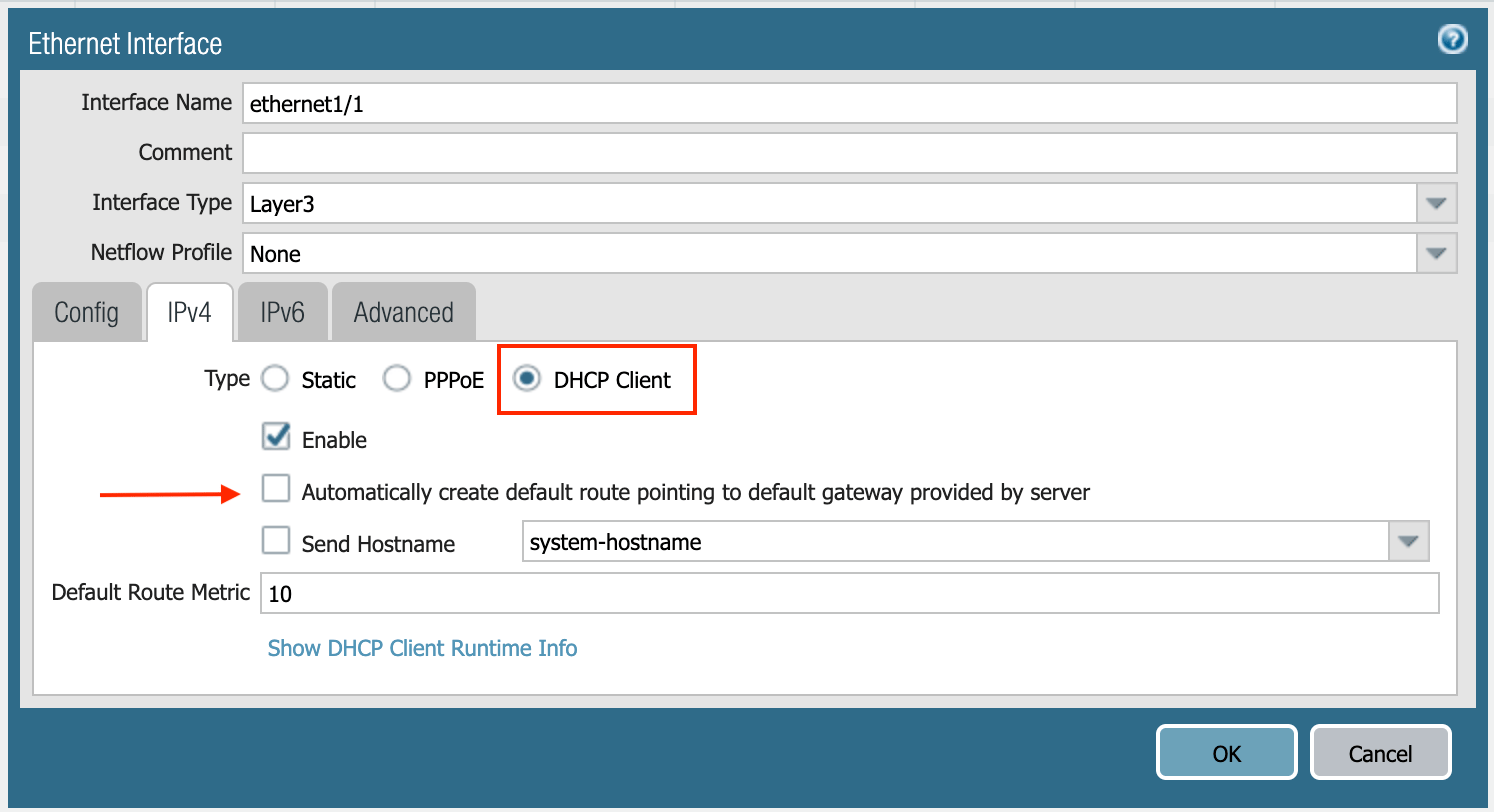 11. Clear the Automatically create default route pointing to default gateway
provided by server checkbox as shown below.
12. Click Commit. Once Commit is complete, you should see the Link State turn
green at the Network page for ethernet1/1.
## Configuring VM-Series Ethernet 1/2 with LAN Zone
1. Repeat the steps from Configuring VM-Series ethernet1/1 with WAN Zone section
above for ethernet1/2. Name the new zone LAN.
2. Click Commit. Once Commit is complete, you should see the Link State turn
green at the Network page for ethernet1/2.
## Configuring Allow Outbound Policies
1. Navigate to Policies > Security > Click Add.
2. Name the policy "Outbound," then select the Source tab.
3. Select LAN zone > Destination tab.
4. Select WAN zone > Click OK.
## Configuring NAT for Egress
Complete the following steps to enable NAT, to test Egress of the firewall.
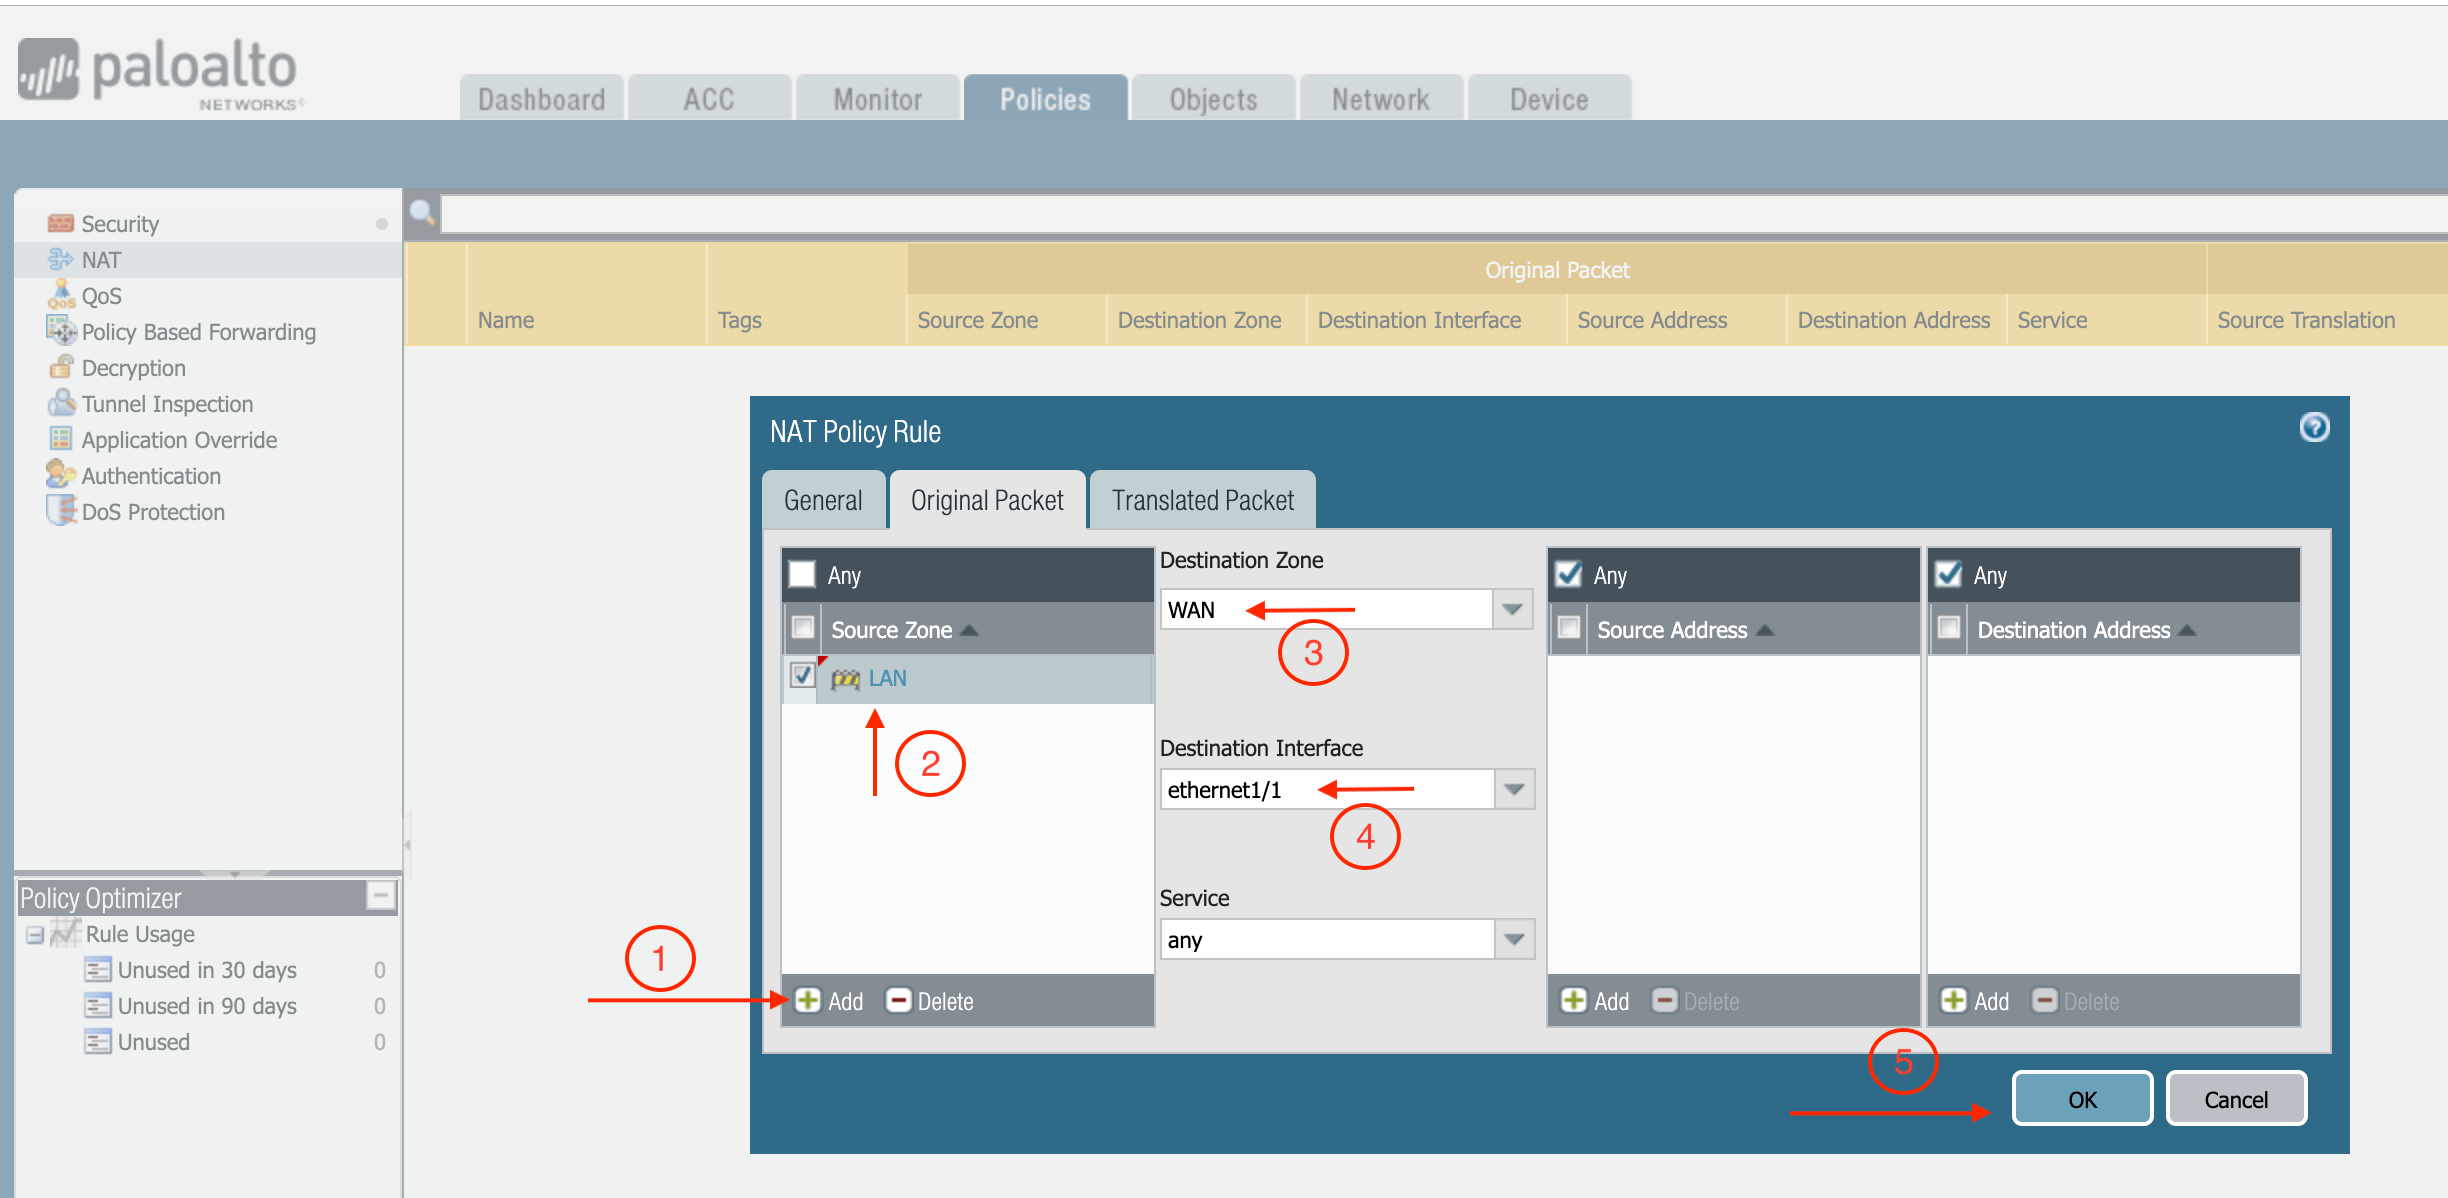
1. Navigate to Policies > NAT and click Add.
2. Select the General tab and name the policy.
3. Click Original Packet.
4. At Source Zone, click Add, and select LAN.
5. At Destination Zone, select WAN.
6. At Destination Interface, select Ethernet1/1, as shown below.
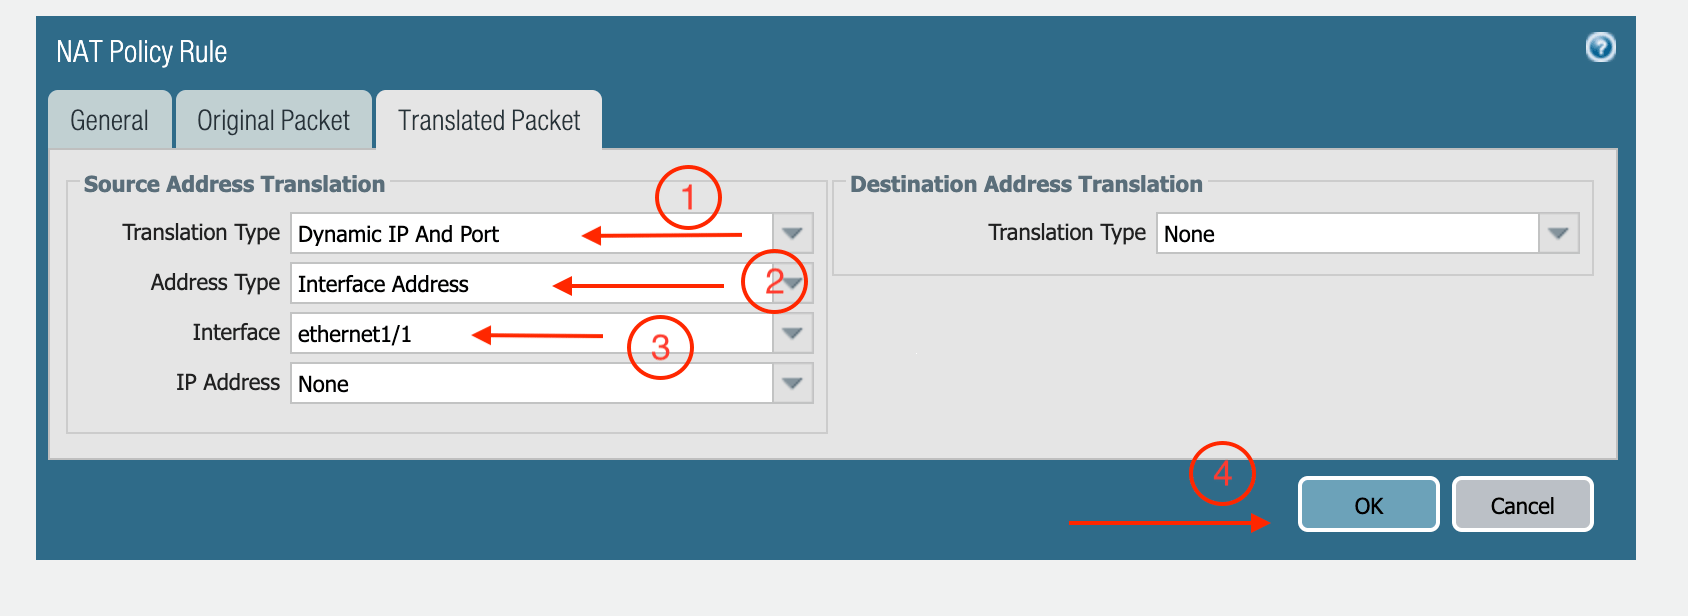
 7. Click Translated Packet. At Translation Type, select Dynamic IP And Port.
8. At Address Type, select Interface Address.
9. At Interface, select ethernet1/1, as shown below.
 ## Setting up API Access
Follow the instructions in
[Setting up API Access to Palo Alto Networks VM-Series](https://legacy.docs.aviatrix.com/documentation/latest/security/paloalto-api-setup.html)
to enable API access.
## View Traffic Log
You can view if traffic is forwarded to the firewall instance by logging in to
the VM-Series console.
1. Click Monitor.
2. Start pinging packets from one Spoke VPC to another Spoke VPC where one or
both of Network Domains are connected to Firewall Network Domain.