> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.

# Field Notices

> These field notices are provided as a service to our customers to proactively update them on major issues. This service is provided without any changes in our SLA. The information in this field notice will be updated as we learn more.

These field notices are provided as a service to our customers to proactively
update them on major issues. This service is provided without any changes in our
SLA. The information in this field notice will be updated as we learn more.

<a id="field-notice-57" />

## 57. Field Notice

### New CDN IPs Added to cdn.aviatrix.com – Action Required to Allow IPs on Edge Management Interface

**Date**: June 3, 2026

**Severity**: High

### Issue Description

Aviatrix has added two new IP addresses (Hong Kong) to the FQDN
`cdn.aviatrix.com` for the APAC region. Customers who restrict outbound access
on their Edge Management interface by IP allowlist must add these new IPs to
their firewall or security group rules to maintain uninterrupted connectivity to
Aviatrix CDN services.

**New IPs added to `cdn.aviatrix.com`:**

* `18.162.118.170`
* `16.162.153.248`

### Who is Impacted?

All Aviatrix customers who use Aviatrix Edge Gateways in the APAC region with
IP-based allowlists or firewall rules on the **Edge Management** interface that
control outbound access to external services.

### Symptoms

If the new CDN IPs are not allowed on the Edge Management interface, you may
observe:

* Edge Gateway software or image downloads from `cdn.aviatrix.com` failing or
  timing out, resulting in upgrade failures.

### Trigger

This issue is triggered when the Edge Management interface attempts to reach
`cdn.aviatrix.com` and DNS resolves to one of the two newly added IPs
(`18.162.118.170` or `16.162.153.248`), which are not yet present in the
customer's IP allowlist.

### Impact

CDN-dependent operations on the Aviatrix Edge Gateway — including software
upgrades, image pulls, and CDN-hosted resource retrieval — may fail or be
unavailable until the new IPs are permitted on the Edge Management interface.
There is no impact to data plane traffic or existing tunnels.

### Actions Required to Be Taken

Customers with IP-based allowlists on their Edge Management interface must add
the two new IPs before their next CDN access attempt to avoid disruption.

Add the CDN IPs to the allowlist on your Edge Management interface firewall or
security group rules:

* `18.162.118.170`
* `16.162.153.248`

For the complete and up-to-date list of all IP addresses and domains that
Aviatrix products require access to, refer to the Aviatrix Support article:
[Aviatrix Products – Required Access for External Sites](https://aviatrix.zendesk.com/hc/en-us/articles/4417312119437-Aviatrix-Products-Required-Access-for-External-Sites).

### What to Do If Impacted

If you are already experiencing upgrade failures, immediately add
`18.162.118.170` and `16.162.153.248` to the outbound allowlist on your Edge
Management interface.

<a id="field-notice-56" />

## 56. Field Notice (FN-2026-AZ-001)

### Azure MANA Driver Compatibility – Action Required for All Azure Gateways

**Date**: May 28, 2026

**Field Notice Last Updated**: 24 August 2026

**Severity**: High

<Info>
  **Update, 6 July 2026: MANA long-term fix now available.** The MANA-compatible
  Aviatrix gateway releases are now GA: **8.0.70, 8.1.40, 8.2.20, 9.0.10, and
  all subsequent releases (10.0.1 and future releases)**. Perform a gateway
  image upgrade to the patched release for your train (8.0.x → 8.0.70, 8.1.x →
  8.1.40, 8.2.x → 8.2.20, 9.0.x → 9.0.10). If you are already on 10.0.1 or a
  later release, MANA support is included by default — no patch upgrade is
  required. Keep the `LegacyVMNVA` tag applied through the upgrade, then remove
  the tag after the patched image is verified healthy. See [Long-Term Fix:
  MANA-Compatible Images and Upgrade
  Groups](#long-term-fix-mana-compatible-images-and-upgrade-groups) for the
  recommended sequence.
</Info>

<Warning>
  **Immediate action required.** Microsoft has begun deploying MANA hardware
  across Azure. Any Aviatrix gateway that is redeployed, scaled, image-upgraded,
  or service-healed in a MANA-enabled region may land on hardware that current
  gateway images do not fully support, resulting in performance degradation.
  **Apply the `LegacyVMNVA` opt-out tag to all Aviatrix gateway subscriptions
  now.**
</Warning>

Aviatrix has independently validated the opt-out process and the efficacy of the
tag against shipping gateway images (8.0.60, 8.1.30, 8.2.10, 9.0.0). The tag
survives image upgrades and gateway lifecycle operations.

**Active rollout regions. Schedule maintenance windows and re-apply
immediately:**

| Date         | Region          | Status    |
| ------------ | --------------- | --------- |
| May 26, 2026 | West Central US | Live      |
| May 27, 2026 | East Asia       | Live      |
| May 28, 2026 | Norway West     | Scheduled |
| May 29, 2026 | Spain Central   | Scheduled |

Additional regions announced via Azure Service Health on May 29, 2026. Tracking
ID: **5RWW-K4G**.

### Summary

Microsoft is rolling out MANA (Microsoft Azure Network Adapter) hardware across
Azure regions starting May 26, 2026. All Aviatrix gateways running on currently
shipping software may experience intermittent performance degradation if placed
on MANA hardware. Aviatrix has a validated short-term fix available today and a
permanent fix now available as of June 23, 2026 in gateway releases 8.0.70,
8.1.40, 8.2.20, 9.0.10, and all subsequent releases (10.0.1 and future
releases).

### What To Do

1. **Apply the `LegacyVMNVA` tag now** (validated by Aviatrix). Assign the
   built-in Azure Policy (`e87a87f5-e6dd-4919-be21-abb0a4ea4630`) at Management
   Group or Subscription scope. Set the **Tag Value** parameter to `true` (not
   blank).

2. **Activate the tag in a maintenance window, starting with your active rollout
   regions.** The tag does not take effect until the VM is re-applied or
   stop/deallocated/started. Schedule maintenance windows in the currently
   active rollout regions (West Central US, East Asia, Norway West, Spain
   Central) and re-apply immediately. Through Aviatrix's partnership with
   Microsoft, Microsoft has shared that `az vm reapply` may cause a VM reboot or
   redeployment on some hosts. Perform this action in a planned maintenance
   window. Both `reapply` and stop-deallocate-start achieve the same outcome.
   This field notice will be updated with additional guidance as Microsoft
   delivers improvements to the reapply process.

3. **Image upgrade to the MANA-compatible release** (now GA as of June 23, 2026:
   8.0.70, 8.1.40, 8.2.20, 9.0.10, and all subsequent releases including 10.0.1
   and future releases). Aviatrix CoPilot's **Upgrade Groups** feature rolls out
   the upgrade fleet-wide with automatic failover and fail-back between HA
   pairs. No user-managed per-gateway maintenance windows are required.

### Issue Description

Microsoft is progressively deploying MANA hardware, the next-generation network
adapter for Azure VMs, across Azure data centers. MANA replaces the Mellanox
(mlx5) SR-IOV adapters used by prior VM generations and is required for all new
Azure Boost / Gen 6 SKUs.

Aviatrix gateways on all currently shipping releases (8.0.x, 8.1.x, 8.2.x,
9.0.x, and earlier) are not yet MANA-compatible. Gateway VMs placed on MANA
hardware may exhibit intermittent performance degradation. Gateway versions
below 8.0 are End of Life and will not receive a MANA-compatible patch.

### Scope: Which Aviatrix Components Are Affected?

This field notice applies to all Aviatrix gateway types running on Microsoft
Azure across Intel v5, V6/Cobalt 100, and V2-V4 VM families, including **Transit
Gateways, Spoke Gateways, Specialty Gateways, and their HA peers**. See
[Microsoft's VM family list](https://learn.microsoft.com/en-us/azure/virtual-network/accelerated-networking-mana-existing-sizes)
for the full transition matrix.

**Aviatrix Controller and CoPilot instances running in Azure are not affected by
this issue.** This field notice applies only to Aviatrix gateway VMs.

### When Am I Exposed?

A gateway VM is exposed to MANA placement whenever it is provisioned,
stop/deallocated and restarted, redeployed, image-upgraded, scaled, or
service-healed in a MANA-enabled region. This applies whether the action is
initiated by:

* **Azure**: planned maintenance, host health events, hardware failure.
* **Aviatrix Controller or CoPilot**: image upgrade, scaling, HPE or BGPoLAN
  enable/disable.
* **An Azure administrator out-of-band**: manual stop/start from the portal or
  CLI.

Applying the `LegacyVMNVA` tag at subscription or management-group scope
protects every one of these paths once activated.

For live regional rollout status, monitor Azure Service Health (Tracking ID:
**5RWW-K4G**).

### Short-Term Fix: `LegacyVMNVA` Opt-Out Tag

<Warning>
  Schedule a maintenance window in your active rollout regions and re-apply
  immediately. Do not wait. Gateways in active regions (West Central US, East
  Asia, Norway West, Spain Central) are at immediate risk of landing on MANA
  hardware on the next lifecycle event.
</Warning>

Through Aviatrix's partnership with Microsoft, Microsoft has shared that
`reapply` may still cause a reboot or redeployment on some hosts and should be
performed during a planned maintenance window. Plan this as a maintenance event
for both `reapply` and stop-deallocate-start.

Aviatrix is actively working with Microsoft. This field notice will be updated
with additional information to reduce disruption as Microsoft delivers
improvements to the reapply process, including the forthcoming VM
impact-assessment tooling (see FAQ).

Aviatrix has independently validated the opt-out process and the efficacy of the
`LegacyVMNVA` tag against shipping gateway images on 8.0.60, 8.1.30, 8.2.10, and
9.0.0. The tag survives image upgrades and gateway lifecycle operations. Apply
it now.

1. **Assign the Azure Policy.** Apply policy ID
   `e87a87f5-e6dd-4919-be21-abb0a4ea4630` at Management Group or Subscription
   scope. Set the **Tag Value** parameter to `true` (Microsoft's default is
   blank; Aviatrix requires a non-empty value). Aviatrix is on Microsoft's
   [recognized NVA publisher list](https://learn.microsoft.com/en-us/azure/virtual-network/accelerated-networking-mana-network-virtual-appliance-opt-out#network-virtual-appliances).
   The policy tags Aviatrix gateway VMs automatically.

2. **Activate the tag on existing VMs in active rollout regions first** during a
   maintenance window using either:

   * `az vm reapply` (preferred; Microsoft has shared with Aviatrix that this
     method is intended to reduce operational impact compared with
     stop/deallocate/start)
   * Stop-deallocate-start (predictable maintenance event)

   Both methods register the tag and update Azure's placement behavior. Azure
   Policy remediation cannot trigger `reapply` directly. Use Azure CLI,
   PowerShell, REST API, or SDK for bulk execution. Once active regions are
   covered, schedule maintenance windows for the remaining regions ahead of
   Microsoft's August 1, 2026 global cutover.

<Warning>
  Do not apply the `LegacyVMNVA` tag directly to gateway VMs via the Azure
  Portal, CLI, or PowerShell as a standalone action. These out-of-band methods
  may not survive gateway lifecycle operations. Use Azure Policy.
</Warning>

### Long-Term Fix: MANA-Compatible Images and Upgrade Groups

The MANA-compatible Aviatrix gateway releases are now GA as of **June 23,
2026**: **8.0.70, 8.1.40, 8.2.20, 9.0.10, and all subsequent releases (10.0.1
and future releases)**. Perform a gateway image upgrade to the patched release
for your train. If you are already on 10.0.1 or a later release, MANA support is
included by default — no patch upgrade is required.

The **Upgrade Groups** feature in Aviatrix CoPilot rolls out the upgrade
fleet-wide on your behalf, with **automatic failover and fail-back between HA
pairs** at each step. CoPilot handles ordering, health checks, and rollback. You
do not need to plan per-gateway maintenance windows.

**Recommended upgrade sequence:**

1. **Keep the `LegacyVMNVA` tag applied** through the upgrade so gateways stay
   off MANA hardware while still running a pre-patch image.
2. **Upgrade the gateway image** to the patched release for your train using
   Aviatrix CoPilot Upgrade Groups.
3. **Verify** that gateways are healthy and running the patched release.
4. **Remove the `LegacyVMNVA` tag.** After the patched image is verified
   healthy, remove the tag and gateways return to a fully MANA-supported
   configuration. Removing the tag alone does not move the gateway; a `reapply`
   (`az vm reapply` or stop-deallocate-start) is required for the VM to move
   onto MANA hardware, and whether it does so depends on SKU and region
   availability. Because the gateway is now on a MANA-compatible image, this
   transition is safe.

If you prefer not to upgrade yet, the `LegacyVMNVA` opt-out tag remains a valid
alternative. Keep the tag applied and your gateways stay off MANA hardware until
you are ready to upgrade. The tag is honored through May 31, 2027.

<Tip>
  **Aviatrix strongly recommends completing this upgrade well in advance of
  Microsoft's May 31, 2027 tag-expiry deadline.** The tag is a temporary
  mechanism. Once it expires, any VM lifecycle event in any region will land the
  gateway on MANA hardware. Plan to be on MANA-compatible images months ahead of
  the deadline, not days.
</Tip>

| Current Version   | Target Patched Release (GA June 23, 2026)                    |
| ----------------- | ------------------------------------------------------------ |
| 7.2.x and earlier | End of Life. Upgrade to a supported 8.x+ release.            |
| 8.0.x             | Image upgrade to **8.0.70**                                  |
| 8.1.x             | Image upgrade to **8.1.40**                                  |
| 8.2.x             | Image upgrade to **8.2.20**                                  |
| 9.0.x             | Image upgrade to **9.0.10**                                  |
| 10.0.1 and later  | MANA support included by default. No patch upgrade required. |

For release availability and detailed changelogs, see the

<a href={"/docs/enterprise/" + "10.1" + "/reference/release-notices/release-notes/controller-images/index"}>Aviatrix Controller and Gateway Image Release Notes</a>
.

### Important Dates

| Date               | Event                                                                                                                                                                   |
| ------------------ | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| May 26, 2026       | MANA rollout begins in first four regions                                                                                                                               |
| **June 23, 2026**  | **Aviatrix MANA-compatible releases GA (8.0.70, 8.1.40, 8.2.20, 9.0.10, and all subsequent releases including 10.0.1 and later); Upgrade Groups available in CoPilot.** |
| **August 1, 2026** | **Microsoft global cutover. All V2-V5 family VMs may land on MANA hardware in all regions.**                                                                            |
| **May 31, 2027**   | **Microsoft disables the `LegacyVMNVA` opt-out tag. All Azure gateways must be on a MANA-compatible release by this date.**                                             |

### Frequently Asked Questions

**How can I verify if my gateway is already running on MANA hardware?**

Contact [Aviatrix Support](https://support.aviatrix.com) and reference this
field notice. Support can verify the current hardware configuration of your
gateways.

**Does the `LegacyVMNVA` tag protect new (greenfield) gateway deployments?**

Azure Policy applies the tag at VM creation time. Aviatrix is awaiting
Microsoft's confirmation that the tag is applied early enough in the
provisioning pipeline to influence initial host placement. This notice will be
updated once confirmed. Azure Policy remains the recommended approach today.

**Reapply vs. stop-deallocate-start: which should I use?**

Both methods activate the tag and produce the same outcome. Use `reapply` for
lower operational impact during a maintenance window. Use stop-deallocate-start
if you prefer a predictable maintenance event or if `reapply` fails on a
specific VM.

Through Aviatrix's partnership with Microsoft, Microsoft has shared that
`reapply` is intended as an alternative to stop/deallocate/start that reduces
operational impact while achieving the same outcome, but that it may still cause
a reboot or redeployment on some hosts and should be used during planned
maintenance windows. Microsoft has not yet published dedicated reapply
documentation. Aviatrix will link to it here once it is available.

**Is there tooling to determine whether `reapply` will reboot a specific VM
before I run it?**

Through Aviatrix's partnership with Microsoft, Microsoft has shared that two
pieces of tooling are in active development. GA dates have not been provided:

1. A solution to identify VMs that may be impacted by `reapply` actions (results
   will be point-in-time).
2. A query to identify VMs that have changes staged that would cause a reboot
   under `reapply`.

Until Microsoft releases these, treat every `reapply` as potentially disruptive
and schedule a maintenance window. This field notice will be updated when the
tooling becomes available so you can reduce maintenance-window impact on later
region waves.

**What about V6 / Cobalt 100 SKUs?**

V6 SKUs, including MANA compatibility, are supported starting with release
**10.0.1**. Performance benchmarking for V6 SKUs is available as of release
**10.1**. If you are running gateways today on V2-V5 family SKUs, follow the
short-term and long-term fix guidance in this notice.

**When does the `LegacyVMNVA` tag stop working?**

May 31, 2027. All Azure gateways must be on a MANA-compatible Aviatrix release
before that date. Aviatrix strongly recommends completing the upgrade to
MANA-compatible images well in advance of May 31, 2027. Do not run the deadline
close. Aviatrix Upgrade Groups in CoPilot handles the fleet-wide rollout of the
patched images (GA June 23, 2026: 8.0.70, 8.1.40, 8.2.20, 9.0.10, and all
subsequent releases including 10.0.1 and future releases), making it
straightforward to migrate the entire fleet on your timeline rather than at the
last minute.

**Are Aviatrix Controller and CoPilot affected?**

No. The MANA driver update applies to the data plane only. Aviatrix Controller
and CoPilot do not run data plane functions and are not affected by this issue.

### Additional Information

* [Microsoft Azure MANA Overview](https://learn.microsoft.com/en-us/azure/virtual-network/accelerated-networking-mana-overview)
* [MANA Support for Existing VM Sizes](https://learn.microsoft.com/en-us/azure/virtual-network/accelerated-networking-mana-existing-sizes)
* [MANA NVA Opt-Out (Azure Policy)](https://learn.microsoft.com/en-us/azure/virtual-network/accelerated-networking-mana-network-virtual-appliance-opt-out)
* Azure Service Health, Tracking ID: **5RWW-K4G**

### Support

If you have questions about this field notice or need assistance planning your
upgrade, contact Aviatrix Support:

* **Support Portal**: [support.aviatrix.com](https://support.aviatrix.com)
* **Documentation**: [docs.aviatrix.com](https://docs.aviatrix.com)

<a id="field-notice-55" />

## 55. Field Notice

### CoPilot Appliance Version 2 (Ubuntu 16) and Earlier – End of Software Updates

**Date**: 16 March 2026

**Severity**: High

### Issue Description

CoPilot deployments running Appliance Version 1 or Appliance Version 2 are built
on Ubuntu 16.04 LTS, which has reached end-of-life (EOL) with Canonical and no
longer receives security patches or updates.

To ensure continued access to software updates and maintain a secure, supported
environment, customers running these appliance versions must migrate to CoPilot
Appliance Version 3.

CoPilot instances running Appliance Version 1 or Appliance Version 2 will
continue to operate, but they will no longer receive future software updates
once support ends.

The tentative release date for CoPilot version 4.32.0 is the week of April
20, 2026.

### Who is impacted?

Customers running Aviatrix CoPilot on Appliance Version 2 (Ubuntu 16.04) or
earlier, including Appliance Version 1.

Customers can verify their CoPilot appliance version directly from the CoPilot
UI. Navigate to the top-right corner of the CoPilot UI and click on the dropdown
(triangle) icon next to the user/profile icon to view the appliance version
details.

### Required Actions

Customers running CoPilot Appliance Version 1 or Appliance Version 2 must
complete migration to Appliance Version 3 at the earliest, or before **April 20,
2026**, in order to receive CoPilot version 4.32.0 and future software updates
and security fixes.

#### Migration Instructions

To migrate your CoPilot instance to Appliance Version 3, please follow the
instructions in the Aviatrix documentation:
[Migrate CoPilot to Appliance Version 3](https://docs.aviatrix.com).

We strongly recommend completing this migration **prior to the CoPilot 4.32.0
release (week of April 20, 2026)** to avoid disruption to future upgrade paths.

If you have questions or require assistance with the migration process, please
contact [Aviatrix Support](https://support.aviatrix.com).

<Note>
  * Customers who do not migrate to Appliance Version 3 before the CoPilot
    4.32.0 release will remain on their current installed version.
  * Customers on unmigrated appliances will not receive future software updates,
    security patches, or feature enhancements from Aviatrix.
</Note>

<a id="field-notice-54" />

## Field Notice 54

### CloudFormation Template Version Guidance for Aviatrix Controller High Availability in AWS

**Date**: 26 January 2026

**Severity**: Medium

### Issue Description

Aviatrix Engineering has identified a version compatibility issue between AWS
Controller High Availability (HA) CloudFormation templates and Aviatrix
Controller software versions.

Using an incompatible CloudFormation template version may result in unsupported
or unstable HA deployments.

### Who is impacted?

Customers deploying Aviatrix Controller High Availability (HA) on AWS using
CloudFormation templates that are incompatible with their Controller software
version.

Impacted scenarios include:

* Controllers running 7.1 or earlier deployed using CloudFormation template v3
* Controllers running 7.2 or later deployed using CloudFormation template v2

### Required Actions

Customers must use the correct CloudFormation template version based on their
Controller software version.

#### Controllers 7.1 and Earlier

Use CloudFormation template **v2**:

[https://aviatrix-cloudformation-templates.s3.us-west-2.amazonaws.com/aviatrix-aws-existing-controller-ha.json](https://aviatrix-cloudformation-templates.s3.us-west-2.amazonaws.com/aviatrix-aws-existing-controller-ha.json)

Follow the steps below if currently deployed using template v3:

1. Delete the existing HA CloudFormation stack created using template v3.
2. Re-deploy Controller HA using template v2.
3. After upgrading the Controller to the latest 7.2 release, customers may
   migrate to template v4.

#### Controllers 7.2 and Later

Customers may use CloudFormation template v3 or later.

**Recommended:** Use CloudFormation template **v4**, which includes additional
security enhancements.

* v3 template:
  [https://aviatrix-cloudformation-templates.s3.us-west-2.amazonaws.com/aviatrix-aws-existing-controller-ha-v3.json](https://aviatrix-cloudformation-templates.s3.us-west-2.amazonaws.com/aviatrix-aws-existing-controller-ha-v3.json)

* v4 template (recommended):
  [https://aviatrix-cloudformation-templates.s3.us-west-2.amazonaws.com/aviatrix-aws-existing-controller-ha-v4.json](https://aviatrix-cloudformation-templates.s3.us-west-2.amazonaws.com/aviatrix-aws-existing-controller-ha-v4.json)

Follow the step below:

1. If currently deployed using template v3, upgrade directly to v4 using a
   CloudFormation stack update.
   * There is no requirement to wait for Controller 8.x.
   * Template v4 is fully supported on Controller versions 7.2 and above.

<Note>
  * Controller HA CloudFormation templates v3 and earlier are deprecated, except
    where version requirements mandate v2 for Controllers 7.1 and earlier.
  * Documentation under **Controller HA for AWS** has been updated to reflect
    correct template usage.
  * Template v4 resolves an issue in v3 where the Lambda function URL was
    publicly accessible by restricting access to VPC internal endpoints.
</Note>

<a id="field-notice-53" />

## 53. Field Notice

### Aviatrix Controllers, Gateways and CoPilot in Azure - Basic SKU Public IP Address discontinuation by Azure

**Date**: 16 July 2025

**Severity**: High

### Issue Description

Azure announced the retirement of Basic SKU public IP addresses will occur on
September 30, 2025. To ensure uninterrupted service, upgrade to Standard SKU
public IP addresses. More details can be found in Azure's official announcement,
see
[Azure Updates](https://azure.microsoft.com/en-us/updates?id=upgrade-to-standard-sku-public-ip-addresses-in-azure-by-30-september-2025-basic-sku-will-be-retired).

### Who is impacted?

All customers using the Aviatrix Controller, Gateways, or CoPilot UI in Azure
using Basic SKU public IP addresses.

### Required Actions

Upgrade your Basic SKU public IP addresses to Standard SKU IP addresses on your
Aviatrix Controller, Gateways, or CoPilot UI in Azure by **September 30, 2025**,
to avoid service disruption.

#### Aviatrix Controller with Basic SKU public IP address in Azure

1. **Stop the Aviatrix Controller VM**. This is a mandatory step to avoid
   traffic disruption. From the Azure portal, stop the Aviatrix Controller VM to
   prevent traffic disruption.

2. **Upgrade Public IP Address**. Follow Azure's instructions to upgrade the
   Basic SKU public IP address to a Standard SKU public IP address. For more
   information, see
   [Upgrade a public IP address using the Azure portal, Azure CLI, or Azure PowerShell](https://learn.microsoft.com/en-us/azure/virtual-network/ip-services/public-ip-upgrade?tabs=azureportal#upgrade-public-ip-address).

3. Associate Public IP Address with Controller VM. After upgrading, associate
   the new Standard SKU public IP address with the Aviatrix Controller VM.

4. **Start the Aviatrix Controller VM**. After the previous steps are completed,
   start the Aviatrix Controller VM from the Azure portal.

**Aviatrix CoPilot VM with Basic SKU public IP address in Azure**. Follow
Azure's instructions and upgrade to Standard SKU public IP address.

**Aviatrix Gateway with Basic SKU public IP address in Azure**. Follow Azure's
instructions and upgrade to Standard SKU public IP address.

<Note>
  Any gateway deployed in Azure after June 2020 including releases v6.0, v6.1
  are deployed by Aviatrix with Standard SKU IP addresses. If your gateway has
  been deployed before June 2020, you might either have to rebuild the gateway
  or perform an image\_upgrade of the Gateway while Aviatrix Controller is
  running version 7.2.5090 or 8.0.0 and the software will automatically upgrade
  the public IP address SKU from Basic to Standard.
</Note>

<a id="field-notice-52" />

## 52. Field Notice

### IPSec Tunnel Flaps on Aviatrix Transit Gateways with High Tunnel Count (<a href={"/docs/enterprise/" + "10.1" + "/reference/release-notices/release-notes/controller/controller-rn-8.0.0#\_corrected_issues_in_aviatrix_release_8_0_0"}>AVX-62067</a>)

*Date*: 10 July 2025

*Severity*: High

### Issue Description

Aviatrix Transit Gateways with a large number of tunnels and running for a long
time could encounter an issue where the IPSec process becomes unresponsive
leading to all IPsec tunnels going into a DOWN state. The cause of this is an
internal counter reaching its maximum value and overflowing. To recover, the
transit gateway needs to be rebooted.

While it is not possible to specify the exact number of tunnels and length of
time it would take for the internal counter to overflow, the few customers who
encountered this issue had greater than 200 IPsec tunnels and had an uptime of
three to four months on their transit gateways before encountering this issue.

The number of IPsec tunnels on the transit gateway can be viewed in the Copilot
UI under *Diagnostics > Cloud Routes > Gateway Routes*. In the Gateway
Routes window, search for your transit gateways and check the Tunnels count.

### Who is impacted?

Customers who have Transit Gateways with large numbers of tunnels and are
running one of the following Controller versions:

* 7.2.5012, 7.2.4996, 7.2.4820
* 7.1.4191, 7.1.4183, 7.1.4139, 7.1.4105, 7.1.3958

### Symptoms

* All IPsec tunnels on the Transit Gateway will be in a DOWN state.
* The IPsec process becomes unresponsive.

### Triggers

* High tunnel volume environments with aggressive rekeying or frequent status
  checks.
* Internal counter overflow when reaching the maximum value (2^32), causing a
  freeze in IPsec activity.

### Required Actions

Customers running the affected versions and having greater than 200 IPSec
tunnels, must perform all the following:

1. Upgrade Software to one of the software releases with the fix which are
   [7.1.4208](https://docs.aviatrix.com/documentation/v7.1/release-notes/controller-software-release-notes/controller-software-release-notes.html#corrected-issues-in-aviatrix-release-7-1-4208),
   [7.2.5090](https://docs.aviatrix.com/documentation/v7.2/release-notices/controller-software-release-notes/controller-software-release-notes.html#corrected-issues-in-aviatrix-release-7-2-5090)
   and
   <a href={"/docs/enterprise/" + "10.1" + "/reference/release-notices/release-notes/controller/controller-rn-8.0.0"}>8.0.0</a>
   . Upgrading directly to 8.0.0 requires Aviatrix Support assistance.
2. Perform a transit gateway image upgrade.

For assistance with upgrading your Aviatrix Controller and Gateways, please open
a ticket with the [Aviatrix Support](https://support.aviatrix.com/) team and
select *Software Upgrade Assistance* for the Product.

### How to Recover if Impacted

To recover from the unresponsive IPsec process, STOP and then START the impacted
Aviatrix Transit Gateways.

<a id="field-notice-51" />

## 51. Field Notice

**Date**: 13 February 2025

### Severity

High

### Who is impacted?

All Aviatrix customers with:

* Azure Gateways running versions lower than 7.1.4101, regardless of where the
  Controller and CoPilot are hosted.

* Controller or CoPilot in Azure running Controller versions lower than
  7.1.4101.

* CoPilot appliance versions lower than 3.

### Issue Description

Microsoft Azure has flagged images associated with Aviatrix Controller and
Gateway versions lower than 7.1.4101 and CoPilot appliance versions lower than
version 3 as having security vulnerabilities due to using an operating system
that has reached end-of-support. Microsoft has indicated plans to permanently
remove these older images from availability. Once these images are removed from
Azure, they cannot be reinstated. If you do not upgrade to Controller and
Gateway version 7.1.4101 or greater, and CoPilot appliance version 3 or greater,
you risk being unable to maintain or upgrade your instances.

### Symptoms

New Gateway deployments or image upgrades below Controller and Gateway version
7.1.4101 will fail. Impact: If you do not upgrade to Controller and Gateways
versions 7.1.4101 or greater and Copilot appliance versions 3 or greater before
Azure removes older images may face severe operational disruptions, including
being unable to upgrade or maintain their deployments.

### Impact

Traffic connectivity will be disrupted, as tunnels on the gateway that failed to
resize are not restored.

### Workaround

There is no viable workaround once Azure removes the older images. You must
proactively upgrade your instances to avoid potential service disruptions.

### Recommendations

* Immediate Action: All impacted customers are advised to upgrade your
  Controller and Gateway instances to version 7.1.4101 or greater and CoPilot
  appliances to version 3 or greater.

* Target Deadline: Complete the upgrade as soon as possible and no later than
  Oct 31st, 2025 to ensure a secure and supported environment.

* Important Note: Although the images associated with version 7.1.4101 include
  security patches, Microsoft Azure may still classify them as insecure and
  proceed with their removal. Therefore, upgrading to versions higher than
  7.1.4101 is essential to avoid being stranded.

For assistance with upgrading your Aviatrix Controller and Gateways, please open
a ticket with the [Aviatrix Support](https://support.aviatrix.com/) team and
select **Software Upgrade Assistance** for the Product.

<a id="field-notice-50" />

## 50. Field Notice

**Date**: 7 January 2025

### Severity

High

### Issue Description

CVE-2024-50603 - Critical Vulnerability Security Patch.

### Recommendations

Please review
[CVE-2024-50603](https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2024-50603)
and take action as described in

<a href={"/docs/enterprise/" + "10.1" + "/reference/release-notices/psirt-advisories/index#remote-code-execution-vulnerability-in-aviatrix-controllers"}>Remote Code Execution Vulnerability in Aviatrix Controllers</a>
.

If you have any questions, please contact the
[Aviatrix Support](https://support.aviatrix.com/) team.

<a id="field-notice-49" />

## 49. Field Notice

**Date**: 6 November 2024

### Severity

Moderate

### Who is impacted?

Customers using Controller versions lower than 7.1.4105 and attempting to resize
their HPE-enabled Gateways.

### Issue Description

When attempting to resize a gateway on anAviatrix Controller running versions
older (lower) than 7.1.4105 with HPE enabled, the controller will fail to
restore peering tunnels if a resize operation fails. For example, due to
insufficient CSP resources to support the resize.

### Symptoms

The Aviatrix Controller will display a notification indicating that the resize
operation failed, along with error messages. As a result, routes to the peer
will be missing from the gateway's routing table.

### Impact

Traffic connectivity will be disrupted, as tunnels on the gateway that failed to
resize are not restored.

### Trigger

Resizing of HPE enabled gateways.

This issue can occur when running a Controller version older (lower) than
7.1.4105 with HPE enabled gateways and the gateway resize fails due to any
errors, such as a CSP resource issue, not enough IPs available, etc.

### Workaround

No workaround available. Contact the
[Aviatrix Support](https://support.aviatrix.com/) team prior to performing a
Gateway resize activity if you are running a release that is impacted.

### Recommendations

Contact the [Aviatrix Support](https://support.aviatrix.com/) team prior to
performing a Gateway resize activity if you are running a release that is
impacted.

If you have any further questions, please contact the
[Aviatrix Support](https://support.aviatrix.com/) team.

<a id="field-notice-48" />

## 48. Field Notice

**Date**: 1 August 2024

### Attention: Deprecation of V1 Controller API

**Who is impacted**: This deprecation notice is only relevant to users who
directly consume the Aviatrix Controller API. Terraform and UI usage is not
affected.

The V1 Controller API is being deprecated with the announcement of this field
notice, and it will be removed with the release of Controller version 8.0
expected early in 2025. You can find out if you are using the V1 Controller API
by searching for "https\://\<controller\_ip>/v1/api/" in your configuration.

### Action Required

* **Adopt V2 API Before Upgrading**: Anyone currently using the V1 API should
  transition to the V2 API before upgrading to Controller v8.0 to ensure
  uninterrupted service.
* **V2 API Availability**: The V2 API is already available for organizations
  that are running Controller version 7.0 or later, and we encourage you to
  start the migration process as soon as possible.

### Support and Information

* **Migration method**: The V2 API provides a superset of the V1 API
  capabilities published in the Postman collection, which should make the
  migration relatively straightforward. The migration can generally be achieved
  by changing the base URL from https\://\<controller\_ip>/v1/api/ to
  https\://\<controller\_ip>/v2/api/.
* **Testing and Reporting Issues**: We recommend thoroughly testing your
  integration with the V2 API as part of your migration and reporting any issues
  to the [Aviatrix Support](https://support.aviatrix.com/) team promptly.
* **API Documentation**: For access to the V1 and V2 API Postman collections,
  please contact the [Aviatrix Support](https://support.aviatrix.com/) team.
* **Migration Support**: For further information and assistance regarding the V2
  API, please reach out to the [Aviatrix Support](https://support.aviatrix.com/)
  team.
* **Continued Use of V1 API**: You can continue using the V1 API until you are
  ready to upgrade to Controller version 8.0, but you must migrate to API V2
  before upgrading to Controller version 8.0.
* **V1 API Availability on 7.2**: The V1 API will remain available on Controller
  version 7.2 and will be supported until version 7.2 reaches its end of support
  cycle.

### Migrating from Controller API V1 to V2

When migrating from Controller API V1 to API V2, in most instances there is a
direct equivalent API operation in V2 and simply changing the base URL from /v1/
to /v2/ is sufficient for a successful migration. There are a few exceptions
where there is no equivalent V2 API operation. In some cases, there is no direct
equivalent operation available. In other cases, a different operation must be
used to achieve the same outcome. These exceptions are listed in the table
below.

**Changed Operation Exceptions**

<div className="fn48-table">
  | API V1 Operation                                 | API V2 Operation                                                       | Comments                                                                                                                                                                                |
  | ------------------------------------------------ | ---------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
  | get\_gateway\_supported\_size                    | list\_transit\_gw\_supported\_sizes, list\_spoke\_gw\_supported\_sizes | get\_gateway\_supported\_size still works, but requires an additional mandatory parameter (cloud\_type) and returns only cloud specific results, rather than an object with all clouds. |
  | create\_transit\_gw                              | create\_multicloud\_primary\_gateway                                   | Requires "transit" parameter to be set to "yes".<br /><br />Required parameter changes:<br /><br />region → vpc\_region<br /><br />public\_subnet → gw\_subnet                          |
  | enable\_transit\_ha                              | create\_multicloud\_ha\_gateway                                        | Required parameter changes:<br /><br />public\_subnet → gw\_subnet                                                                                                                      |
  | create\_spoke\_gw                                | create\_multicloud\_primary\_gateway                                   | Requires "transit" parameter to be set to "no" (default).<br /><br />Required parameter changes:<br /><br />region → vpc\_region<br /><br />public\_subnet → gw\_subnet                 |
  | enable\_spoke\_ha                                | create\_multicloud\_ha\_gateway                                        | Required parameter changes:<br /><br />public\_subnet → gw\_subnet                                                                                                                      |
  | enable\_firenet\_fail\_close                     | None                                                                   | Not available (feature deprecated)                                                                                                                                                      |
  | disable\_firenet\_fail\_close                    | None                                                                   | Not available (feature deprecated)                                                                                                                                                      |
  | list\_firenet\_display\_fields                   | None                                                                   | Not available (Should only be used by Aviatrix controller UI.)                                                                                                                          |
  | list\_firewall\_manager\_vendor\_display\_fields | None                                                                   | Not available (Should only be used by Aviatrix controller UI.)                                                                                                                          |
  | list\_profile\_policies\_and\_base\_policy       | list\_profile\_policies                                                | Does not provide a description with the base policy.                                                                                                                                    |
  | resume\_dmz\_firewall                            | None                                                                   | Not available (feature deprecated)                                                                                                                                                      |
  | bypass\_dmz\_firewall                            | None                                                                   | Not available (feature deprecated)                                                                                                                                                      |
  | switchover\_dmz\_firewall                        | None                                                                   | Not available (feature deprecated)                                                                                                                                                      |
</div>

If you have any further questions, please contact the
[Aviatrix Support](https://support.aviatrix.com/) team.

<a id="field-notice-47" />

## 47. Field Notice

**Date**: 27 June 2024

### Advisory: Explore capabilities with Aviatrix CoPilot

<a href={"/docs/enterprise/" + "10.1" + "/concepts-architectures/components/controlplane/copilot-overview"}>Aviatrix CoPilot</a>
offers many
<a href={"/docs/enterprise/" + "10.1" + "/concepts-architectures/components/controlplane/copilot-features"}>features</a>
to simplify Day-0 and Day-2 operations, including:

* Automation of Controller Migration to latest image.

* Improved Gateway Management Page with the ability to download gateway
  configuration details and metrics (CPU and memory usage) in .csv or .xlsx
  format.

* The Upgrade Plan & Upgrade Groups feature allows you to better plan gateway
  upgrades based on Region, Cloud or Environment, etc.

* Simplification of Spoke & Transit Gateway deployment with fewer steps.

* Up to 15 high availability (HA) spoke gateway instances for each Spoke
  Gateway.

<Note>
  Spoke Gateways with HA enabled do not support BGP, Site2Cloud, SNAT, DNAT, or
  FQDN.
</Note>

* <a href={"/docs/enterprise/" + "10.1" + "/guides/monitoring/metrics-api-enable"}>External Monitoring with the Metrics and Status APIs</a>
  allows you to retrieve network metric and status data across your Aviatrix
  data plane for integration with third-party tools for data analysis and
  visualization of the performance and health of your Aviatrix-managed
  resources.

* Practical and useful tools to view Gateway Performance and to configure Alert
  Notifications for Gateway health.

Please reach out to your Account Representative if you need more information on
CoPilot OR contact [Aviatrix Support](https://support.aviatrix.com/) by opening
a support ticket for help to get started with

<a href={"/docs/enterprise/" + "10.1" + "/guides/controlplane/planning-deployment"}>Planning</a>
and
<a href={"/docs/enterprise/" + "10.1" + "/guides/controlplane/copilot-deployment"}>Deploying</a>
Aviatrix CoPilot.

<a id="field-notice-46" />

## 46. Field Notice

**Date**: 02 Nov 2023, revised 26 June 2024

### Issue Description:

#### Extension of End-of-Support and End-of-Life Dates for Aviatrix Software Releases

To better serve our customers, Aviatrix has decided to provide a one-time
extension to the End-of-Support (EOS) and End-of-Life (EOL) dates for
Controllers running release 6.9, 7.0, and 7.1.

Related to this extension, we will also be releasing an additional patch for
releases 6.9 and 7.0 before they reach EOL. This patch will provide extended
time outside of the 2023 holiday window to support our customers in upgrading to
our latest releases.

The previous EOS/EOL timeline was as follows:

| **Release** | **GA Date** | **EOL Date** | **EOS Date** |
| ----------- | ----------- | ------------ | ------------ |
| 6.8         | AUG 09 2022 | AUG 09 2023  | NOV 09 2023  |
| 6.9         | SEP 09 2022 | SEP 09 2023  | DEC 09 2023  |
| 7.0         | DEC 08 2022 | DEC 08 2023  | MAR 08 2024  |
| 7.1         | MAY 11 2023 | MAY 11 2024  | AUG 11 2024  |

The updated EOS/EOL Timeframe is as follows:

| **Release** | **GA Date** | **EOL Date**        | **EOS Date**        |
| ----------- | ----------- | ------------------- | ------------------- |
| 6.8         | AUG 09 2022 | AUG 09 2023         | NOV 09 2023         |
| 6.9         | SEP 09 2022 | JAN 09 2024\*       | APR 09 2024\*       |
| 7.0         | DEC 08 2022 | APR 08 2024\*       | JUL 08 2024\*       |
| 7.1         | MAY 11 2023 | To be announced\*\* | To be announced\*\* |

​\* *Dates have been adjusted by this Field Notice.*

​\*\* *7.1 EOL has been deferred and will be announced upon the
availability of our next major release. After 7.1 EOL Aviatrix will provide at
least an additional 6 months of support before EOS.*

Always reference the Aviatrix EOS/EOL policy for the most up-to-date
information. The EOS/EOL policy is
[here](https://support.aviatrix.com/Aviatrix-EOL-Policy).

For any clarifications on this Field Notice or for upgrade assistance, please
contact [Aviatrix Support](https://support.aviatrix.com/).

<a id="field-notice-45" />

## 45. Field Notice

**Date**: 28 October 2023

**Severity**: High

### Image upgrade and new gateway deployment fails.

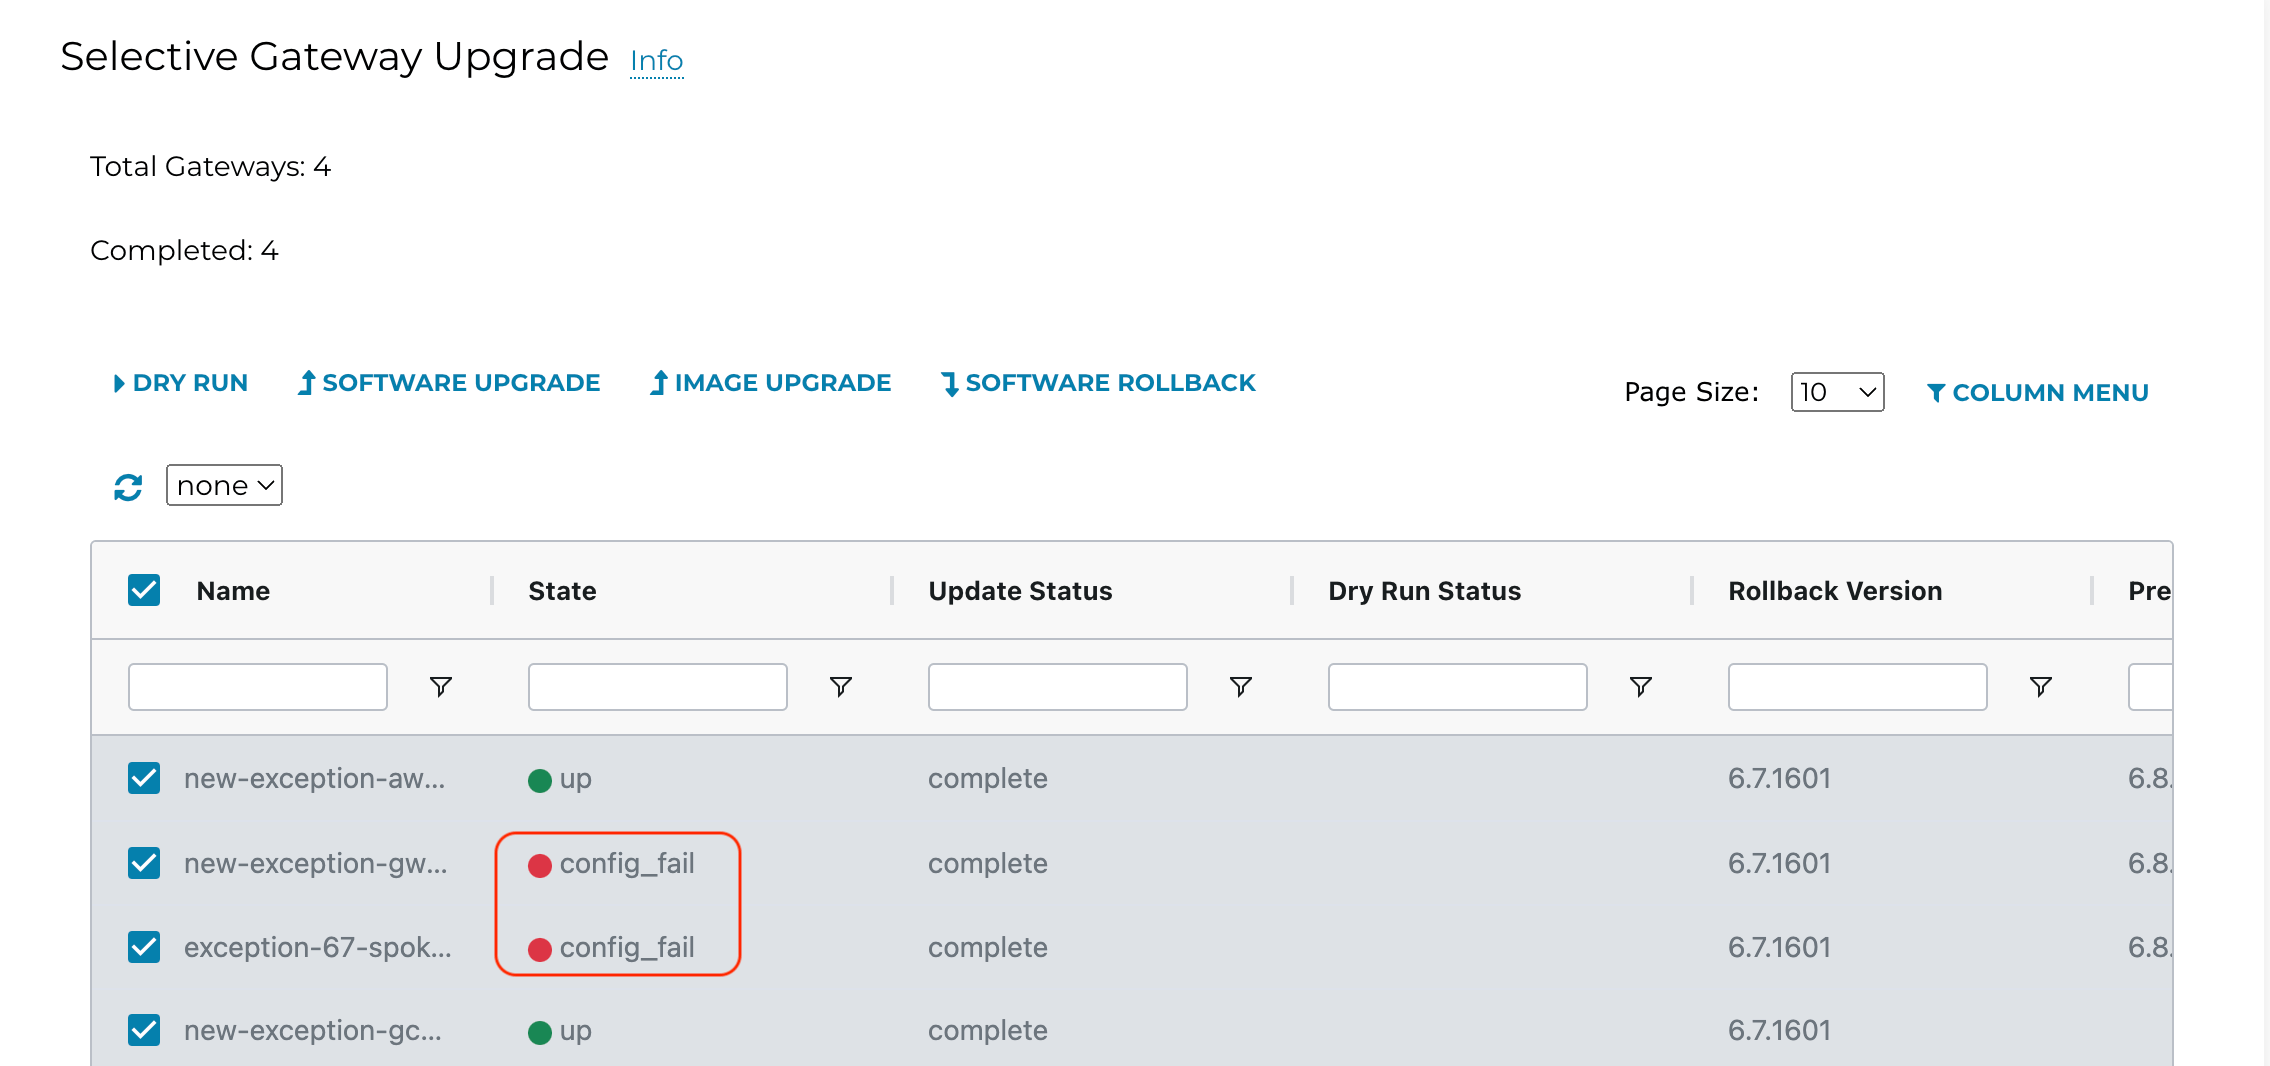
A gateway state on an Aviatrix Controller might change to **"Config\_fail"** when
it is created or just after the image is upgraded. This could occur if the setup
had previously applied a patch named **"Remove unnecessary packages from
gateway"** under the Controller's **Software patches** section. This issue does
not always occur in all regions and clouds, but out of an abundance of caution
we recommend all users who have applied the **"Remove unnecessary packages from
gateway"** patch take action.

### What is the impact?

Customers who applied the **"Remove unnecessary packages from gateway"** patch
need to update the patches before deploying or upgrading gateways. Otherwise,
the gateways might move into a **"Config\_fail"** state.

### Who is impacted?

To encounter this problem, the below conditions should be met:

The **"Remove unnecessary packages from gateway"** patch should show as
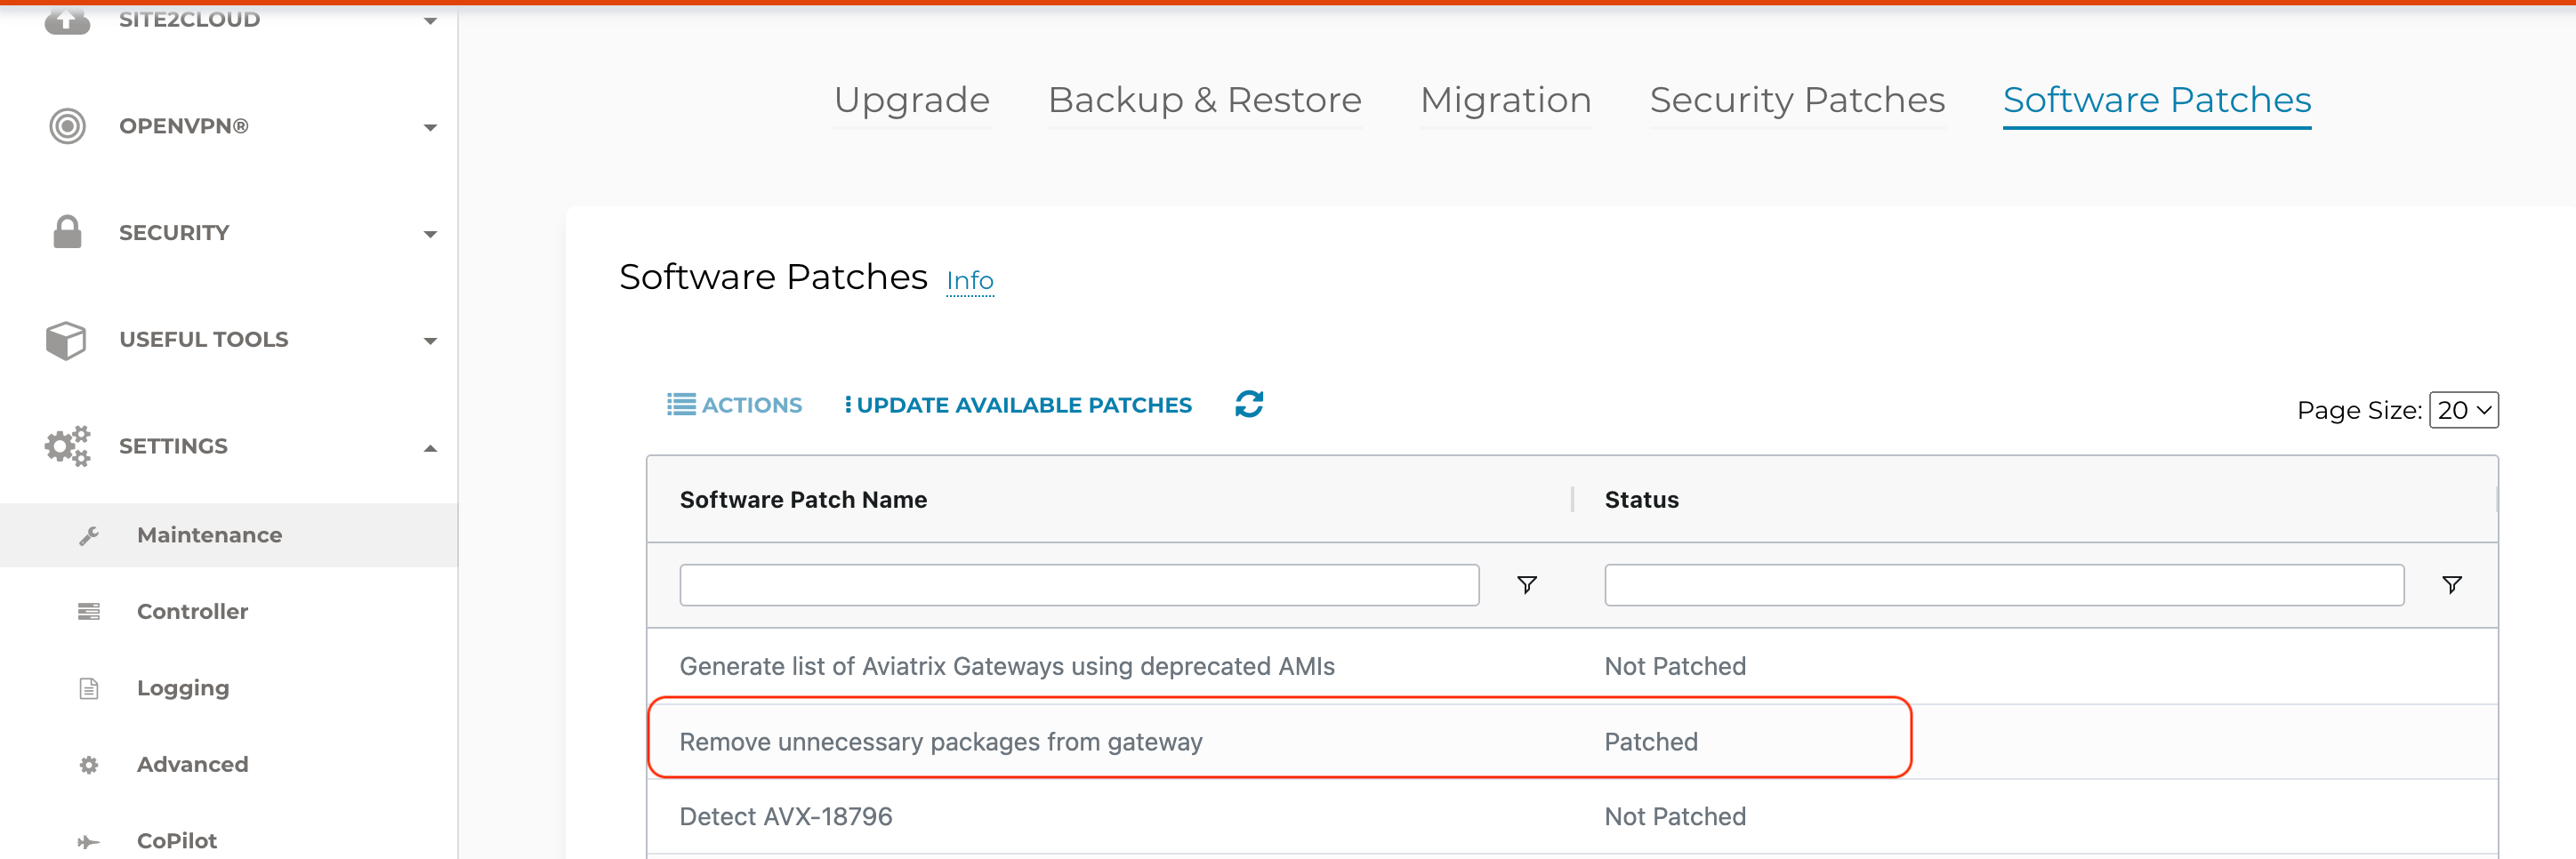
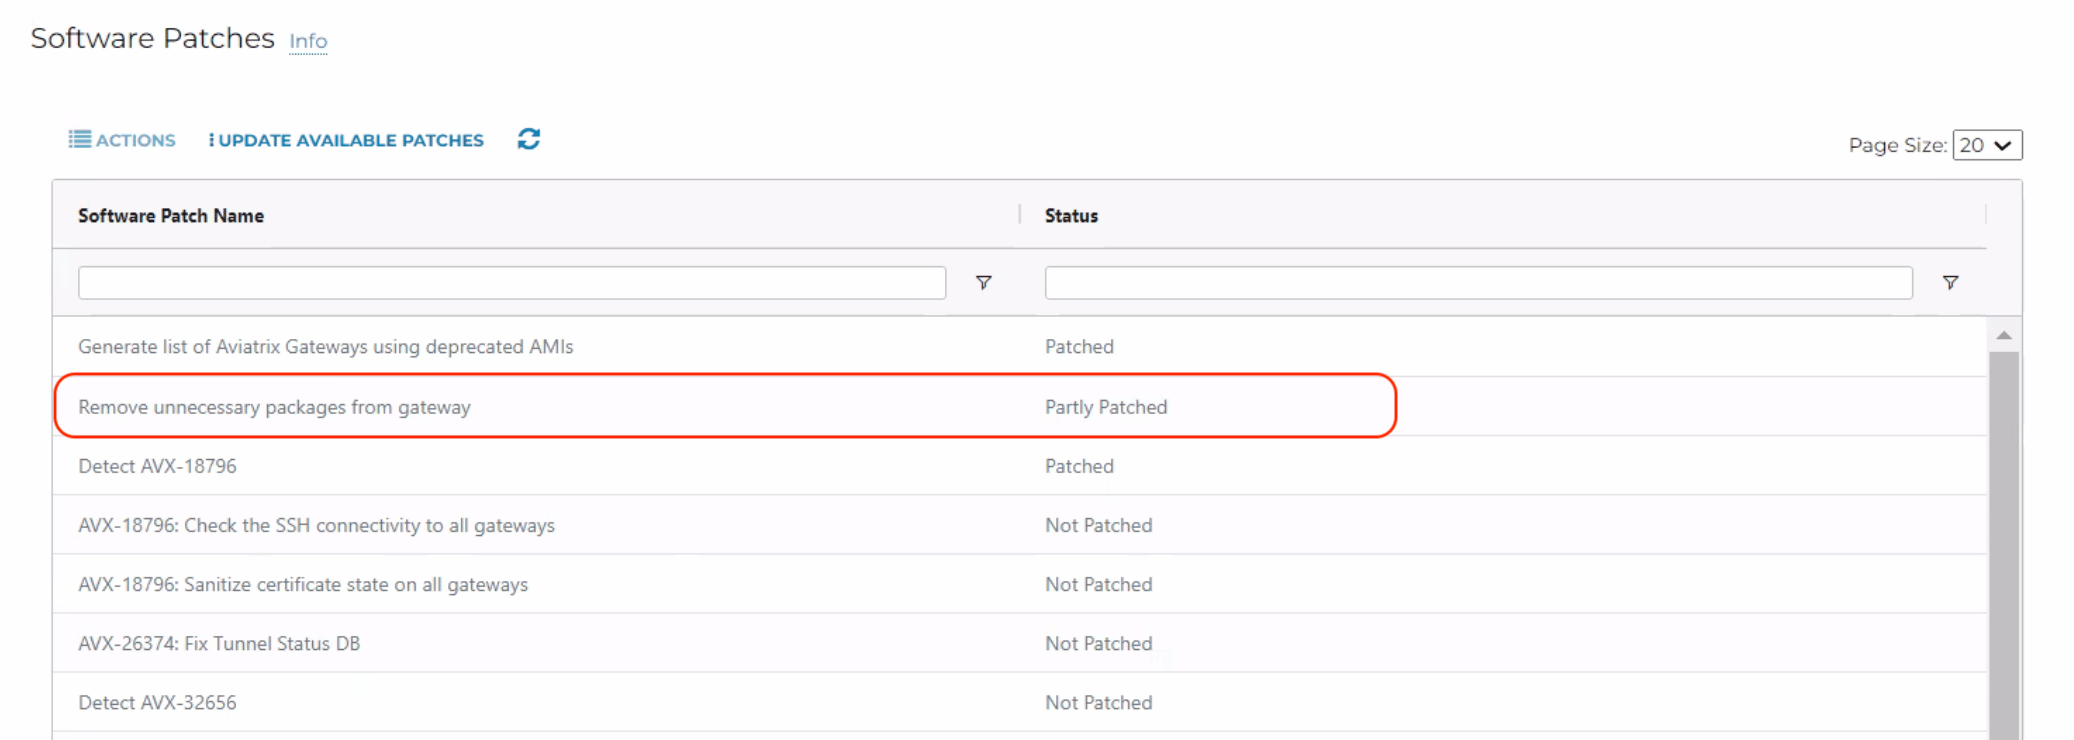
**Patched** or **Partly Patched** on the Controller. To verify the status, go to
**Aviatrix Controller > Settings > Maintenance > Software Patches**.

<div align="center">
  <img src="https://mintcdn.com/aviatrix-14b37c43/Iy8akyzSsTgQ2_0d/images/general/status-patched.png?fit=max&auto=format&n=Iy8akyzSsTgQ2_0d&q=85&s=a5bc6f8f71b48c76ae83d6cbb7acbe88" alt="Patched" width="2896" height="966" data-path="images/general/status-patched.png" />
</div>

<div align="center">
  <img src="https://mintcdn.com/aviatrix-14b37c43/Iy8akyzSsTgQ2_0d/images/general/status-partly-patched.png?fit=max&auto=format&n=Iy8akyzSsTgQ2_0d&q=85&s=f5d50258b2dd2eeaab32db1e48fdae05" alt="Partly Patched" width="2074" height="740" data-path="images/general/status-partly-patched.png" />
</div>

### What is the recommendation?

Aviatrix Systems has updated the patch, and it is now available as a **Software
Patch**.

<Warning>
  Aviatrix strongly recommends not to attempt a gateway image upgrade or to
  deploy a new gateway until you update the available patches.
</Warning>

### How to detect the issue?

The gateway will display the **config\_fail** state in the gateway page of the
Controller:

<div align="center">
  <img src="https://mintcdn.com/aviatrix-14b37c43/Iy8akyzSsTgQ2_0d/images/general/gateway-image-config-fail.png?fit=max&auto=format&n=Iy8akyzSsTgQ2_0d&q=85&s=4a17c6aa04a83eaf7386ee1bd644c32e" alt="Config Fail" width="2270" height="1066" data-path="images/general/gateway-image-config-fail.png" />
</div>

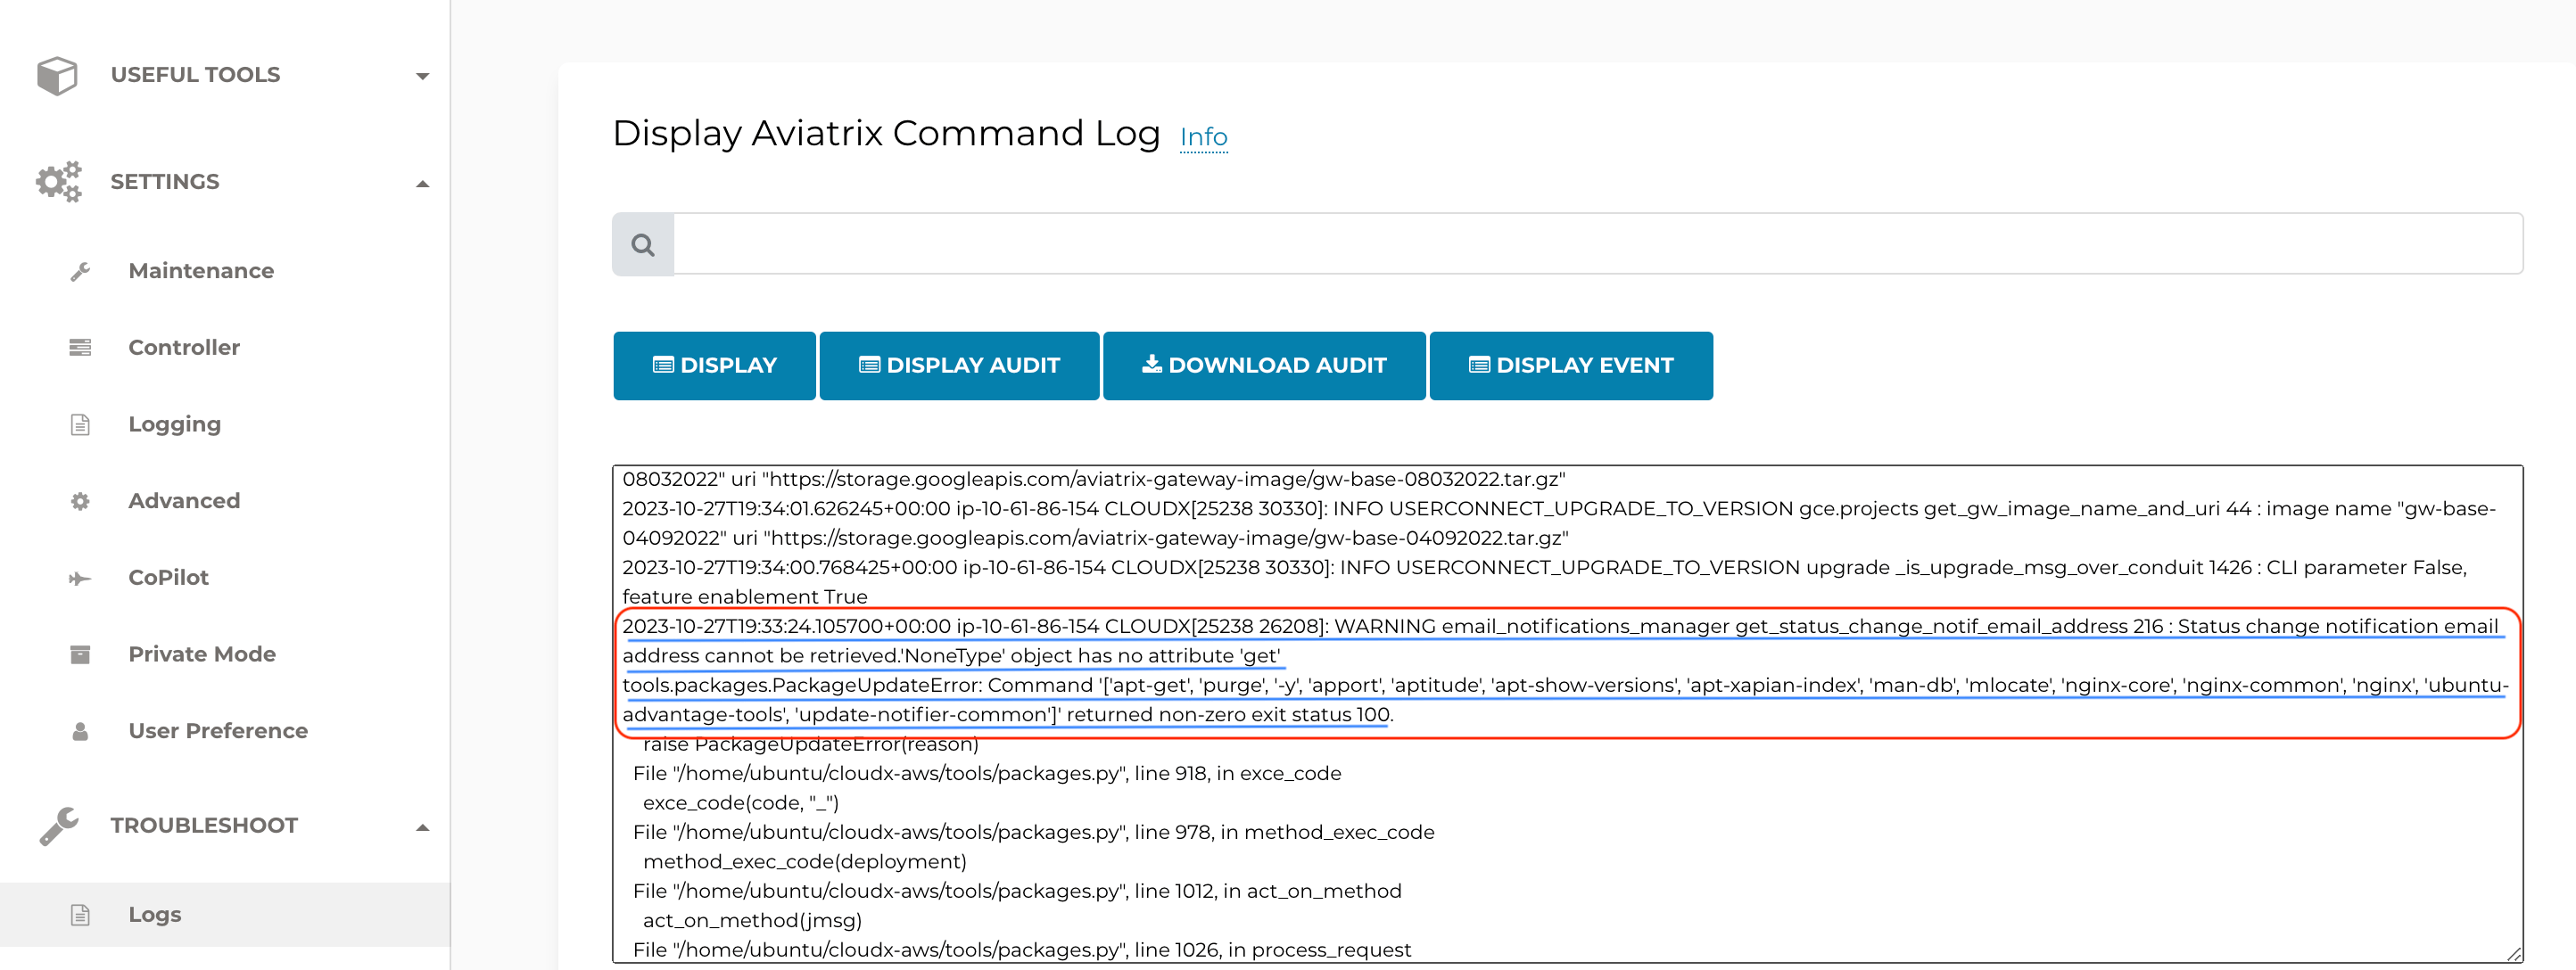
In addition, the following log entries appear on the Controller under **Aviatrix
Controller > Troubleshoot > Logs > Display Aviatrix Command Log > DISPLAY**.

<div align="center">
  <img src="https://mintcdn.com/aviatrix-14b37c43/Iy8akyzSsTgQ2_0d/images/general/display-log-warning.png?fit=max&auto=format&n=Iy8akyzSsTgQ2_0d&q=85&s=3a68bb9d0701bcb264063e967bb6f086" alt="Display Log Warning" width="2888" height="1088" data-path="images/general/display-log-warning.png" />
</div>

Log entry text.

```courier theme={null}
2023-10-26T23:03:05.846367+00:00 ip-10-61-86-154 CLOUDX[25238 26208]:
WARNING email_notifications_manager get_status_change_notif_email_address 216 : Status change
notification email address cannot be retrieved.'NoneType' object has no attribute 'get'
tools.packages.PackageUpdateError: Command '['apt-get', 'purge', '-y', 'apport', 'aptitude',
'apt-show-versions', 'apt-xapian-index', 'man-db', 'mlocate', 'nginx-core', 'nginx-common',
'nginx', 'ubuntu-advantage-tools', 'update-notifier-common']' returned non-zero exit status
100.
```

### How to fix and avoid the issue?

Aviatrix has updated the **"Remove unnecessary packages from gateway"** patch.

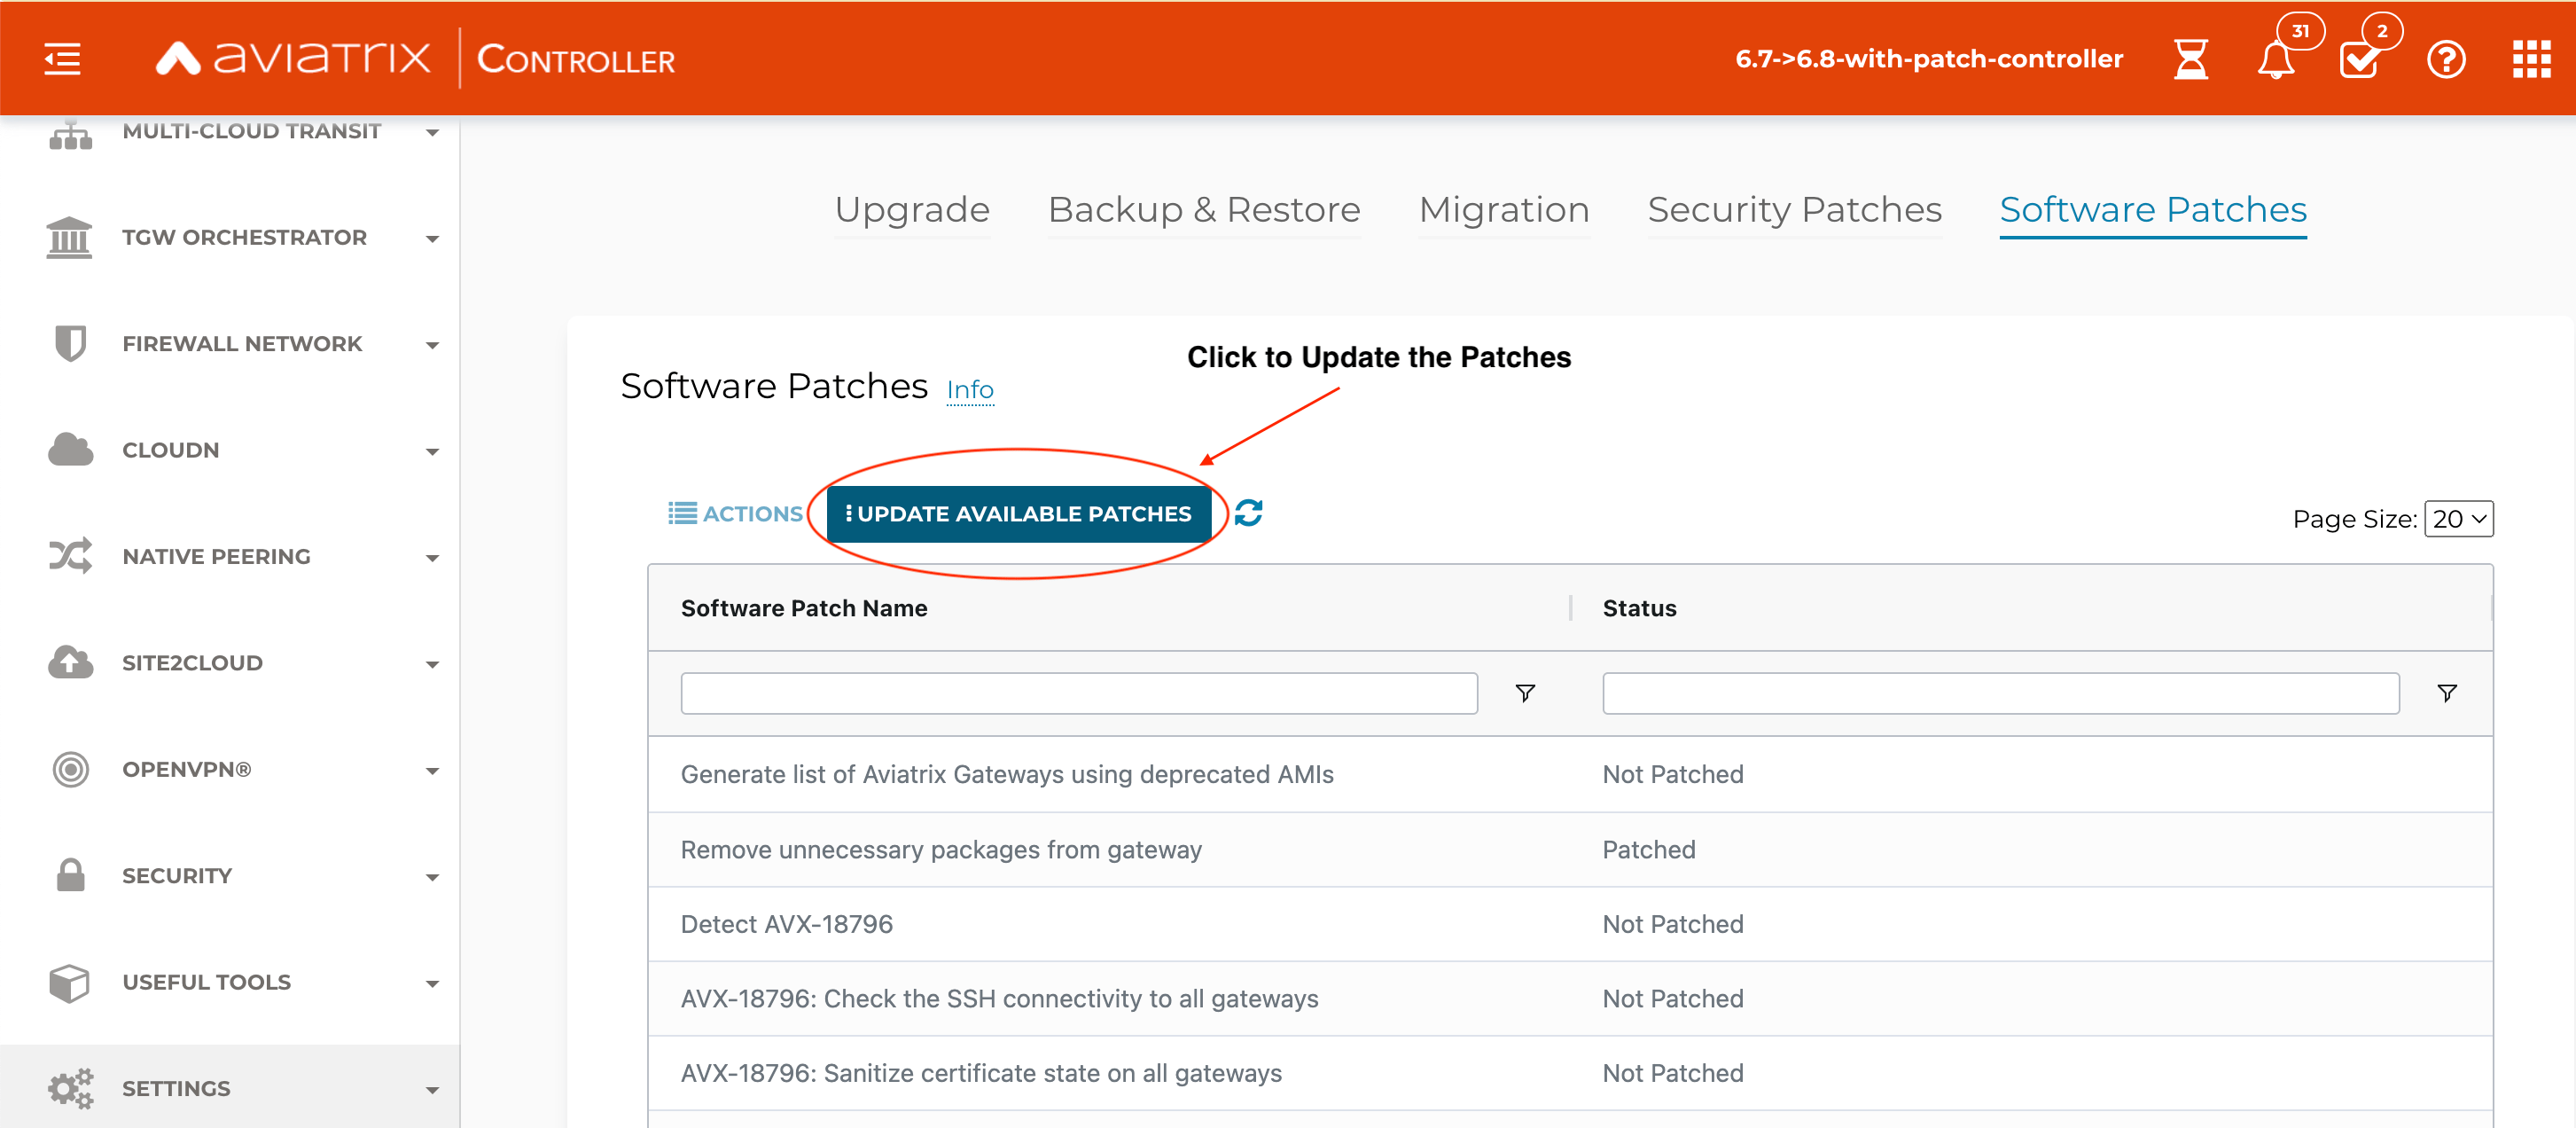
1. Prior to performing an image upgrade or deploying a gateway in the current
   release, please go to **Aviatrix Controller > Settings > Maintenance >
   Software Patches** and click on **UPDATE AVAILABLE PATCHES**. Once the
   patches are updated, a gateway image upgrade or gateway deployment can be
   performed. The update of the available patches is required to be done one
   time per Controller unless a Controller upgrade or a Controller migration is
   performed.

<div align="center">
  <img src="https://mintcdn.com/aviatrix-14b37c43/Iy8akyzSsTgQ2_0d/images/general/controller-patch-update.png?fit=max&auto=format&n=Iy8akyzSsTgQ2_0d&q=85&s=92982f238bedfe2fbc8796a4fbf6c91b" alt="Controller Patch Update" width="2906" height="1272" data-path="images/general/controller-patch-update.png" />
</div>

2. Whenever a Controller software upgrade (Platform Upgrade) is performed, you
   are required to **Update Available Patches** again before performing an image
   upgrade or gateway deployment. Please go to **Aviatrix Controller >
   Settings > Maintenance > Software Patches** and click on **UPDATE AVAILABLE
   PATCHES**.

3. Whenever a Controller Migration is performed, once the backup restore
   completes on the new Controller and all gateways are connected to it, you are
   required to **Update Available Patches** again before performing an image
   upgrade or gateway deployment. Please go to **Aviatrix Controller >
   Settings > Maintenance > Software Patches** and click on **UPDATE AVAILABLE
   PATCHES**.

### How to fix the issue if you have already hit it.

Perform **Step 1** in the previous **How to fix and avoid the issue** section,
then perform a gateway image upgrade.

<a id="field-notice-44" />

## 44. Field Notice

**Date**: 25 October 2023

**Who is impacted**: Customers modifying rules in the Egress FQDN Filtering
feature

### Issue Description:

A critical issue identified within the Aviatrix Controller may impact your rule
modifications in the Egress FQDN Filtering feature.

In versions 7.1.1710, 7.1.1794, and 7.1.1906, when you attempt to edit an
existing FQDN Egress rule under a specific tag and click **Save and Update**,
the Controller removes other rules with the same tag. This unexpected behavior
can lead to an outage that may impact your business operations.

### Workaround

To avoid encountering this issue, we recommend adding or deleting rules instead
of modifying existing rules.

If you do need to modify an existing rule, use the following workaround:

1. Export the rules.
2. Modify the rules as needed in the text file.
3. Make sure no filters are in use in the Edit screen for the rules. Then,
   import the file with the modified rules.
4. Click **Save and Update**.

If you have already encountered the issue, please follow the above workaround.
Our team highly recommends upgrading to version **7.1.2131**, where this issue
has been resolved, or a later release.

<a id="field-notice-42" />

## 42. Field Notice

**Date**: 13 April 2023

(The content of this field notice was revised for clarity on 04/17/2023.)

### Issue Description:

For all current Controller software versions (all versions earlier than
7.0.1726), Aviatrix gateways are exporting files to a remote log collection
entity. Starting in Controller software version 7.0.1726, instead of exporting
files to a remote log collection entity, the Aviatrix Controller and gateways
will start streaming the log lines being written to "Syslog" and "Auth.log".

When you use the default rsyslog server configuration suggested in

<a href={"/docs/enterprise/" + "10.1" + "/guides/monitoring/aviatrix-logging#rsyslog-config-on-controller"}>Aviatrix Documentation</a>
, the logs streamed from the Controller and gateways will now have multiple
files. Each file will be named with the application that generated the log.

For example: All logs generated by the avx-gw-state-sync application would be
re-directed to a file named "avx-gw-state-sync" on the log server.

There will be a change in log format. You must change your syslog collectors and
any related automation to accept the new log format.

Old format:

Mar 23 19:17:50 GW-UdpGateway-50.17.41.173 syslog 2023-03-05T19:17:50+00:00
GW-UdpGateway-50.17.41.173 avx-gw-state-sync\[11249]:
warn#011gateway\_launcher/gateway\_launcher.go:212#011daemon exited

New format:

Mar 23 19:17:50 GW-UdpGateway-50.17.41.173 avx-gw-state-sync\[11249]:
warn#011gateway\_launcher/gateway\_launcher.go:212#011daemon exited

Prefix of old format: Mar 23 19:17:50 GW-gg-aws-usw2-s127-35.162.124.66 syslog
2023-03-05T19:17:50+00:00

Prefix of new format: Mar 23 19:17:50 GW-gg-aws-usw2-s127-35.162.124.66

<a id="field-notice-41" />

## 41. Field Notice

*Date*: 28 Nov 2022

### *Change in Default Behavior*

The latest 7.0 version of Aviatrix controller introduces a token verification to
Aviatrix's private API.

Please take notice of a change in behavior beginning with Aviatrix Controller
version 7.0. The 7.0 version introduces token-based Controller API operations
that binds Aviatrix's private API usage by Aviatrix API Legal Terms of Use\*.

To allow time for customers to make necessary changes in their infrastructure to
support token-based API operations, we will not enforce a strict check for the
token in the 7.0 release. Therefore, Aviatrix's private API will continue to
work for your existing use cases while running 7.0. However, token checking will
be enforced in a later release.

### Who is impacted?

Direct users of Aviatrix's private API would be impacted by this change. There
is no impact to users of Aviatrix Terraform Provider, Aviatrix CoPilot and
Aviatrix Controller UI. Customers who have a Controller HA set up would also be
affected. After upgrading to the release with token enforcement enabled,
recreate your Controller HA configuration. Use HA script 2.01 or above. For
details on HA script version, refer to

<a href={"/docs/enterprise/" + "10.1" + "/guides/controlplane/controller-ha-aws#aws-ha"}>Controller HA</a>
.

### Recommended Solution:

To insulate customers from our evolving private API, Aviatrix strongly
recommends you switch to Aviatrix Terraform Provider for all operations
involving automation.

If you have special need to still use Aviatrix's private API, please reach out
to Aviatrix Support by opening a ticket at Support Portal at
[https://support.aviatrix.com](https://support.aviatrix.com) for guidance on Aviatrix's private API token
generation.

Please mention your Aviatrix private API use case(s) in your ticket for us to
better understand your automation needs, thereby enhancing our Terraform
Support.

**\*Aviatrix API Legal Terms of Use:**

Use of Aviatrix API software ("Developer Software") is governed by the
[Customer Terms of Use](https://aviatrix.com/terms-of-use/). We reserve the
right to rescind any license to the Developer Software at our sole discretion
without prior notice. DEVELOPER SOFTWARE IS MADE AVAILABLE BY US TO YOU ON AN
"AS IS" AND "AS AVAILABLE" BASIS, (I) WITHOUT ANY REPRESENTATION OR WARRANTY OF
ANY KIND, WHETHER EXPRESS, IMPLIED OR STATUTORY TO THE FULLEST EXTENT PERMITTED
BY LAW AND (II) WITHOUT ANY OBLIGATION OF US TO PROVIDE TECHNICAL SUPPORT OR ANY
INDEMNITY FOR YOUR ACCESS TO, AND USE OF, THE DEVELOPER SOFTWARE.