> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Transit FireNet Vendor Integration
> The Vendor Integration function allows you to log into a firewall or firewall manager and change the route table on the firewall to program the routing for Transit FireNet, or to change routing if a gateway in Transit FireNet fails.
The Vendor Integration function allows you to log into a firewall or firewall
manager and change the route table on the firewall to program the routing for
Transit FireNet, or to change routing if a gateway in Transit FireNet fails.
You can also use Vendor Integration to configure the RFC 1918 and non-RFC 1918
routes between the Aviatrix Gateway and the vendor's firewall instance.
To turn On IPv6 on an existing FireNet, revoke the existing Vendor Integration
settings, enable IPv6 on the FireNet, and then reconfigure Vendor Integration.
Controller Version 9.0 extends IPv6 FireNet vendor support to Fortinet and Check
Point, in addition to Palo Alto Networks (supported from Release 8.2). IPv6
Vendor Integration applies to **Palo Alto Networks** standalone firewalls
(without Panorama) from Release 8.2, and to **Fortinet** and **Check Point**
from Release 9.0. The Controller blocks attaching firewall instances whose
firmware does not support IPv6 to an IPv6-enabled FireNet Gateway.
IPv6 vendor integration in Azure is currently not functional. If you require
vendor-driven IPv6 route programming in Azure, configure IPv6 routes manually
in the firewall.
You can only configure information on this dialog if a firewall is already
attached to the Transit FireNet.
## Configuring Vendor Integration
1. From the Security > FireNet Gateways tab, click the vertical ellipsis icon
 in a FireNet Gateway row and select **Manage Vendor Integration**.
2. In the Vendor Integration dialog, select **Through Firewall** or **Through
Firewall Manager**. You should only select the latter if the Vendor is a Palo
Alto firewall (managed by Panorama).
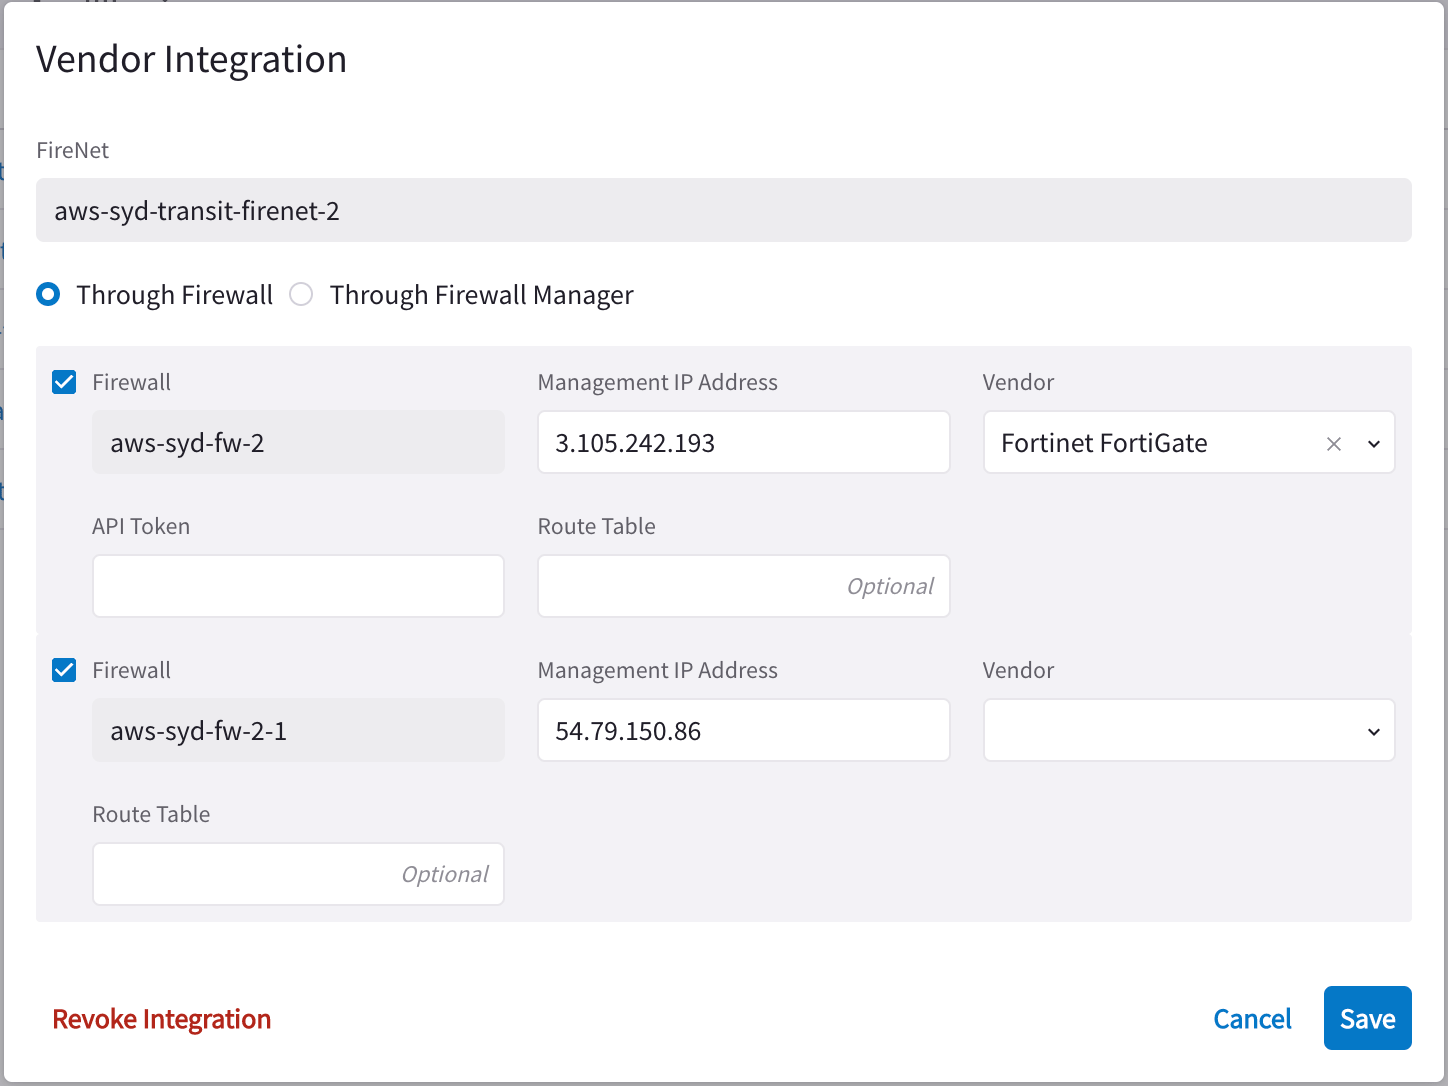 3. Configure the following:
| Field | Description |
| ------------------------------------------------------------------ | --------------------------------------------------------------------------------------------------------------- |
| **Firewall** | Name of the attached firewall (this is pre-populated with the name of the attached firewall). |
| **Firewall Manager Vendor (Through Firewall Manager option only)** | Palo Alto Networks Panorama |
| **Management IP Address** | Management IP address of the firewall. |
| **Vendor (Through Firewall option only)** | Firewall vendor (Palo Alto Networks VM-Series, Fortinet FortiGate, Check Point CloudGuard). |
| **Authentication (Check Point CloudGuard)** | Password or Private Key |
| **Username (Check Point, Palo Alto)** | Username for logging on to the firewall. |
| **Password (Check Point, Palo Alto)** | Password for logging on to the firewall. |
| **Private Key (Check Point)** | If you selected Private Key authentication for your Check Point firewall, you must upload the private key here. |
| **FireNet Instance** | |
| **Template Name (Firewall Manager Vendor only)** | Name of the template. |
| **Template Stack Name (Firewall Manager Vendor only)** | Name of the Template Stack. |
| **Route Table** | Optional |
| **API Token (Fortinet FortiGate only)** | API token generated from the Fortinet FortiGate instance |
4. Click **Save**.
## Revoking Vendor Integration
You cannot revoke vendor integration for FireNet gateways that have the
Generic vendor selected.
To revoke Vendor Integration:
1. Select Vendor Integration as per step 1 above, and then click **Revoke
Integration** on the dialog.
2. When prompted about being sure you want to revoke, click **Revoke**.
## Syncing Routes to Firewall
The Vendor Integration tab only displays for a Transit FireNet if you have
configured a Firewall Manager (Panorama) and attached it to this Transit
FireNet.
You can click **Sync Routes to Firewall** on the FireNet Gateway Vendor
Integration tab (you must configure vendor integration first) or the details
panel for the firewall, to ensure that the FireNet routes are synced to the
selected firewall.
You can also sync routes to the firewall from the Security > FireNet > Firewall details tab.
Since vendor integration requires that the firewall be pinged periodically, you
should
[configure the 'ping' ability](https://legacy.docs.aviatrix.com/documentation/latest/security/firewall-paloalto-enabling-ping.html)
in the respective firewall UIs.
You can also sync routes to the firewall from the Security > FireNet > Firewall tab (click a firewall to see its details, and then click **Sync Routes to Firewall**).
## Related Topics
* Transit FireNet Security Groups
* Transit FireNet Diagnostics