> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Managing Egress Security for VPC/VNets
> Controller 8.0 is required for all features and functionality on this tab except for applying local egress to VPC/VNets.
Controller 8.0 is required for all features and functionality on this tab
except for applying local egress to VPC/VNets.
The Egress VPC/VNets tab displays all VPC/VNets discovered by your cloud
accounts and their protection
status.
VPC/VNets with No Egress status require the deployment of a Spoke gateway for
Local Egress.
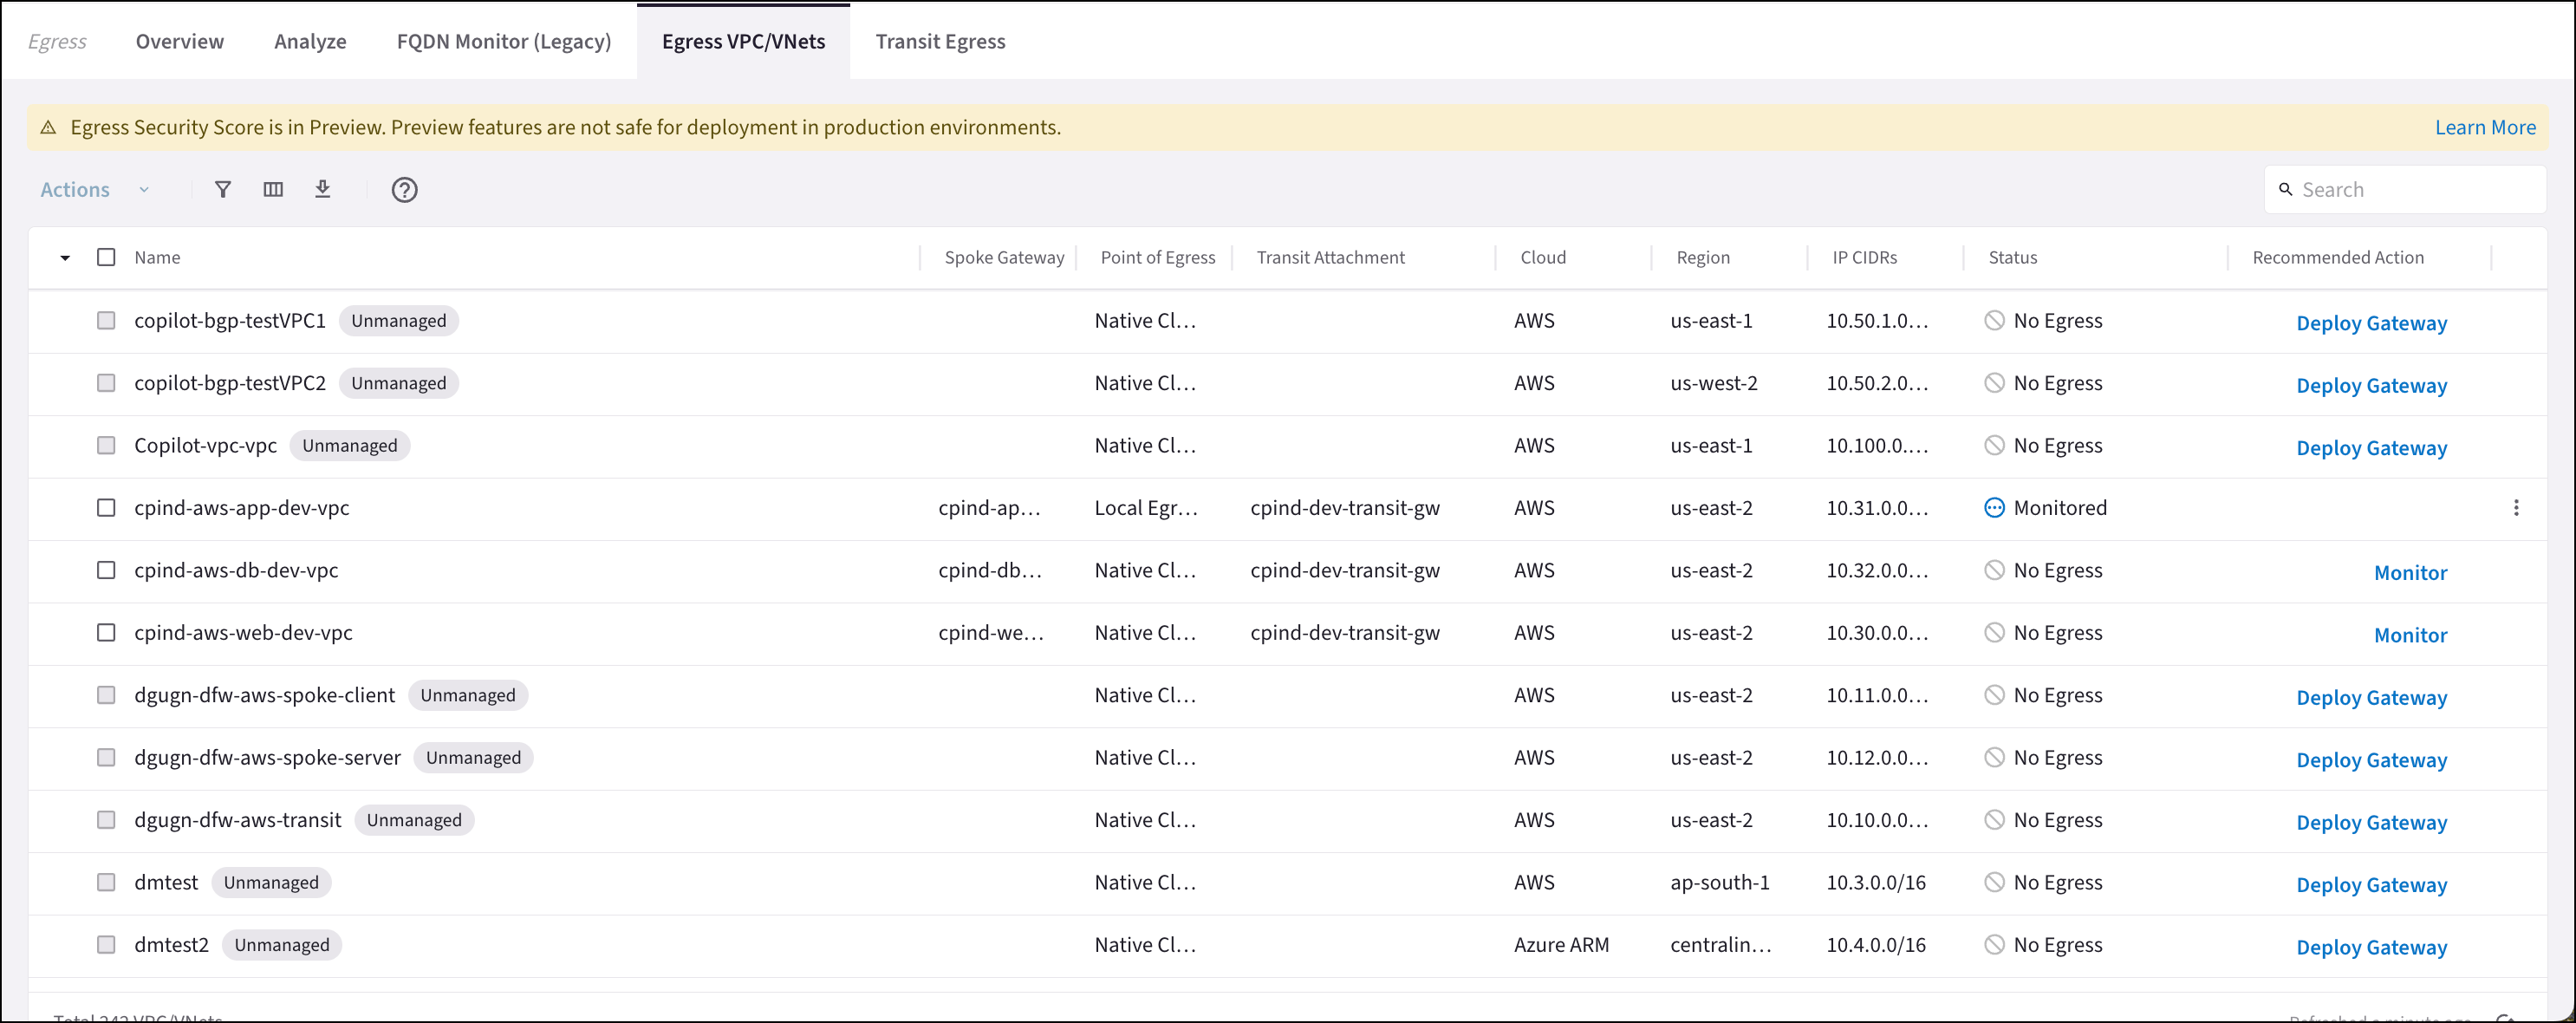 The Egress VPC/VNets tab displays:
* Spoke gateways that have Local Egress enabled (Spoke gateways that send
traffic directly to the Internet).
* Spoke gateways that have Transit Egress enabled (Spoke gateways that forward
traffic to a Transit gateway, which then sends the traffic to the Internet).
This Transit gateway must have Transit Egress Capability (selectable when you
[create a Transit
gateway](https://legacy.docs.aviatrix.com/documentation/latest/network/transit-gateway-about.html?expand=true)).
* Spoke gateways where Egress is not configured by Aviatrix (Native Cloud
Egress). These are not editable.
* GCP Spoke gateways that have Global VPC and Transit Egress enabled. These are
not editable.
* Any Transit gateways attached to the Spoke gateways.
## Actions on the Egress VPC/VNets Tab
You can do the following on this tab if you have upgraded to Controller 8.0 and
have the DCF feature enabled:
* [Deploy a Spoke Gateway within a VPC/VNet](https://legacy.docs.aviatrix.com/documentation/latest/security/egress-deploy-spoke-gateway.html),
so that Local Egress can be applied
* Apply Local Egress to VPC/VNets
* Remove Local Egress from VPC/VNets
* Monitor VPC/VNets
, to determine if any of them require protection
* Protect VPC/VNets
by only allowing trusted traffic flows
* Unprotect but still monitor VPC/VNets
* Include VPC/VNets in the Egress Security Score
* Exclude VPC/VNets from the Egress Security Score
You can do the following on this tab if you have not yet upgraded to Controller
8.0:
* Apply Local Egress to VPC/VNets
* Remove Local Egress from VPC/VNets
## Views on the Egress VPC/VNets Tab
The following views are available on the Egress VPC/VNets tab:
* Default View: Shows a comprehensive view of all VPC/VNets where Local Egress
is enabled, including their protection status.
* Local Egress: Displays VPC/VNets with Local Egress enabled, showing which
Spoke gateways are sending traffic directly to the Internet.
* Transit Egress: Displays VPC/VNets with Transit Egress enabled, where Spoke
gateways forward traffic to a Transit gateway for Internet access.
* Monitored VPC/VNets: Displays VPC/VNets that are being monitored for egress
traffic, allowing you to see which VPC/VNets have traffic flows logged at
L4/L7.
* Unprotected VPC/VNets: Displays VPC/VNets that have direct access to the
Internet without any egress protection applied.
* Unmanaged VPC/VNets: Displays VPC/VNets that are not yet onboarded or do not
have Aviatrix gateways deployed within them.
## Related Topics
* Overview of Egress Security Score Protection
* [Egress Traffic Overview](https://legacy.docs.aviatrix.com/documentation/latest/security/egress-traffic-overview.html?expand=true)
* Analysis of Egress Traffic