> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.

# Transit Gateway to Palo Alto VM-Series Workflow

> This is not a common scenario. You would only set up this type of connection if you want to connect an Aviatrix Transit gateway to a firewall that is outside your Cloud service provider (for example, in a branch office or warehouse).

<Note>
  This is not a common scenario. You would only set up this type of connection
  if you want to connect an Aviatrix Transit gateway to a firewall that is
  outside your Cloud service provider (for example, in a branch office or
  warehouse).
</Note>

This document describes how to build a Transit connection between an Aviatrix
Transit Gateway and Palo Alto Networks Firewall. To simulate an on-prem
Firewall, we use a VM-Series in an AWS VPC.

Network setup is as following:

* VPC1 (with Aviatrix Transit Gateway)
  * VPC1 CIDR: 10.5.0.0/16
  * VPC1 Public Subnet CIDR: 10.5.3.0/24
  * VPC1 Private Subnet CIDR: 10.5.2.0/24
* VPC2 (with Palo Alto Networks VM-series)
  * VPC2 CIDR: 10.0.0.0/16
  * VPC2 Public Subnet CIDR: 10.0.0.0/24
  * VPC2 Private Subnet CIDR: 10.0.1.0/24
* Sample subnet advertised with the help of BGP - 192.168.0.24/32 (loopback
  interface on PaloAlto)

Configuration WorkFlow:

1. In CoPilot, navigate to Cloud Fabric > Gateways > Transit Gateways.

2. [Create a Transit gateway](https://legacy.docs.aviatrix.com/documentation/latest/network/transit-gateway-about.html?expand=true)
   in AWS that will connect to your Palo Alto firewall.

3. To connect the transit VPC GW to Palo Alto, navigate to Networking >
   Connectivity > External Connections.

4. Click *+External Connection*.

5. In the Add External Connection dialog, configure the following:

   | Field                   | Value                                                                                             |
   | ----------------------- | ------------------------------------------------------------------------------------------------- |
   | Connect Public Cloud to | External Device > BGP over IPsec                                                                  |
   | Local Gateway           | Select the Transit gateway you created in step 2 above                                            |
   | Local ASN               | Enter the BGP AS Number the Transit Gateway will use to exchange routes with the external device. |
   | Remote ASN              | Enter the BGP AS number configured on the LAN                                                     |
   | Remote Device IP        | This is the Palo Alto WAN IP                                                                      |

6. Click *Save*.

   <a id="download-config" />

7. <a href={"/docs/enterprise/" + "10.1" + "/guides/connectivity/gateways/external-connection-download-configuration"}>Download the configuration</a>
   .

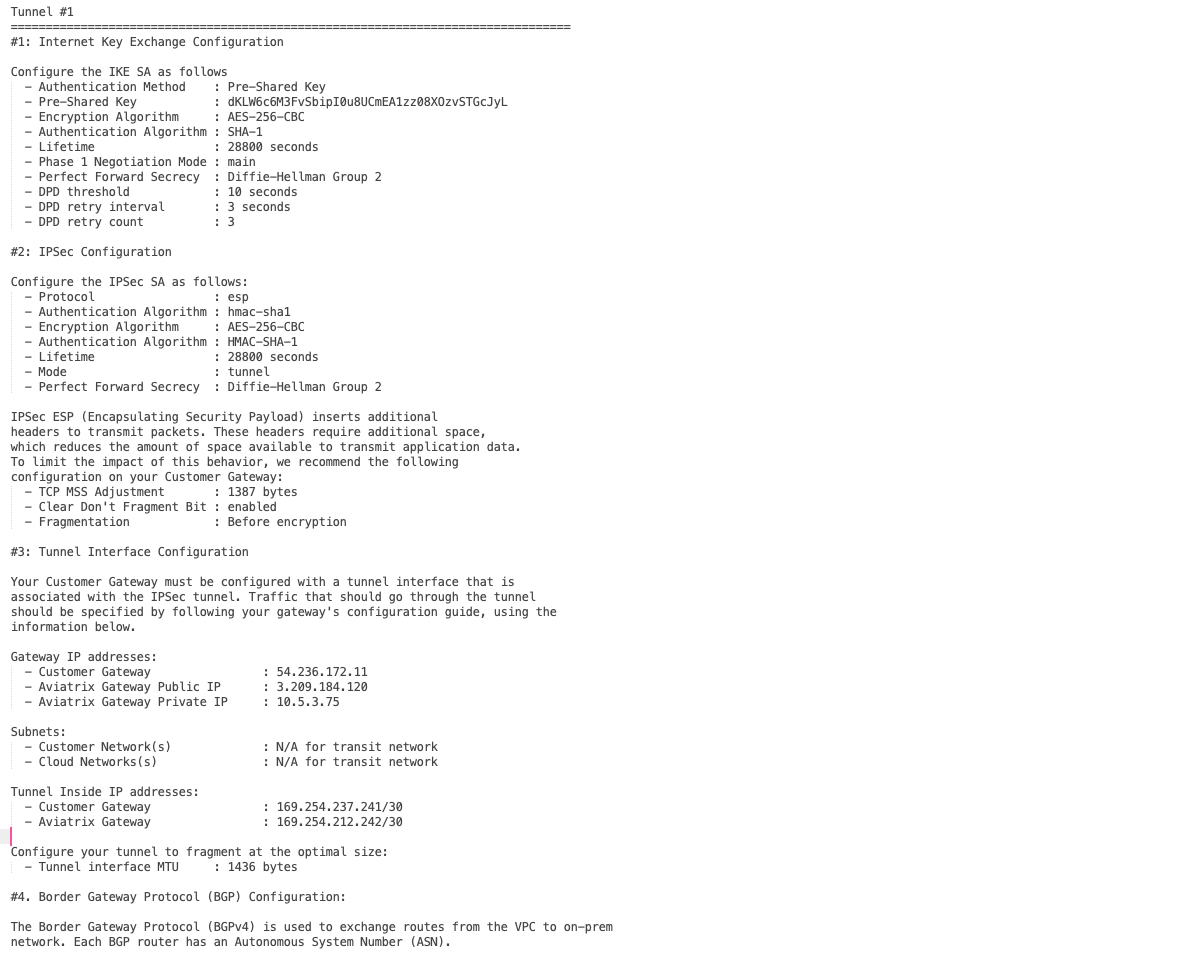
8. Use the information in the downloaded file to configure the router.

   The following is a sample configuration based on the Site2Cloud configuration
   above.
   <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto4.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=ad6568b9e307003c6d55ef7722a22089" alt="image4" width="1184" height="961" data-path="images/guides/connectivity/vpn/paloalto4.png" />

## Configuring the Palo Alto VM-Series Firewall

Log into Palo Alto Networks VM Series and configure it as follows:

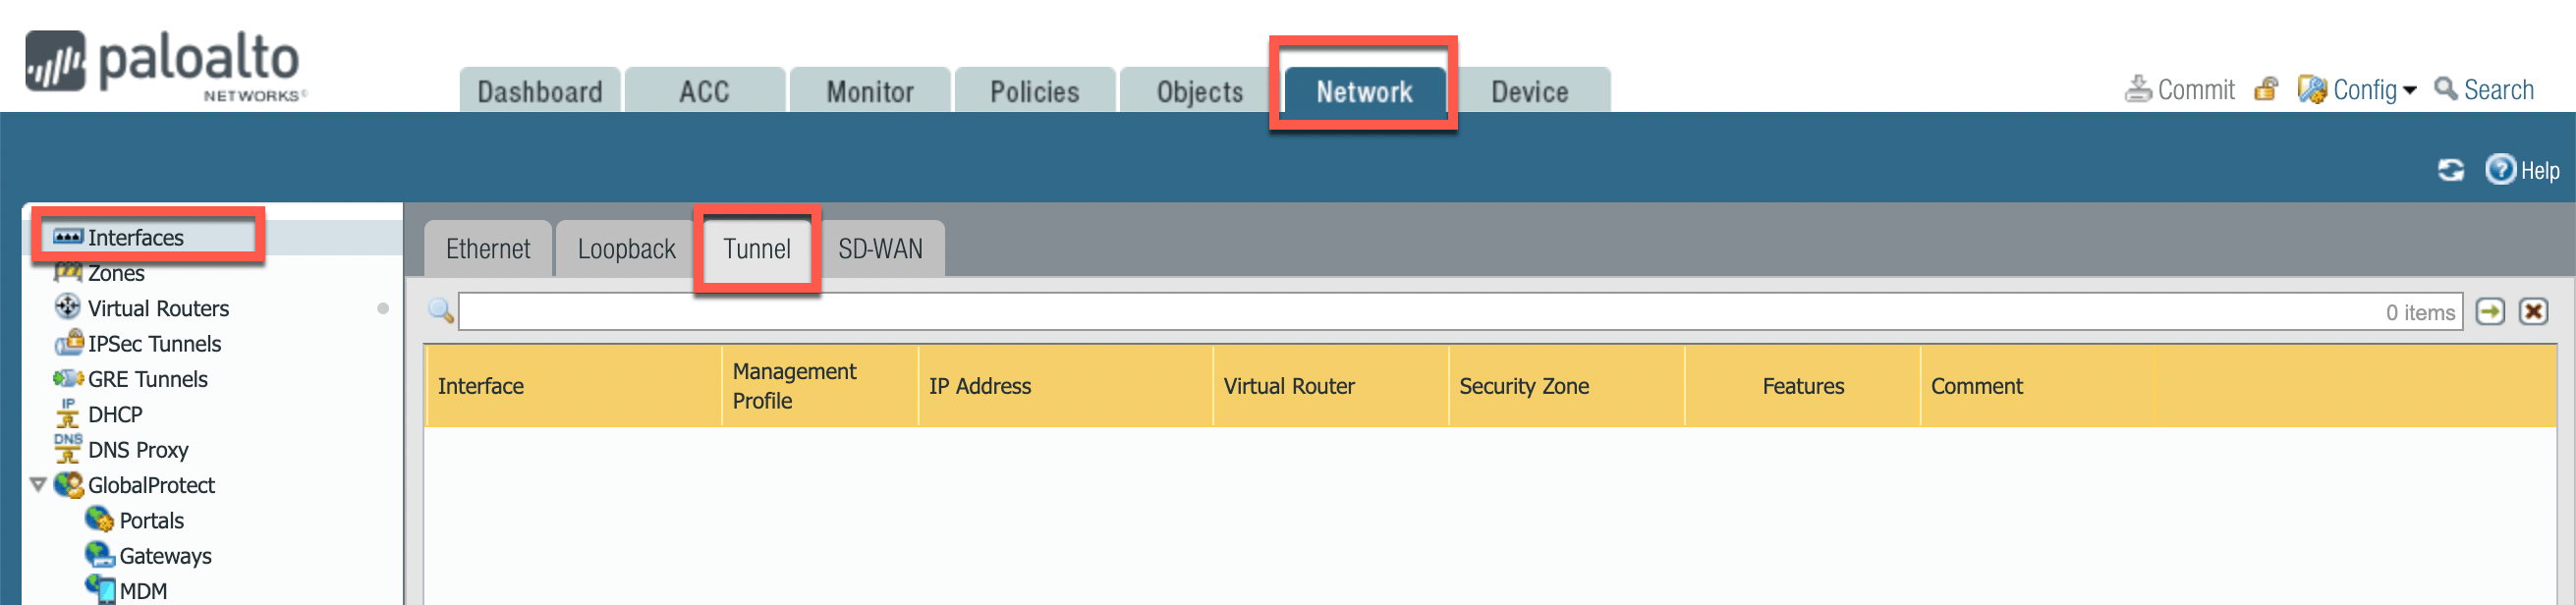
1. Navigate to Network > Interfaces > Tunnel.
   <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto-create-tunnel.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=a7b1a3bf03843f9a159705cea9a5621e" alt="" width="2622" height="616" data-path="images/guides/connectivity/vpn/paloalto-create-tunnel.png" />

2. Click *Add* to create a new tunnel interface. In the Tunnel Interface dialog,
   on the Config tab, assign the following parameters.

   <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto5.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=0305e8945eeab9dc9bc96cfd9aa4f953" alt="paloalto5" width="1404" height="602" data-path="images/guides/connectivity/vpn/paloalto5.png" />

   | **Field**      | **Value**                                                                                                           |
   | -------------- | ------------------------------------------------------------------------------------------------------------------- |
   | Interface Name | Type an ID in the yellow field next to Interface Name (for example, 45; this tunnel will then be named 'tunnel.45') |
   | Virtual Router | Select the existing *default* virtual router                                                                        |
   | Security Zone  | Select the layer 3 internal zone from which traffic originates                                                      |

   <Note>
     If the tunnel interface is in a zone different from the one where the
     traffic will originate, you must create a policy to allow the traffic to
     flow from the source zone to the zone containing the tunnel interface.
   </Note>

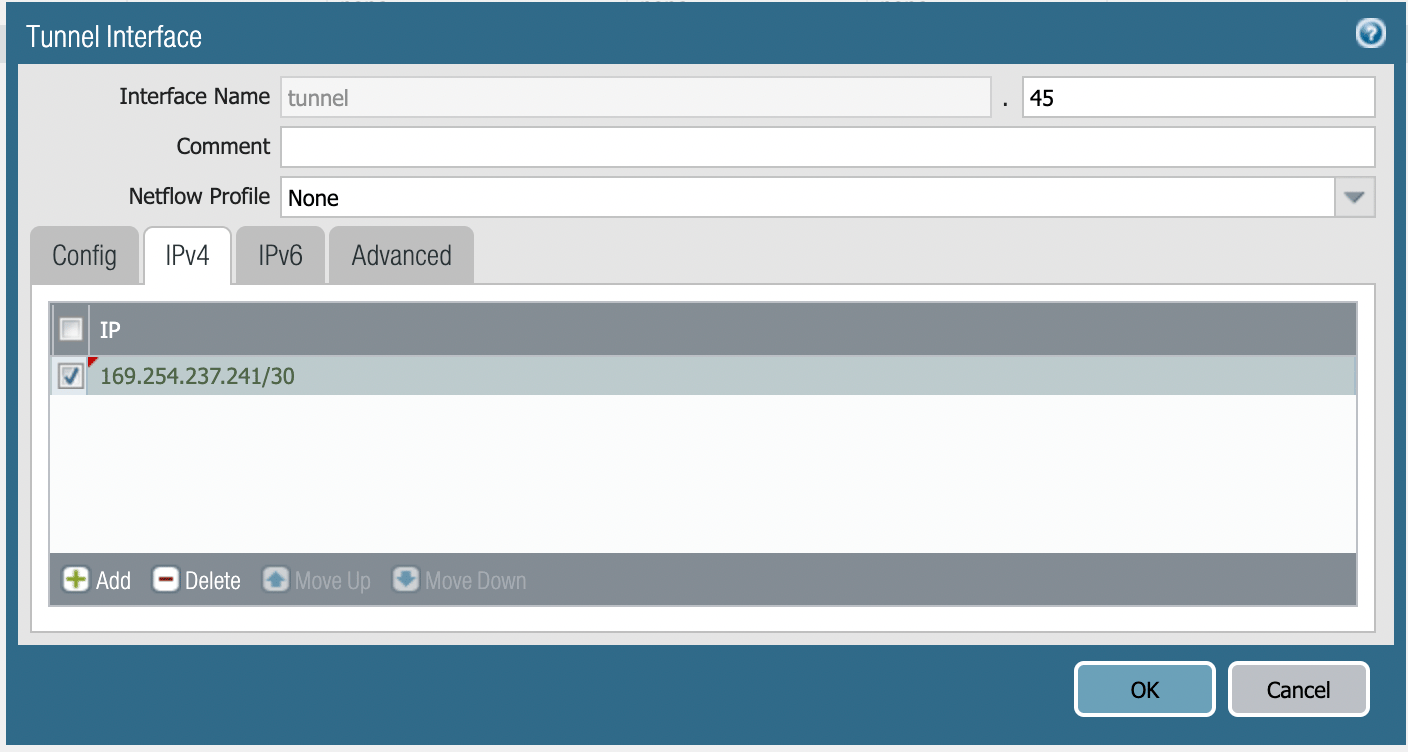
   Click the IPv4 tab and add the tunnel IP address from the configuration
   downloaded above.
   <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto6.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=36a0f201d0bc2fc1ddba07424f2de1e8" alt="paloalto6" width="1408" height="752" data-path="images/guides/connectivity/vpn/paloalto6.png" />

3. Click *OK*.

4. Navigate to Network > Network Profiles > IKE Crypto.

5. Click *Add*.

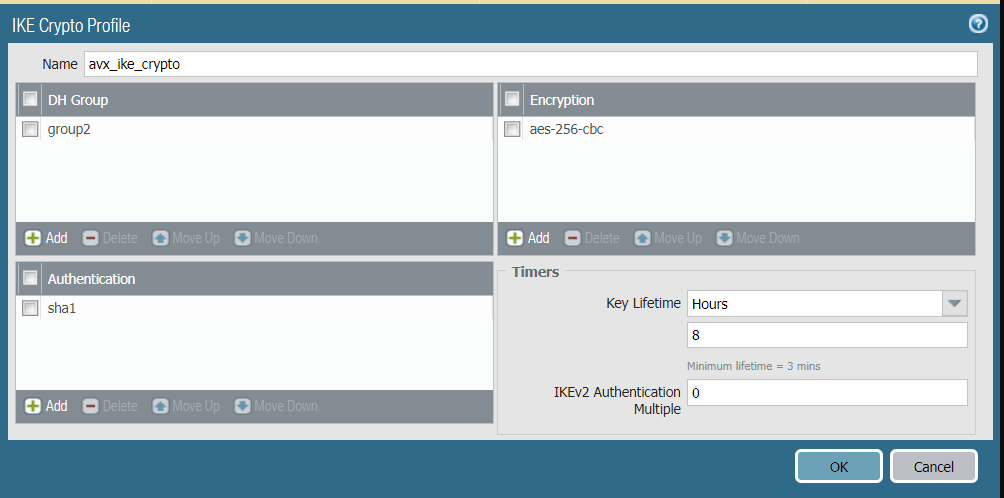
6. In the IKE Crypto Profile dialog, define the IKE Crypto profile (IKEv1
   Phase-1) parameters as shown.
   <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto7.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=c0c3280b397b24f6c2cc2eb253d2a20c" alt="paloalto7" width="1004" height="498" data-path="images/guides/connectivity/vpn/paloalto7.png" />

7. Click *OK*.

8. Navigate to Network > Network Profiles > IKE Gateways and click *Add*.

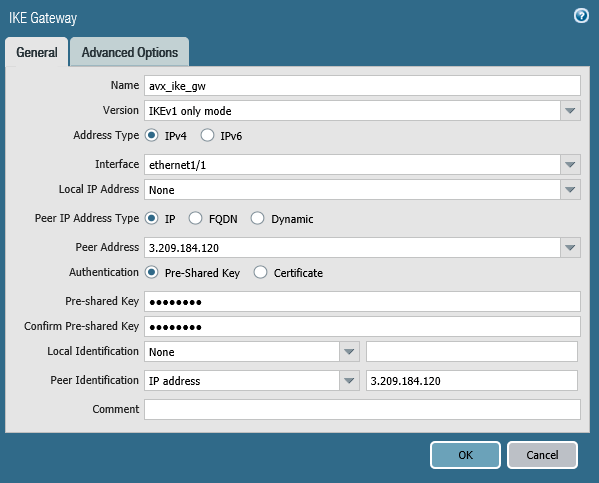
9. In the IKE Gateway dialog, configure the IKE Phase-1 Gateway as shown below.
   These parameters should match the Site2Cloud configuration
   [downloaded here](#configuring-the-palo-alto-vm-series-firewall).
   <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto8.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=508eace9e0beb04521c64cc09b5c3a06" alt="image8" width="599" height="483" data-path="images/guides/connectivity/vpn/paloalto8.png" />

   | **Field**                               | **Value**                                                                                                                                                                    |
   | --------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
   | Name                                    | avx\_ike\_gw                                                                                                                                                                 |
   | Address Type                            | IPv4                                                                                                                                                                         |
   | Interface                               | Palo Alto Networks WAN port (ethernet 1/1)                                                                                                                                   |
   | Peer IP Address Type                    | IP                                                                                                                                                                           |
   | Peer Address                            | Aviatrix Gateway public IP<br /><br />If using remote private IP, the Peer Address should be the remote private IP while Peer Identification should be the remote public IP. |
   | Authentication                          | Pre-Shared Key                                                                                                                                                               |
   | Pre-shared Key / Confirm Pre-shared Key | Key from <a href={"/docs/enterprise/" + "10.1" + "/guides/connectivity/gateways/external-connection-download-configuration"}>downloaded configuration</a>                    |
   | Peer Identification                     | IP Address & Aviatrix Gateway public IP                                                                                                                                      |

10. On the Advanced Options tab, select the *IKE Crypto Profile* created in
    step 6.

11. Click *OK*.

12. Navigate to Network > Network Profiles > IPSec Crypto.

13. Click *Add* to create a new profile.

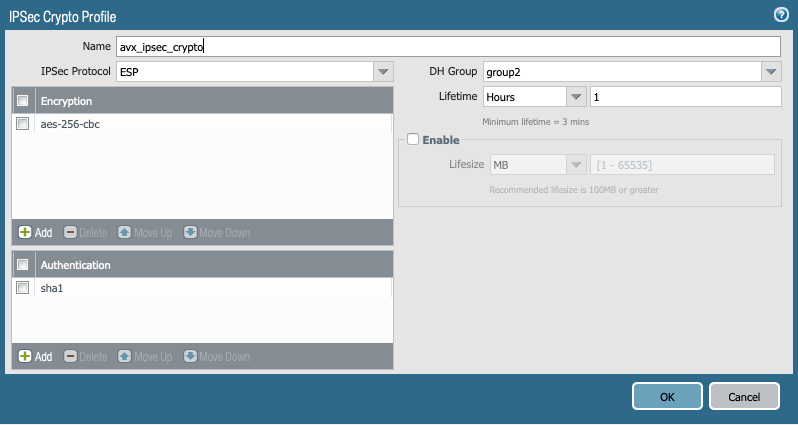
14. In the IPSec Crypto Profile dialog, define the IPSec crypto profile (IKEv1
    Phase-2). These parameters should match the relevant values in the <a href={"/docs/enterprise/" + "10.1" +
    "/guides/connectivity/gateways/external-connection-download-configuration"}>downloaded
    configuration</a>.

    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto10.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=d38ccb329b94cd4782fe77c885e13e4b" alt="paloalto10" width="798" height="425" data-path="images/guides/connectivity/vpn/paloalto10.png" />

15. Click *OK*.

16. Navigate to Network > IPSec Tunnels and click *Add* to create a new IPSec
    Tunnel.

17. Configure the General tab as follows:

    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto11.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=53c5903e54edfed8220f9fed919fd8bb" alt="image11" width="1001" height="402" data-path="images/guides/connectivity/vpn/paloalto11.png" />

    | **Field**            | **Value**                               |
    | -------------------- | --------------------------------------- |
    | Tunnel Interface     | Tunnel interface created in step 3      |
    | IKE Gateway          | IKE gateway created in step 9           |
    | IPSec Crypto Profile | IPSec crypto profile created in step 14 |

    <Note>
      There is no need to configure proxy-id. Commit the configuration. The
      IPSec tunnel should now be green.

    </Note>

    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto14.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=502bbfcd36e9fb3e4ac31f4de68d3f09" alt="image23" width="624" height="50" data-path="images/guides/connectivity/vpn/paloalto14.png" />

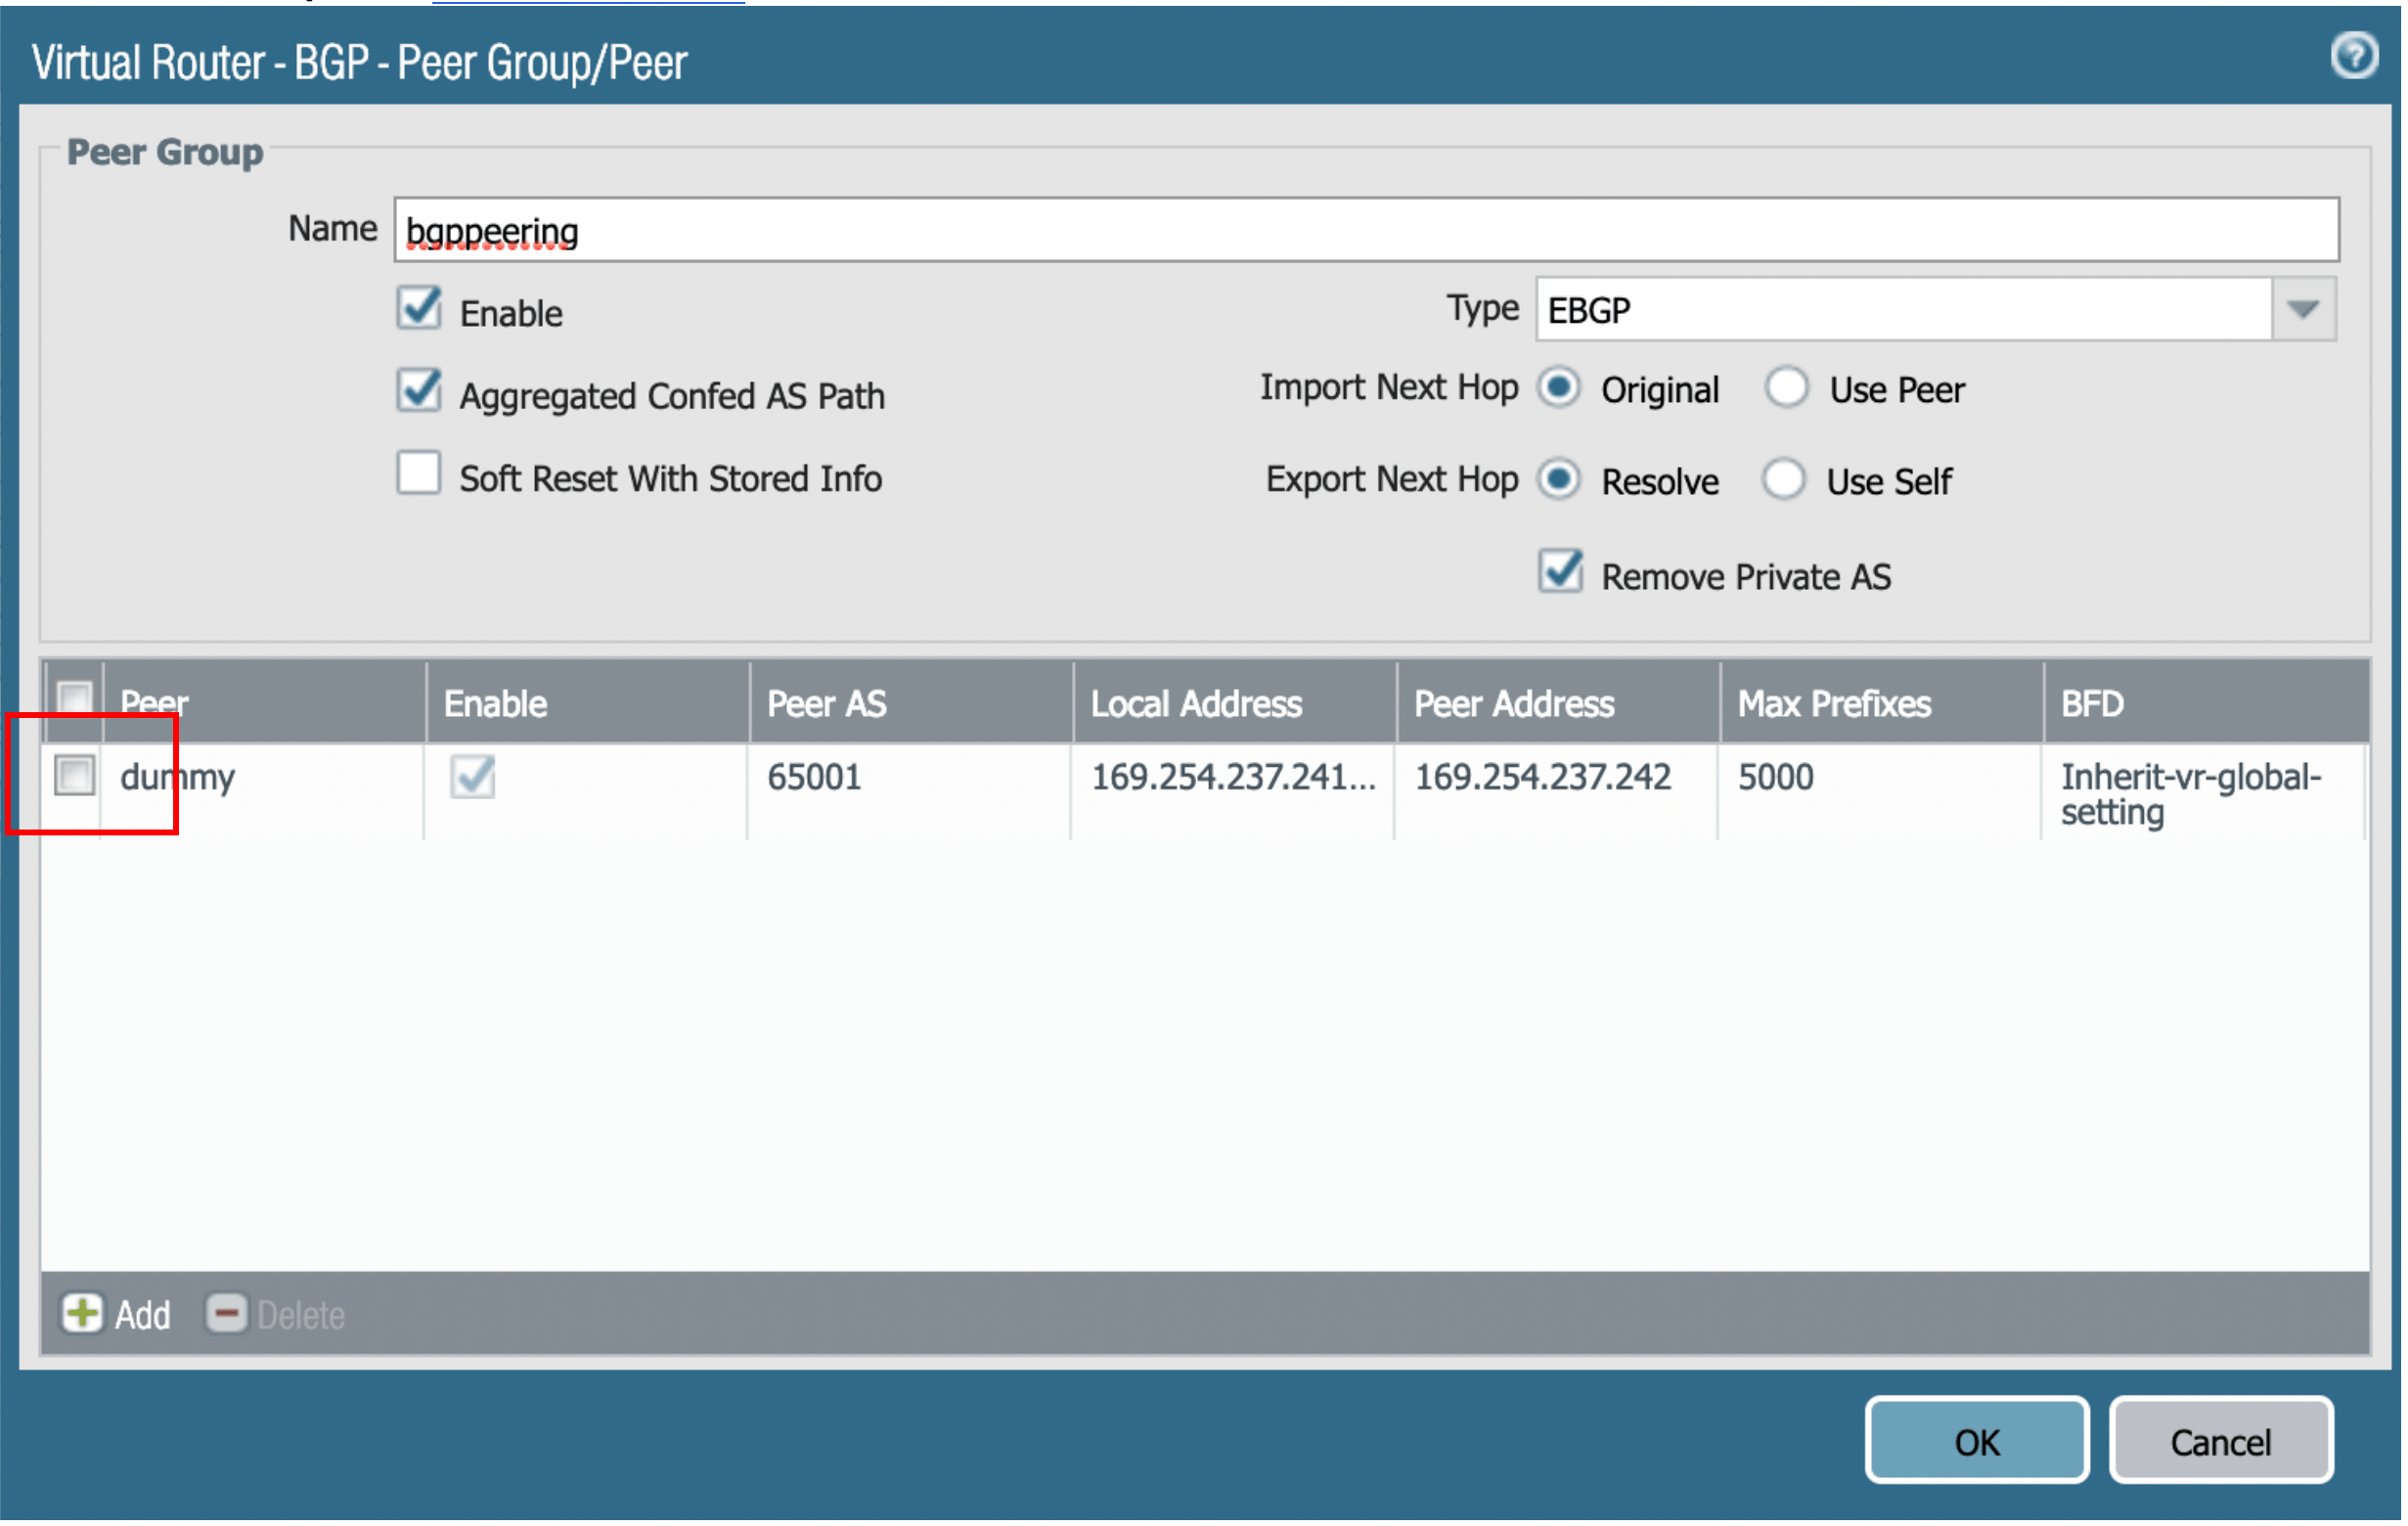
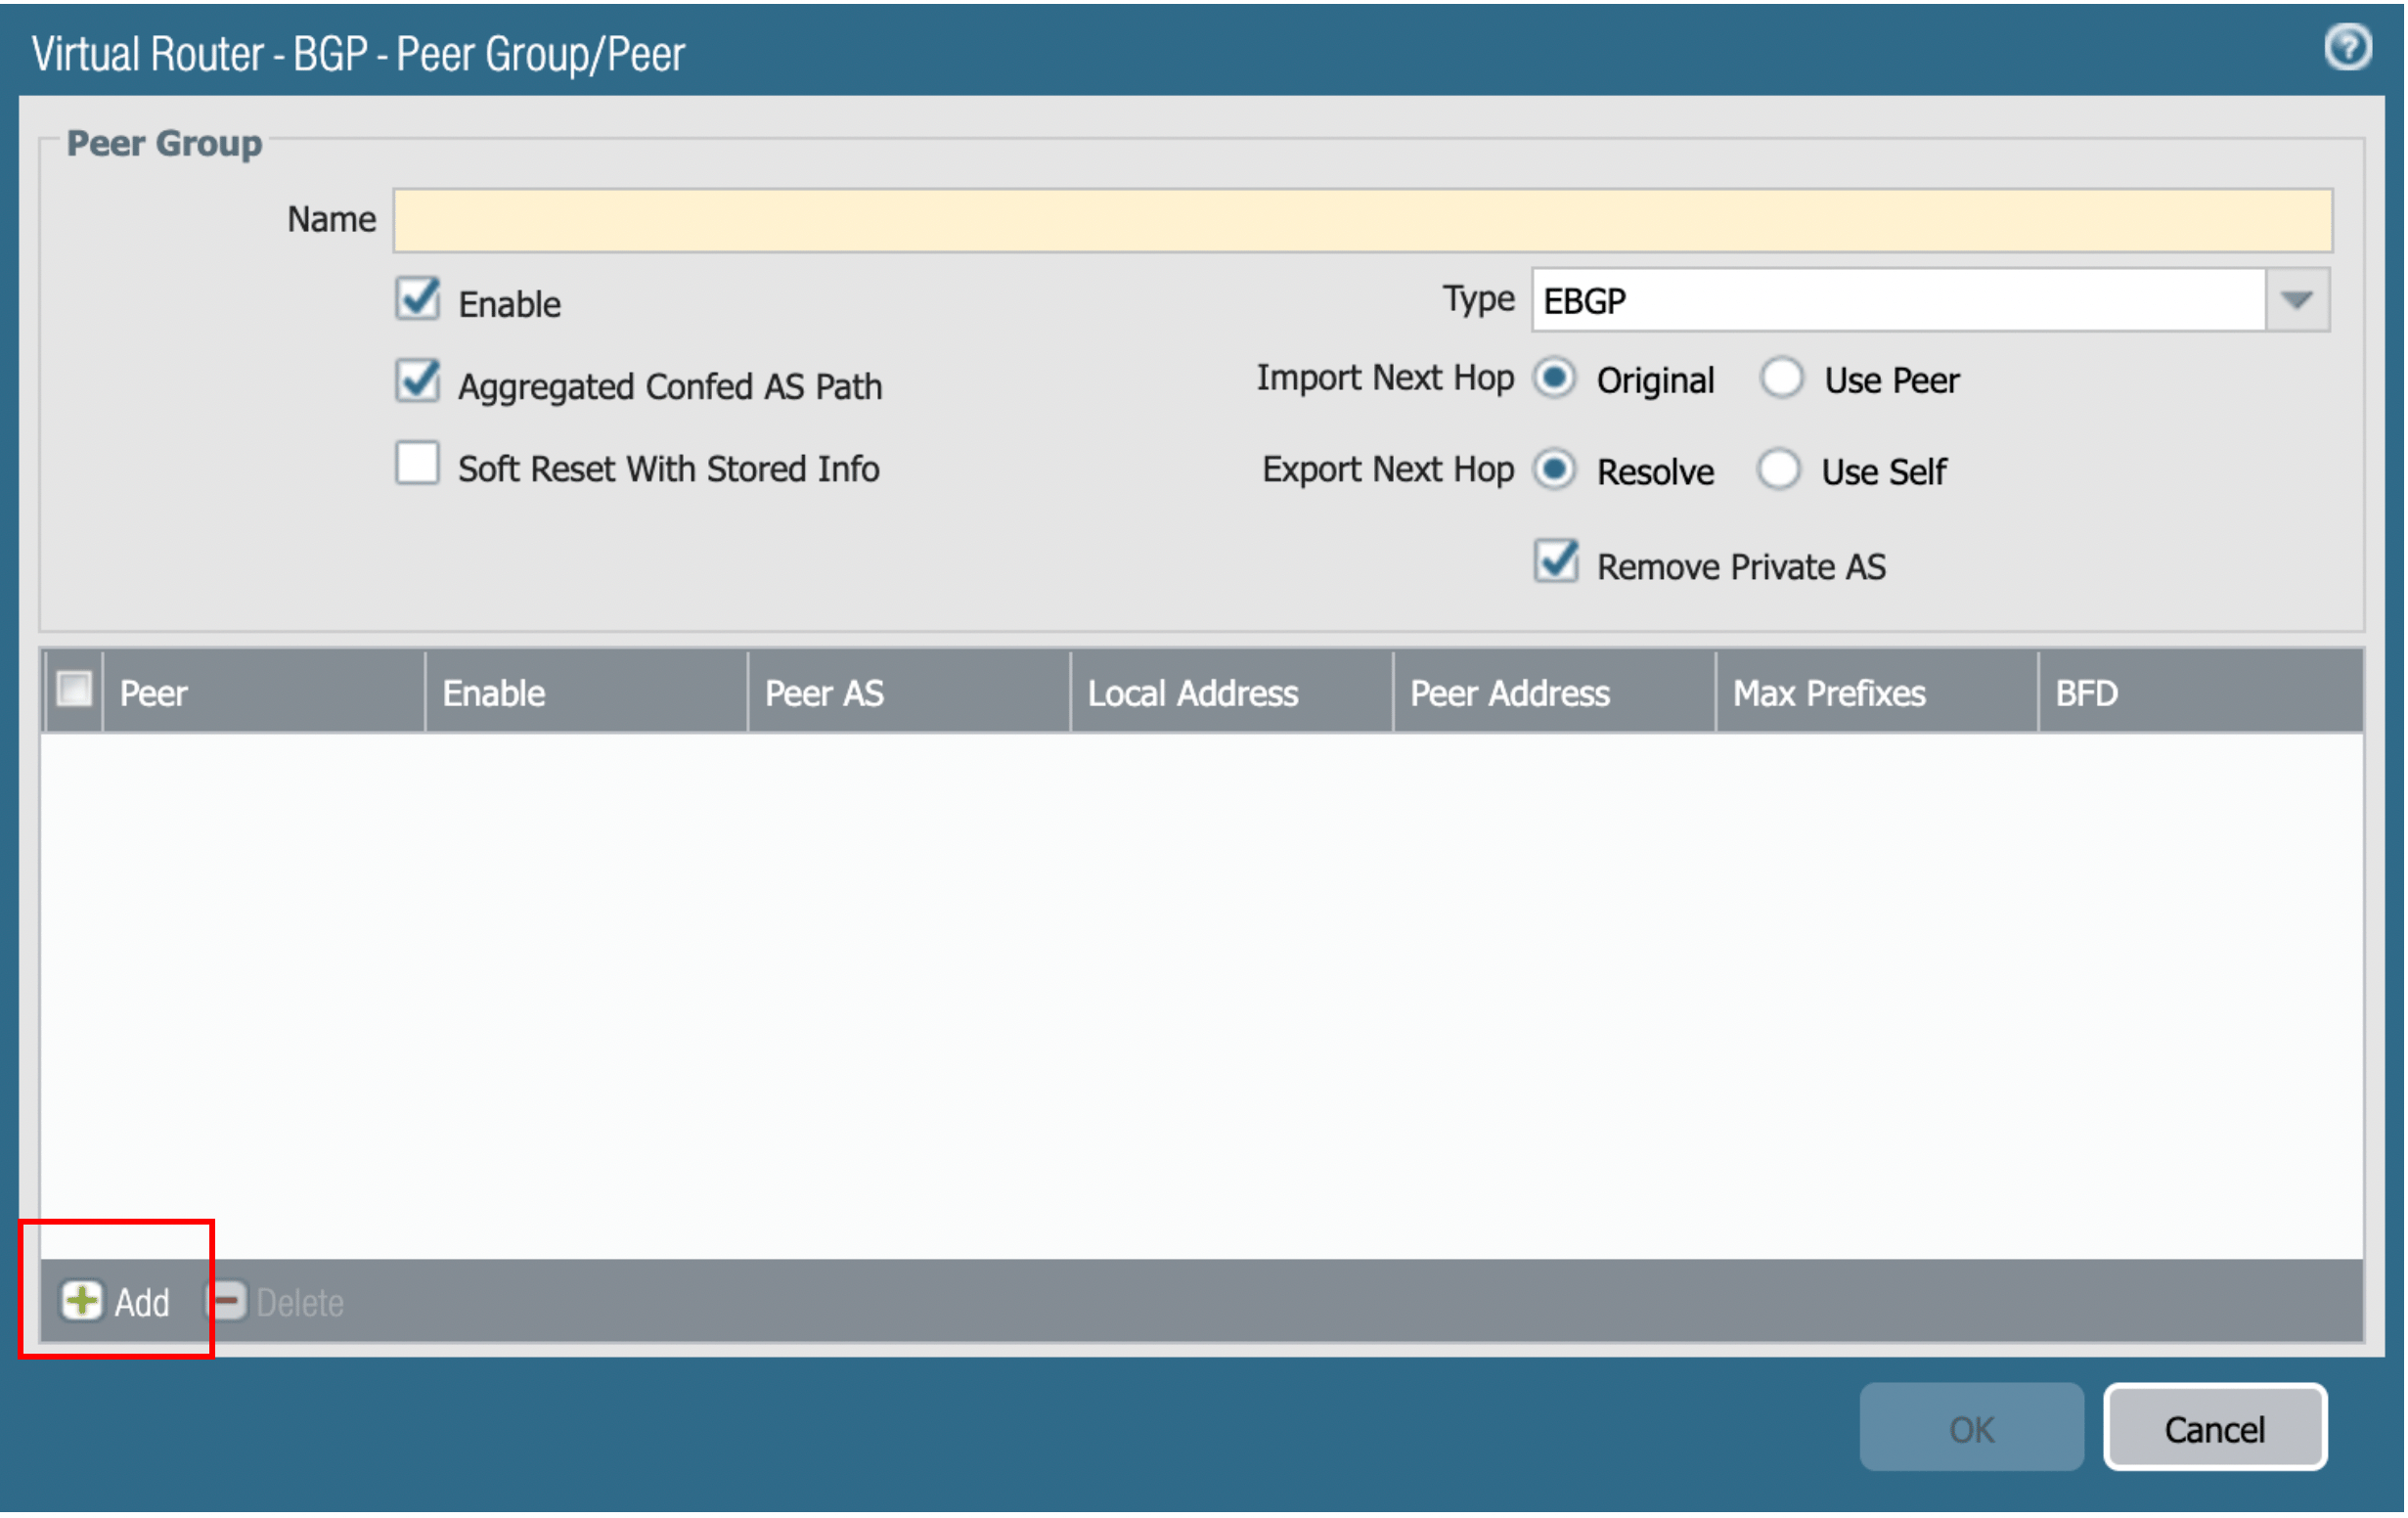
18. Steps to configure BGP: a. Navigate to Network > Virtual Routers. b. Click
    the 'default' link. c. In the Virtual Router - default dialog, click the BGP
    tab, and then the Peer Group tab. d. Click *Add*. e. Name the peer group
    (e.g bgppeering) and then click *Add* as shown to add BGP peering.
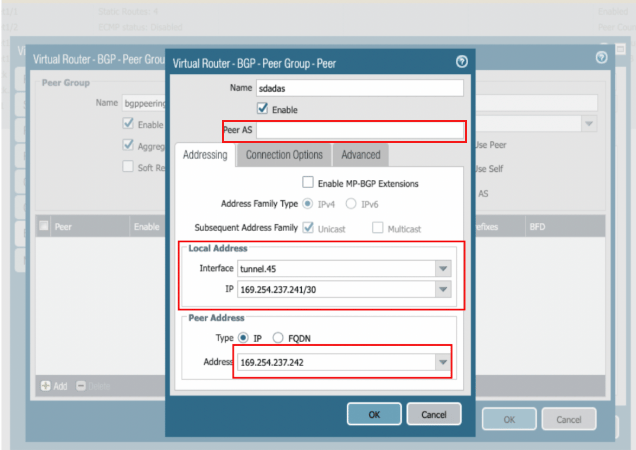
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp1.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=08a192ba0ad10e9278d948c7137a2868" alt="paloaltobgp1" width="2462" height="1552" data-path="images/guides/connectivity/vpn/paloaltobgp1.png" /> f. In the
    Virtual Router-BGP-Peer Group-Peer dialog, enter the information as shown in
    the below screenshot. Click *OK*.
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloalto13.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=27384010e899d35cf87f71a9aa4ab77d" alt="image14" width="636" height="450" data-path="images/guides/connectivity/vpn/paloalto13.png" />

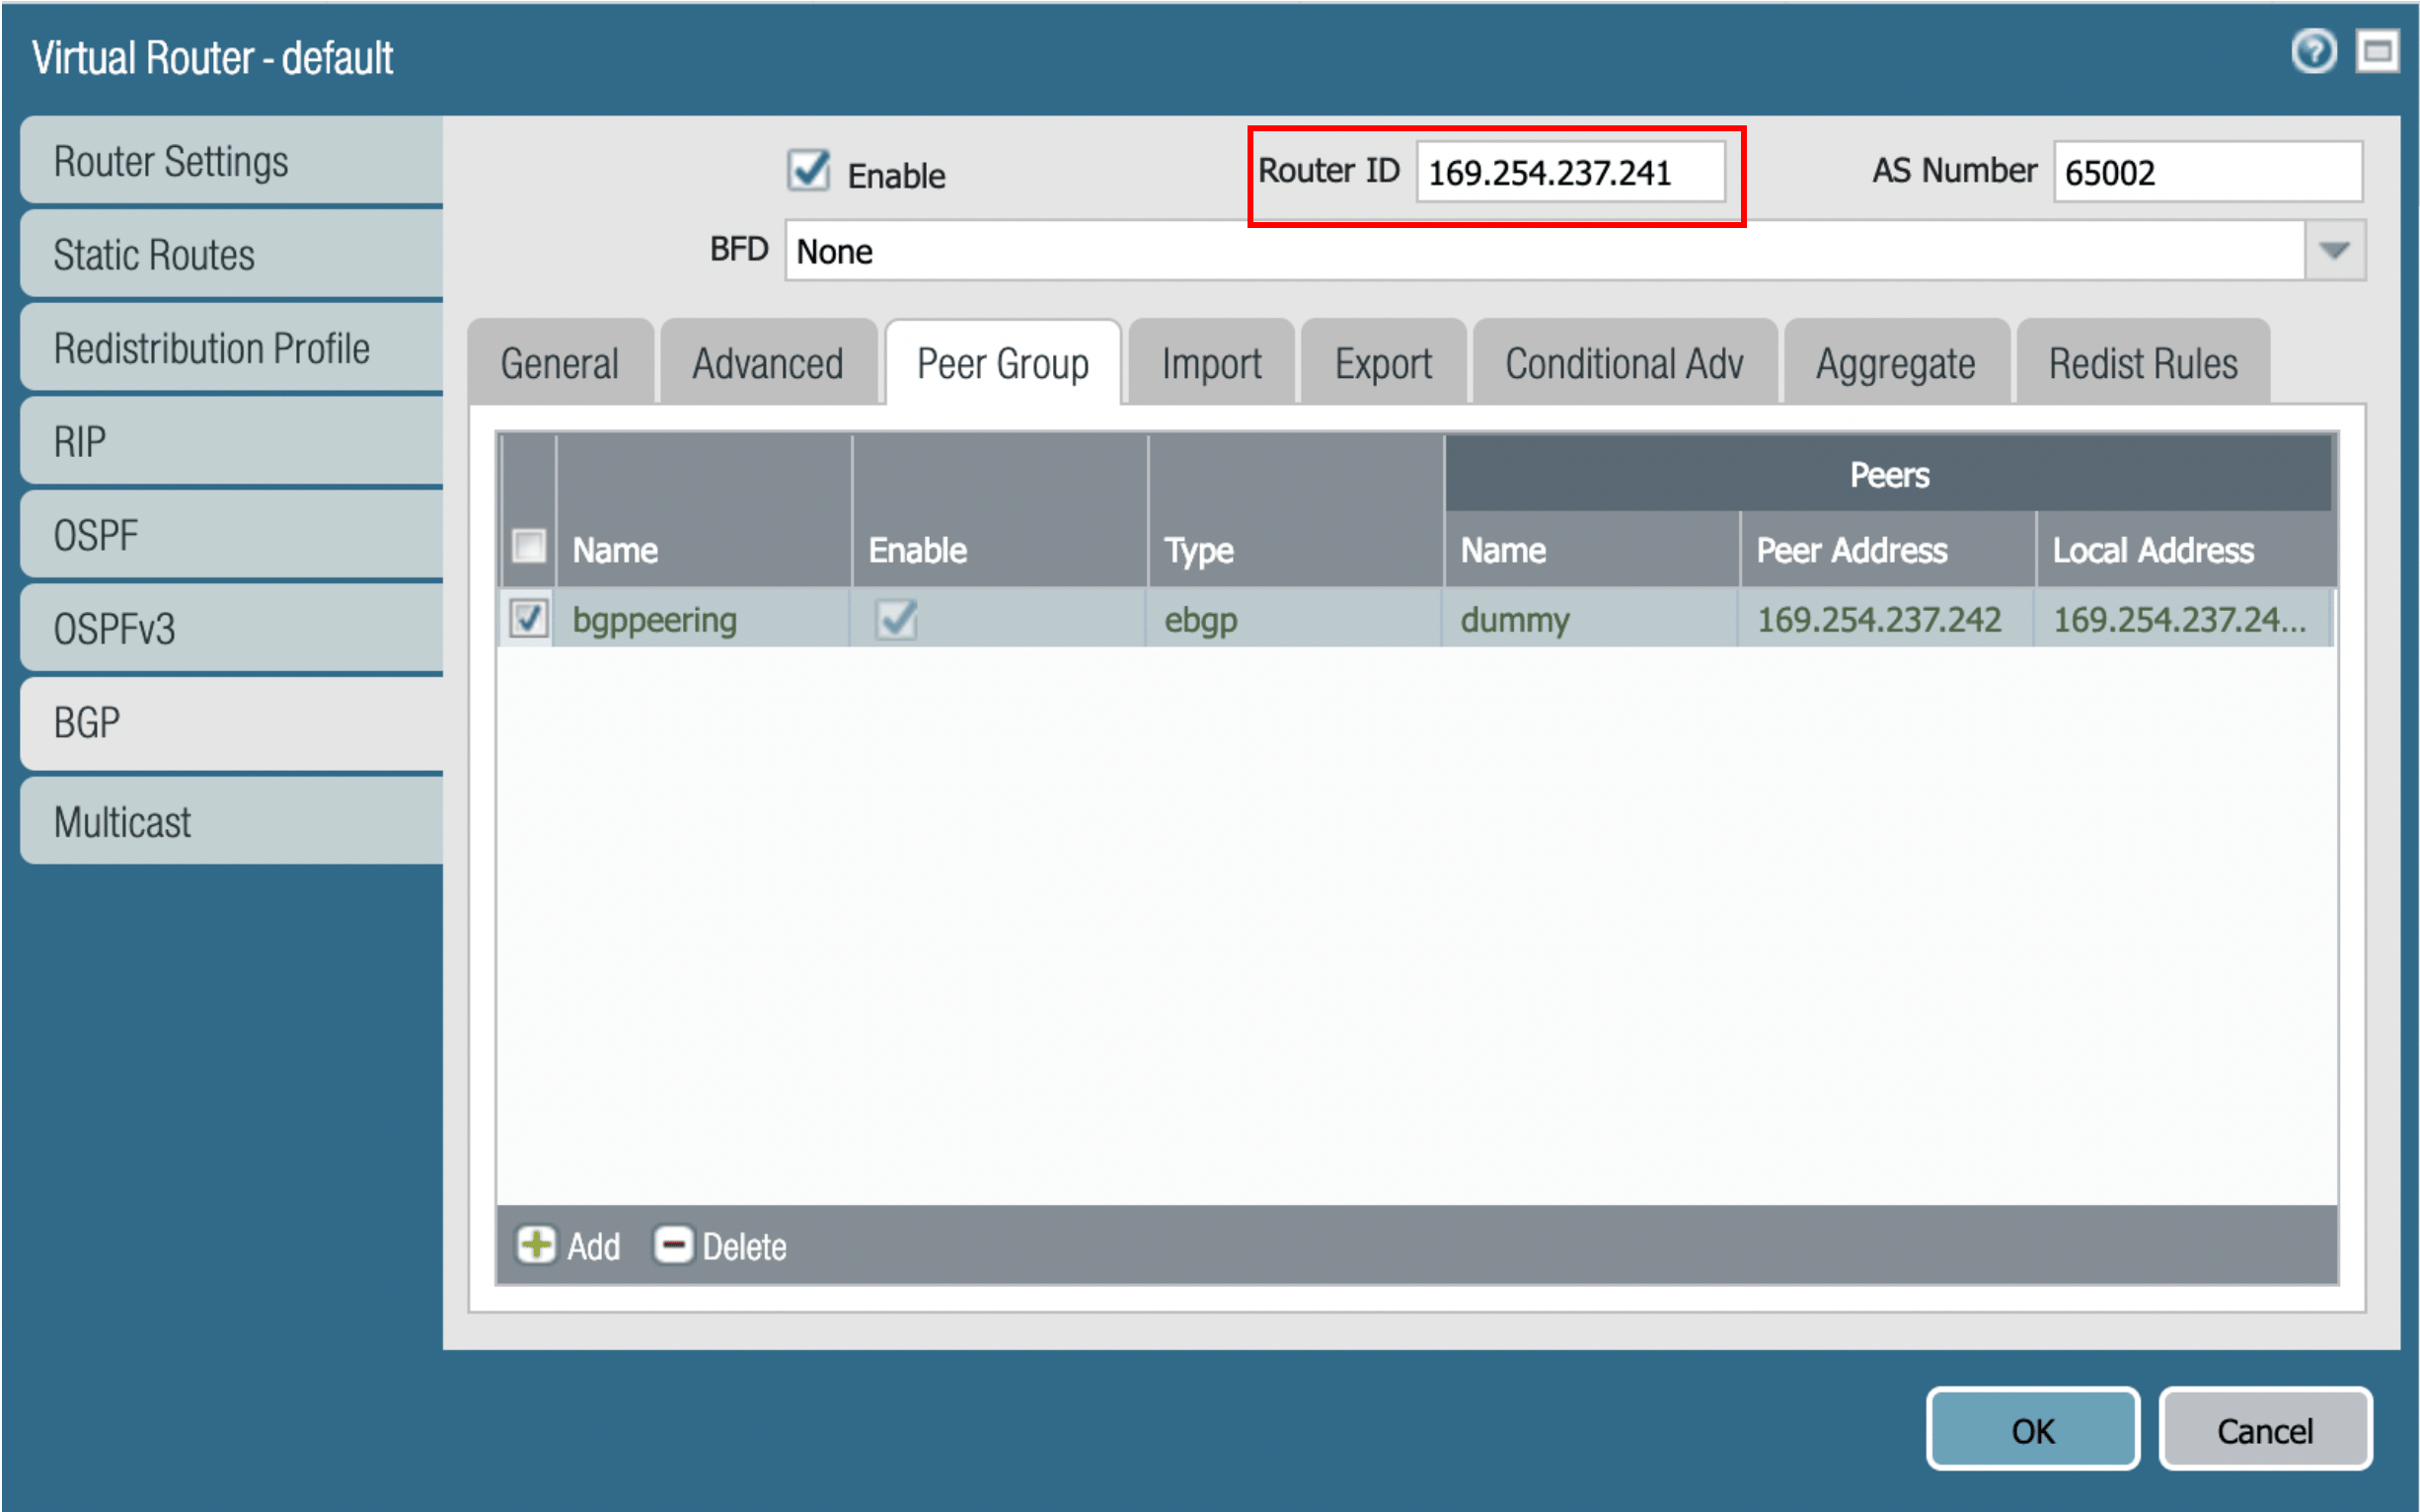
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp3.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=8f15f477674934eb50a066be4c3fe53e" alt="image15" width="2462" height="1560" data-path="images/guides/connectivity/vpn/paloaltobgp3.png" /> g. After
    everything is created, click *OK* to commit the configuration. The Router ID
    is taken from the downloaded config file (it should be the IP address of the
    tunnel created).
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp4.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=7db2e1ab990f1692fd8f0c938af2e099" alt="image16" width="2452" height="1532" data-path="images/guides/connectivity/vpn/paloaltobgp4.png" /> h. Click *OK*.
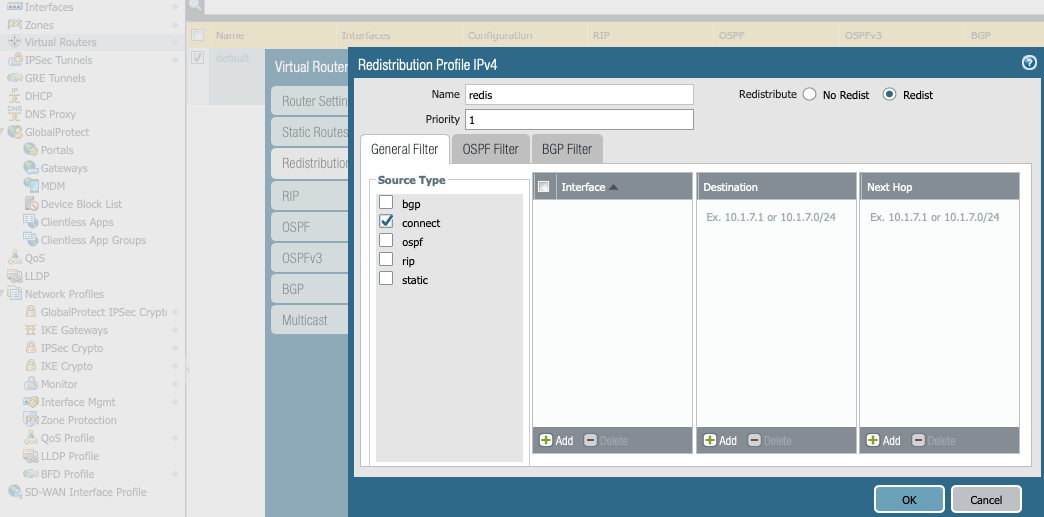
    i. Navigate to Network > default > Redistribution Profile. j. On the IPv4
    tab, click *Add*. k. In the *Name* field, enter 'redis'. l. Enter a
    priority. m. Select the *connect* Source Type to create a redistribution
    profile.
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp11.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=088d4115749891760e78523cb17a3ef7" alt="image12" width="1044" height="517" data-path="images/guides/connectivity/vpn/paloaltobgp11.png" />

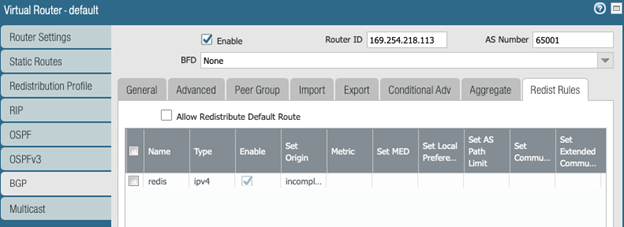
    n. Click *OK*. o. On the Virtual Router dialog, click BGP > Redist Rules. p.
    Click *Add* to add the redistribution rule you just created and click *OK*.
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp12.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=037b62bc6cd45d32411b9a0f88cd67ca" alt="image18" width="624" height="227" data-path="images/guides/connectivity/vpn/paloaltobgp12.png" />

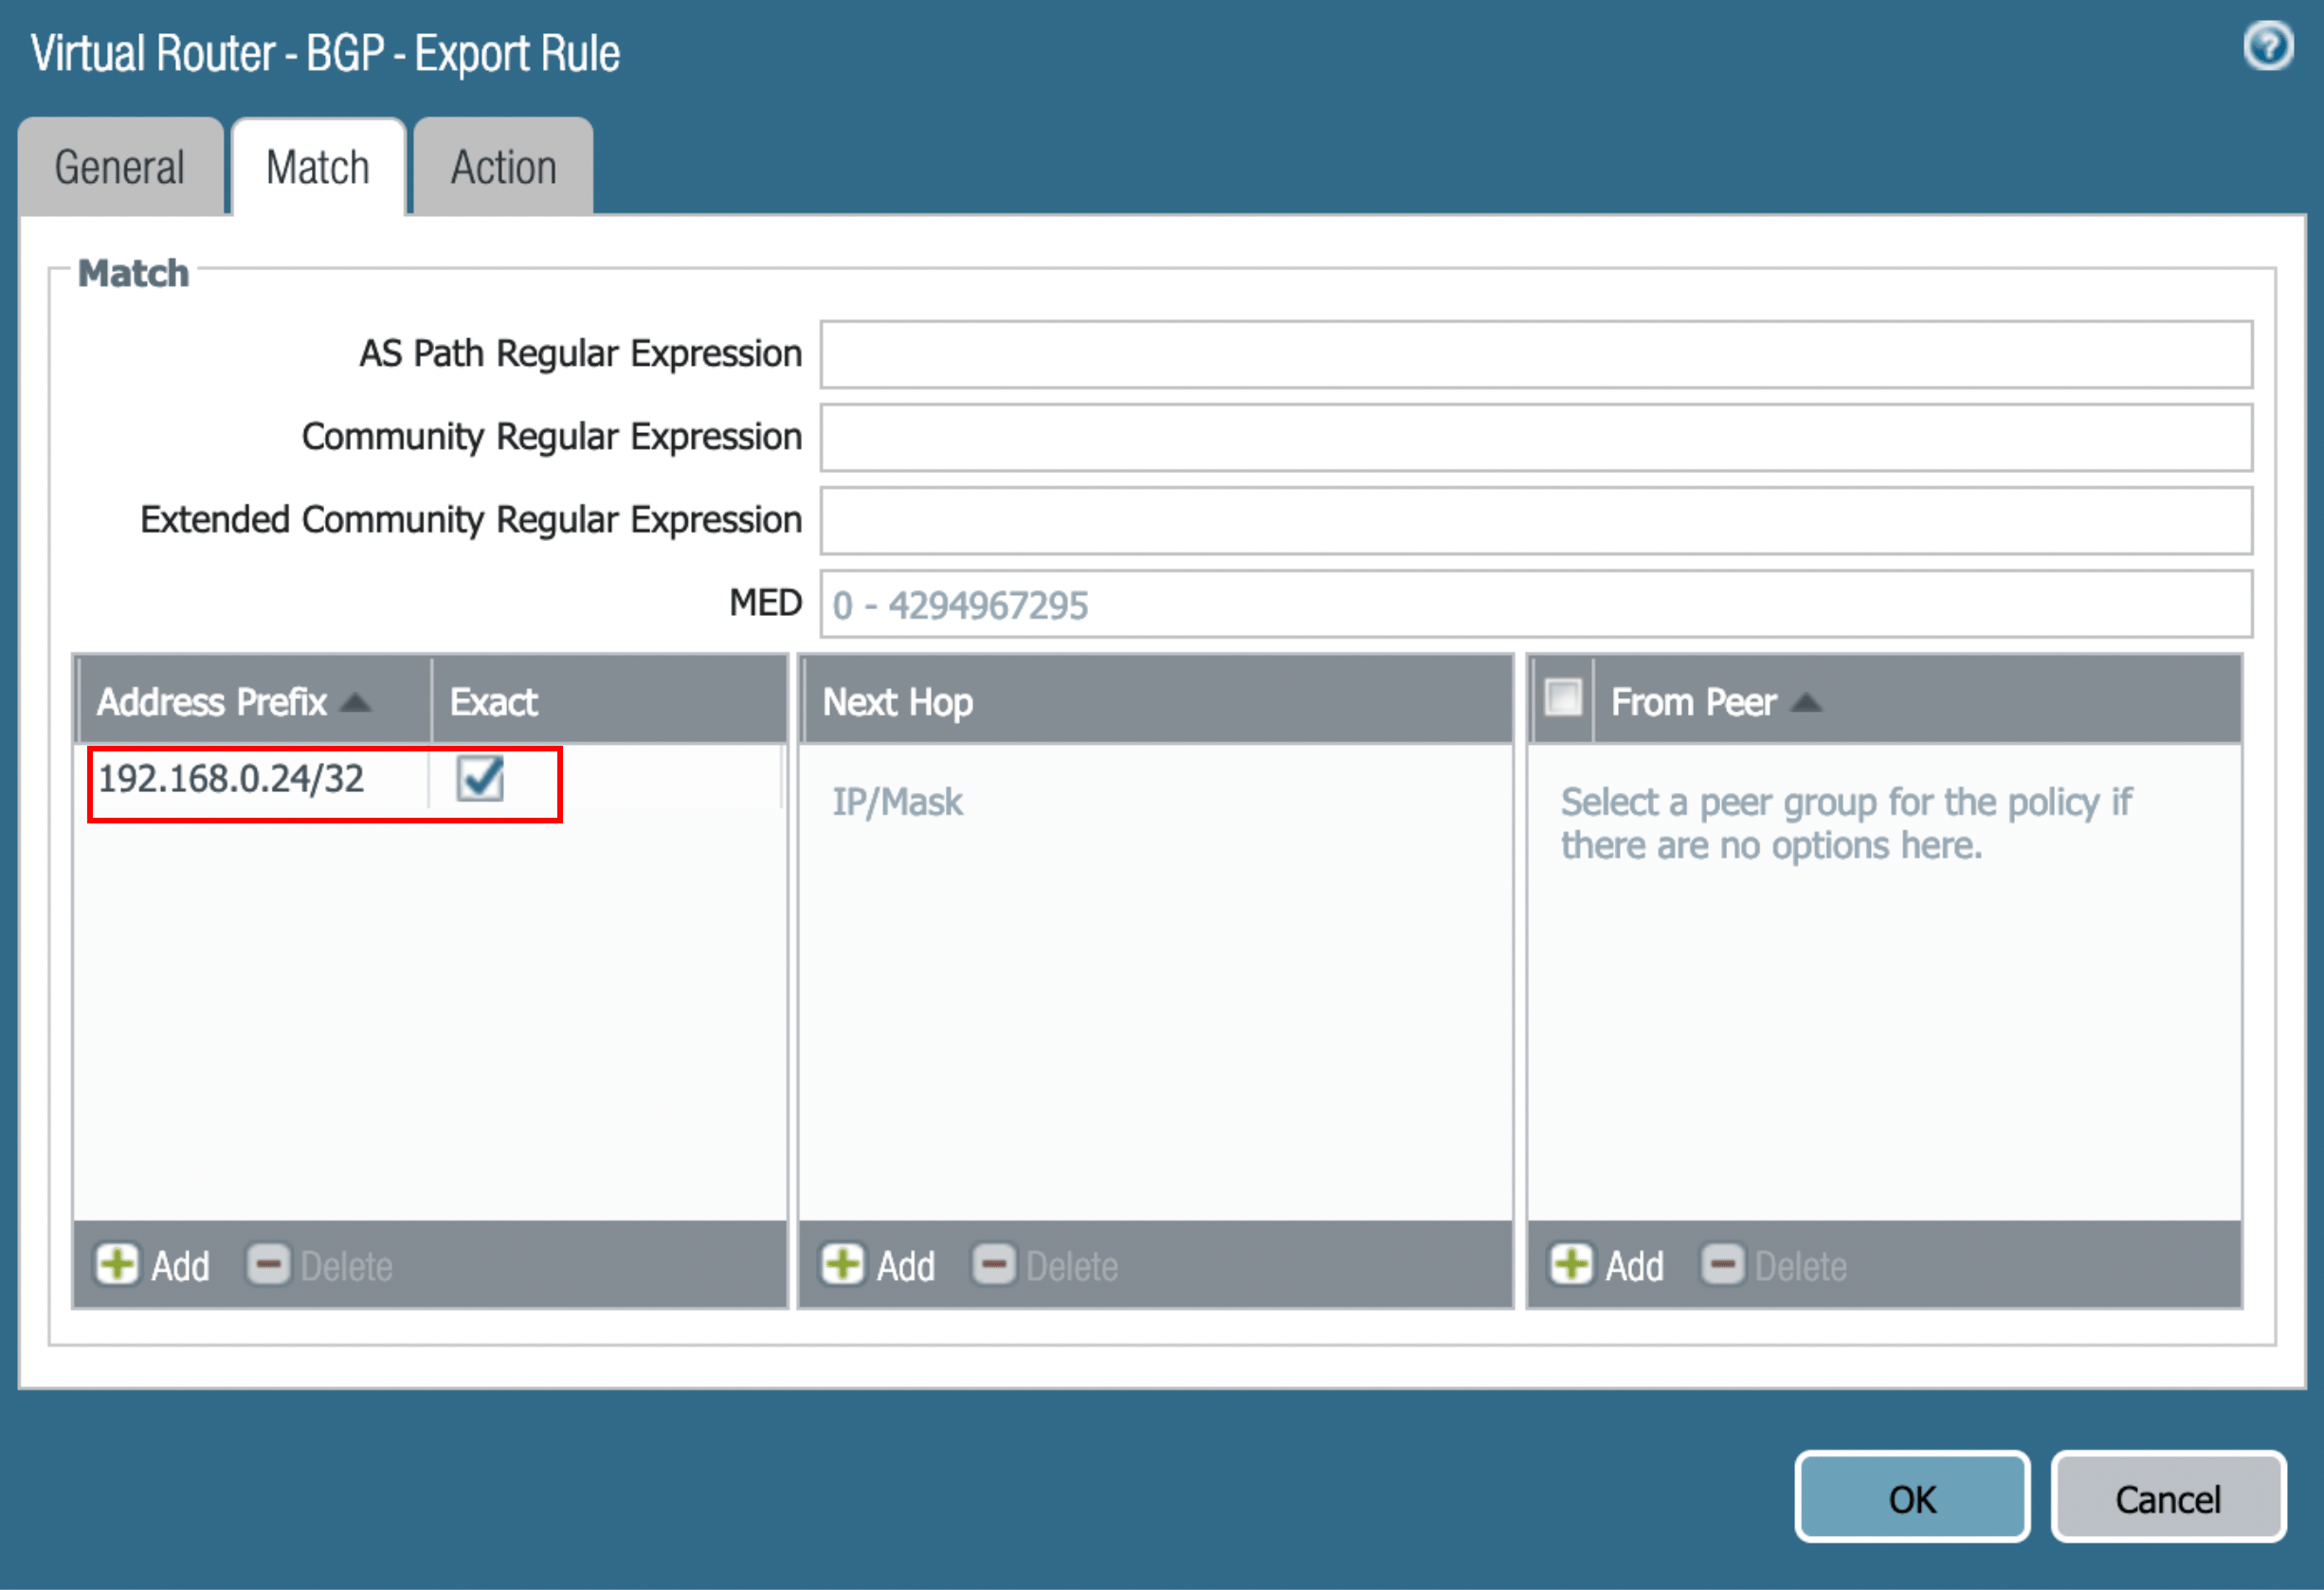
    q. On the same Virtual Router dialog, navigate to BGP > Export and click
    *Add*. r. In the Virtual Router - BGP - Export Rule dialog, add a name in
    the Rules field, and Enable the Export rule. s. Click *Add* to add the Peer
    Group from which the routes will be imported. Select Match and define the
    options used to filter routing information.
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp7.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=4e94faafde3d95cb511082bb11ff591d" alt="image19" width="2452" height="1678" data-path="images/guides/connectivity/vpn/paloaltobgp7.png" />

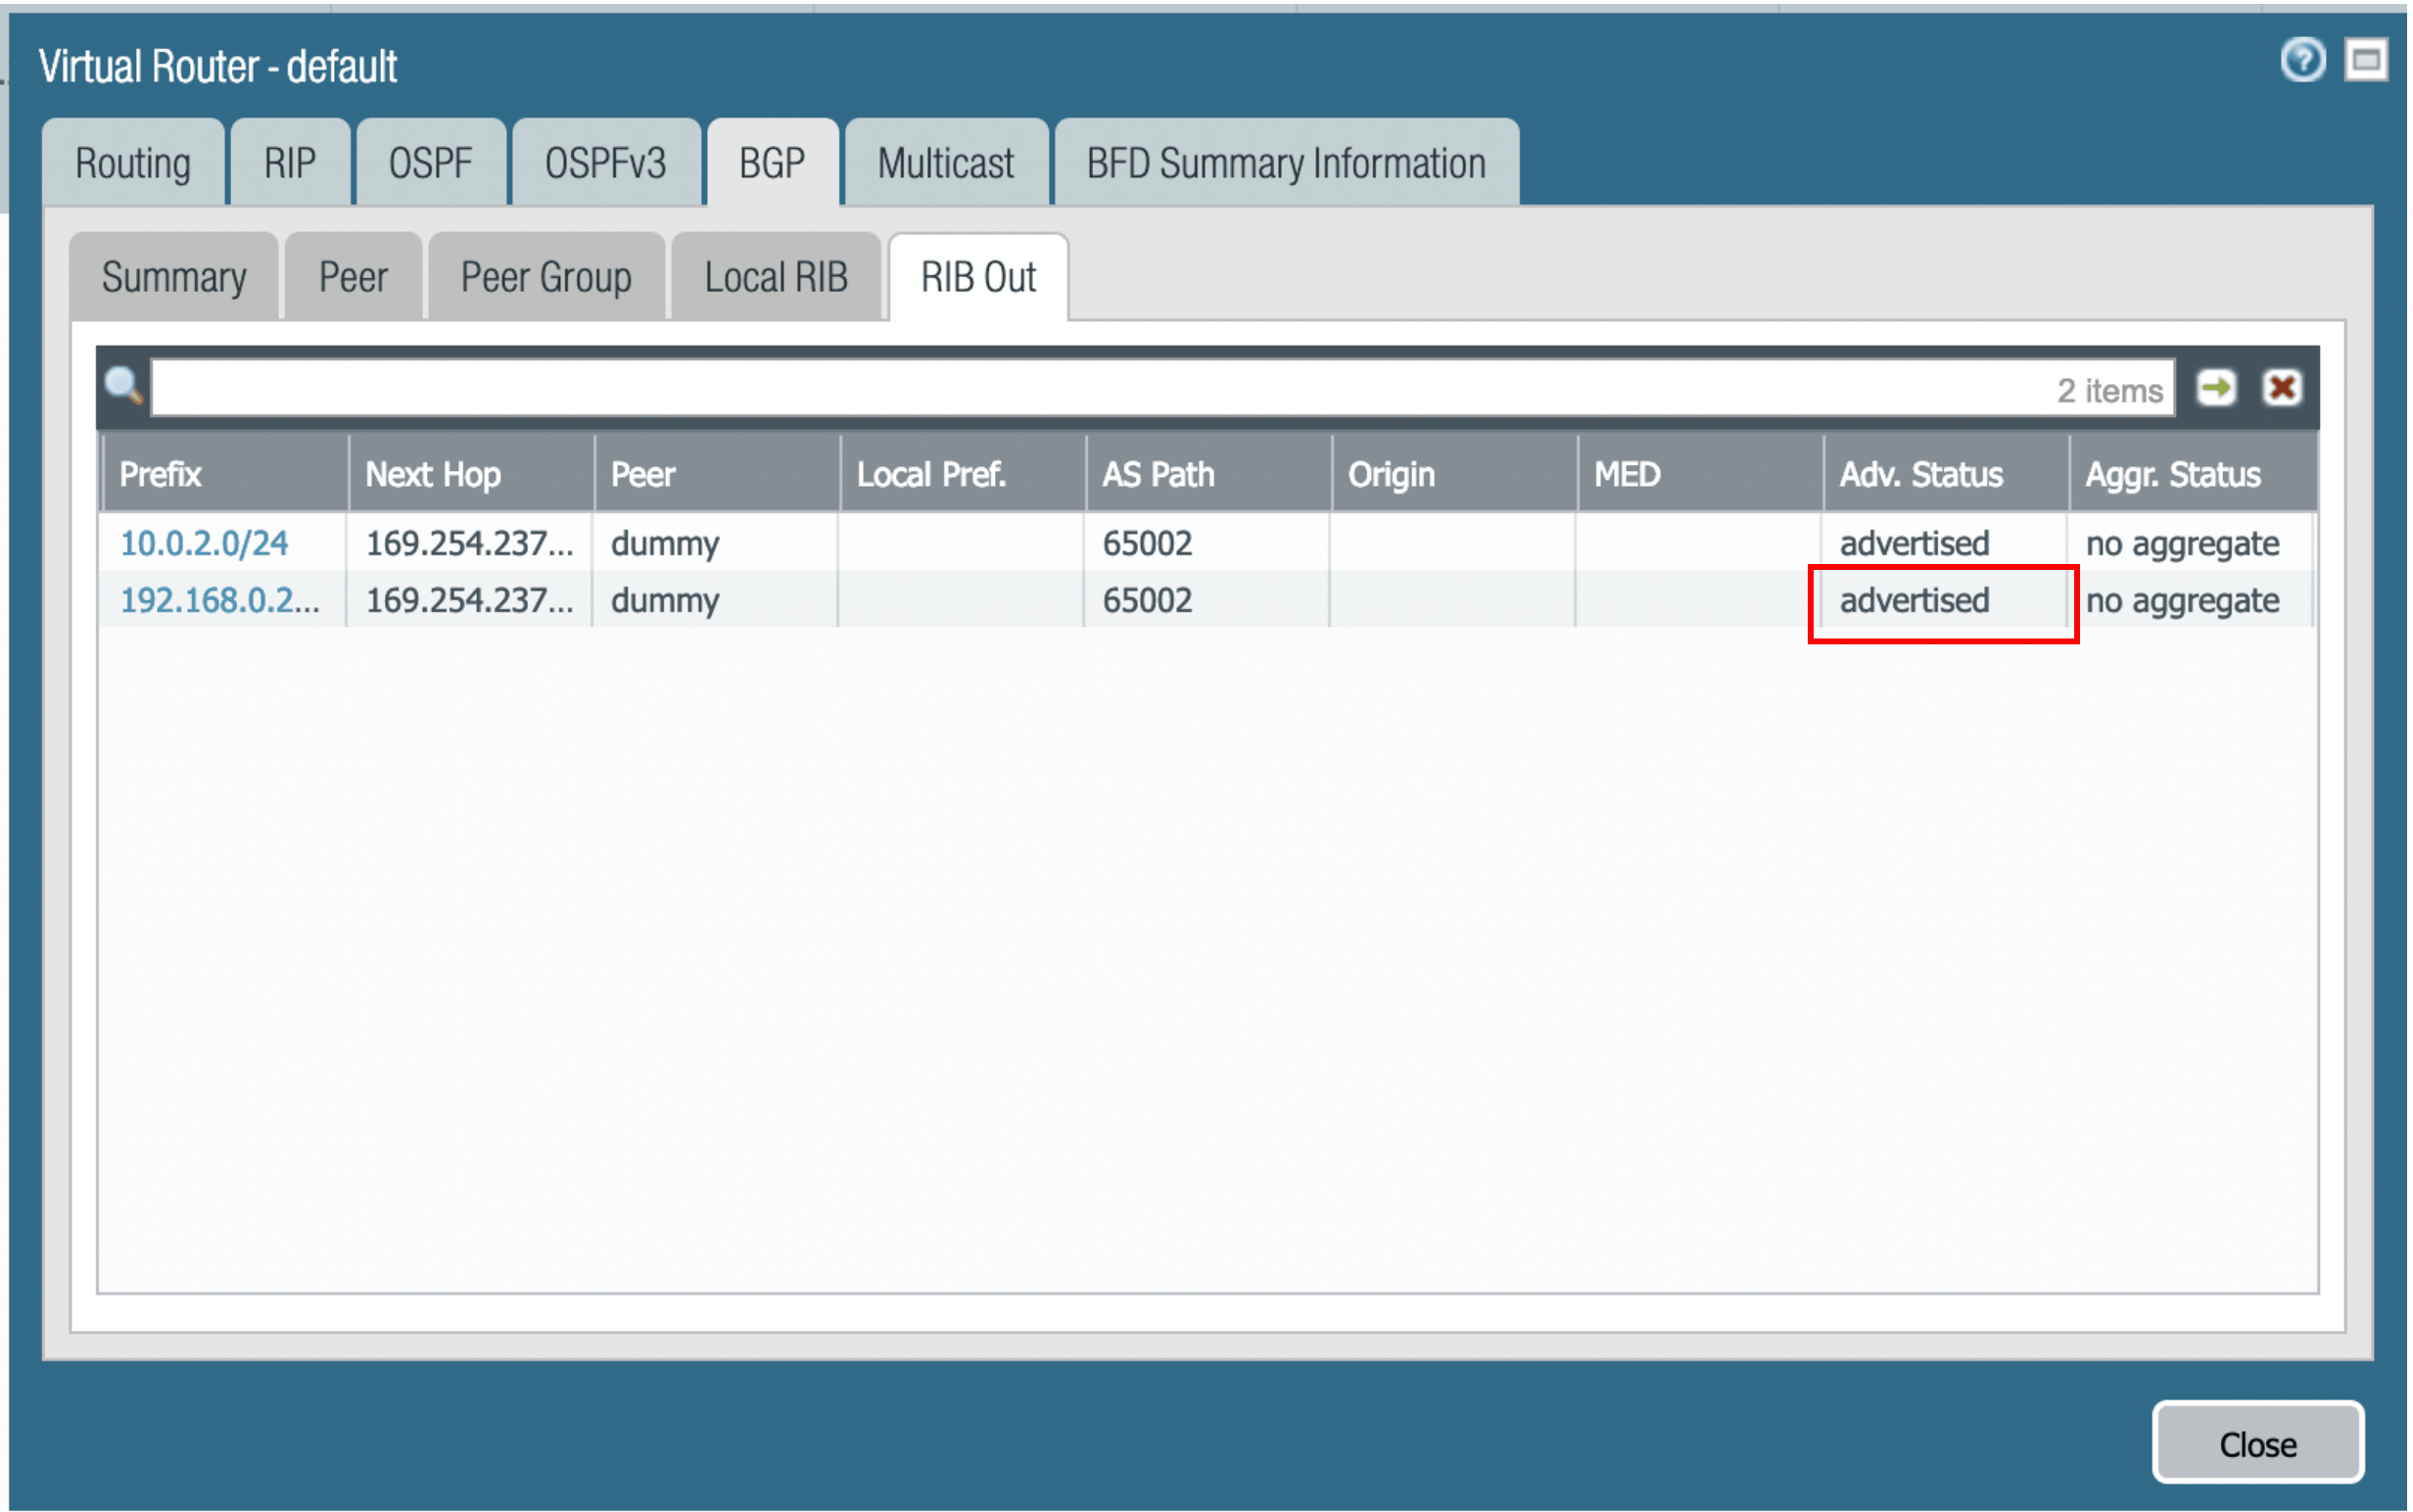
    t. Click *OK*. u. After the BGP route has been advertised it looks like the
    following image. Navigate to Network → More runtime stats → BGP → RIB out.
    <img src="https://mintcdn.com/aviatrix-14b37c43/Gre8pdluiL7JmlpL/images/guides/connectivity/vpn/paloaltobgp8.png?fit=max&auto=format&n=Gre8pdluiL7JmlpL&q=85&s=941a9ff6cc7a8757e2a1a14e9dddd404" alt="image20" width="2464" height="1544" data-path="images/guides/connectivity/vpn/paloaltobgp8.png" />

19. In the AWS portal, configure the VPC Route Table associated with the private
    subnet of VPC2. Add a route with VPC1 private subnet as the destination and
    Palo Alto Networks VM LAN port as the gateway.

20. In CoPilot, go to Diagnostics > Diagnostic Tools > BGP Diagnostics.

21. Select the gateway name from the dropdown list.

22. In the Command field, enter the 'show Ip bgp' command.

23. Click *Run* to verify the BGP Routes.