> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Aviatrix Gateway to FortiGate
> This document describes how to configure an IPsec tunnel between an Aviatrix Gateway and a FortiGate firewall using Aviatrix Site2Cloud. This task is divided into two parts:
This document describes how to configure an IPsec tunnel between an Aviatrix
Gateway and a FortiGate firewall using Aviatrix Site2Cloud. This task is divided
into two parts:
1. Configure a [Site2Cloud tunnel](#setting-up-external-s2c-connection) in
Aviatrix CoPilot.
2. Configure a [VPN tunnel](#fortigate-configuration) and related components in
the FortiGate Firewall.
## Setting up External (S2C) Connection
1. In Aviatrix CoPilot, launch an
Aviatrix Transit Gateway
.
2. Navigate to Networking > Connectivity > External Connections (S2C) and click
*Add New* to create a Site2Cloud connection using the values for one of the
below options (for either you can select either PSK or certificate-based
authentication).
* [Static Route-Based](https://legacy.docs.aviatrix.com/documentation/latest/network/external-connection-create-static-route-based-unmapped.html)
* [Static Policy-Based](https://legacy.docs.aviatrix.com/documentation/latest/network/external-connection-create-static-policy-based-unmapped.html)
3. After the connection is created, select the vertical ellipsis
 menu for
that connection and select *Download Configuration*.
4. Select *Generic* from the *Vendor* dropdown list and click the *Download* to
download the external (S2C) configuration. Use this configuration file to
configure the tunnels and interfaces in your Fortinet FortiGate firewall.
## FortiGate Configuration
The configuration and screenshots below make the following three assumptions:
* There are two interfaces on the FortiGate:
* Interface port1 is an externally facing interface.
* Interface port2 is an internally facing interface.
* You have a subnet in AWS, Azure, or GCP in a VPC/VNet that has an Aviatrix
Gateway. This subnet is defined as "10.0.0.0/16" for the examples below but it
can be any valid CIDR range.
In the examples below this range is referred to as *AWS\_Cloud*.
* You have a subnet behind your FortiGate firewall that will be accessible in
the cloud. This subnet is defined as "172.16.0.0/20" in the examples below but
it can be any valid CIDR range.
In the examples below, this range is referred to as *Shared\_With\_AWS*.
### Configuring Named Address Ranges in FortiGate
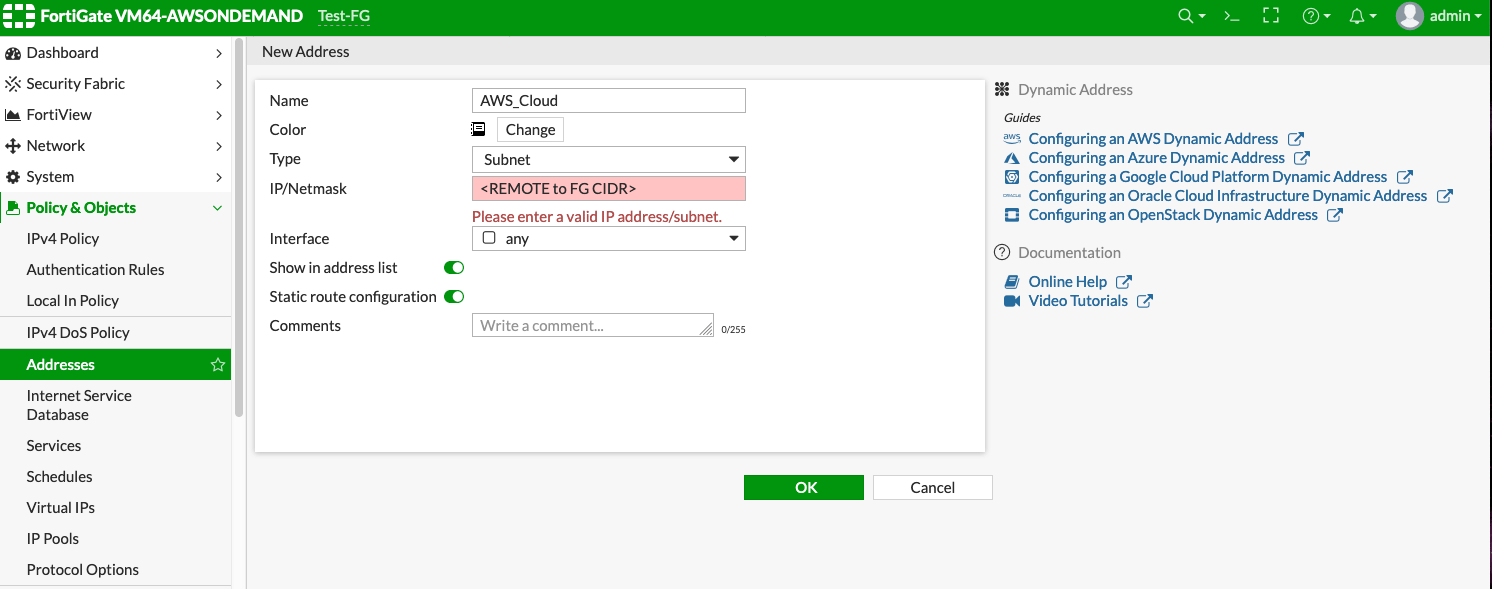
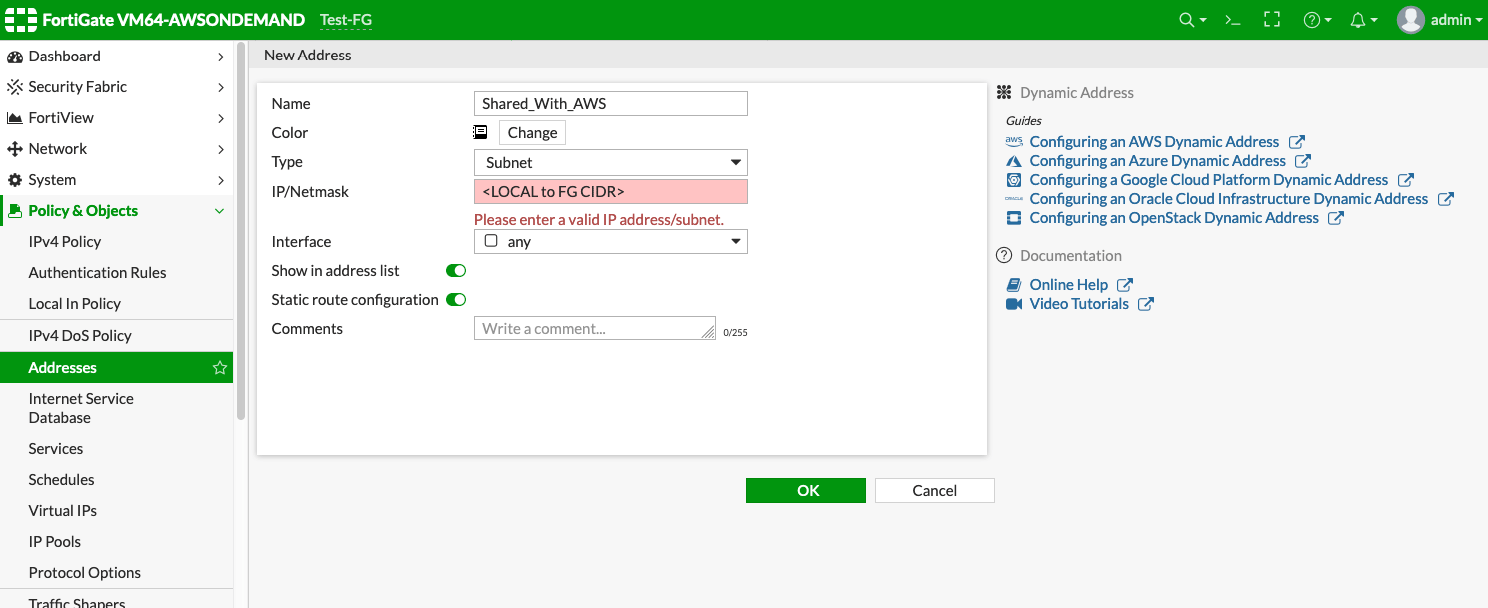
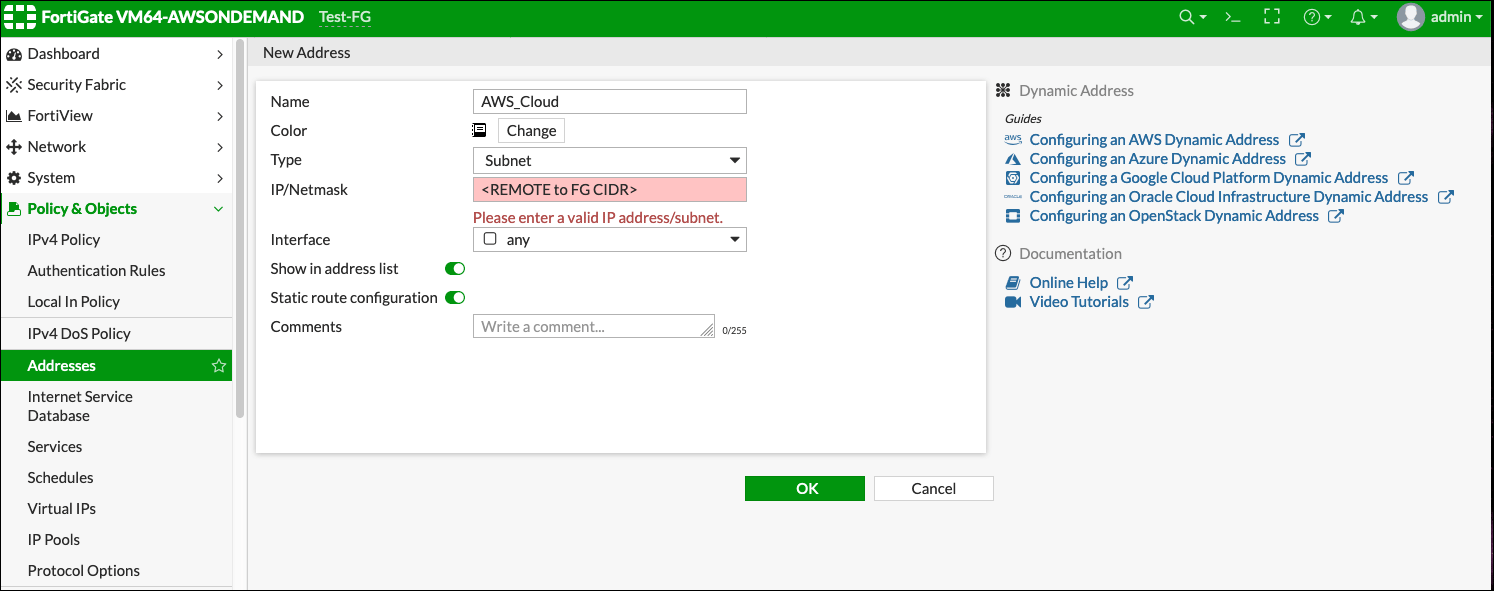
Access the FortiGate Dashboard. Under *Policy & Objects* > *Addresses*, create
two new addresses: AWS\_Cloud and Shared\_With\_AWS.
#### AWS\_Cloud
| Field | Expected Value |
| -------------------------- | ------------------------------------------------------------------------------- |
| Name | AWS\_Cloud |
| Type | Subnet |
| Subnet / IP Range | CIDR matching the range specified in tunnel configuration (remote to FortiGate) |
| Interface | Any |
| Show in Address List | Enabled |
| Static Route Configuration | Enabled |
 #### Shared\_With\_AWS
| Field | Expected Value |
| -------------------------- | ------------------------------------------------------------------------------ |
| Name | Shared\_With\_AWS |
| Type | Subnet |
| Subnet / IP Range | CIDR matching the range specified in tunnel configuration (local to FortiGate) |
| Interface | Any |
| Show in Address List | Enabled |
| Static Route Configuration | Enabled |
 ### Creating an IPsec Tunnel on FortiGate
1. Log in to the FortiGate and access the Dashboard.
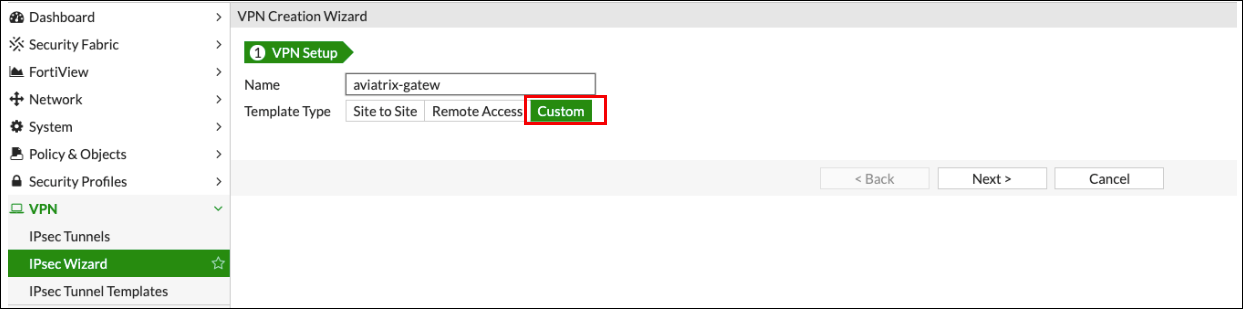
2. In the VPN menu, select *IPsec Wizard*.
3. Change the Template Type to "Custom."
4. Enter any value as the Name. For this example, we are using "aviatrix-gatew."
5. Click *Next >*.
6. Fill out the Network fields as recommended below:
| Field | Expected Value |
| ------------- | ---------------------------- |
| Name | aviatrix-gatew (for example) |
| Template Type | Custom |
 ### New VPN Tunnel Tab
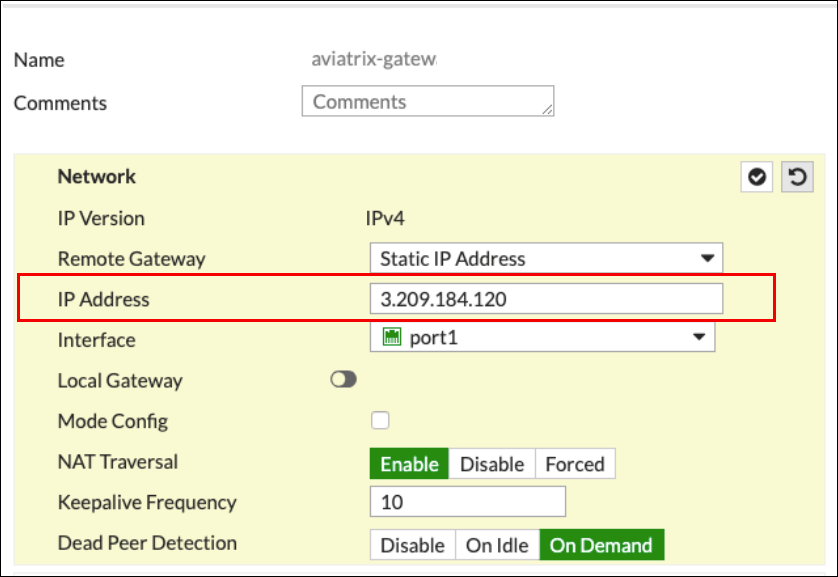
Complete the Network fields on the New VPN Tunnel tab as follows:
*Network section of New VPN Tunnel Tab*
| Field | Expected Value |
| ------------------------ | ------------------------------------- |
| IP Version | IPv4 |
| Remote Gateway | Static IP Address |
| IP Address | Public IP address of Aviatrix Gateway |
| Interface | Select the Appropriate Port/Interface |
| Local Gateway | Disabled |
| Mode Config | Unmark this checkbox |
| NAT Traversal | Enable |
| Keepalive Frequency | Any value |
| Dead Peer Detection | On Demand |
| Forward Error Correction | Unmark this checkbox |
| Advanced Options | Disabled |
 *Authentication section of New VPN Tunnel Tab*
| Field | Expected Value |
| -------------- | ----------------------------------------------------------------------------------------------------------- |
| Method | Pre-shared Key |
| Pre-shared Key | Enter the value from the downloaded configuration or the value typed in to the field in Aviatrix Site2Cloud |
| IKE Version | 1 |
| IKE Mode | Main (ID protection) |
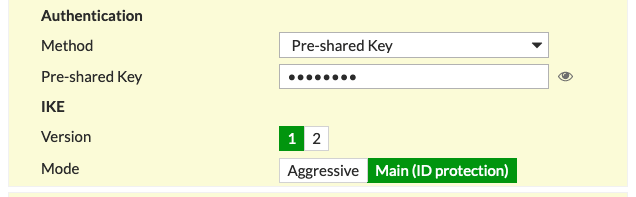 *Phase 1 Proposal section of New VPN Tunnel Tab*
| Field | Expected Value |
| ---------------------- | ---------------------------------------------------------------------------- |
| Encryption | Match value specified in Aviatrix S2C configuration (Phase 1 Encryption) |
| Authentication | Match value specified in Aviatrix S2C configuration (Phase 1 Authentication) |
| Diffie-Hellman Group | Match value specified in Aviatrix S2C configuration (Phase 1 DH Groups) |
| Key Lifetime (seconds) | 28800 |
| Local ID | Leave Blank |
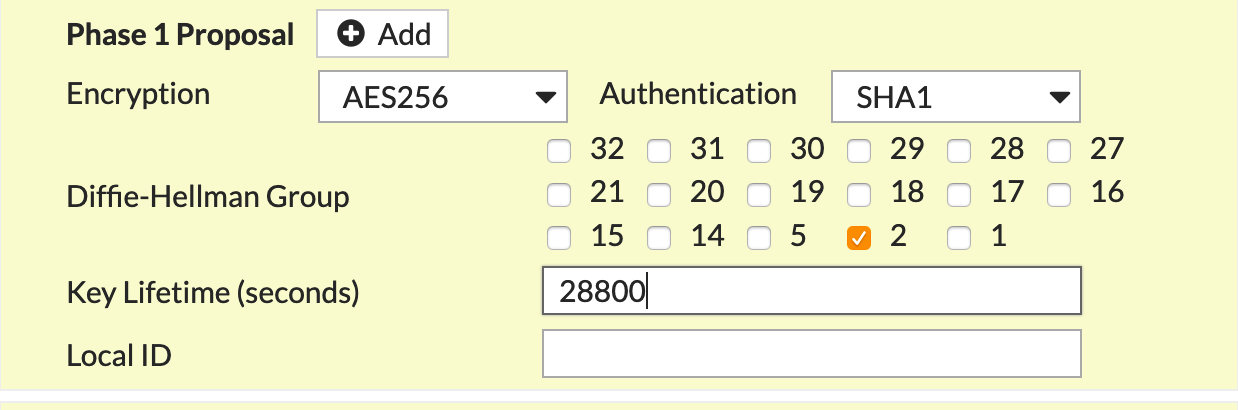 *XAUTH section of New VPN Tunnel Tab*
| Field | Expected Value |
| ----- | -------------- |
| Type | Disabled |
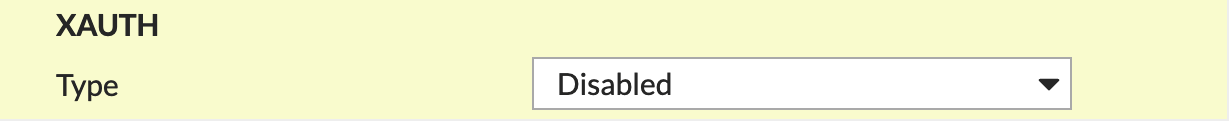 *Phase 2 Selectors > New Phase 2 seciton of New VPN Tunnel Tab*
| Field | Expected Value |
| -------------- | ----------------------------------- |
| Name | Any String Value |
| Comments | Any String Value |
| Local Address | Named Address - *Shared\_With\_AWS* |
| Remote Address | Named Address - *AWS\_Cloud* |
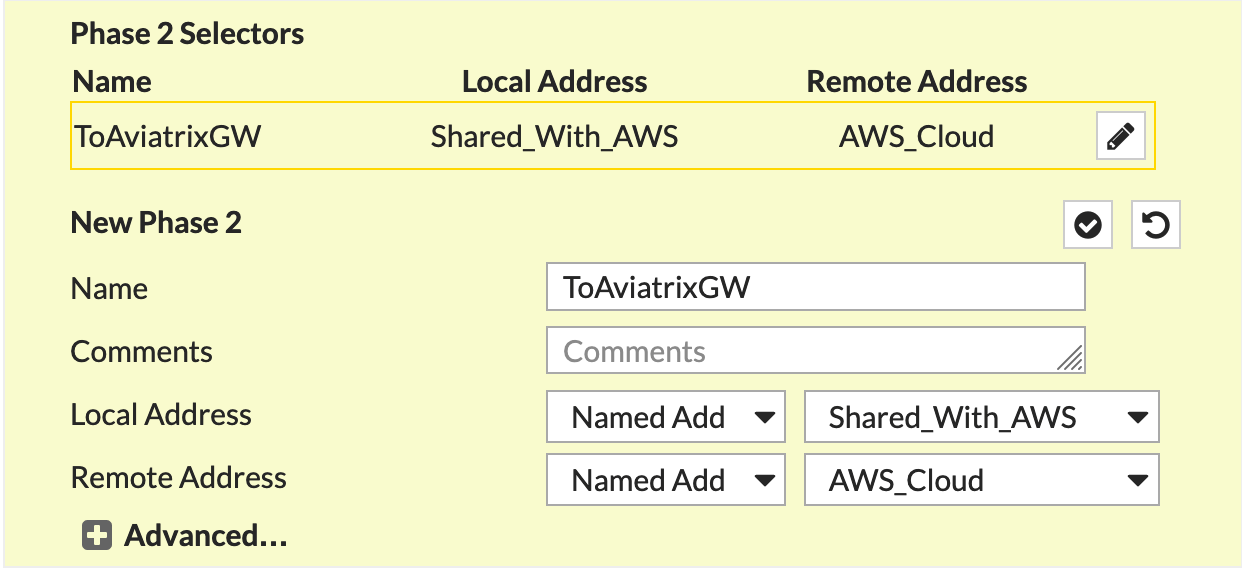 *Advanced section of New VPN Tunnel Tab*
Obtain the values from the downloaded configuration file.
| Field | Expected Value |
| ---------------------- | ---------------------------------------------------------------------------- |
| Encryption | Match value specified in Aviatrix S2C configuration (Phase 2 Encryption) |
| Authentication | Match value specified in Aviatrix S2C configuration (Phase 2 Authentication) |
| Diffie-Hellman Group | Match value specified in Aviatrix S2C configuration (Phase 2 DH Groups) |
| Key Lifetime (seconds) | 3600 |
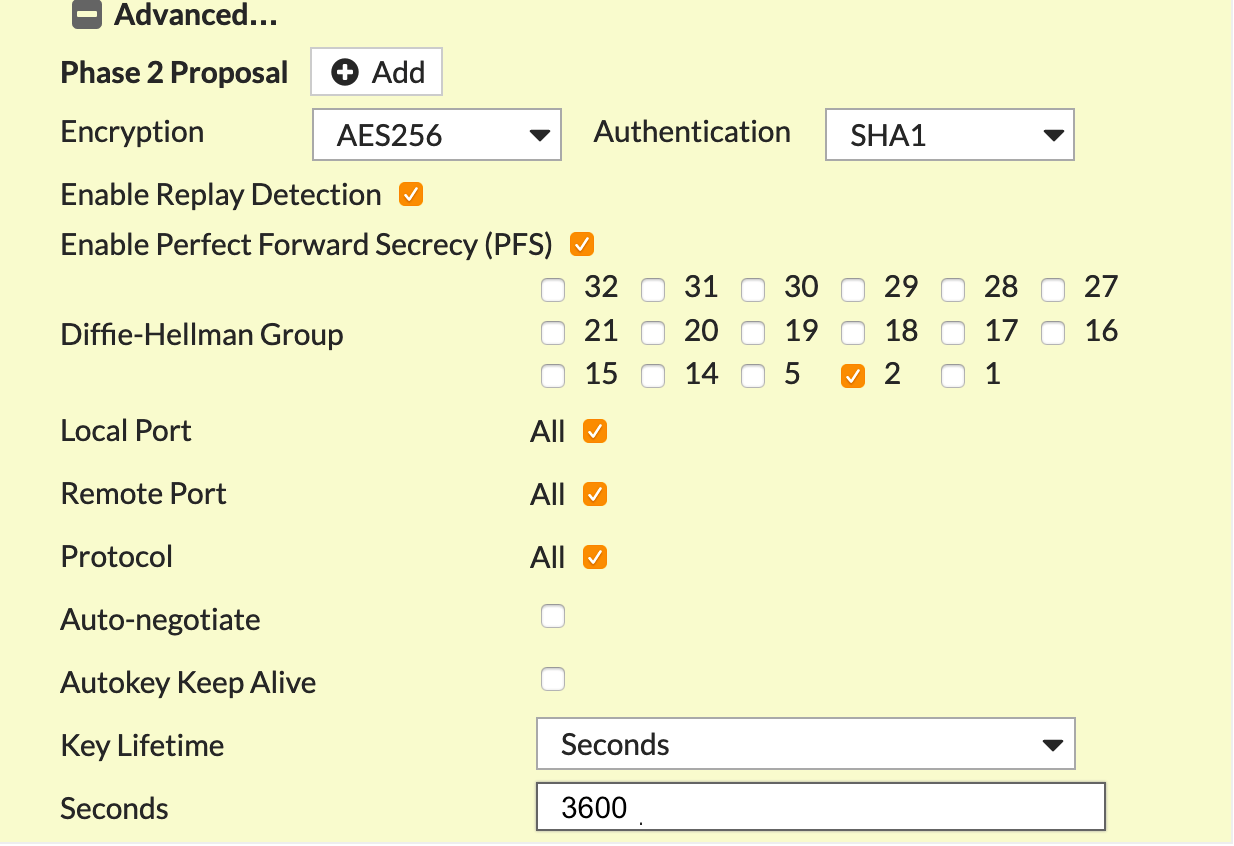 7. Click *OK*.
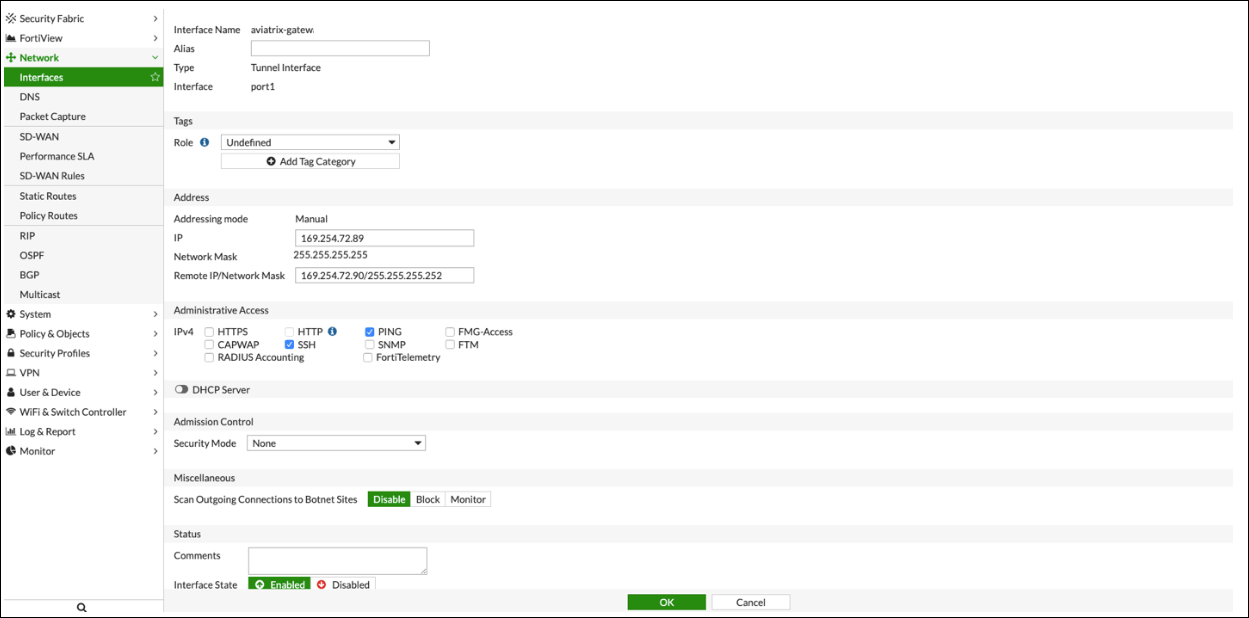
8. Navigate to Network > Interfaces.
9. Click on the Tunnel created above (e.g. aviatrix-gatew) and assign the IP
address from the downloaded configuration file.
 ### Configure IPv4 Policy
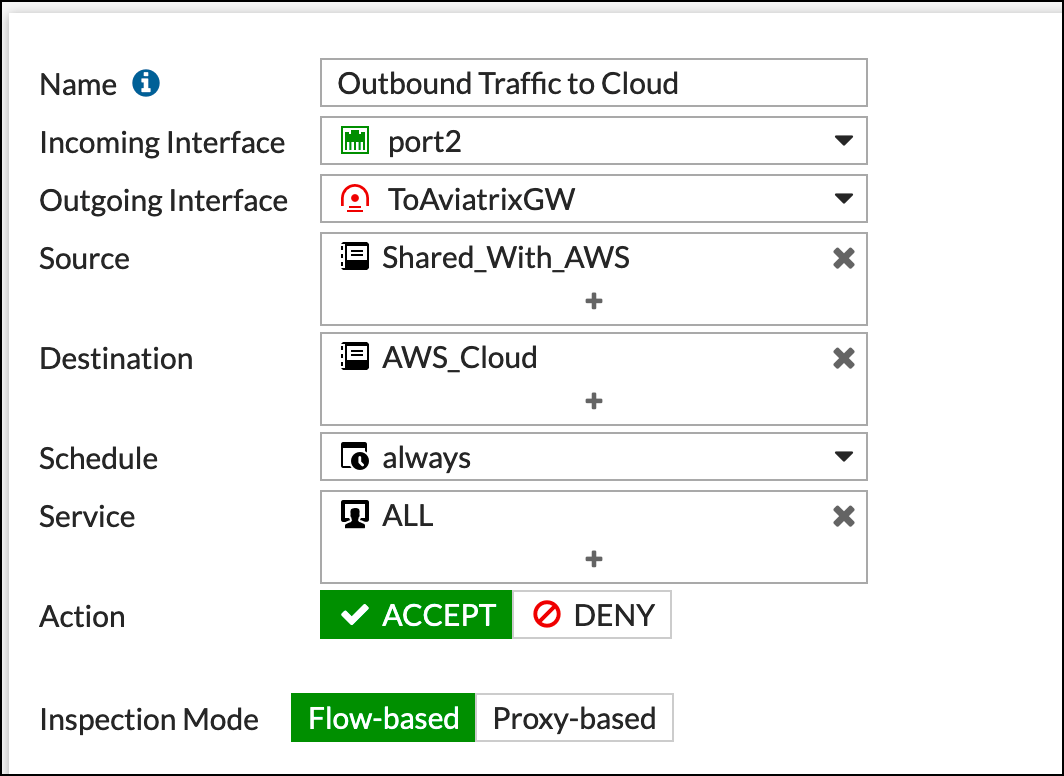
1. Go to Policy & Objects > IPv4 DoS Policy.
2. Create two new IPv4 policies:
* Outbound traffic from FortiGate (Shared\_With\_AWS) to Aviatrix (AWS\_Cloud)
 * Inbound traffic from Aviatrix (AWS\_Cloud) to FortiGate (Shared\_With\_AWS)
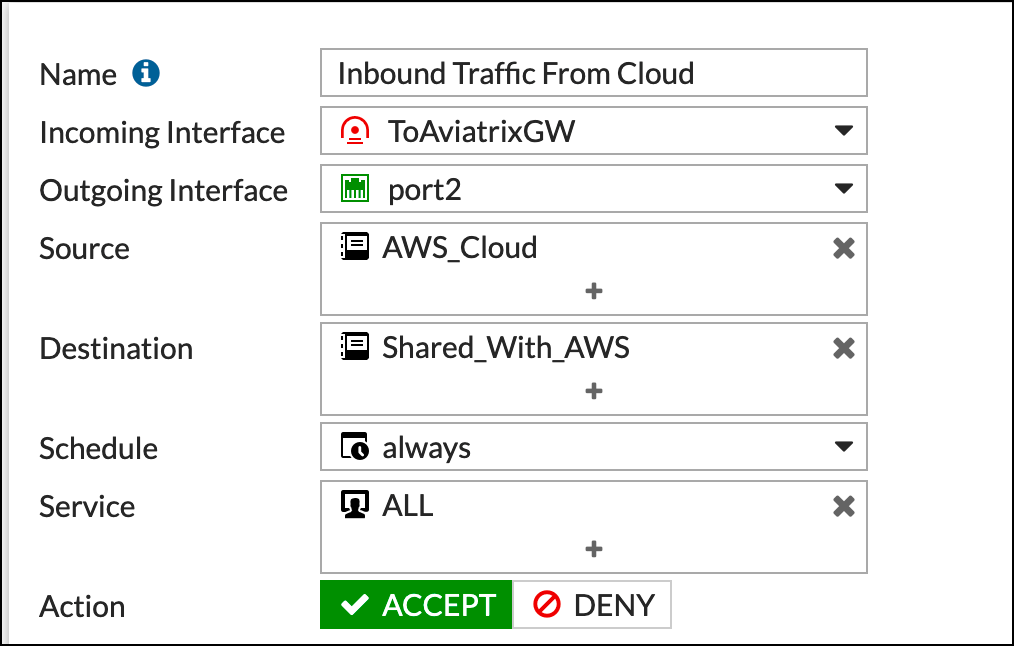 The reference to port2 in the screenshots should be replaced with your own
interface name that represents the internal facing interface.
Be sure to select *ACCEPT* for "action" and select *ALL* for "service."
### Adding a Static Route
In the FortiGate UI, go to Network > Static Routes and add a new static route
for traffic destined to "AWS\_Cloud" to use the VPN tunnel.
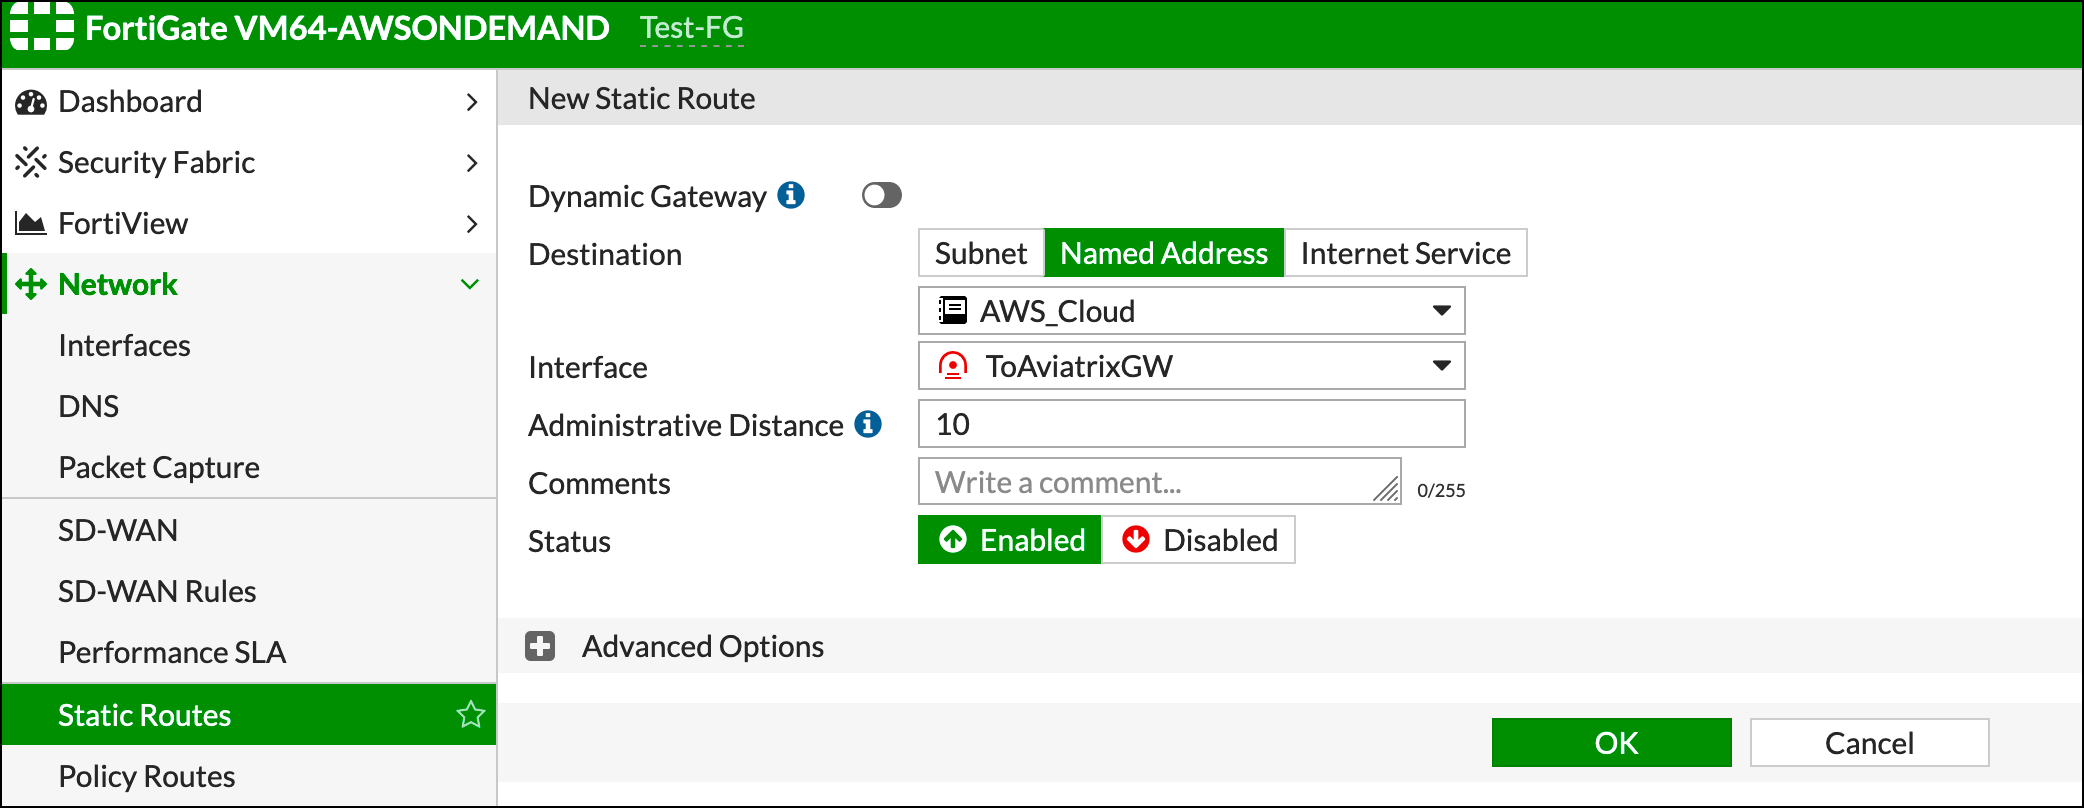 If Named Address is disabled, be sure that you enabled Static Route
Configuration on the Address configuration.
 ### IPsec Monitor
1. In the Fortigate UI, navigate to Dashboard > Network and click the IPsec
widget.
2. Select the Aviatrix tunnel, and click *Bring Up*.
3. You can then check the tunnel status in CoPilot under Diagnostics > Cloud
Routes.
## Troubleshoot
*Error Message*
`failed to get valid proposal`
`no suitable proposal found`
*Solution*
Check that the Phase 1 authentication, encryption, and Diffie-Hellman groups
match on both sides.
If you are experiencing low IPsec throughput, you may want to configure two
commands on the Fortigate.
```cli theme={null}
config system global
set ipsec-asic-offload disable
end
configure system global
set ipsec-hmac-offload disable
end
```
## Related Topics
* About External Connection Settings