> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Aviatrix Gateway to Check Point(R77.30)
> This document describes how to build an IPsec tunnel-based Site2Cloud connection between Aviatrix Gateway and Check Point Firewall. To simulate an on-prem Check Point Firewall, we use a Check Point CloudGuard IaaS firewall VM at AWS VPC.
This document describes how to build an IPsec tunnel-based Site2Cloud connection
between Aviatrix Gateway and Check Point Firewall. To simulate an on-prem Check
Point Firewall, we use a Check Point CloudGuard IaaS firewall VM at AWS VPC.
If you do not have access to AWS, you can simulate an on-prem Firewall by
deploying the Palo Alto Firewall in any other cloud (such as Microsoft Azure,
Google Cloud Platform, or Oracle Cloud Infrastructure).
The network setup is as follows:
**VPC1 (with Aviatrix Gateway)**
*VPC1 CIDR: 10.0.0.0/16*
*VPC1 Public Subnet CIDR: 10.0.1.0/24*
*VPC1 Private Subnet CIDR: 10.0.2.0/24*
**VPC2 (with Check Point Security Gateway)**
*VPC2 CIDR: 10.10.0.0/16*
*VPC2 Public Subnet CIDR: 10.10.0.0/24*
*VPC2 Private Subnet CIDR: 10.10.1.0/24*
## Launching Check Point Security Gateway VM
Refer to the
[Check Point vSEC for AWS Lab Setup Guide](https://supportcenter.checkpoint.com/supportcenter/portal?eventSubmit_doGoviewsolutiondetails=\&solutionid=sk111013)
to launch a CheckPoint VM with at least two network interfaces. One interface
serves as a WAN port and is in VPC2's public subnet. The other interface serves
as a LAN port and is in VPC2's private subnet. Collect the public IP address of
the WAN port.
## Creating an External Connection
1. In Aviatrix CoPilot, launch an
Aviatrix Transit Gateway
in VPC1's public subnet. Collect both the public and private IP address of
the Gateway.
2. Navigate to Networking > Connectivity > External Connections (S2C) and click
**Add New** to create a Site2Cloud connection (selecting Pre-Shared Key)
using the values for one of the below options:
* [Static Route-Based](https://legacy.docs.aviatrix.com/documentation/latest/network/external-connection-create-static-route-based-unmapped.html)
* [Static Policy-Based](https://legacy.docs.aviatrix.com/documentation/latest/network/external-connection-create-static-policy-based-unmapped.html)
Substitute the following values:
* Remote Device Type: Generic
* Algorithms: turn Off
* Remote Device IP: Public IP of the Check Point VM WAN port
* Remote Subnet CIDR(s): 10.10.1.0/24 (VPC2 private subnet)
* Local Subnet CIDR(s): 10.0.2.0/24 (VPC1 private subnet)
3. After the connection is created, select the vertical ellipsis
 menu for that
connection and select **Download Configuration**.
4. Select **Generic** from the **Vendor** dropdown list and click the
**Download** to download the external (S2C) configuration. Use this
configuration file to configure the tunnels and interfaces in your Check
Point VM firewall.
## Downloading and Installing SmartConsole
1. Using a browser, connect to the Gaia Portal of the CheckPoint-VM at
`https:/CheckPoint-VM_Public-IP`:
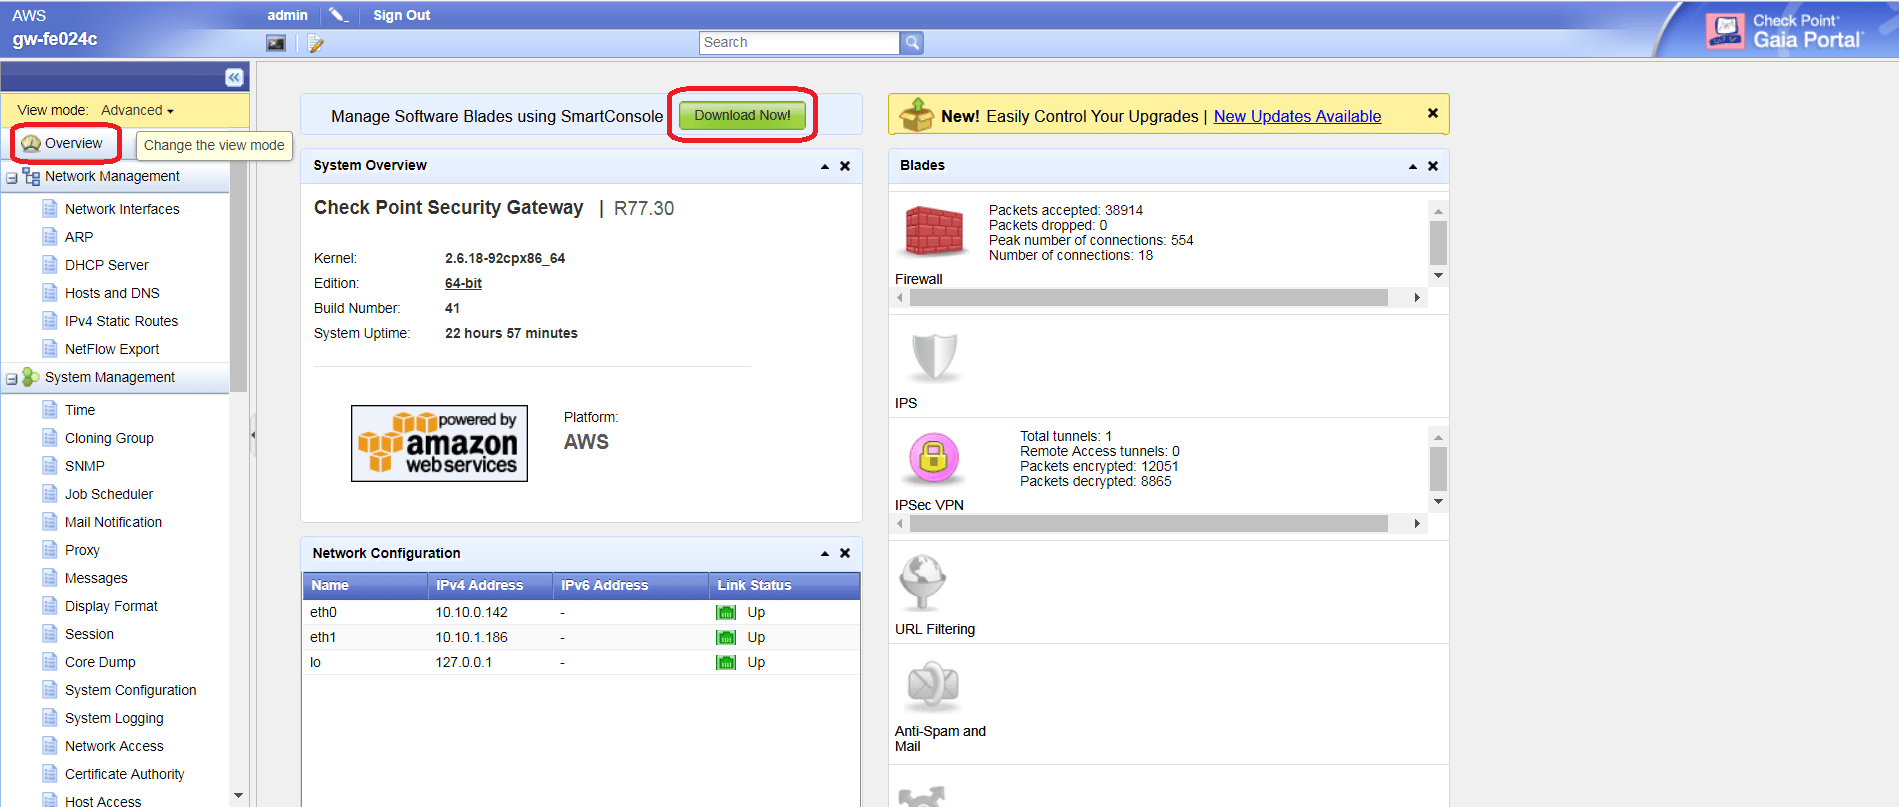 2. Click **Overview** at the left navigation bar, and then click **Download
Now!** to download SmartConsole.
3. Install SmartConsole at your local machine and launch SmartDashboard.
### Creating Network Objects at SmartConsole
1. At the Check Point SmartDashboard window, select the **Desktop** tab. Right
click the **Networks** folder at the left navigation bar and select
**Network**.
2. Create one network for private subnet of VPC2 (Check Point VPC).
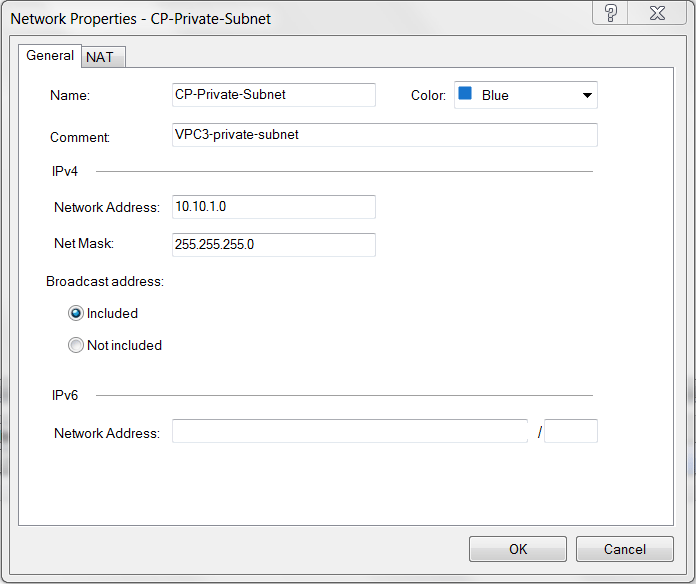 | **Field** | **Value** |
| -------------------- | ---------------------------------- |
| Name | Arbitrary (e.g. CP-Private-Subnet) |
| IPv4 Network Address | VPC2 private subnet CIDR |
| IPv4 Net mask | VPC2 private subnet mask |
3. Create one network for private subnet of VPC1 (Aviatrix Gateway VPC).
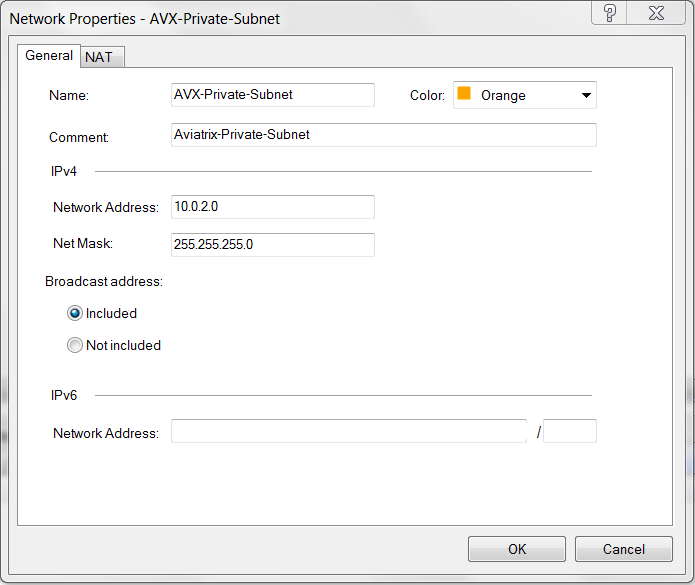 | **Field** | **Value** |
| -------------------- | ----------------------------------- |
| Name | Arbitrary (e.g. AVX-Private-Subnet) |
| IPv4 Network Address | VPC1 private subnet CIDR |
| IPv4 Net mask | VPC1 private subnet mask |
### Configuring Check Point Security Gateway with VPN
1. At the SmartDashboard window, select the **Desktop** tab and expand the
**Check Point** folder at the left navigation bar. Note that your gateway VM
with the name format "gw-xxxxxx" is automatically created.
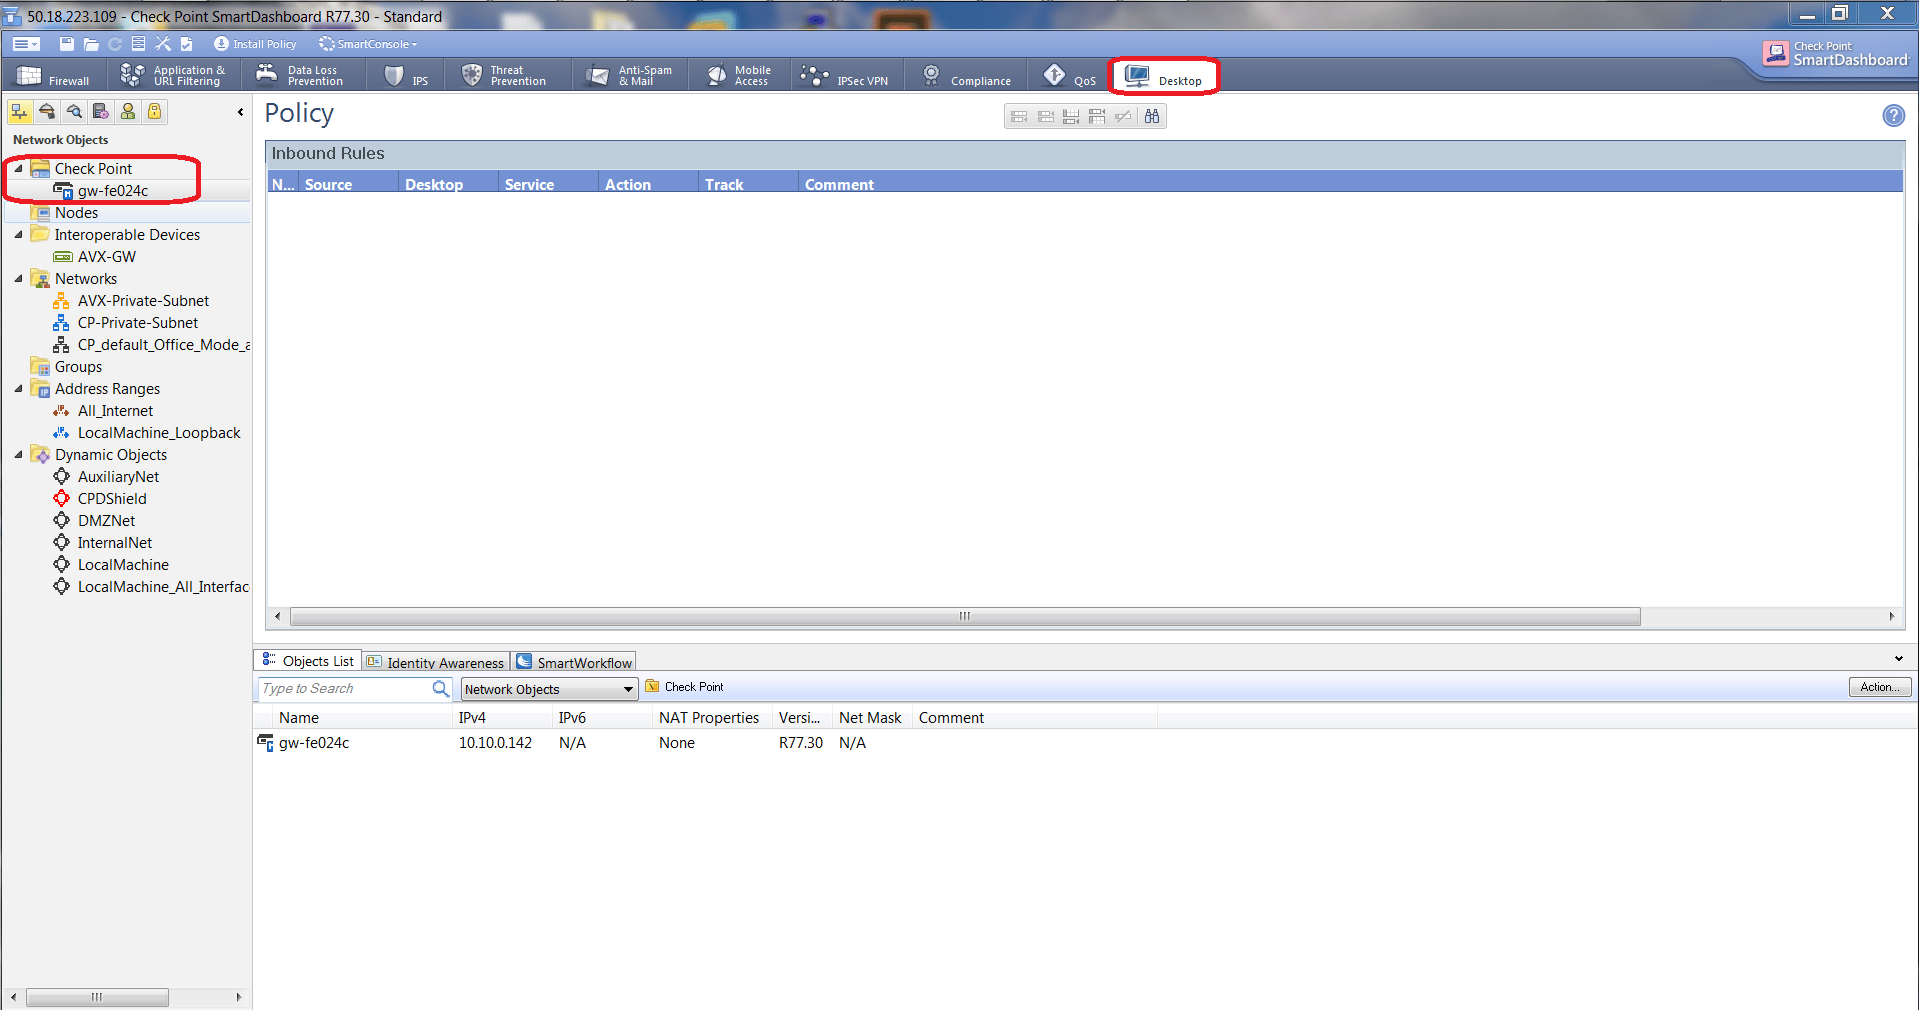 2. Right-click the gateway name and select **Edit** from the menu.
3. At the Check Point Gateway > General Properties window:
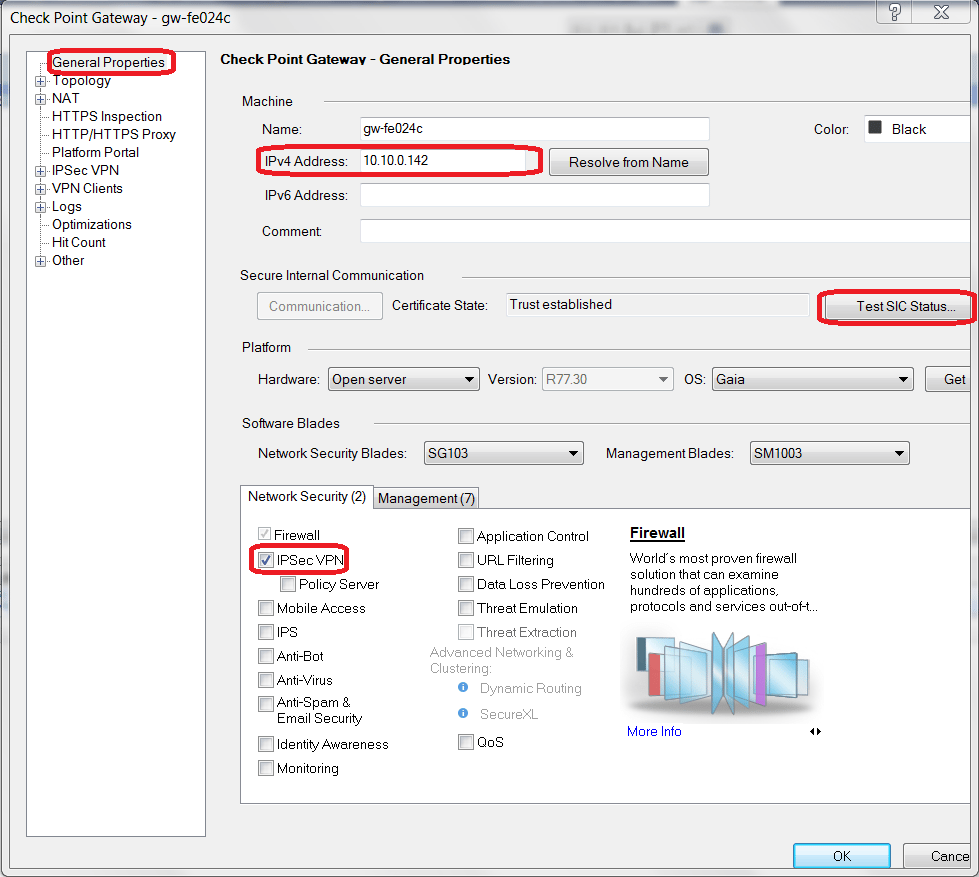 | **Field** | **Value** |
| ---------------- | --------------------------------------- |
| IPv4 Address | Private IP of CheckPoint VM WAN port |
| Test SIC Status | Make sure the status is "communicating" |
| Network Security | Select **IPsec VPN** |
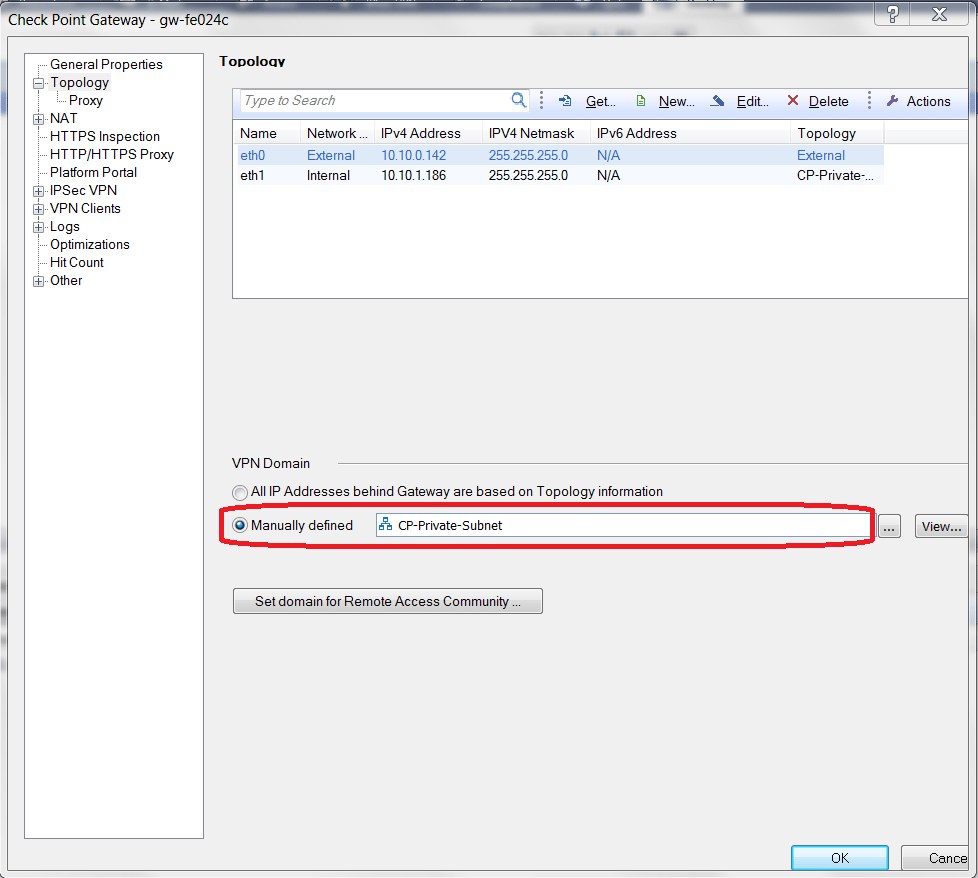
4. At **Check Point Gateway - Topology** window, select **Manually defined** for
VPN Domain. Select the network created when you created a network for private
subnet of VPC2 (Check Point VPC).
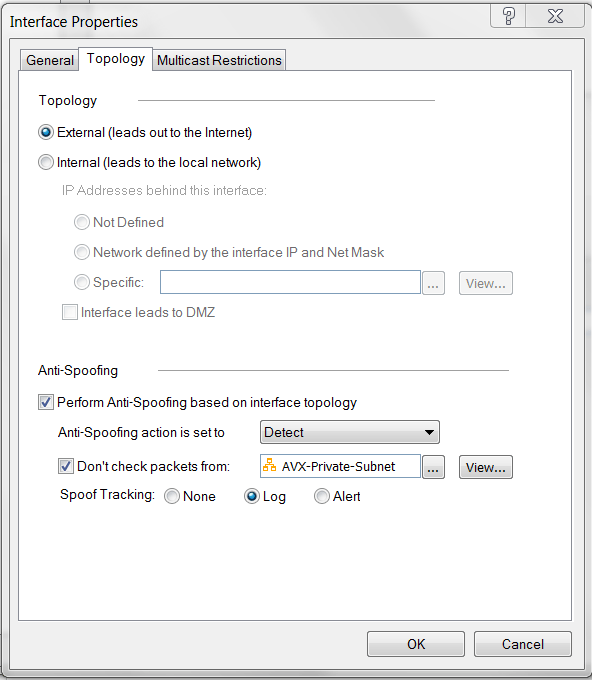
 5. At **Check Point Gateway - Topology** window, double-click "eth0" (Check
Point WAN port). Select **External (leads out to the Internet)**.
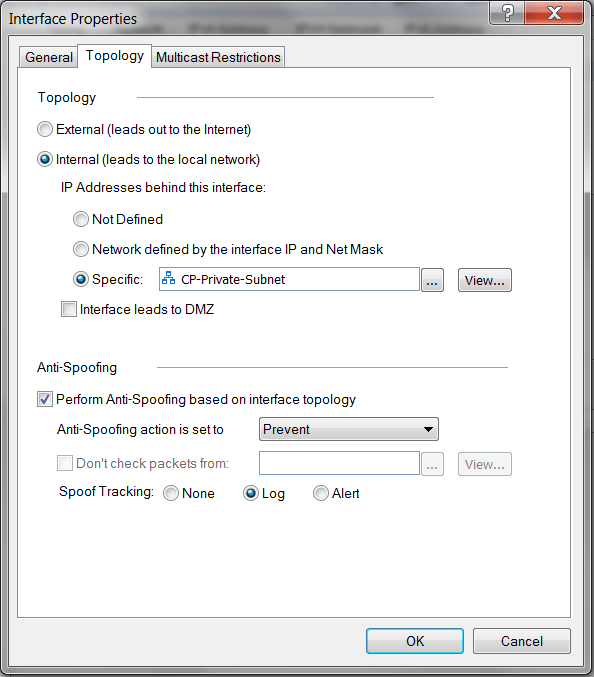
 6. At **Check Point Gateway - Topology** window, double click "eth1" (Check
Point LAN port). Select **Internal (leads to the local network)**.
 7. At the **Check Point Gateway - IPsec VPN - Link Selection** window, configure
the parameters as follows:
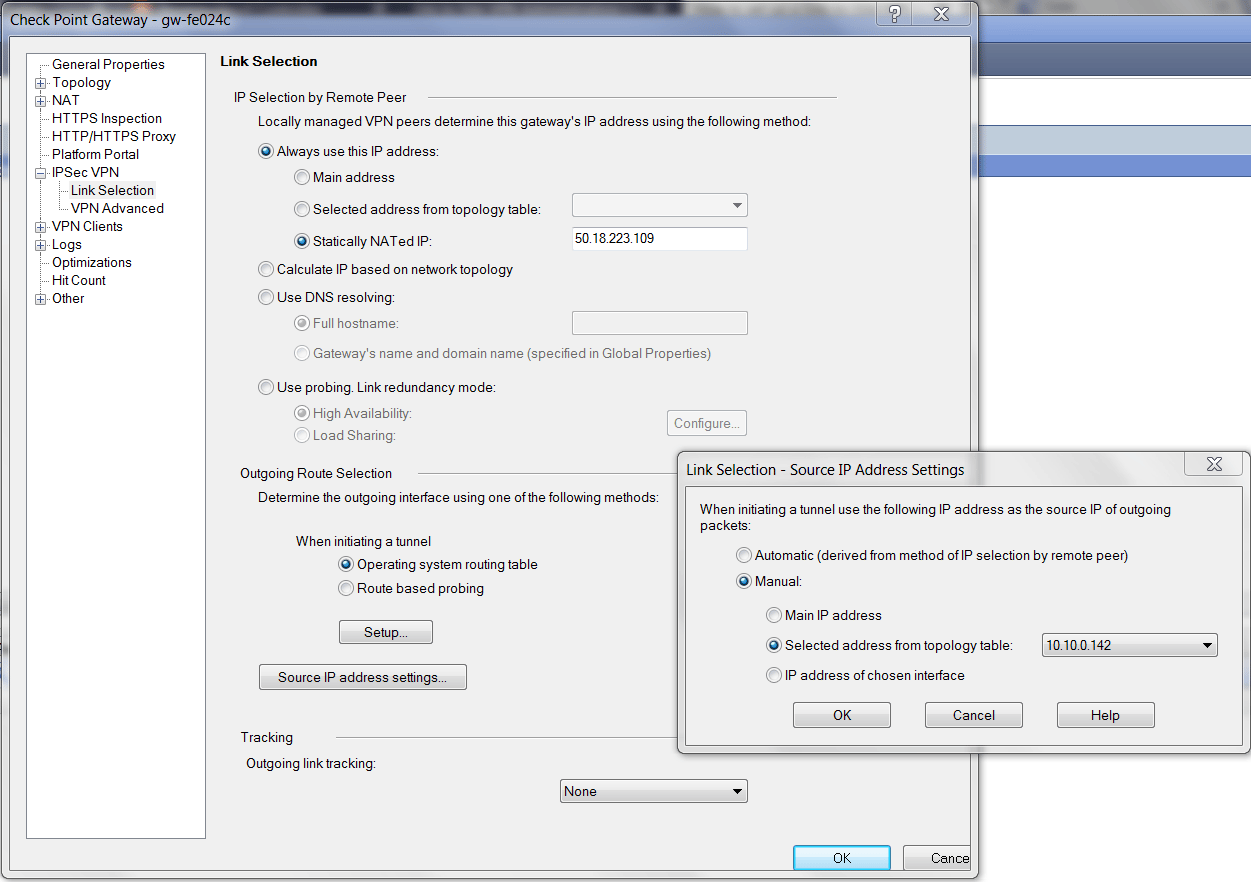 | **Field** | **Value** |
| ------------------------------------ | ---------------------------------- |
| Statically NATed IP | Public IP of Check Point WAN port |
| Selected address from topology table | Private IP of Check Point WAN port |
8. At the **Check Point Gateway - IPsec VPN - VPN Advanced** window, configure
the parameters as follows:
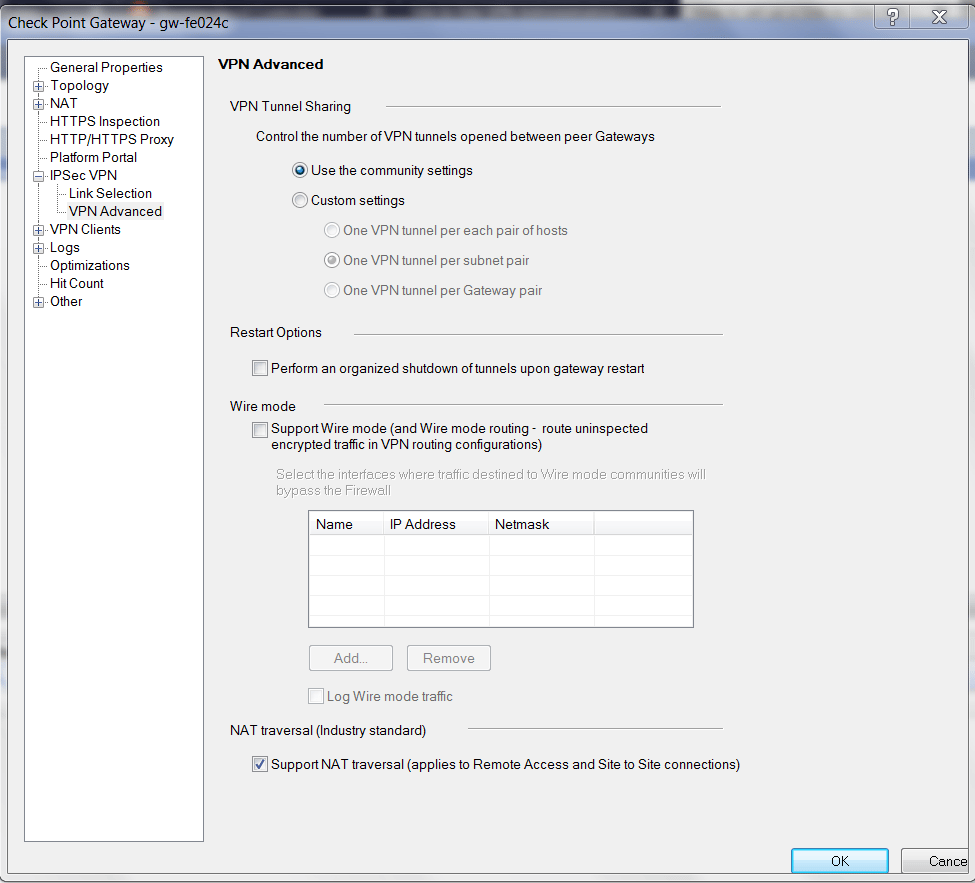 ### Configuring an Interoperable Device to Represent Aviatrix Gateway
1. At Check Point SmartDashboard window, select the **Desktop** tab. Right-click
the **Networks** folder at the left navigation bar to create a new
interoperable device.
2. At the Interoperable Device - General Properties window:
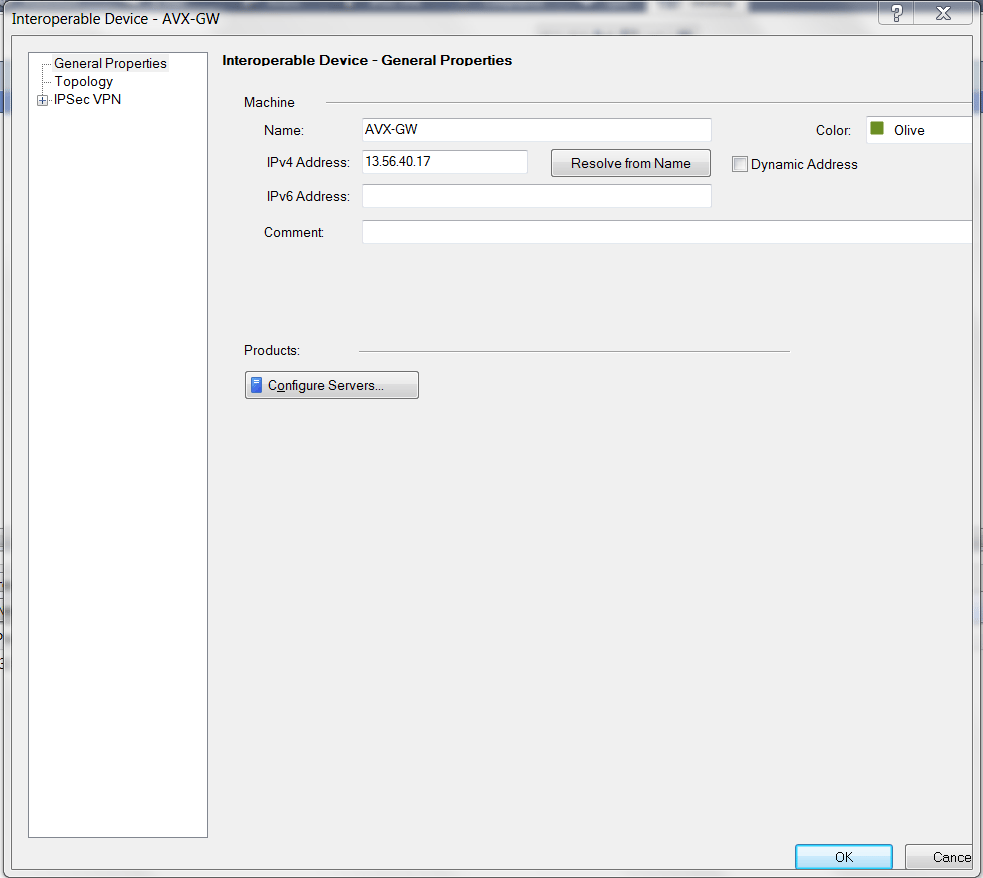 | **Field** | **Value** |
| ------------ | ----------------------------- |
| Name | Arbitrary (e.g. AVX-GW) |
| IPv4 Address | Public IP of Aviatrix Gateway |
3. At the **Interopable Device - Topology** window, select **Manually defined**
for VPN Domain. Select the network private subnet of VPC1 (Aviatrix Gateway
VPC) you created above.
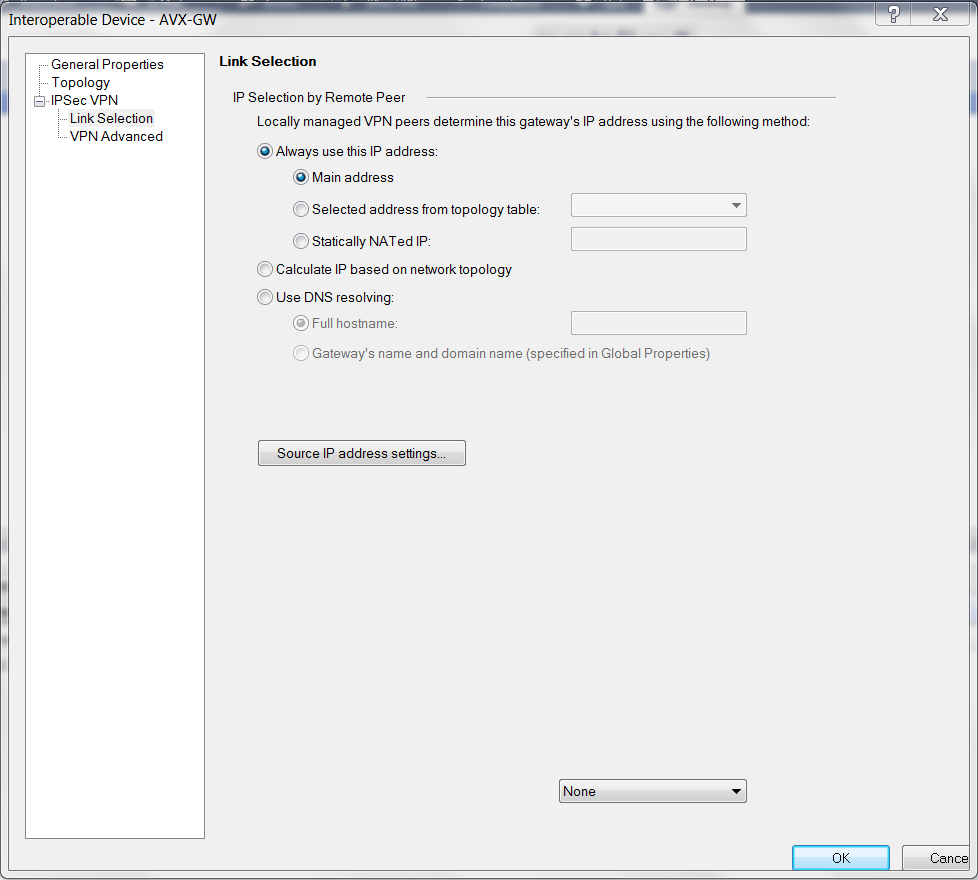
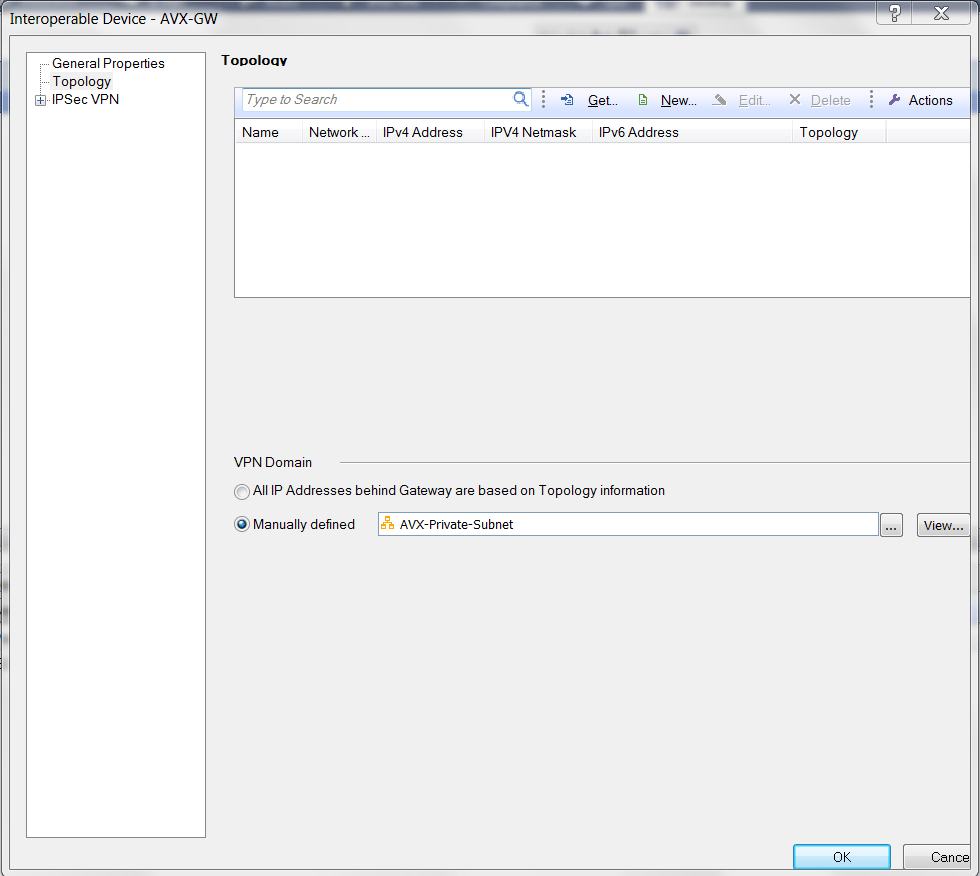 4. At the **Interopable Device - IPsec VPN - Link Selection** window, select
**Always use this IP address > Main Address**.
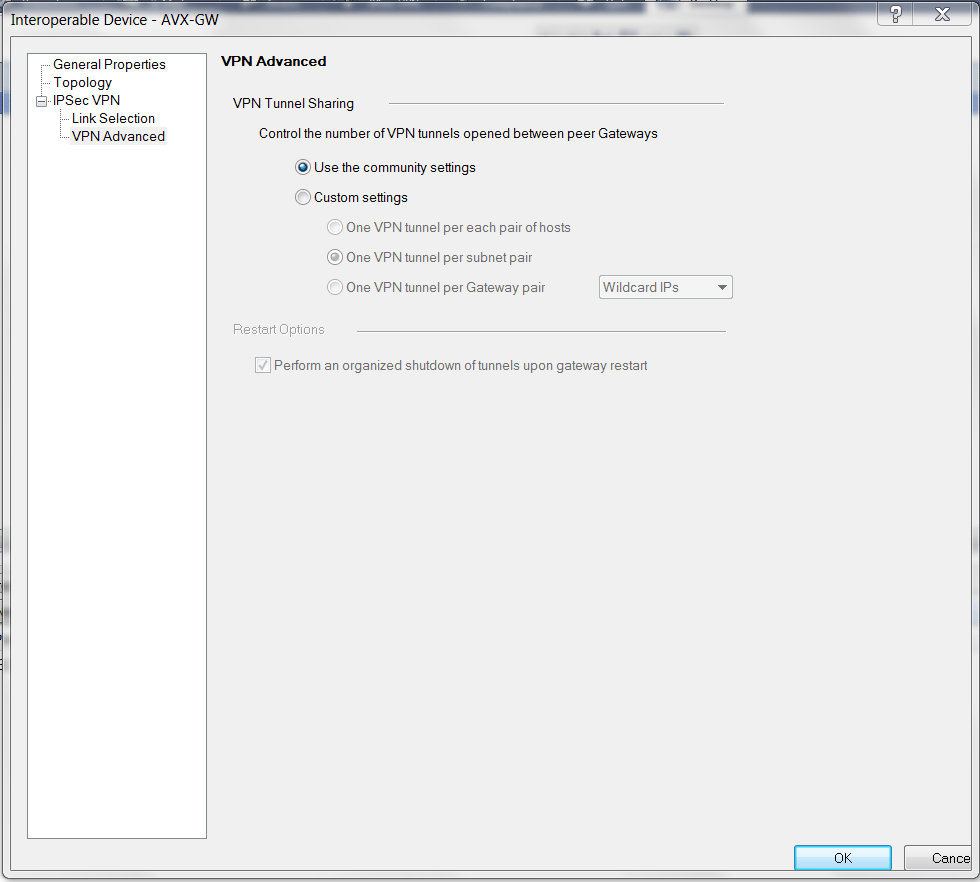
 5. At the **Interopable Device - IPsec VPN - VPN Advanced** window, select **Use
the community settings**.
 ### Creating a VPN Community
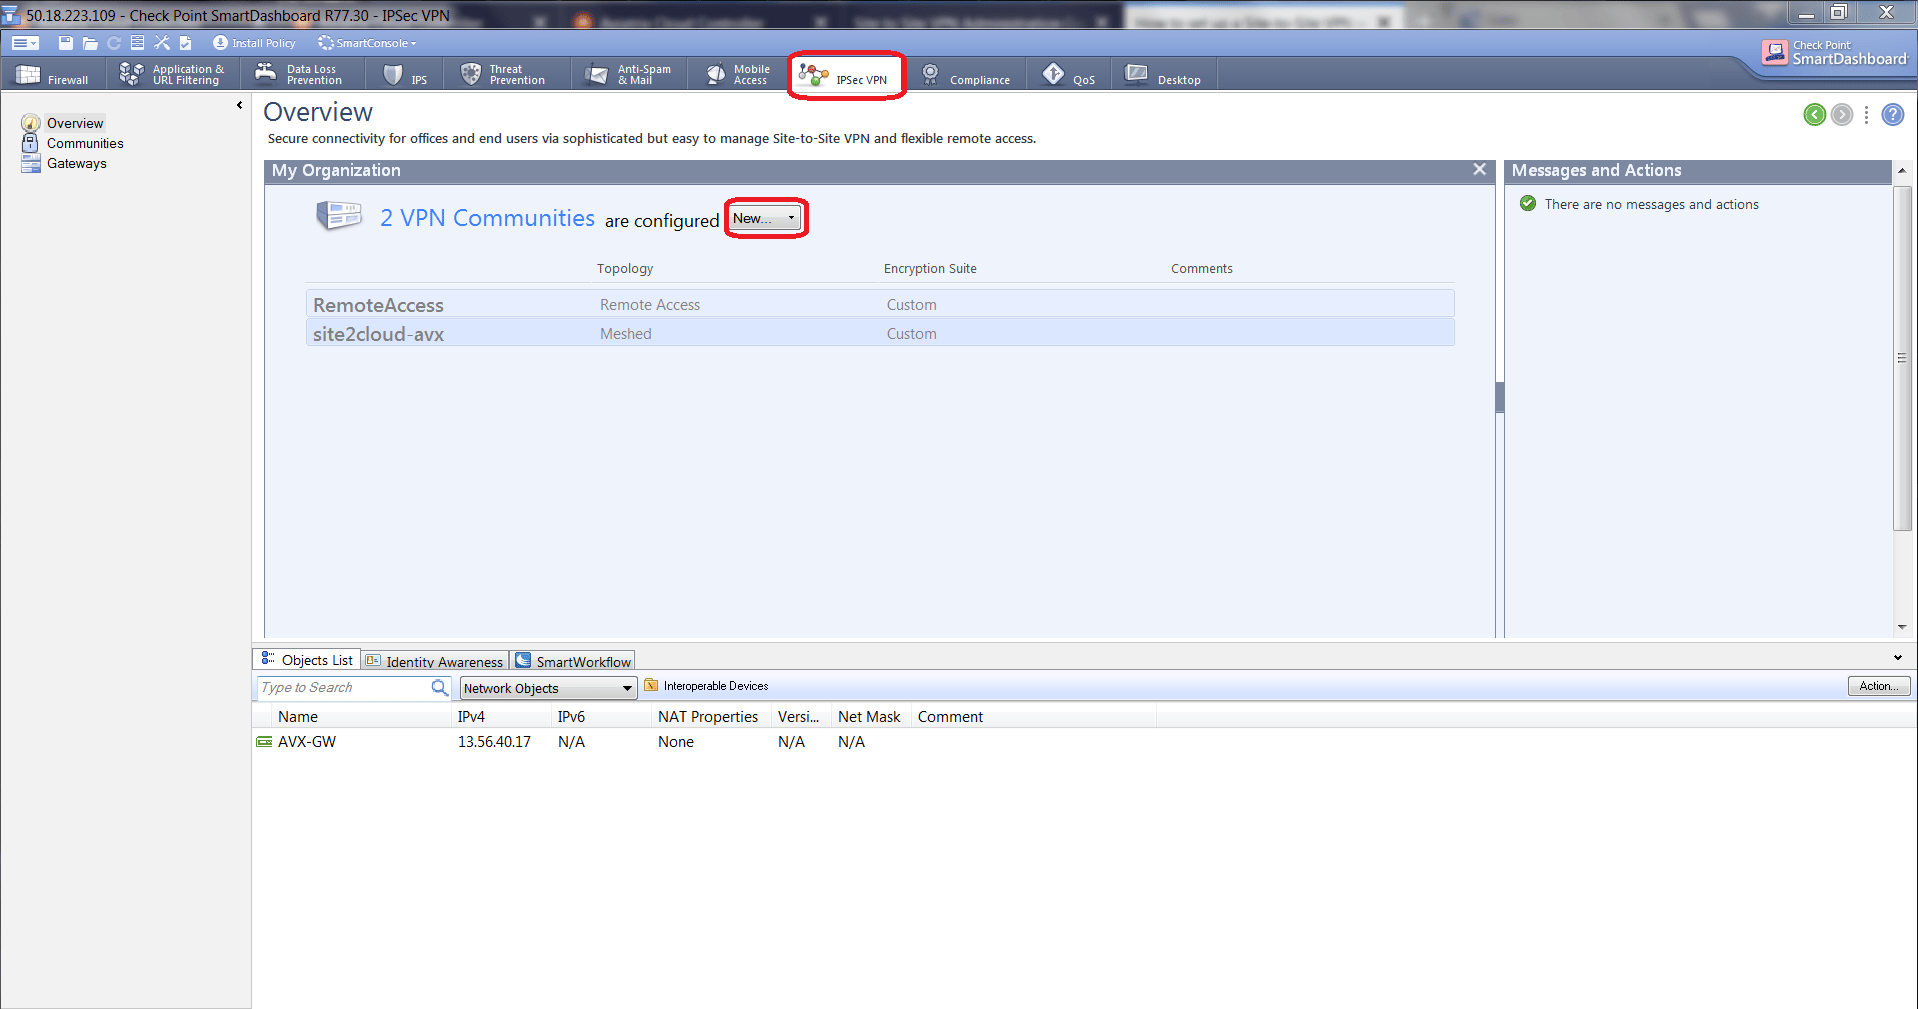
1. At SmartDashboard **IPsec VPN** tab, select **Overview** from left navigation
bar. Click **New** to create a Meshed Community.
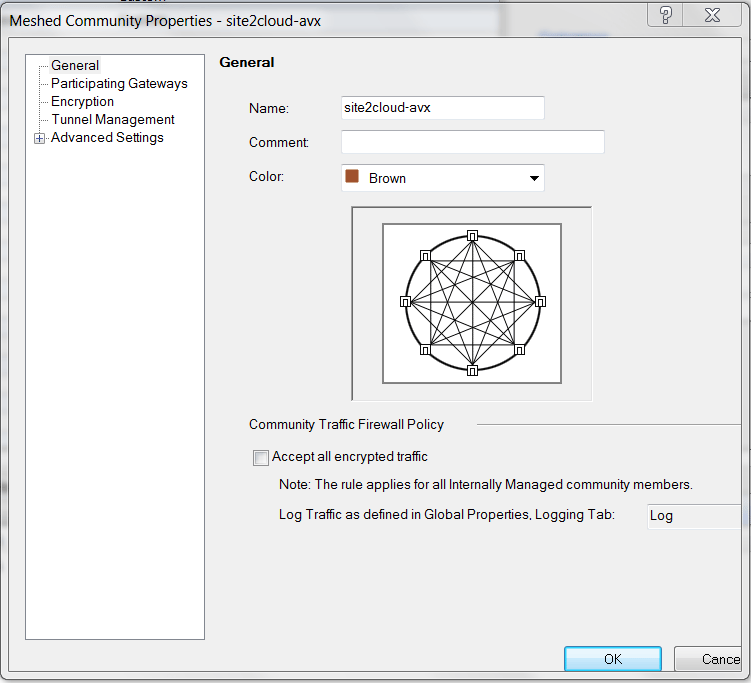
 2. At **Meshed Community Properties - General** window, create one community
with a name (e.g. Site2Cloud-avx).
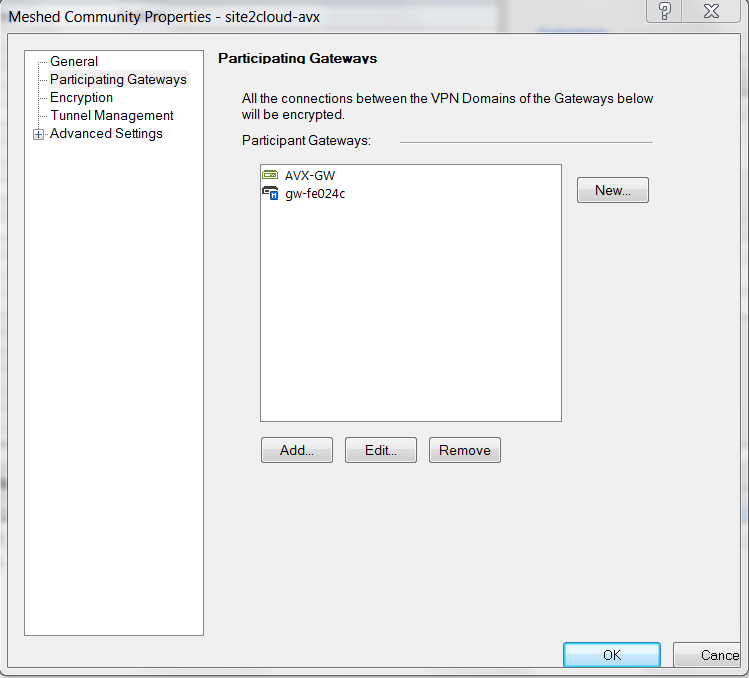
 3. At **Meshed Community Properties - Participating Gateways** window, add both
Check Point Security Gateway (e.g. gw-fe024c) and the interopable device
created when you configured an interoperable device to represent the Aviatrix
Gateway (e.g. AVX-GW) to this community.
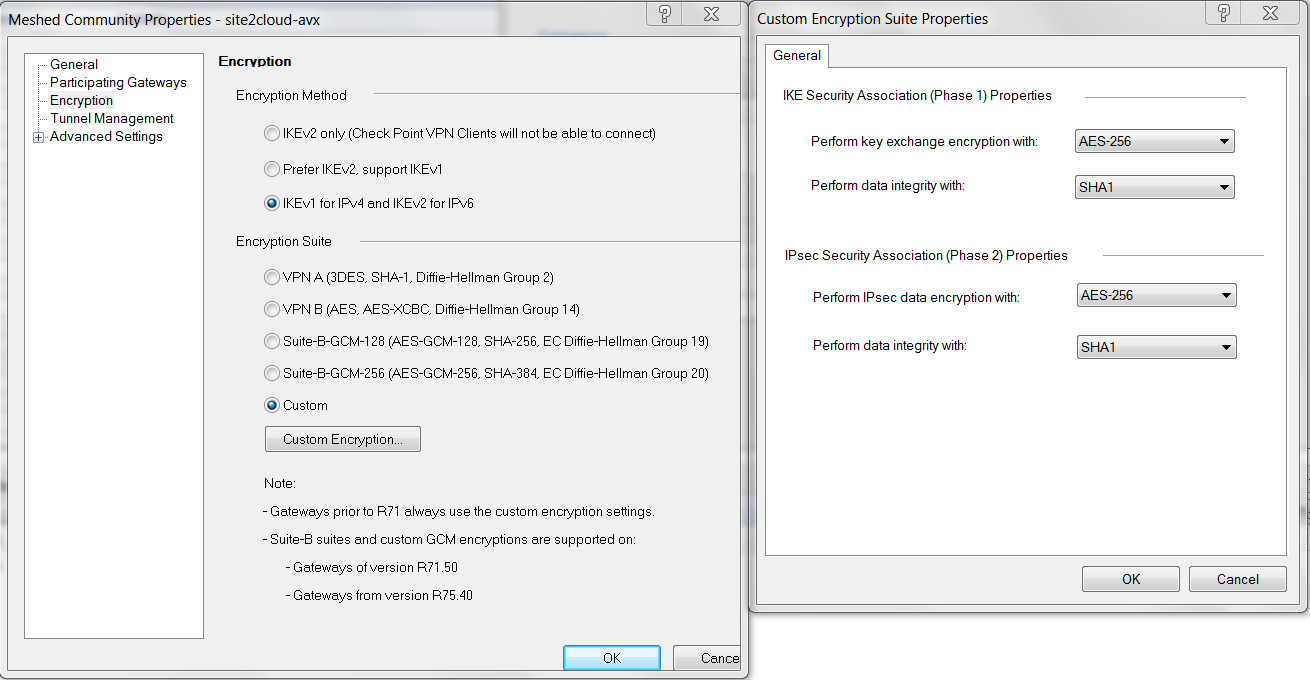
 4. At **Meshed Community Properties - Encryption** window, select the options
according to the Site2Cloud configuration for configuring CheckPoint-VM you
saved and downloaded above.
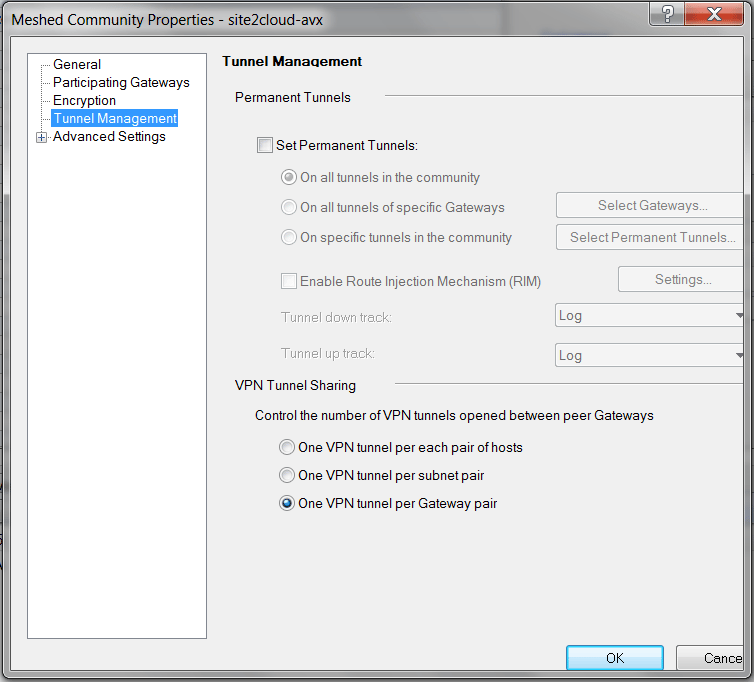
 5. At **Meshed Community Properties - Tunnel Management** window, select **One
VPN tunnel per Gateway pair** for **VPN Tunnel Sharing**.
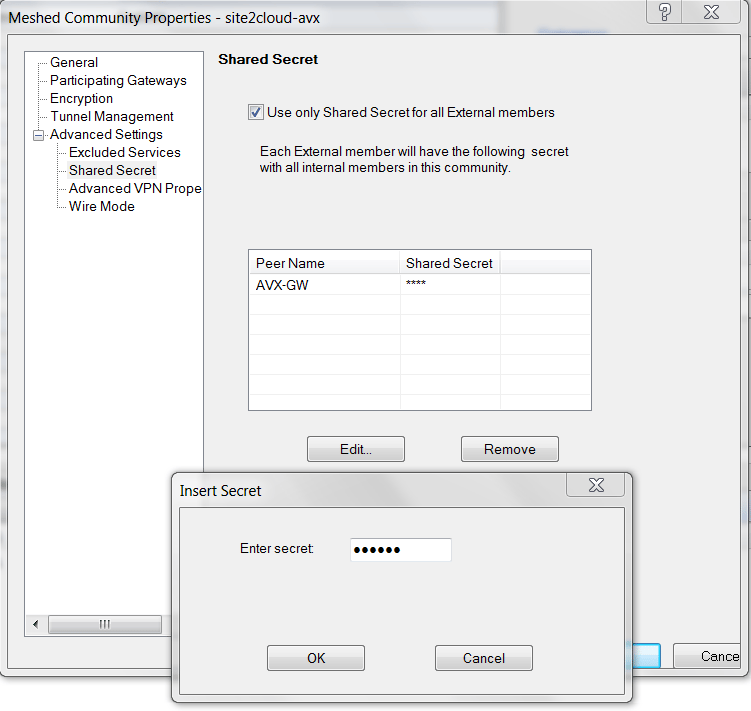
 6. At the **Meshed Community Properties - Advanced Settings - Shared Secret**
window, enter **Shared Secret** by copying the **Pre-Shared Key** from the
Site2Cloud configuration downloaded above.
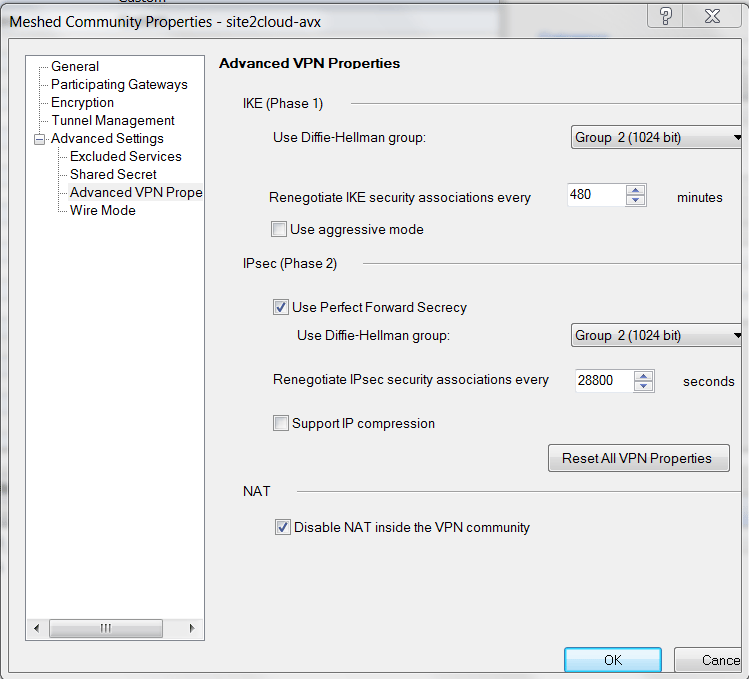
 7. At the **Meshed Community Properties - Advanced Settings - Advanced VPN
Properties** window, enter the Phase1 and Phase2 parameters according to the
Site2Cloud configuration downloaded above.
 ### Creating Firewall Rule for VPN Traffic
1. At SmartDashboard window, select the **Firewall** tab.
2. Select **Policy** to add a new rule.
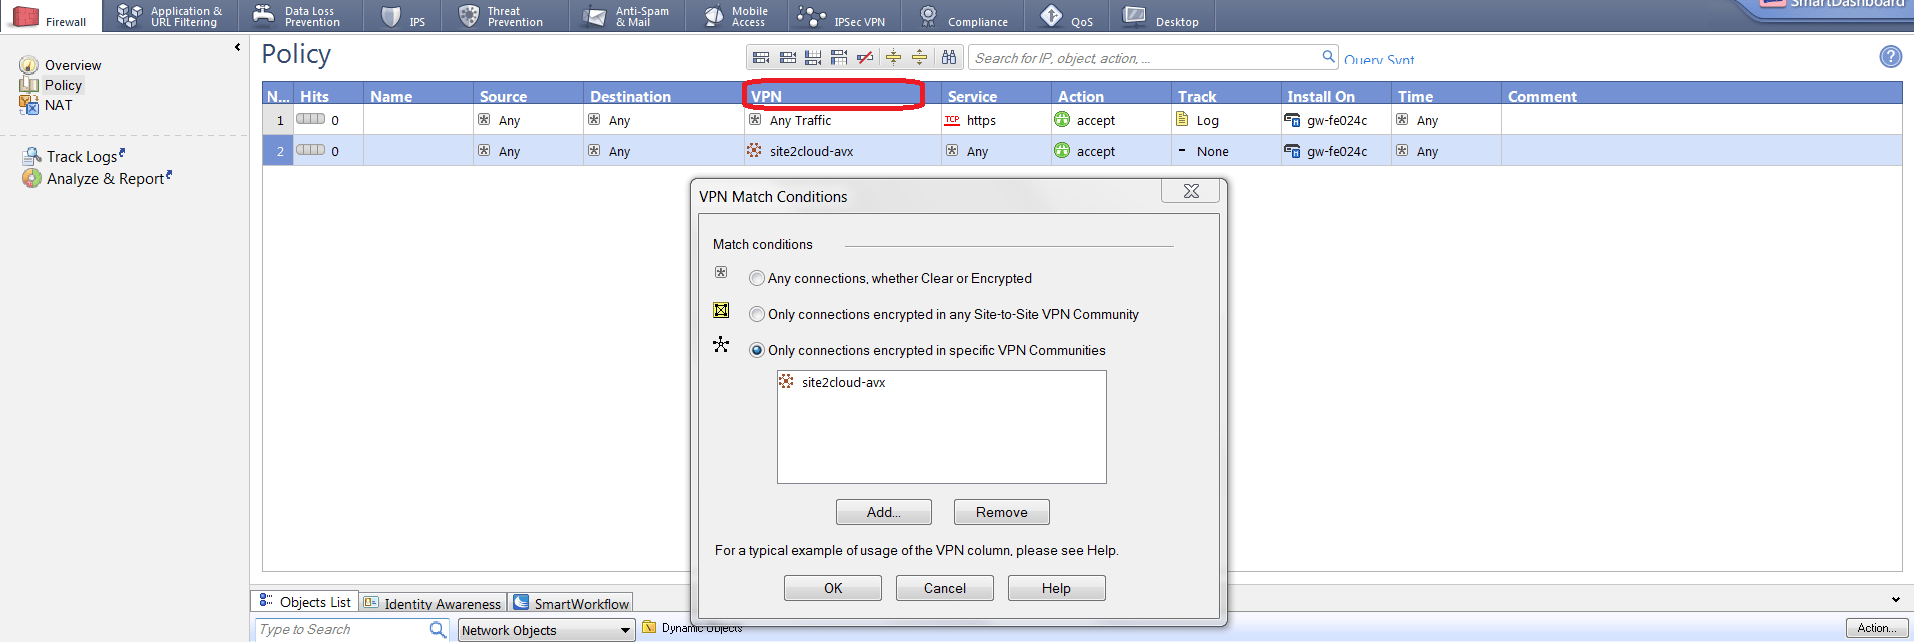 | **Field** | **Value** |
| ---------- | --------------------------------------------- |
| VPN | Select the Meshed VPN Community created above |
| Install On | Select Check Point Security Gateway |
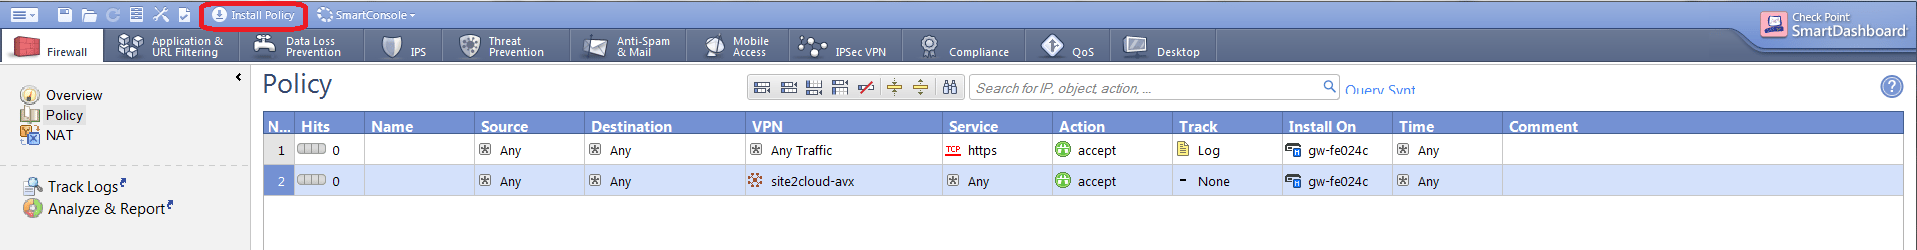
3. Click **Install Policy** to push the firewall policy to the Check Point
Security Gateway.
 ### Troubleshooting and Verifying at Check Point Security Gateway
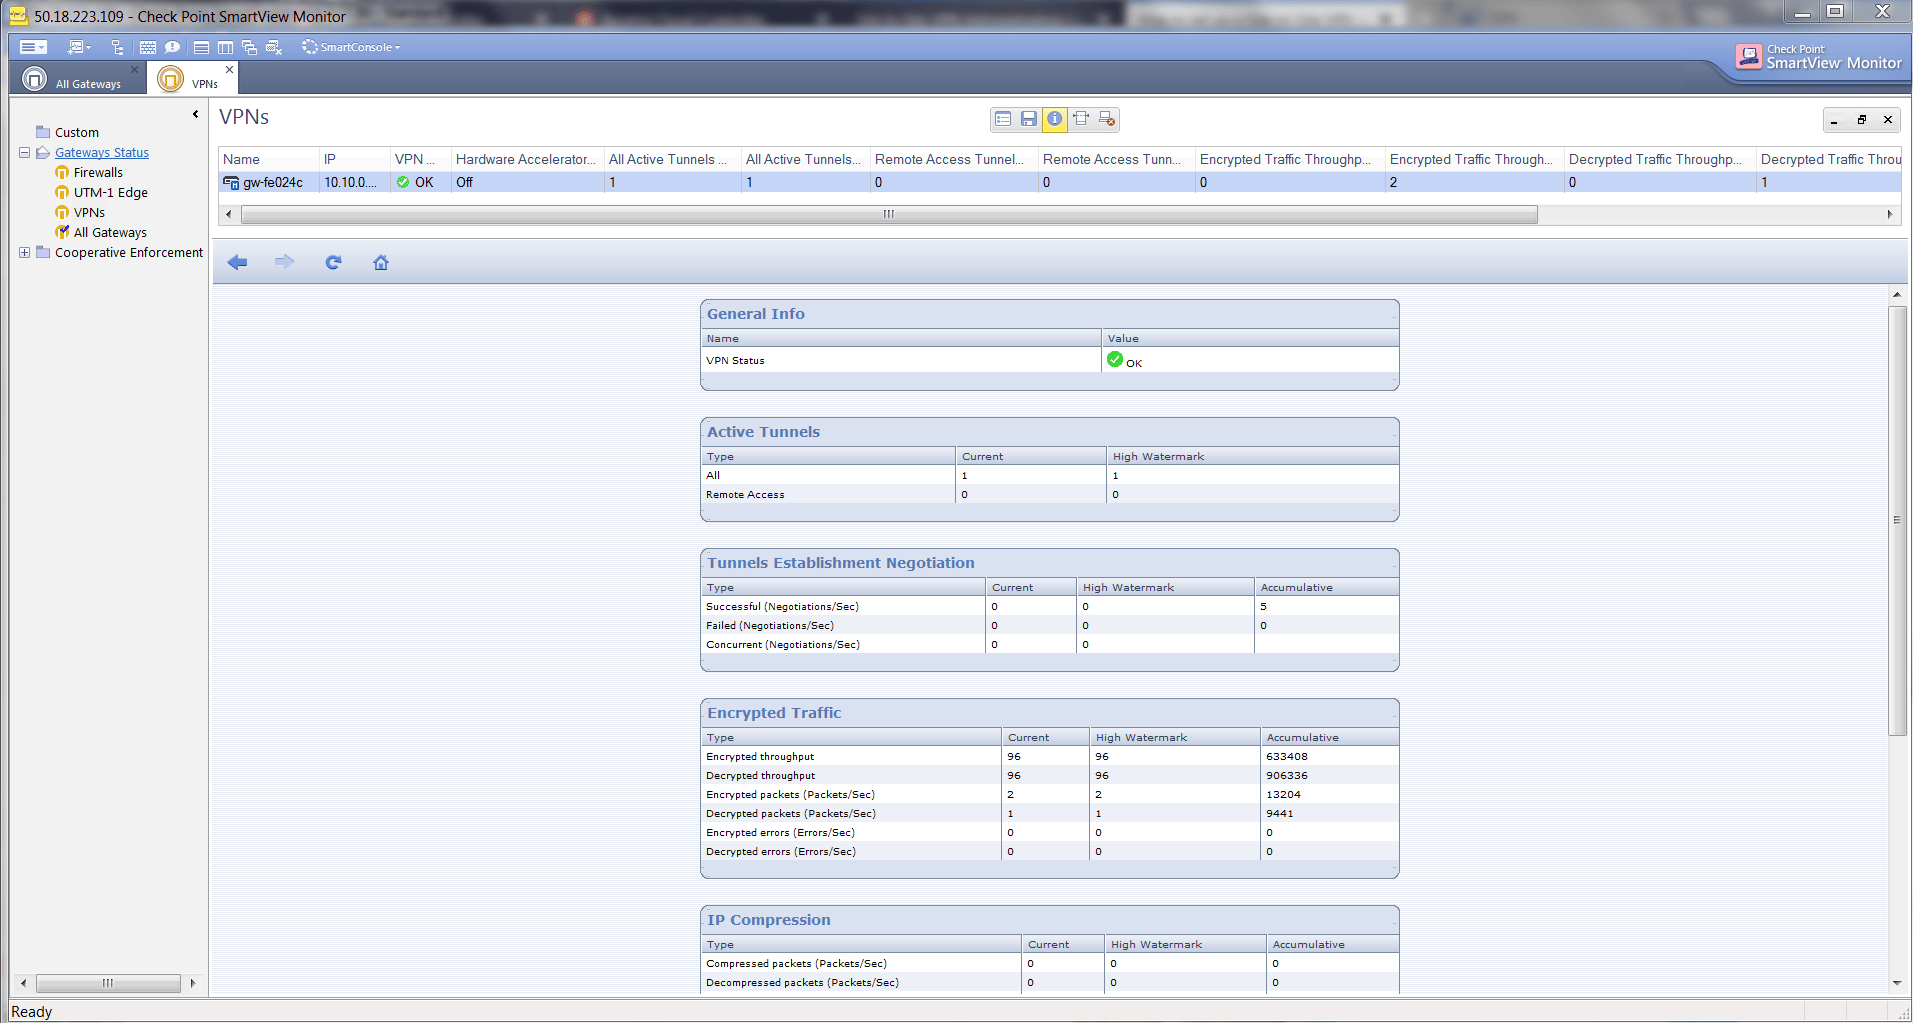
1. At SmartDashboard window, from **SmartConsole** dropdown list, select
**SmartView Monitor**.
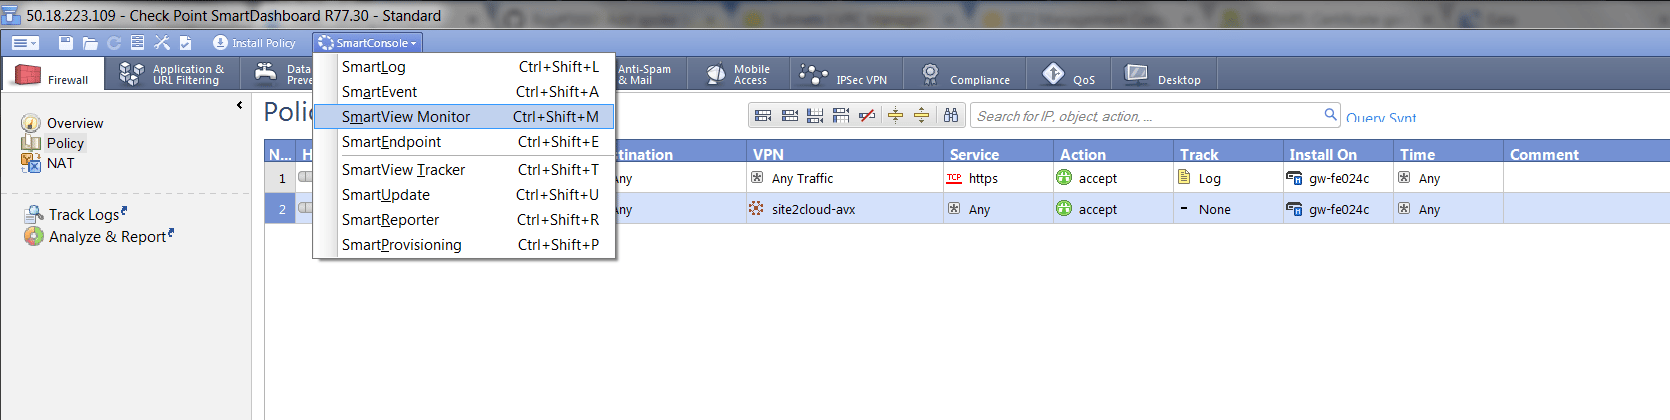 2. At the SmartView Monitor window, select **VPNs** from **Gateway Status** and
verify **Encrypted Traffic**.
 ### Verifying the Connection Status
In CoPilot, go to the Diagnostics > Cloud Routes > External Connections tab to
confirm the Status and Tunnel Status of the external connection.
### Troubleshooting
You can use the Diagnostic Tools (under Diagnostics in the left navigation menu)
to troubleshoot any connection issues.
For support, please open a support ticket at
[Aviatrix Support Portal](https://support.aviatrix.com).
## Related Topics
* [About External Connection Settings](https://legacy.docs.aviatrix.com/documentation/latest/network/externaldevice-settings.html)