> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Transit Network Segmentation
> Aviatrix Multicloud Transit Segmentation provides network isolation through network domains and connection policies to Aviatrix Transit network where both Spoke and Transit networks deploy Aviatrix Gateways across multi-region and multicloud.
## What is Multicloud Transit Segmentation?
Aviatrix Multicloud Transit Segmentation provides network isolation through
network domains and connection policies to Aviatrix Transit network where both
Spoke and Transit networks deploy Aviatrix Gateways across multi-region and
multicloud.
The concept is described in the below diagram.
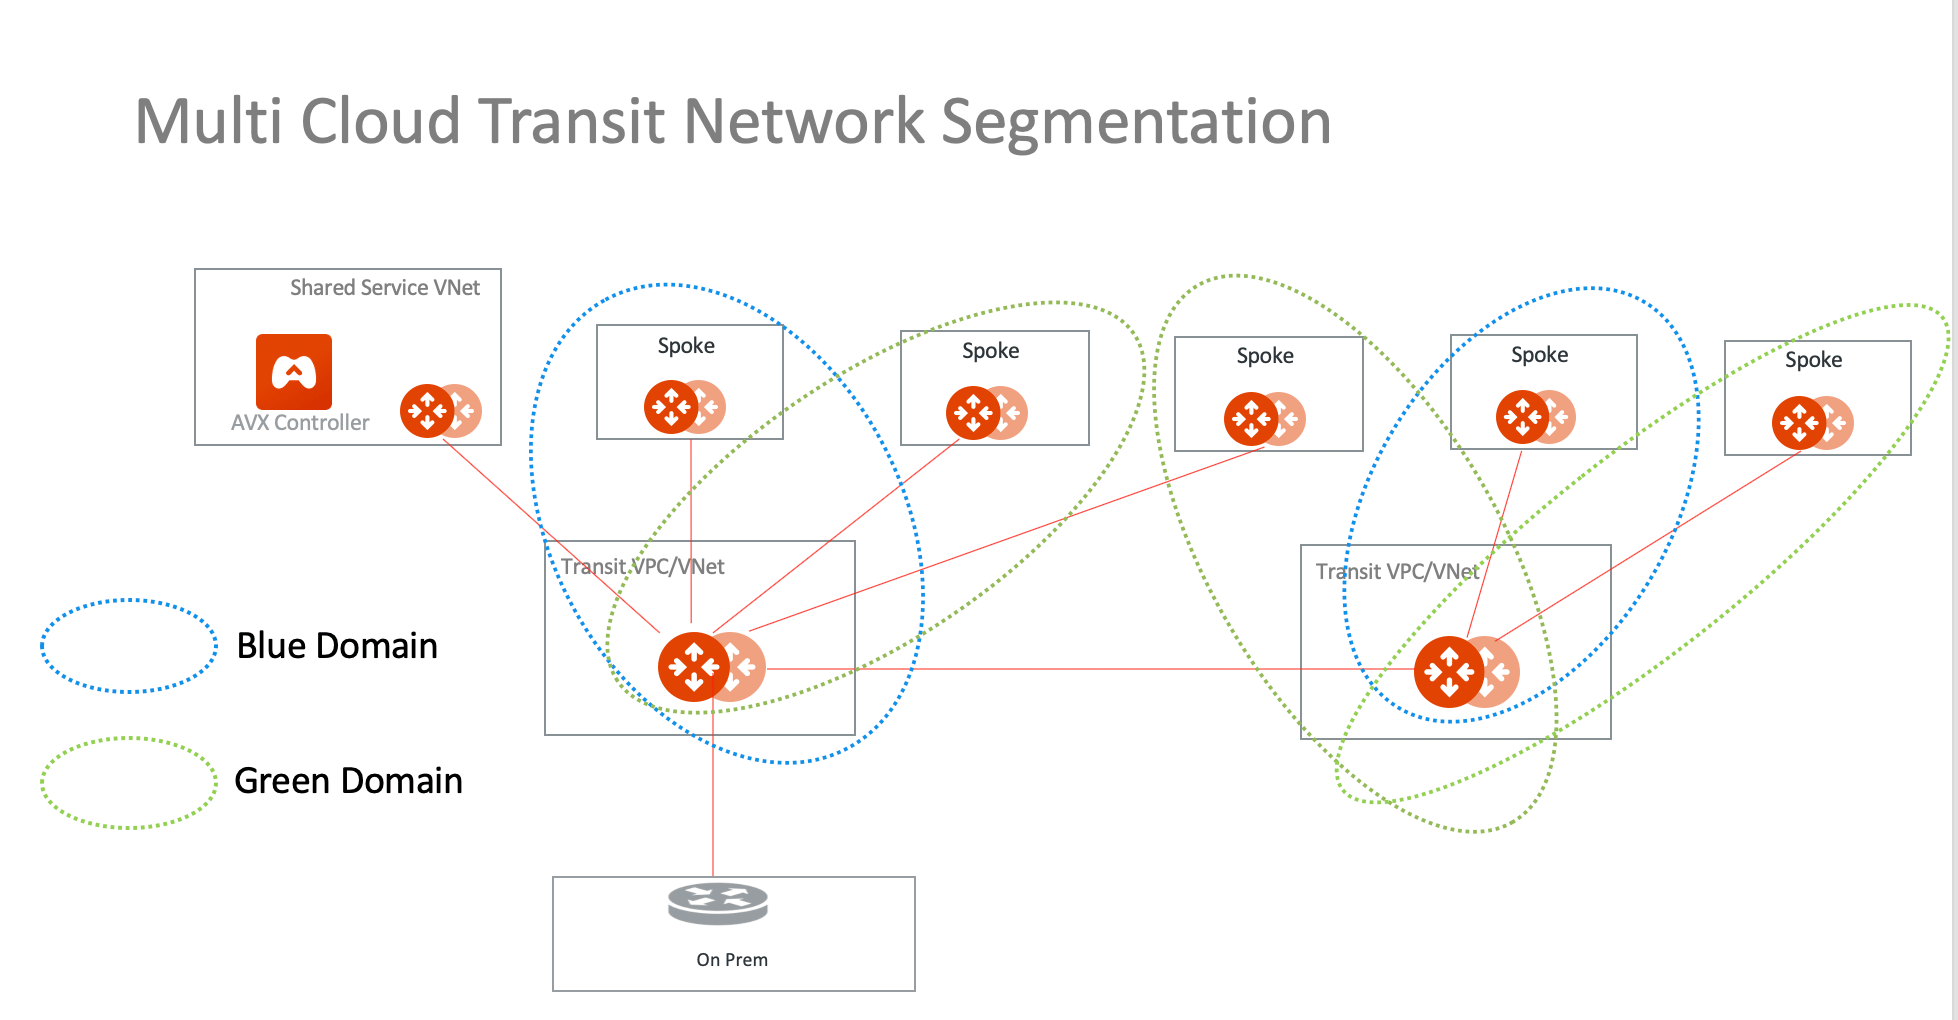 Where Spokes associated with the blue domain can communicate with each other
while Spokes associated with the green domain can communicate with each other.
But there is no cross communication between blue domain and green domain unless
there is connection policy. The concept is the same as
Network Domains
and
Connection Policies
defined in TGW Orchestrator, except this is implemented with Aviatrix Transit
where both Spokes and Transit VPC/VNet deploy Aviatrix gateways. (Note the
segmentation works with Azure native Spoke VNets.)
## What is a Network Domain in Multicloud Transit?
A Network Domain is an Aviatrix enforced network of VPC/VNet members, where
VPC/VNets in the Network Domain can communicate with each other, and VPC/VNets
not in the network domain cannot communicate with VPC/VNets in the Network
Domain.
One or more Spoke VPC/VNets are members in a network domain.
Spokes in a network domain can communicate with each other via an Aviatrix
Transit Gateway.
The Aviatrix Controller dynamically programs and updates both VPC/VNet route
tables so that instances in different Spoke VPC/VNets in the same domain can
communicate with each other.
Two network domains are not connected, i.e., a Spoke in one domain has no
connectivity to another Spoke in a different domain. Connection policy must be
specified to connect the two domains so that Spokes in each domain can
communicate with each other.
The Network Domain also applies to the hybrid connection from Aviatrix Transit
Gateway to on-prem or remote sites. Each BGP peer or connection can be
associated with one Network Domain.
## What is a Connection Policy?
A connection policy is a rule enforced by Aviatrix for cross Network Domain
connectivity.
## What are the benefits of using Network Domains and Connection Policies?
The key use case for building Network Domains is to segment traffic for enhanced
security posture.
Using Network Domains and Connection Policies allow you to identify groups of
Spokes and Edges with the same requirements from a networking point of view and
then apply connection policies at the group level. This avoids having to
individually specify connections at the Spoke level. The Aviatrix Controller
takes care of route programming of all route tables.
## Can an Aviatrix Transit Network Domain work with TGW Orchestrator Network Domain?
They do not work together at this time, however we have plan to integrate them
in the future.
## How do I set up Multicloud Transit Segmentation?
Follow the
Transit Segmentation Workflow
.
## How many Network Domains are supported in Multicloud Transit Segmentation?
The configuration of Network Domain is managed as a global setting. Each
Controller can support a maximum of 200 network domains. The number of network
domains is independent of the number of gateways.
## What is the difference in implementation of Segmentation between Release 6.1 and Release 6.0?
In Release 6.1 and later, each Network Domain is implemented as an individual
route table on the Aviatrix Transit Gateway. This allows better handling for the
default route (0.0.0.0/0) traffic if different domains require different egress
next hop. In addition, duplicate Spoke CIDRs attached to different Aviatrix
Transit Gateways can co-exist if they belong to different domains.
## What is the limitation of Segmentation?
* Duplicated CIDRs that cross domains or cross transits may not work all the
time. Aviatrix does not support duplicated CIDRs that cross domains or cross
transits.
* Overlapping CIDRs advertised from on-prem to different Spoke network domains
connected to one Aviatrix Transit Gateway is not supported.