> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Protect VPC/VNets
On the Security > Egress > Protected VPC/VNets tab, you can protect VPC/VNets
that are being monitored, to ensure that only trusted traffic is going to the
Internet.
To protect VPC/VNet egress traffic:
1. On the Security > Egress > Protected VPC/VNets tab, do one of the following:
1. Select one or more VPC/VNets in the table and click *Protect* in the
Actions menu.
2. Click *Protect* next to a VPC/VNet in the table.
2. The Protect VPC/VNet dialog displays all trusted traffic flows observed in
the selected VPC/VNet. Select one or more domains to continue to allow
traffic to flow to those domains. You can use the AI FQDN Analyzer to view
details on the domains and determine if you want to trust them.
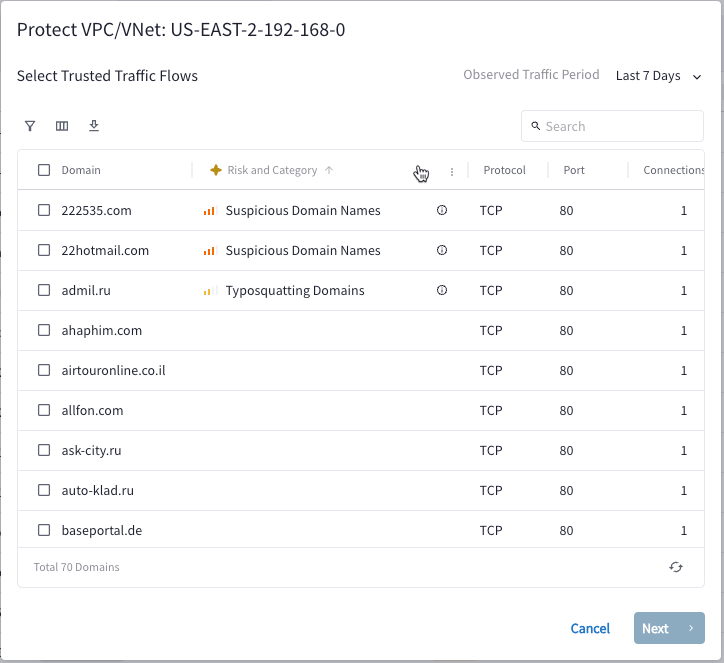 If there are no domains listed, you cannot proceed to the next step.
3. Click *Next*. The Review Distributed Cloud Firewall Rule Changes page
displays.
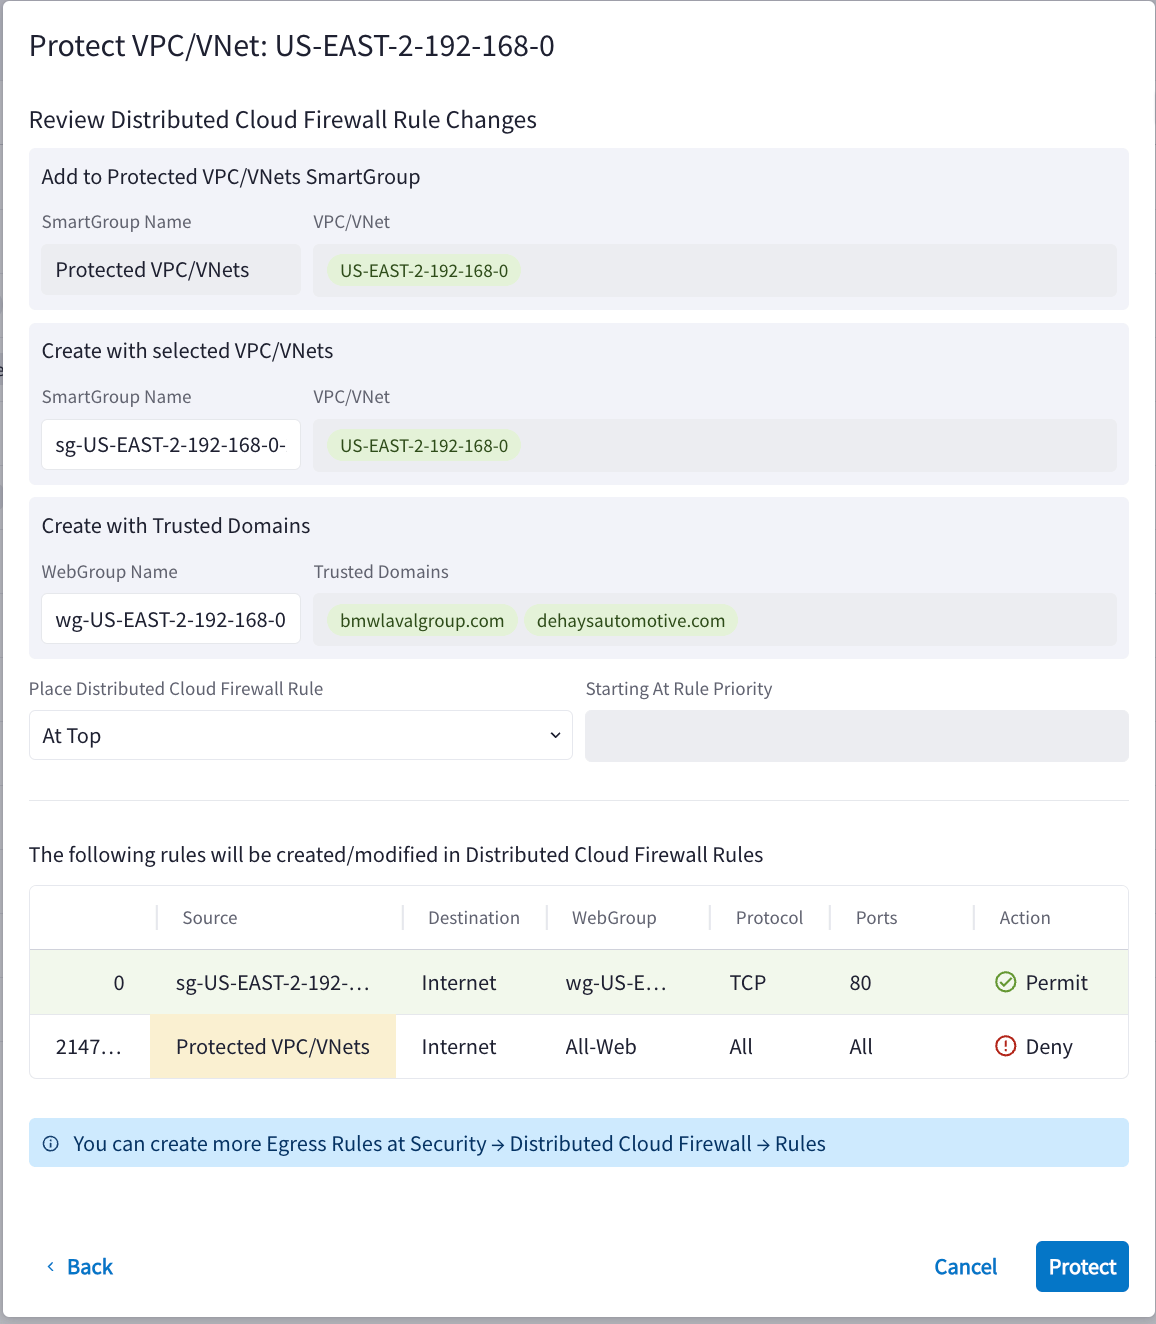 This page displays the changes that will occur after protection is applied.
* The selected VPC/VNets will be added to the Protected VPC/VNets SmartGroup.
This SmartGroup contains all VPC/VNets that are protected.
* Another SmartGroup is created that contains just the VPC/VNets you selected.
* The selected trusted domains will be added to a new WebGroup.
4. Select where the new DCF rules will be placed. You can also enter a value for
*Starting at Rule Priority* (if applicable).
* A new DCF rule will be created for the selected VPC/VNets that permits traffic
from the VPC/VNets to the trusted domains.
* The Protected VPC/VNets Rule will be updated with the selected VPC/VNets. This
acts as a Default Deny Rule.
5. Click *Protect*.
6. A message displays indicating any change in Egress Score.
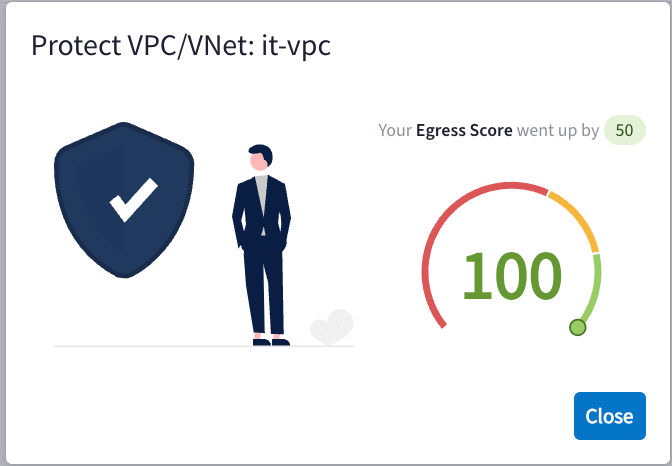 The VPC/VNets are now protected (and continue to be monitored). Also, a new
WebGroup is created for the trusted domains, and the Protected VPC/VNets
SmartGroup and Rule are updated.
## Next Steps
* View the Egress Security Score
The Protect VPC/VNets dialog displays all trusted traffic flows observed in the
selected VPC/VNet.
Select one or more domains to continue to allow traffic to flow to those
domains. You can use the AI FQDN Analyzer to view details on the domains and
determine if you want to trust them. If there are no domains listed, you cannot
proceed.
After clicking *Next*, the Review Distributed Cloud Firewall Rule Changes page
displays. This page displays the changes that will occur after protection is
applied.
* The selected VPC/VNets will be added to the Protected VPC/VNets SmartGroup.
This SmartGroup contains all VPC/VNets that are protected.
* Another SmartGroup is created that contains just the VPC/VNets you selected.
* The selected trusted domains will be added to a new WebGroup.
Select where the new DCF rules will be placed. You can also enter a value for
*Starting at Rule Priority* (if applicable).
* A new DCF rule will be created for the selected VPC/VNets that permits traffic
from the VPC/VNets to the trusted domains.
* The Protected VPC/VNets Rule will be updated with the selected VPC/VNets. This
acts as a Default Deny Rule.
Click *Protect*. A message displays indicating any change in Egress Security
Score.
The VPC/VNets are now protected (and continue to be monitored.) Also
* A new WebGroup is created for the trusted domains.
* The Protected VPC/VNets SmartGroup and Rule are updated.
## Related Topics
* [Egress Traffic Protection](/docs/cloud/security/egress-nat/egress-traffic-protection)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.