> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# About Decryption CA Certificates and Trust Bundles
> Decryption CA Certificate
The CA certificate is used when you enable TLS Decryption on a policy. The
decryption CA certificate (the Aviatrix certificate, or your own) must be
distributed to all of your client machines so that signature checks are
successful.
Aviatrix strongly recommends replacing the default Aviatrix CA certificate with your own CA certificate.
The certificate must be in .pem format and must be private.
If TLS Decryption is enabled, encrypted gateway traffic is decrypted and inspected, and then re-encrypted. All inspection and policy enforcement occur within the customer's cloud environment.
You can perform the following actions for CA certificates and trust bundles:
* [Upload your own certificate](#upload-or-replace-your-own-certificate)
* [Renew a certificate](#renew-the-aviatrix-certificate)
* [Upload or remove your own trust bundle](#upload-replace-or-remove-a-trust-bundle)
* [Determine which level of enforcement](#edit-enforcement) to apply to CAs that
are not signed by a root certificate in the trust bundle
Decryption CA Certificates should be trusted by the Source SmartGroup virtual
machines when TLS Decryption is enabled for proxy.
## Upload or Replace Your Own Certificate
It is best to upload your own certificate (must be in .pem format), since you
likely have this certificate in use throughout your environment.
When you upload a certificate, it replaces the default Aviatrix CA certificate.
If you remove a certificate, the Aviatrix default certificate is automatically
uploaded.
Ensure that the downloaded file is saved to the appropriate location on your
computer, and any client machines involved in your Distributed Cloud Firewall
(DCF) configuration.
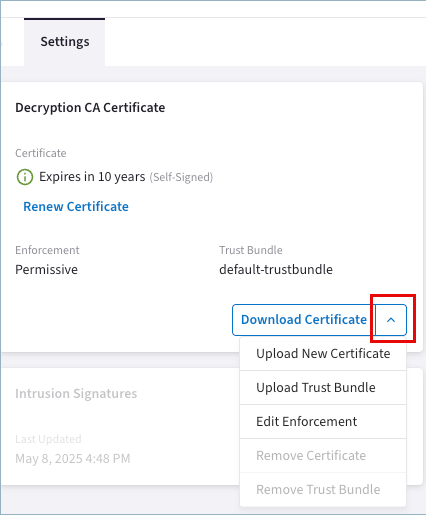
1. On *Distributed Cloud Firewall > Settings > Decryption CA Certificate* card,
click the *More Options* arrow next to *Download Certificate*.
 2. To upload or replace a certificate:
1. Click *Upload New Certificate*.
2. In the Upload New Certificate dialog, select the CA certificate to upload.
3. Select the corresponding certificate key. Both fields must be populated.
4. Click *Upload*.
3. To remove a certificate, select *Remove CA Certificate* from the More Options
menu.
## Renew the Aviatrix Certificate
You must renew your Aviatrix CA certificate when it is about to expire. This
feature is available on the *Distributed Cloud Firewall > Settings > Decryption
CA Certificate* card. The renewal only works for the Aviatrix certificate, not
for an uploaded certificate.
When you click *Renew Certificate*, the certificate renews automatically.
You can also
[upload your own CA certificate](#upload-or-replace-your-own-certificate).
## Upload, Replace, or Remove a Trust Bundle
A trust bundle is a list of trusted CA certificates. If a gateway terminates the
TLS connection and negotiates a new TLS connection to the origin certificate,
then the origin certificate must be signed by one of the trusted CA certificates
if running in the Strict [Enforcement mode](#edit-enforcement).
You can upload a trust bundle that has an expired certificate, but you will
see a warning.
When you upload a trust bundle, it replaces the default Aviatrix bundle. If you
remove your trust bundle, the Aviatrix default bundle is automatically uploaded.
To upload, remove, or replace a trust bundle (must be in .pem format):
1. On *Distributed Cloud Firewall > Settings > Decryption CA Certificate* card,
click the *More Options* arrow next to *Download Certificate*.
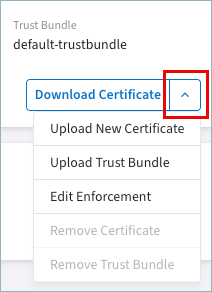 2. To upload or replace a trust bundle, click *Upload Trust Bundle*, select the
.pem file, and click *Upload*.
3. To remove the trust bundle, click *Remove Trust Bundle* on the More Options
menu.
## Edit Enforcement
Use the Enforcement option to determine how Distributed Cloud Firewall handles
origin certificates that are not signed by a trusted Certificate Authority.
Aviatrix strongly recommends changing the enforcement level to *Strict*.
To edit the enforcement level:
1. On *Distributed Cloud Firewall > Settings > Decryption CA Certificate* card,
click the *More Options* arrow next to *Download Certificate* and click *Edit
Enforcement*.
2. In the Edit Enforcement dialog, select an Enforcement level:
* Strict: terminate connection for incorrect signatures
* Permissive: alert, but persist connection for incorrect signatures
* Ignore: certificate signatures are not checked
### Remove a Certificate
To remove a certificate and replace it with your own:
1. On the Security > Distributed Cloud Firewall > Settings tab, on the
Decryption CA Certificate card, click the arrow next to *Download
Certificate* and click *Remove Certificate*.
2. When prompted, click *Delete* to remove the certificate.
3. [Upload your own (private) certificate](#upload-or-replace-your-own-certificate).
## Verify the Decryption CA Certificate
You should check that the CA certificate is imported correctly. The following is
one verification method.
1. Replace the default Decryption CA Certificate with a private decryption CA
certificate.
2. Enable TLS Decryption on the DCF rules to match your traffic.
3. Import the Decryption CA signer or root CA into your VMs.
4. Generate traffic for the above rule(s).
5. To verify that the Decryption CA Certificate chain or root is imported
correctly to the VM, navigate to the relevant URL in your web browser.
If you see 'Untrusted' warnings, you should run through these steps again. If
the import was successful, you should see the new certificate chain with the
Decryption CA as the signer of the website.
## Related Topics
* [Create Distributed Cloud Firewall Egress Rules](/docs/cloud/security/dcf/dcf-create-rules)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.