> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Overview
> Single sign-on to Aviatrix PaaS with OIDC
Single sign-on (SSO) allows users to log in to various applications in your
business using a single set of credentials. You must configure users with an
OAuth Identity Provider (IdP), such as Microsoft. The OAuth application
authenticates the user and then redirects the user to the Aviatrix PaaS console.
Currently, Microsoft Azure Entra ID (OpenID Connect) is the only supported
Identity Provider (IdP).
After a company enables SSO with Aviatrix PaaS, all users from that company must
sign on to Aviatrix using SSO. If SSO is disabled, users that have existing
accounts with email authentication will still be able to log in to Aviatrix
PaaS, if the account is still subscribed to Aviatrix.
Setting up SSO with Aviatrix PaaS is a 4-step process:
1. [Get the Aviatrix PaaS OAuth callback URL](#get-the-aviatrix-paas-oauth-callback-url)
2. [Create an OAuth application in Azure using the callback URL](#create-an-oauth-application-in-azure)
3. [Verify the Token Configuration in Azure](#verify-the-token-configuration)
4. [Configure SSO in Aviatrix Console](#configure-sso-in-aviatrix-paas)
## Get the Aviatrix PaaS OAuth Callback URL
You need the Aviatrix PaaS OAuth callback (redirect) URL to set up the OAuth
application in your IdP.
This URL is the address for the Aviatrix console, to which you will be
redirected after you are successfully authenticated.
To get the callback URL:
1. Log in to Aviatrix PaaS console.
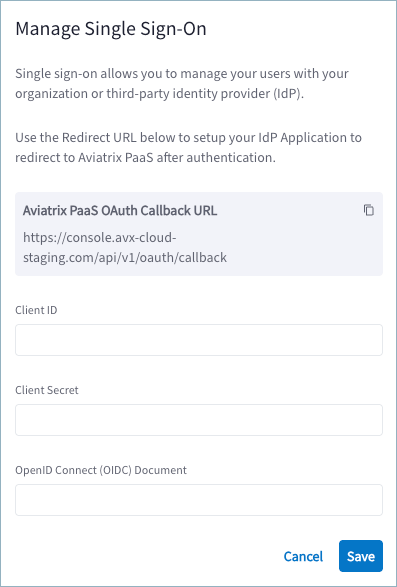
2. Go to **Settings > Single Sign-On** and click **Manage**.
3. In Manage Single Sign-On, go to **Aviatrix PaaS OAuth Callback URL**, click
the copy icon, and then save the URL.
You must enter this URL when creating an application in your CSP account.
 **Next Step:**
[Create an OAuth Application in Azure](#create-an-oauth-application-in-azure)
## Create an OAuth Application in Azure
You must have admin privileges for Microsoft Azure portal to complete this task.
If you do not yet have an Aviatrix PaaS application and client secret, you need
to create them. To create an application in Azure, you need the
[callback (redirect) URL from the Aviatrix PaaS console](#get-the-aviatrix-paas-oauth-callback-url).
For the OAuth application in Azure, you must copy the application (client) ID,
client secret value, and the URI for the OpenID Connect (OIDC) metadata
specification document. You will use this information to configure SSO in the
Aviatrix PaaS console.
To create an OAuth application:
1. Log in to your Azure account.
2. Go to **App registrations**.
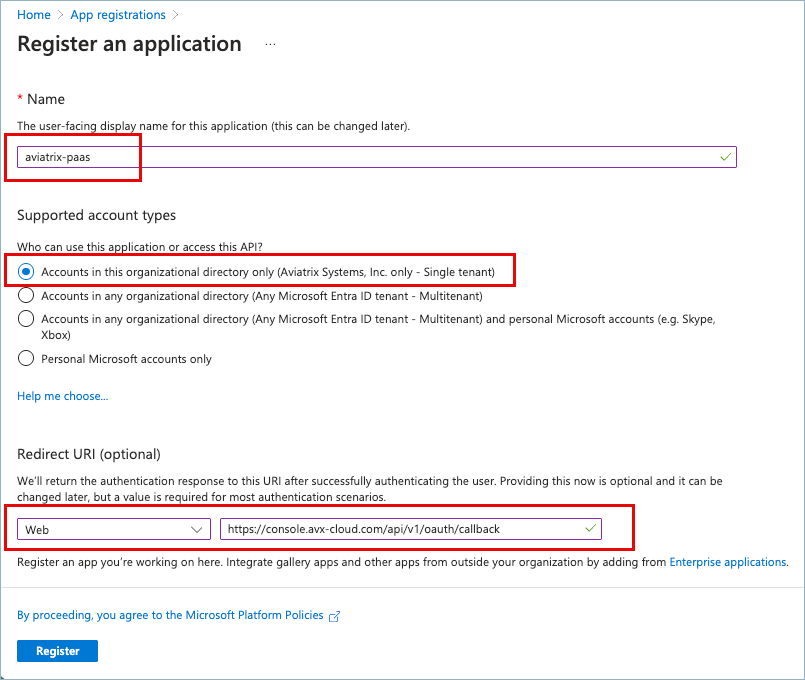
3. Click **+ New registration** and enter the following:
| Option | Action |
| - | - |
| Name | Enter a user-facing display name for the application, such as "aviatrix-paas". |
| Supported account types | Select "Accounts in this organizational directory only (Aviatrix...Single Tenant)". |
| Redirect URI | Select the **Web** platform and enter the Callback URL you copied from the Aviatrix PaaS console. |
 1. Click **Register**.
2. In the left navigation, click **Certificates & secrets > Client secrets**.
3. Click **+ New client secret**, enter a description and expiration date, and
click **Add**.
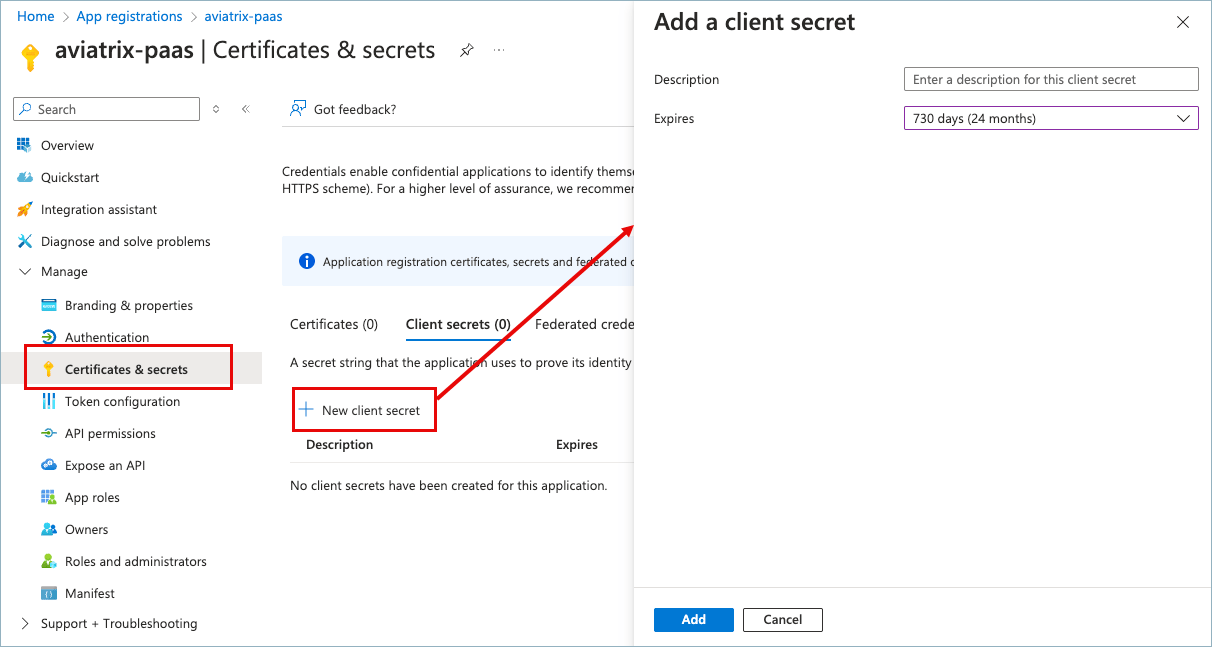 The new client secret displays in the list.
1. Copy the **Value** and **Secret ID** you just created and save them to a safe
place.
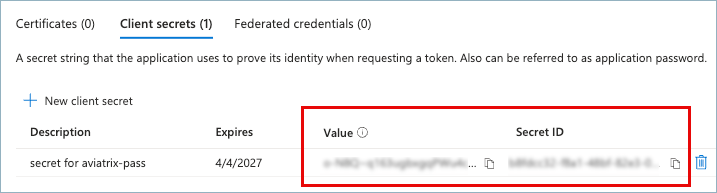 You need the client secret value to enter in the Aviatrix PaaS console.
The client secret value is only available at this time. You cannot retrieve it
later. Be sure to copy and save it now.
1. Go to **App registrations > Owned applications**.
2. Click on the Aviatrix PaaS application you created.
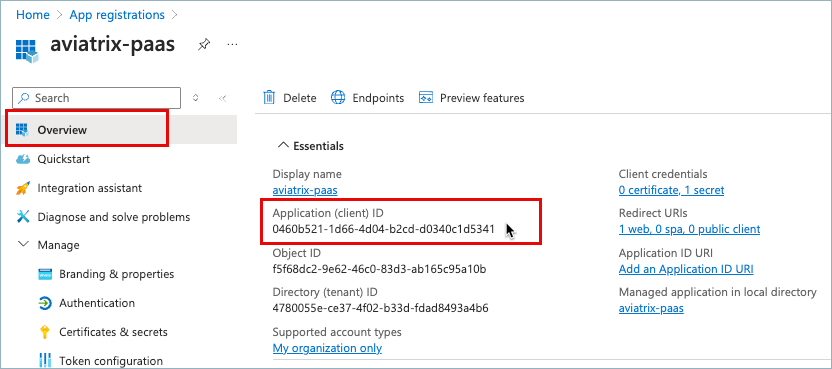
3. On the application Overview page, copy and save the **Application (client)
ID**.
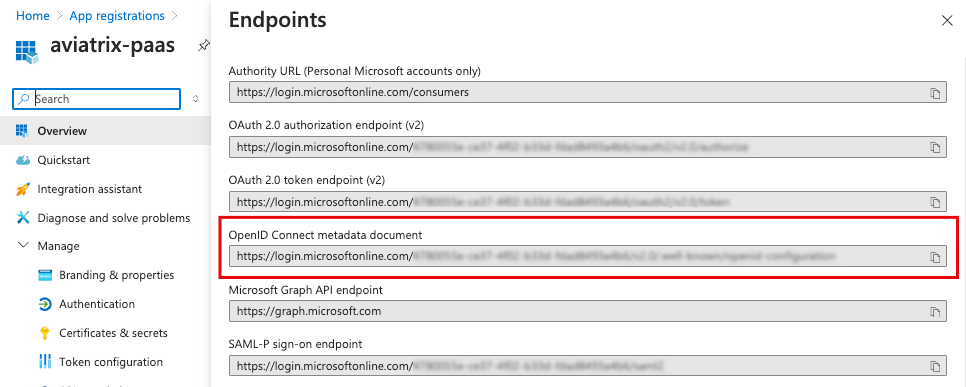
 1. Click the **Endpoints** tab.
2. Scroll through the list, locate **OpenID Connect metadata document**, and
then copy and save the URL.
 **Next Step:** [Verify the Token Configuration](#verify-the-token-configuration)
## Verify the Token Configuration
For SSO to work properly with Aviatrix PaaS, *Group claim* and several *Optional
claims* must be set in Azure for the Aviatrix PaaS application.
For more details about configuring optional claims in tokens, see
[the Microsoft documentation](https://learn.microsoft.com/en-us/entra/identity-platform/optional-claims).
1. In Azure, go to **App Registrations** and select the Aviatrix PaaS
application.
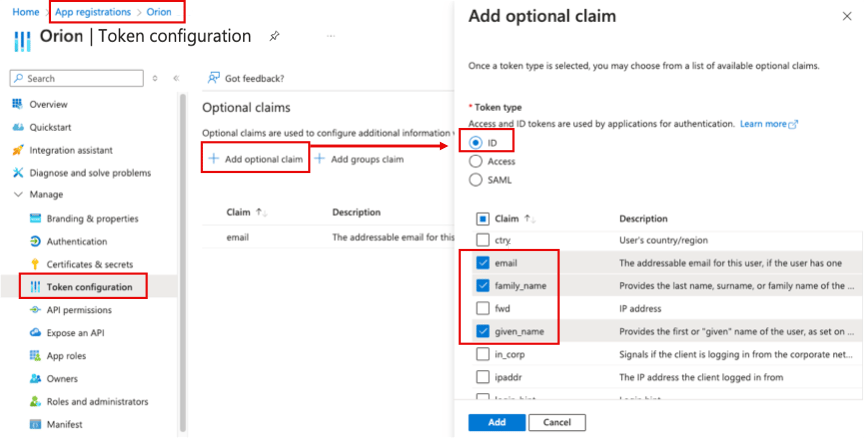
2. In the navigation pane, click **Token configuration**.
3. Verify that the following **Claims** are listed:
* `email`
* `family_name`
* `given_name`
4. If the **Optional claims** are not listed, do the following:
1. Click **+ Add optional claim**.
2. Under **Token type**, select **ID**.
3. Select `email`, `family_name`, and `given_name`, and then click **Add**.
4. If an option displays to "Turn on the Microsoft Graph email, profile
permission", click the checkbox and then click **Add**.
 **Next Step:** [Configure SSO in Aviatrix PaaS](#configure-sso-in-aviatrix-paas)
## Configure SSO in Aviatrix PaaS
Before configuring single sign-on (SSO) in the Aviatrix PaaS console, be sure
you have collected the required information. For more information, see
[Create an OAuth Application in Azure](#create-an-oauth-application-in-azure).
You must have admin privileges in the Aviatrix PaaS console to configure SSO.
To configure SSO:
1. Log in to the Aviatrix PaaS console.
2. Go to **Settings**.
3. On the **Single Sign-On** card, click **Manage**.
4. Select your OAuth identity provider (IdP) and enter the information you
copied from your IdP:
* Client (Application) ID
* Client Secret value
* OpenID Connect (OIDC) Document URL
5. Click **Save**.
The Client ID and OIDC Document URL display on the Single Sign-On card on the
Settings page.
Anyone who has an SSO account with your company and has access to this Aviatrix
account should now be able to log in to Aviatrix PaaS using SSO.
To sign in to an existing Aviatrix console with administrator privileges, you
must be invited by an admin on the console and given the admin role.
Otherwise, you sign in with read-only privileges.
**Next Step:**
[Sign in to Aviatrix Console with SSO](#sign-in-to-aviatrix-console-with-sso)
**Related Topics:**
[Disable SSO](/docs/cloud/platform-administration/manage/sso-disable)
## Sign in to Aviatrix Console with SSO
After SSO has been fully configured between your identity provider (IdP) and
Aviatrix PaaS, you can sign in using your SSO account. Go to the Aviatrix PaaS
console at [console.cloud.aviatrix.com](https://console.cloud.aviatrix.com/).
If you are signed in to your IdP, when you sign in to Aviatrix PaaS with your
email address, you will be immediately redirected and automatically signed in to
the Aviatrix console.
If you are not signed in to your IdP, when you sign in to Aviatrix PaaS an
authentication window displays for you to sign in to your IdP. After signing in
to your IdP, you are then redirected and automatically signed in to the Aviatrix
console.
To sign in to an existing Aviatrix console with administrator privileges, you
must be invited by an admin on the console and given the admin role.
Otherwise, you sign in with read-only privileges.
**Next Step:** [Add a User](/docs/cloud/platform-administration/manage/user-add)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.