> ## Documentation Index
> Fetch the complete documentation index at: https://docs.aviatrix.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Aviatrix Cloud Firewall Secure Egress Implementation Guide for PaaS
The Aviatrix Cloud Firewall™ Secure Egress Implementation Guide for PaaS
outlines the steps required to implement the Aviatrix secure egress use case in
Aviatrix PaaS. The goal is to achieve deep visibility into your traffic and
centralized policy enforcement, ensuring secure, compliant, and optimized
performance and cost efficiency.
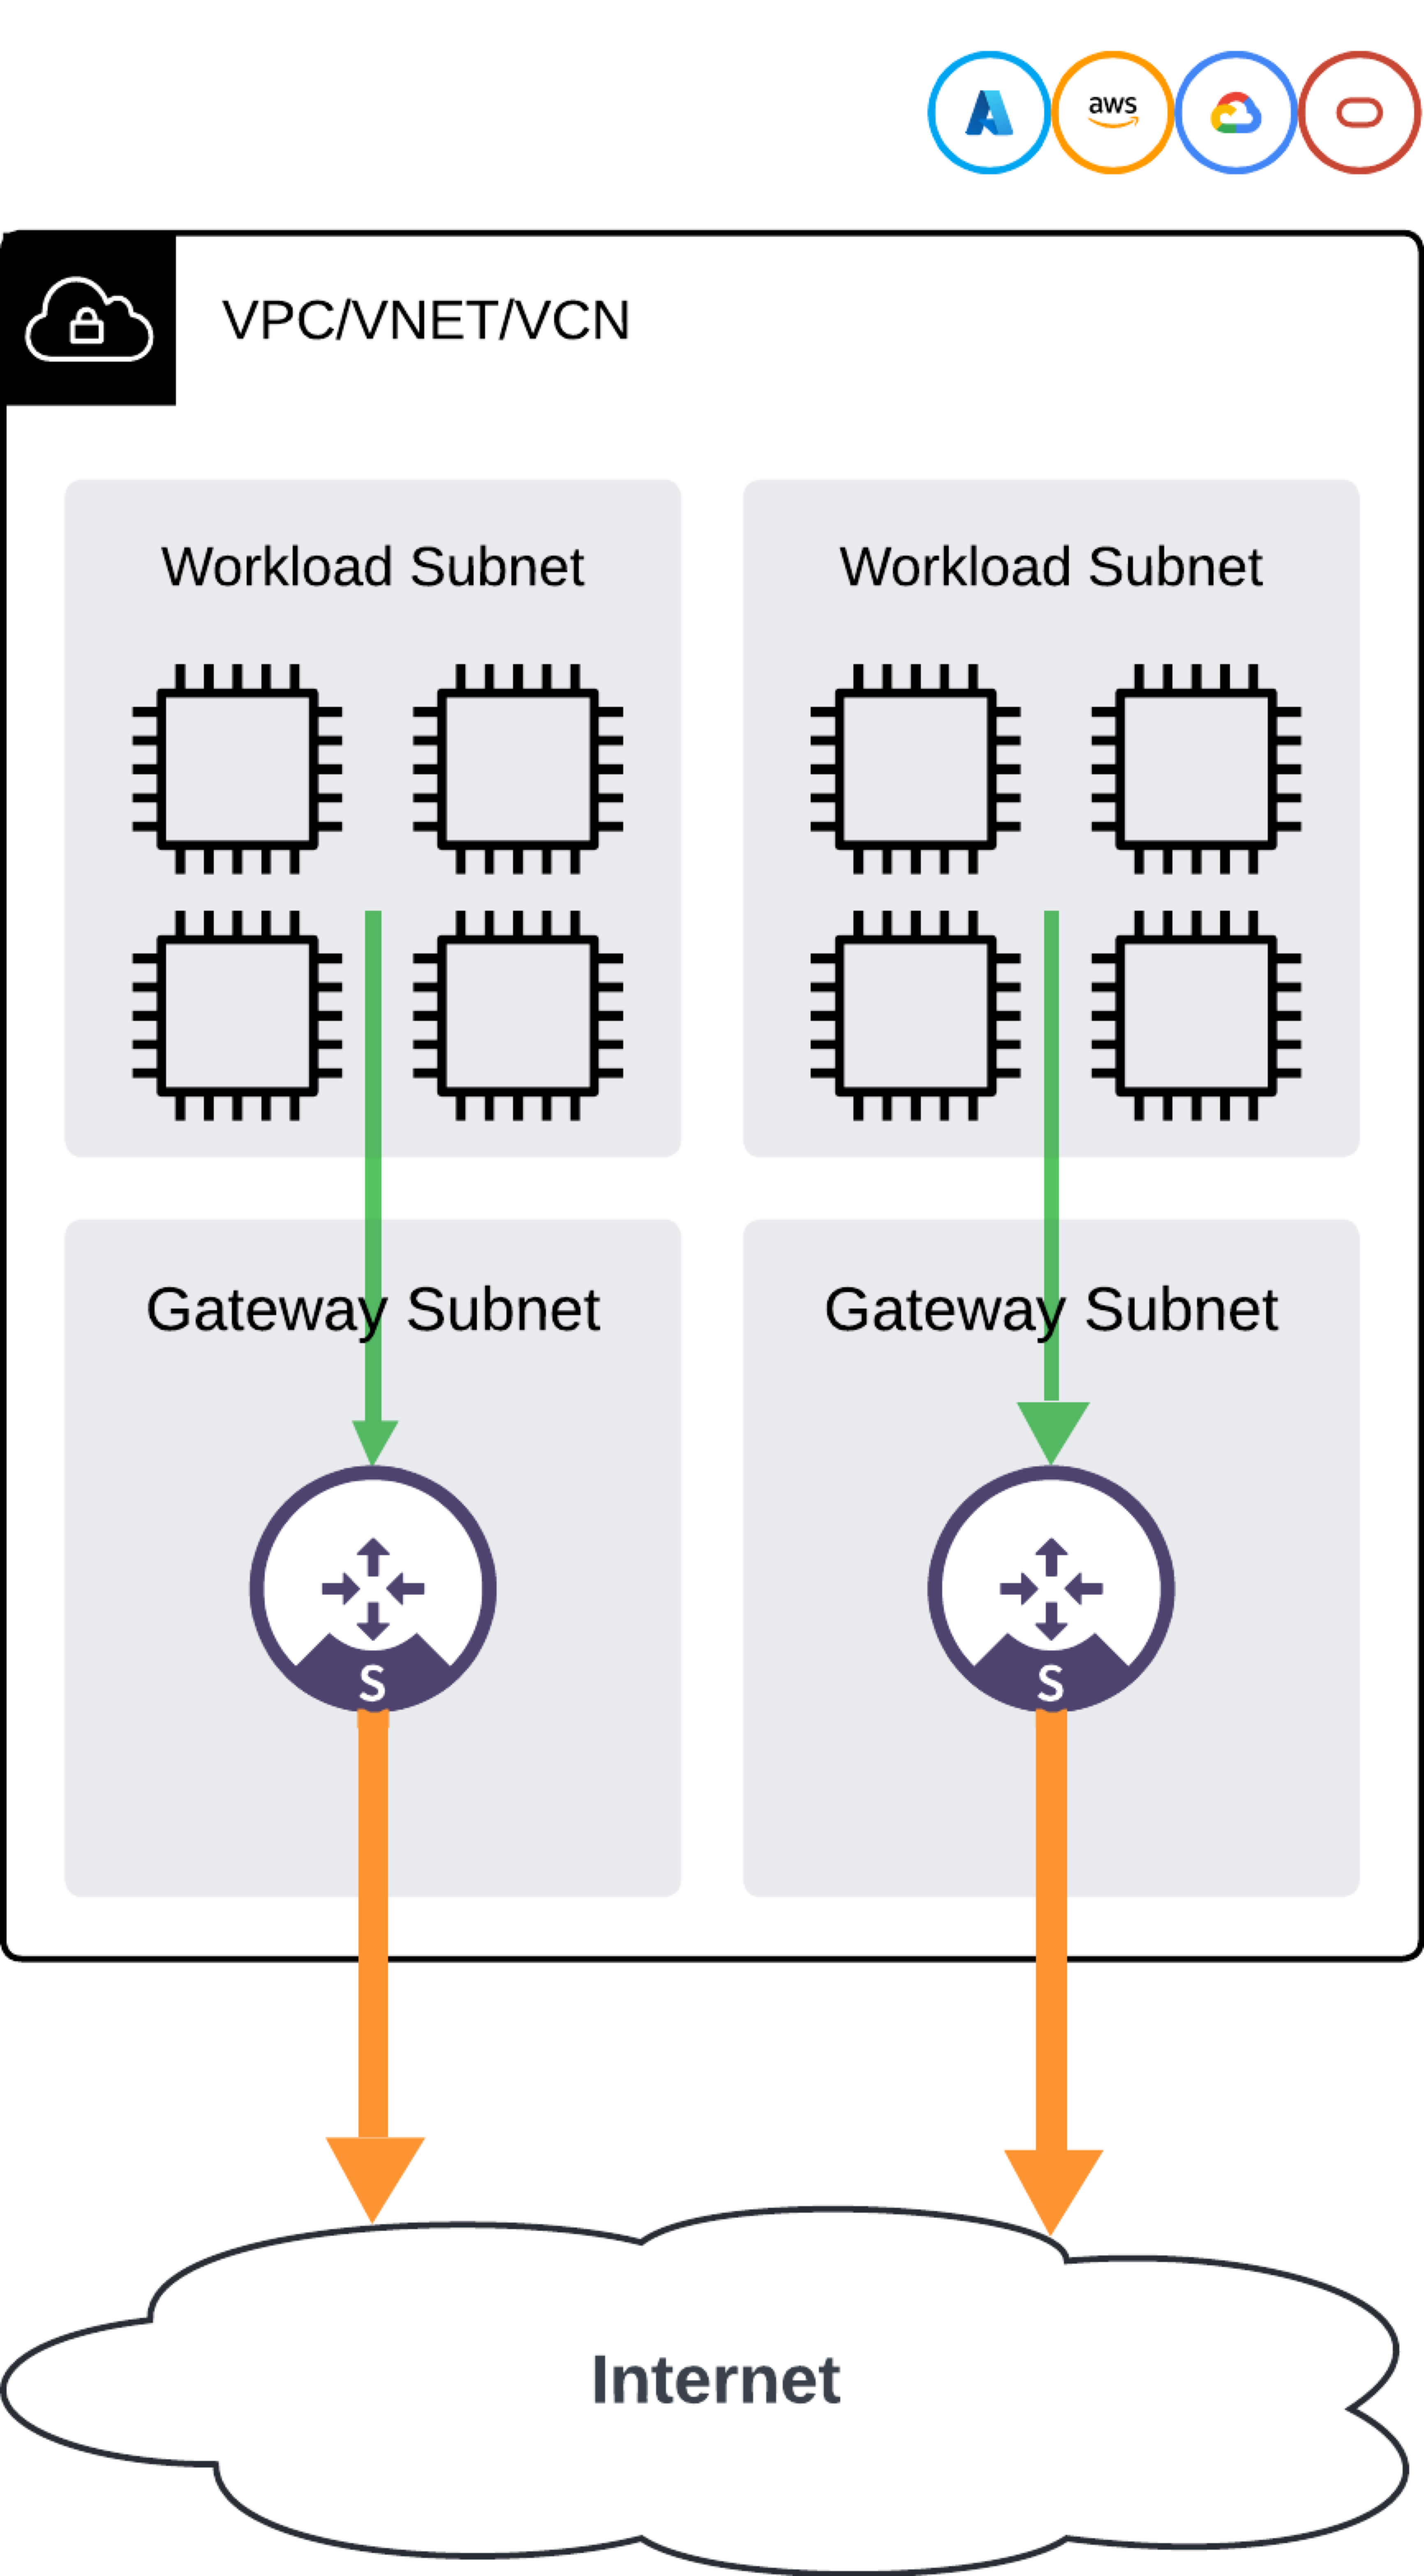 ## Network Design
Aviatrix PaaS utilizes a centralized management and control plane to scale
management across multiple VPCs. This enables customers to deploy and manage
Spoke gateways, along with their NAT and security policies, from a single
console or through automation capabilities such as Terraform and API.
Aviatrix recommends following these steps to implement your cloud egress
security.
## Onboard Your Cloud Accounts and VPC/VNets
* Ensure that your cloud accounts are onboarded:
* [AWS](/docs/cloud/platform-administration/onboard-offboard/aws-cloud-account-onboard)
* [Azure](/docs/cloud/platform-administration/onboard-offboard/azure-cloud-account-onboard)
* [Onboard VPC/VNets](/docs/cloud/platform-administration/onboard-offboard/vpc-vnet-onboard)
Your VPC/VNets are in Unprotected status until they are monitored (Monitored
status). After they are protected, they are in Protected status. This
information is displayed on the Protected VPC/VNets card on the Egress >
Overview tab.
See
[Egress Traffic Protection](/docs/cloud/security/egress-nat/egress-traffic-protection)
for more information on the VPC/VNet status types.
## Monitor Your VPC/VNets
After VPC/VNets are onboarded, you can
[monitor](/docs/cloud/security/egress-nat/egress-monitor-vpc-vnets) them to
check the traffic flows. Monitoring your VPC/VNets also enables egress.
After monitoring your VPC/VNets, you can do one of the following to protect your
traffic:
* [Protect your VPC/VNets using AI](#protect-your-vpcvnets-using-ai) or
* [Protect your VPC/VNets with Groups and Rules](#protect-your-vpcvnets-with-groups-and-rules)
## Protect Your VPC/VNets using AI
After VPC/VNets are monitored, the top traffic destinations, domains, and
offenders are displayed on the Security > Egress > Analyze tab. You can use
filter options on this tab to show results for specific VPC/VNets.
Based on this information, and using AI to reveal information about traffic
flows, you can
[protect specific traffic flows](/docs/cloud/security/egress-nat/egress-protect-vpc-vnets)
to ensure that only trusted traffic is going to the Internet.
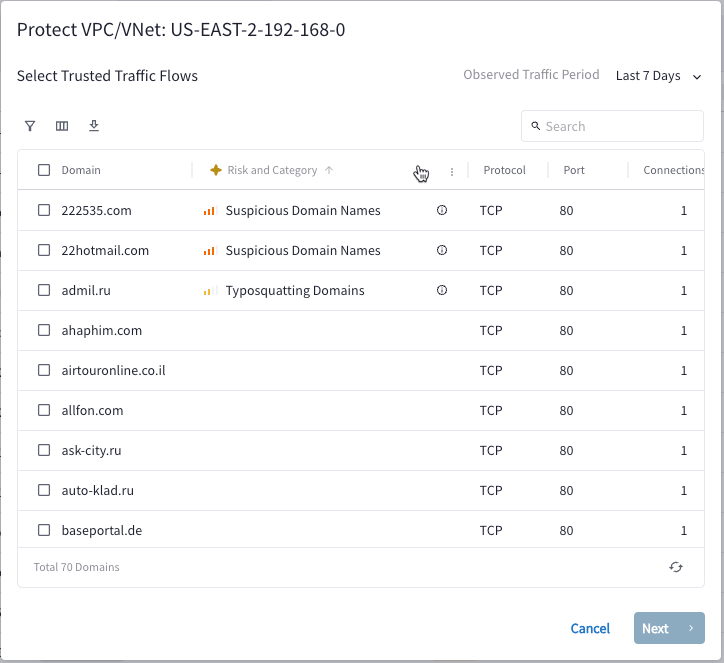 The [AI FQDN Analyzer](/docs/cloud/security/egress-nat/ai-fqdn-analyzer) on the
Protect VPC/VNet dialog provides risk and category details on each domain. After
viewing these details, you can select one or more domains to trust.
After the domains are protected:
* [SmartGroups, WebGroups, and DCF rules are created](/docs/cloud/security/egress-nat/about-egress-security#egress-traffic-protection)
* Your
[Egress Security Score](/docs/cloud/security/egress-nat/egress-security-score)
is updated
## Protect Your VPC/VNets with Groups and Rules
Protecting your VPC/VNets using groups and rules requires a manual approach.
After monitoring your traffic for a certain period, you can establish the
necessary groups and DCF rules to safeguard your traffic.
### Create Groups
* [SmartGroups](/docs/cloud/resource-groups/smartgroup/smartgroups-about):
Create logical groupings of resources for DCF egress rules.
* [WebGroups](/docs/cloud/resource-groups/webgroups/webgroups-create): Manage
outbound Internet traffic with WebGroups.
* [ExternalGroups](/docs/cloud/resource-groups/externalgroup/externalgroup-create):
Manage external feeds (such as Countries, Threat Feeds, and SaaS-based
services) with ExternalGroups.
Here are some examples of SmartGroups, WebGroups, and ExternalGroups you can
create.
#### SmartGroups
1. Create a SmartGroup named "Marketing-Department" that includes all VMs or
resources tagged with `Department: Marketing`.
2. Create a SmartGroup named "Sales-Team" that includes all VMs or resources
tagged with `Team: Sales`.
3. Create a SmartGroup named "All-Employees" that includes all VMs or resources
within the organization.
4. Create a SmartGroup named "Security-Team" that includes all VMs or resources
tagged with `Team: Security`.
#### WebGroups
1. Create a WebGroup named "SaaS-Allowed" that includes the domains
salesforce.com and office.com.
2. Create a WebGroup named "Social-Media-Restricted" that includes the domains
`facebook.com`, `x.com`, and `instagram.com`.
3. Create a WebGroup named "Gambling-Sites" that includes the domains
`bet365.com`, `pokerstars.com`, and `888.com`.
#### ExternalGroups
Create an ExternalGroup named "Blocked-Countries" that includes countries such
as `North Korea` and `Iran`.
### Create Distributed Cloud Firewall Egress Rules
The Aviatrix Distributed Cloud Firewall (DCF) solution in Aviatrix PaaS ensures
consistent security policies across cloud platforms by defining egress rules
that describe the relationship and trust between resources in different
SmartGroups (including the predefined SmartGroup Public Internet, which cannot
be deleted), WebGroups, and External Groups.
Operating within individual VPCs or VNets, DCF inspects and enforces egress
security rules directly in the cloud network where the traffic originates,
regardless of its destination. These rules are applied at the point of egress
and can be customized for logging. Rules are evaluated in order and should
follow a naming convention that indicates their intent, allowing you to
establish a pattern that suits your cloud deployment needs.
All of these rules should use the TCP protocol and port 443.
#### Example 1: Restricting Access to Social Media Sites
*Scenario*: You want to restrict access to social media sites for a specific
department within your organization.
Create a DCF rule with the following characteristics:
* Source: "Marketing-Department" SmartGroup
* Destination: "Social-Media-Restricted" WebGroup
* Action: Deny
#### Example 2: Allowing Access to Specific SaaS Applications
*Scenario*: You want to allow access to specific SaaS applications such as
Salesforce and Office 365 for the Sales team.
Create a DCF rule with the following characteristics:
* Source: "Sales-Team" SmartGroup
* Destination: "SaaS-Allowed" WebGroup
* Action: Allow
#### Example 3: Blocking Access to Gambling Sites
*Scenario*: You want to block access to gambling sites for all employees.
Create a DCF rule with the following characteristics:
* Source: "All-Employees" SmartGroup
* Destination: "Gambling-Sites" WebGroup
* Action: Deny
#### Example 4: Allowing Access to External Threat Feeds
*Scenario*: You want to allow access to external threat intelligence feeds for
your security team.
Create a DCF rule with the following characteristics:
* Source: "Security-Team" SmartGroup
* Destination: Default ThreatGroup ExternalGroup: you can also select one or
more threat types and/or severity types
* Action: Allow
Example 5: Geoblocking Specific Countries Scenario: You want to block access to
specific countries for compliance reasons.
Create a DCF rule with the following characteristics:
* Source: "All-Employees" SmartGroup
* Destination: "Blocked-Countries" ExternalGroup
* Action: Deny
### Distributed Cloud Firewall Monitoring
The Security > Distributed Cloud Firewall > Monitor tab displays all traffic
logged by DCF rules that have logging enabled. Based on what you see here, you
can edit your groups and DCF egress rules for better traffic protection.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.